Seamless crypto off-ramp with a 100% compliant Swiss bank account — zero card fees, 1% top-up, instant Mastercard virtual debit, and global spending via PayPal, Apple Pay, Google Pay & more. Powered by BloFin.
🚨#Web3ThreatIntelligence🚨
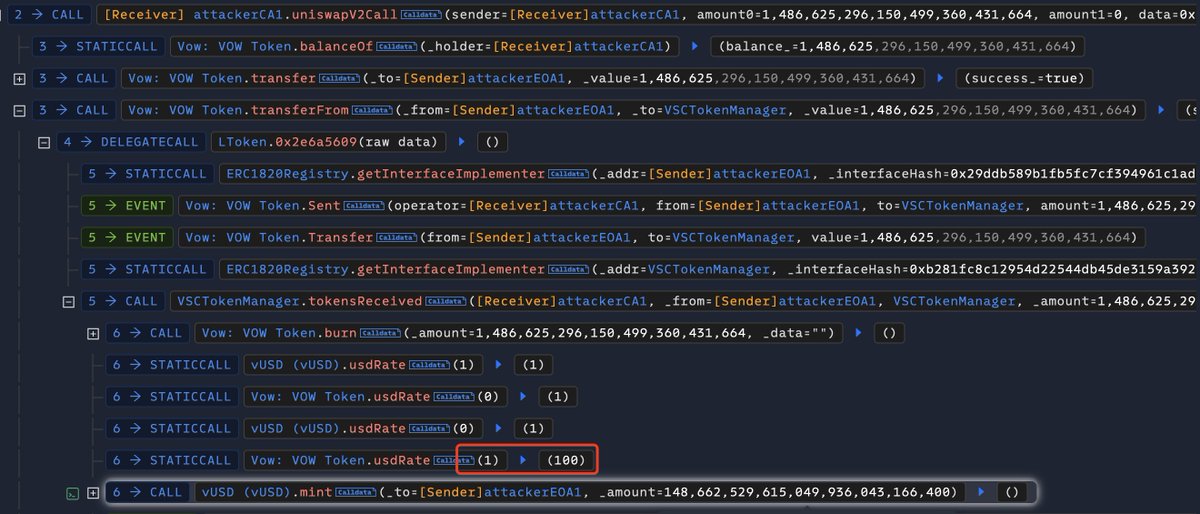
Through our analysis of suspicious transactions in the @Vowcurrency protocol (see the previous tweet for details), it is suspected that the private key of the usdRateSetter (0xbA1be907) of VOW Token has been leaked. Before and after the attacker executed the transaction, the address changed the value of the usdRate parameter[p1].
The attacker used the modified USDRate to mint a large amount of $vUSD (1,486,625,529) in exchange for more
$VOW (59,507,425) profits, the specific attack process is as follows[p2]:
1. From Uniswap V2: VOW Lightning Loan 1,486,625 $VOW
2. Transfer 1,486,625 $VOW to VSCTokenManager
3. Execute burn to destroy 1,486,625 $VOW in the internal function tokenReceived of VSCTokenManager
4. Check that Vow: VOW Token. usdRate (1) returns 100. The key step is that through our analysis, the usdRateSetter (0xbA1be907) address maliciously updated the usdRate exchange rate to 100 in previous transactions, resulting in the minting of a large amount of vUSD
5. Use the exchange rate difference to mint 1,486,625,529 vUSD and then exchange it for 59,507,425 $VOW
6. Repay Uniswap V2: VOW Lightning Loan of 1,491,098 $VOW
7. Exchange 26,107,347 $VOW for 175 $ETH
8. Use 26,107,347 $VOW to exchange for 595,970 $USDT
9. Wallet balance of 5,801,632 $VOW
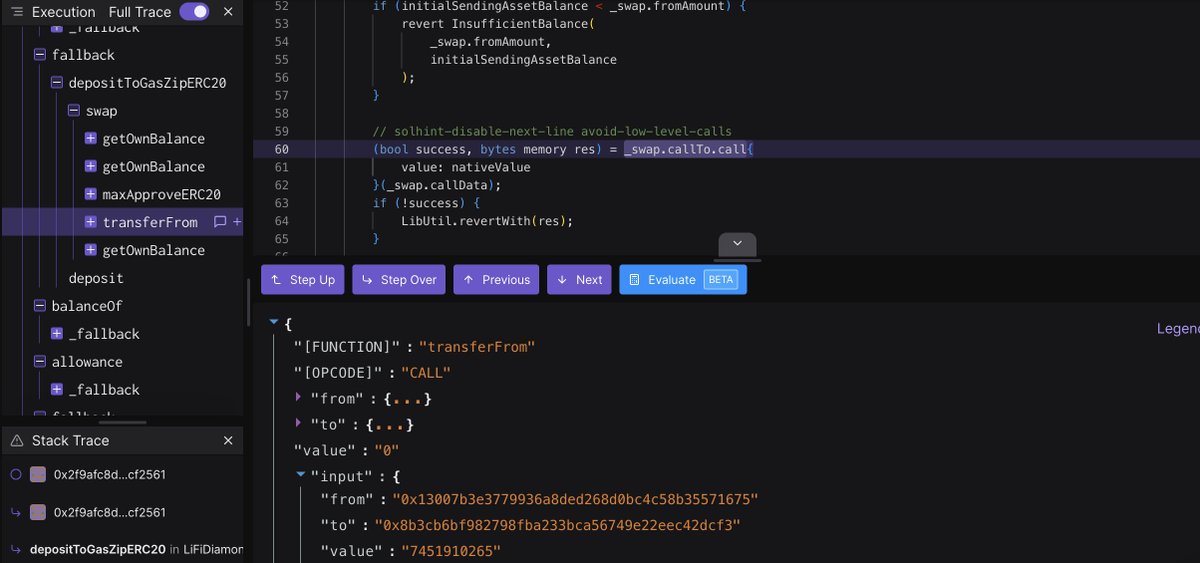
Our analysis reveals that the depositToGasZipERC20 function of the GasZipFacet contract in LiFiDiamond did not validate the LibSwap.SwapData parameter, leading to the attack. The call chain indicates that the attacker ultimately accessed the swap function within the LibSwap library. This function failed to verify the callTo parameter in _swap.callTo.call, enabling the attacker to invoke the transferFrom of the stablecoin contract and transfer assets from authorized users. Notably, the attacker had pre-deployed multiple contracts to circumvent the parameter checks within the swap function, allowing all functions in the attack chain to execute as intended.
We reiterate the importance of conducting comprehensive code security audits and regression testing for DeFi contract code before formal deployment on the blockchain. This ensures that all business logic is correctly implemented and that parameters are strictly verified to prevent such vulnerabilities.
https://t.co/btjI4ZkEaS
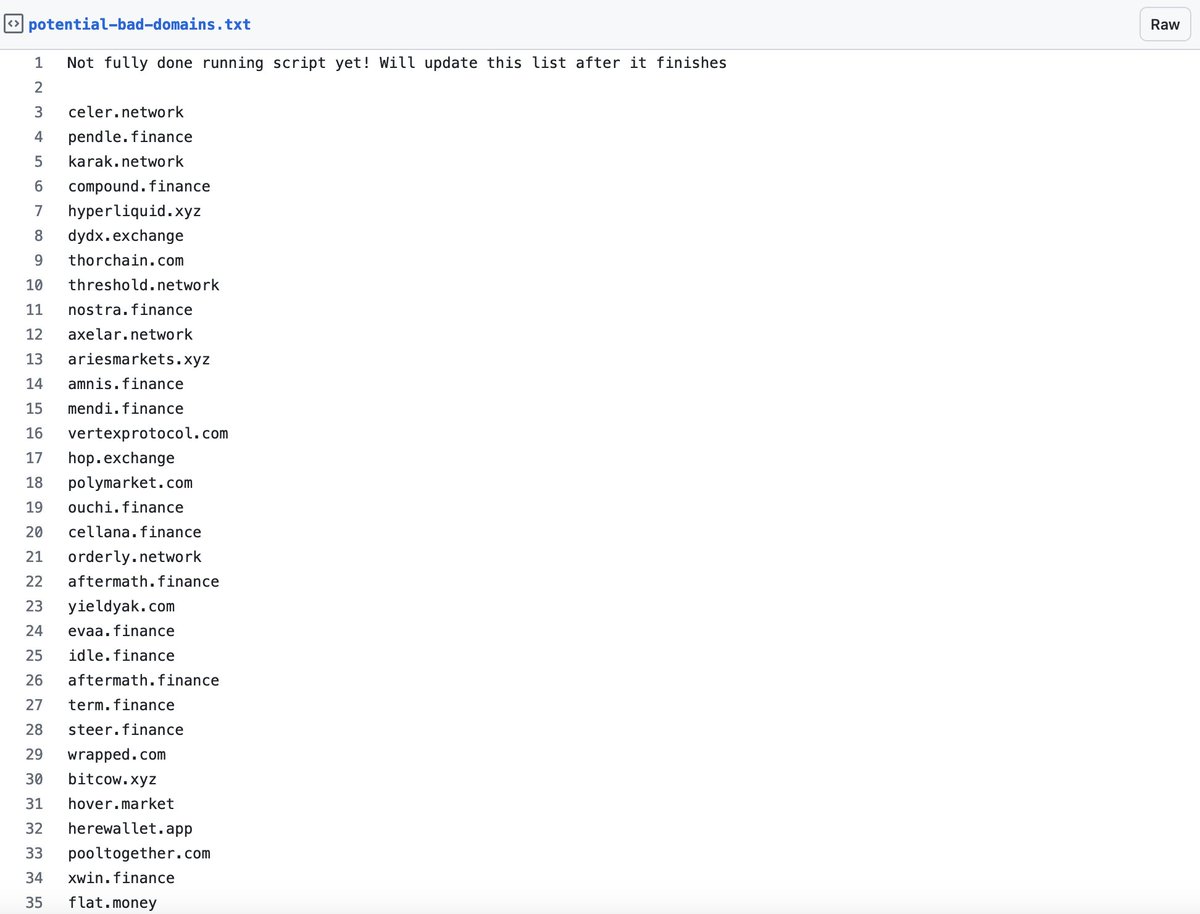
Based on community intelligence, several domains of crypto projects registered with Squarespace are at risk. This is a list of all domains registered with this registrar, which may also be at risk of being hacked. Exercise caution when interacting with domains on this list until an official statement is made.
https://t.co/u9Q35WNH4T