⚡️AI adoption is outpacing security.
Permiso delivers **complete visibility** into AI users, builders & agents with runtime intelligence that stops hidden threats.
Blog post here: https://t.co/sygmClA5kt
🎙️ In the premier episode of the Permiso Security Podcast, @TekDefense provides a detailed step by step breakdown #Salesloft breach. Listen (and watch) as Ian walks through
-A detailed timeline of the breach between June and August
-The challenges associated with Salesforce logging
-Detection tips to help protect and defend against SaaS supply chain attacks
You can access this episode here: https://t.co/yqYQleygcB
Big thanks to Alessandro Mascellino and @InfosecurityMag for covering our latest research on how threat actors are using Microsoft Teams for phishing campaigns.
https://t.co/oKAdyUBM7v
📣 New threat research from the P0 labs team!
Ever get a random “Help Desk” ping in Microsoft Teams? Attackers are exploiting those chats to gain remote access and deliver malware. In our latest research at Permiso Security, we uncover how:
→ Fake “Help Desk” accounts build trust
→ PowerShell payloads hide behind Teams chats
→ Indicators of compromise (IOCs) defenders should track
Read the full breakdown on the Permiso blog:
https://t.co/APBBfr55pz
#MicrosoftTeams #CyberSecurity #ThreatIntel #MalwareDelivery
We are excited to share our latest threat research, and along with it, another open-source tool! This time we're tackling the impact of leaked credentials on AWS infrastructure.
Our latest open-source project, #DetentionDodger, helps teams easily identify a list of all identities with leaked credentials, and their potential impact.
https://t.co/6wNEh1Q0Me
TOOL: Congrats to @AbianMorina on his 1st open-source tool release of #SkyScalpel last week at @sectorca in #Toronto#Canada 🇨🇦!
@permisosecurity is wrapping up 2024 with a few more tool releases, so be on the lookout!
Blog: https://t.co/L7XkMlkEoO
Tool: https://t.co/5aV836J5FY
This past weekend at @BSidesNYC, Ela Dogjani released Permiso’s latest open-source tool called #CloudTail, a tool designed to enhance the long-term retention and searchability of cloud logs in AWS and Azure, all without needing a SIEM!
Start tail-ing your cloud logs today with advanced filtering and feature-extraction capabilities and don’t get caught needing logs no longer accessible via the native cloud provider’s API.
https://t.co/vvYbNxob6G
"Permiso Security co-CEO @paulsnguyening said that regardless of who is responsible for identity security, the survey makes it clear they are likely being overwhelmed. A total of 28% of respondents, for example, noted they are managing more than 5,000 non-human identities created by machine and software in their IT environments, while 49% manage between 1,000-5,000 identities. Those identities, however, were not immaculately conceived, so there is an opportunity to not only determine how they were created but also govern them, he added."
Thanks for sitting down with Paul and writing about our State of Identity Security Survey, @mvizard!
https://t.co/duy0xr1nen
If you're at @sectorca, three Permiso team members will be speaking!
Up first, @gl4ssesbo1's talk, "Nebula - 3 years of kicking *aaS and taking usernames," will be on Wednesday at 10:05am-11:30am (Business Hall - Arsenal Station 2 ) and Thursday at 10:05am-11:30am (Business Hall - Arsenal Station 4).
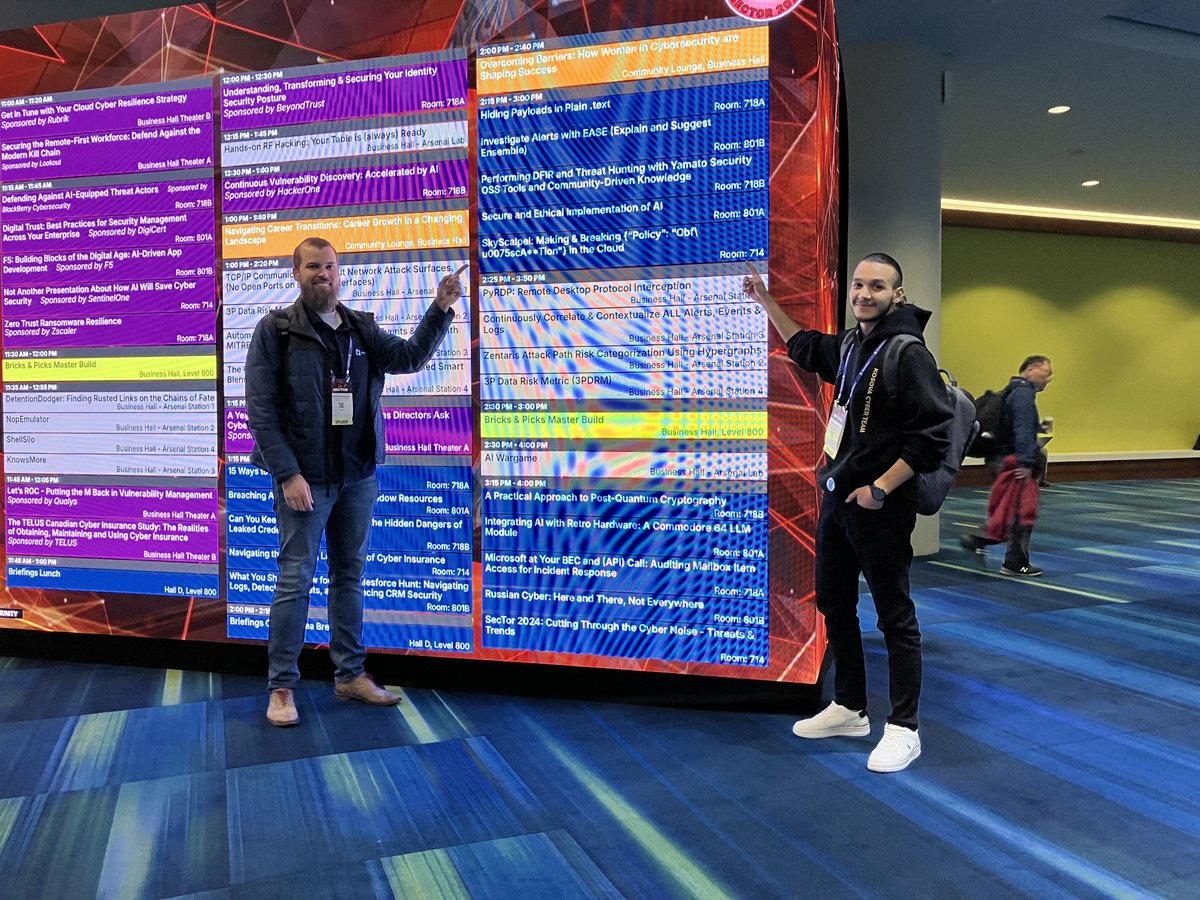
Bleon will also be presenting DetentionDodger: Finding Rusted Links on the Chains of Fate on Thursday at 11:35am-12:55pm (Business Hall - Arsenal Station 1) and Wednesday at 11:35am-12:55pm (Business Hall - Arsenal Station 3).
@danielhbohannon and @AbianMorina will be speaking tomorrow - stay tuned for more!
Permiso's own SVP of P0 Labs, @TekDefense, was quoted in Datadog's State of Cloud Security!
“Long-lived credentials like access keys continue to be targeted opportunistically by threat actors. Over the past six months, we’ve observed a notable shift in how attackers leverage these credentials: increasingly, they’ve turned their attention to large language models (LLMs) as their target. Commodity threat actors follow the money, and right now, hijacking LLM resources is where the opportunity lies.”
https://t.co/q7zDyBM7md
Great work from the team! Obfuscation is a trivial way to bypass exact match conditional rules on policies. If you have detections or scanner rules that look for these be aware! SkyScalpel helps identify and remove obfuscation in AWS policy objects.
Today we are excited to announce the release of SkyScalpel, an open-source tool that helps red and blue teamers understand how policies could be obfuscated by threat actors to avoid detection in an environment.
@danielhbohannon and @AbianMorina will be taking the stage today to showcase #SkyScalpel at SecTor at 2:15pm in Room 714!
https://t.co/NptJgNdt3x
Join us for a deep dive into LLM hijacking attacks we are seeing in the wild and how you can increase your ability to detect these Non-Human Identity-based attacks.
The P0 labs team have observed threat actors compromising non-human identities to hijack AI Infrastructure. We published research by Permiso's own @TekDefense, and in partnership with @briankrebs, shared our findings on the growing frequency of these attacks with the community.
On October 30, Ian will be providing a threat briefing to detail his research and answer your questions, as well as provide tips on how to protect your organization from LLMjacking.
https://t.co/keGhHn46rM
In her recent article in @DarkReading, Karen D. Schwartz sat down with Eric Tan to discuss how he secures @Flock_Safety's infrastructure and cloud environments with Permiso.
"If one of our cameras were to call home and eventually grant themselves access to our GitHub source code library, that would be really odd. Permiso would pick that up," Tan explains. "Similarly, if you had an employee who was a field technician, and that person's user account was granted additional permissions or elevated access within our Google Active Directory or Workspace environment, it would alert us and automatically quarantine them."
https://t.co/F1kGDZYOaa
Awesome work by @1aN0rmus and the Permiso team. The industry knew LLM hijacks were occurring, and now we know why. Stolen credentials are being used to rotate between compromised AWS environments to power illicit AI chatbots.
We are LIVE at @mWISEConference! Stop by booth 526 and visit @paulsnguyening, @PermisoRandall, @gl4ssesbo1 and team to learn how Permiso covers your *aaS in the cloud to defend against identity-based attacks.
We are excited to announce the launch of Azure Activity Log Axe, an open-source tool to simplify and improve the analysis of Azure activity logs! @purely_secure recently shared this tool at @BlueTeamCon and @fwdcloudsec over the last few months and it has been helping security teams navigate the complexities of #Azure logs.
https://t.co/sxtSI9IPKm