Detailed analysis of RomCom’s exploit, chaining the two vulnerabilities together, is available at https://t.co/qugbteKlcE. IoCs available from our GitHub: https://t.co/6HYOvMbeiv 7/7
#ESETresearch reveals the first Linux UEFI bootkit, Bootkitty. It disables kernel signature verification and preloads two ELFs unknown during our analysis. Also discovered, a possibly related unsigned LKM – both were uploaded to VT early this month. https://t.co/CZW6Mfm6bK 1/5
In our search for new forensic artifacts at @ExaTrack, we sometimes deep dive into Windows Internals.
This one is about COM and interacting with remote objects using a custom python LRPC Client.
STUBborn: Activate and call DCOM objects without proxy: https://t.co/FKPocJRN2Z
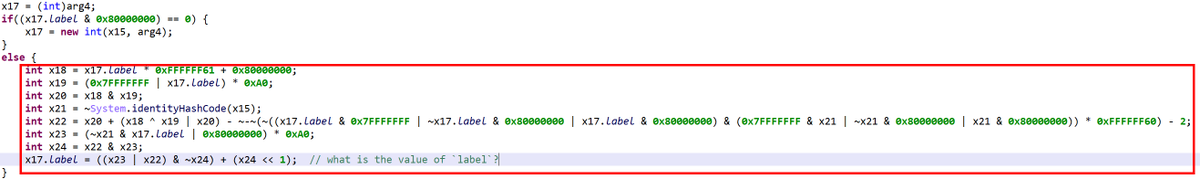
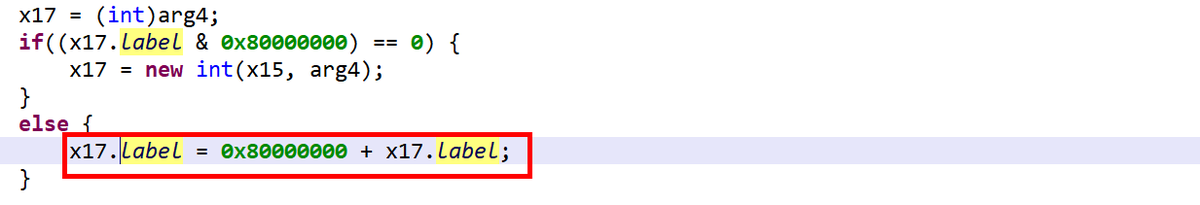
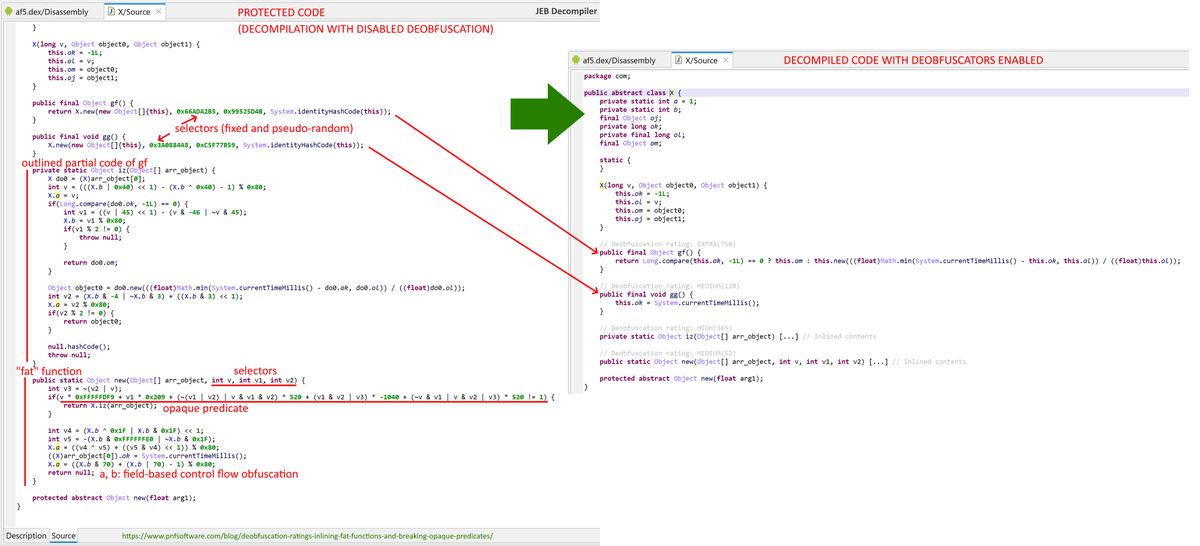
JEB 5.19 is available (https://t.co/vQsTSe1V0n). An interesting new feature in this release is a mixed boolean-arithmetic (MBA) expression simplifier/breaker. It gives interesting results on obfuscated code.
Have a look at the snippet in image 1, which is a decompilation with MBA as well as other bitwise simplifications disabled.
It is not easy to figure out that this code can be reduced to the MSB bit flip of its input, as seen in image 2. (The second input is pseudo-random and not used in the computation; its sole purpose is to obfuscate things further.)
This feature is enabled by default in JEB, but can be disabled by turning off the IR optimizers tagged as "DEOBFUSCATOR" (option: EnableDeobfuscatorOptimizers) #ReverseEngineering
🚀#Ph0wn2024 presents the Android Application Reversing workshop! Join Cedric Lucas to learn how Android apps are built, analyzed, and reverse-engineered using JEB(@jebdec ). Perfect for those diving into Android reverse engineering! 📱🔍
More info: https://t.co/8A3TaPnVZa
By analyzing thousands of samples, #ESETresearch has conducted a comprehensive technical analysis of the toolset the 🇷🇺Russia-aligned #Gamaredon#APTgroup used in 2022 and 2023 to spy on Ukraine🇺🇦 . https://t.co/Hc7ej57bO1 1/9
Hi there!
My latest article on the @harfanglab blog has just been published!
I'm talking about unpacking, XMRig, R77 and FIN7 (or not 🤓)
A special S/O to @splinter_code@JusticeRage and @securechicken
To check it out ➡️ https://t.co/Ko8zHvqQHE
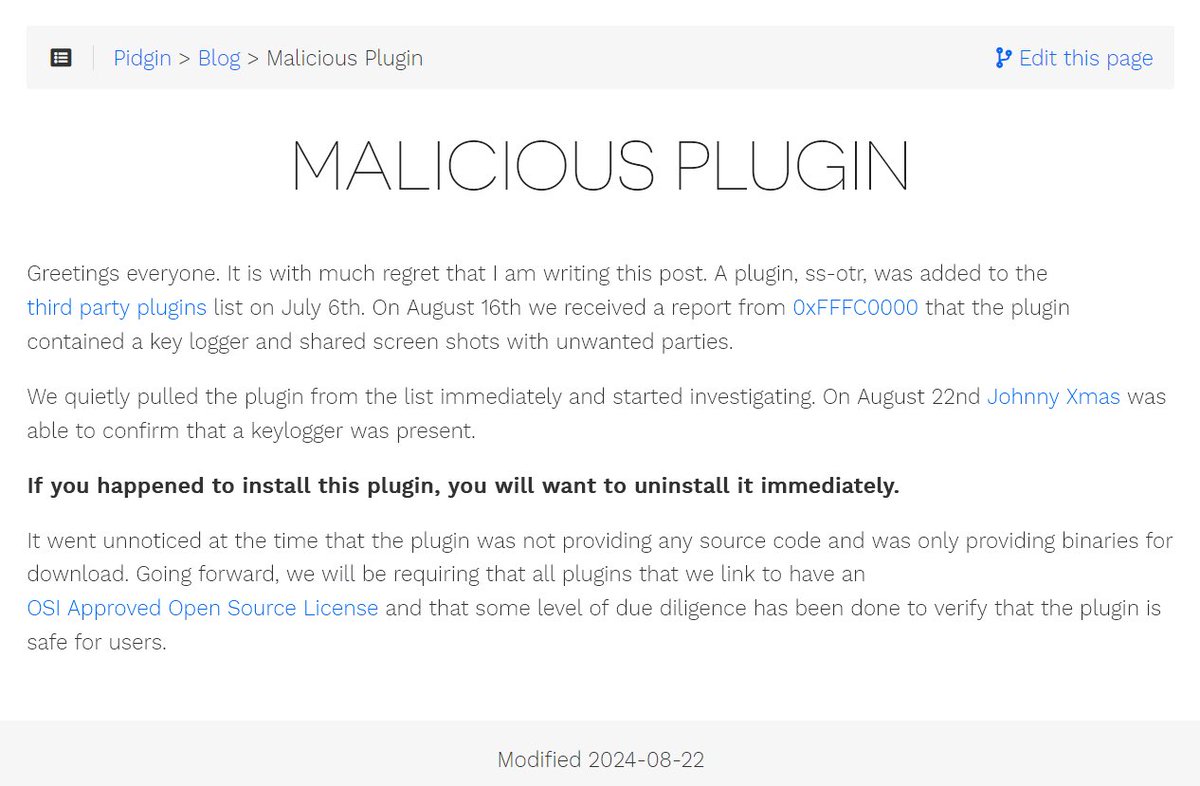
A few days ago, Pidgin Instant Messenger @impidgin published a notification about a malicious plugin (ScreenShareOTR) found in a third-party plugin list. #ESETResearch investigated these plugins and confirmed that they indeed contain malicious code, which downloads and executes binaries from attacker-controlled servers 1/7
https://t.co/QAZH83yx8U
The video from the 30 Years of Decompilation celebration at @QUT
is now live at https://t.co/i4dDuO6eSU. The celebration features discussions with Emeritus Professor John Gough, myself, Mike Van Emmerik, Anne Fitzgerald, and Trent Waddington. Thanks to Paul Roe for organising!
We are looking for a strategic threat intel analyst to join @ESETresearch. Interested in cyber-espionage and geopolitics? Apply!
https://t.co/6I2tK39tsv
#ESETresearch discovered a signed, vulnerable, ad-injecting driver from a mysterious Chinese company. This threat, which we dubbed HotPage, comes self-contained in an executable that installs its main driver and injects libraries into Chromium-based browsers. 1/7
After nearly 10 years of existence, years of use in production on 10k+ computers.
The new PythonForWindows release is 1.0.0 \o/
This release adds three important things: official python 3 support, full Unicode support for py2/py3 & CI testing on GitHub ! https://t.co/MZFd0SfPhE
A big honor to coauthor with @abc_sup and Gulshan the very first blog from Android Red Team on analysis and exploitation of CVE-2023-20938 in Android Binder driver at https://t.co/UF6nlbbzqT 🔥
The slide-deck presented at @offensive_con is available at https://t.co/CYzOLpWK0B
Our new APT activity report is available now, with updates from #ESET researchers on the various threat actors we track. Check it out! https://t.co/6Uco930Eiz
#Breaking#ESETresearch releases a paper about Ebury, among the most advanced server-side Linux malware, which was deployed to 400,000 servers over the course of 15 years, primarily for financial gain. @marc_etienne_ https://t.co/R5yFdlTjqS 1/8
In my experience the value of a degree is largely that it gives you a socially acceptable reason to ignore the real world and spend 4 years tinkering with computers. Ideally, do your degree at a uni *not* renowned for hard coursework (largely not useful, and eats your free time).