Thanks to Trump's tax cuts on investment, there are enormous write-offs to mining bitcoin.
There's only a couple months left in the tax year, to learn more check out this livestream from my sponsor @AbundantMines
American tech workers have been raising alarms about unqualified, lazy & incompetent Indians for decades now…
…. they call Americans stupid and racist and refuse to believe what we are telling them!
You clowns better get a grip on this because your own Government agencies are full of unqualified, lazy & incompetent Indians!!!
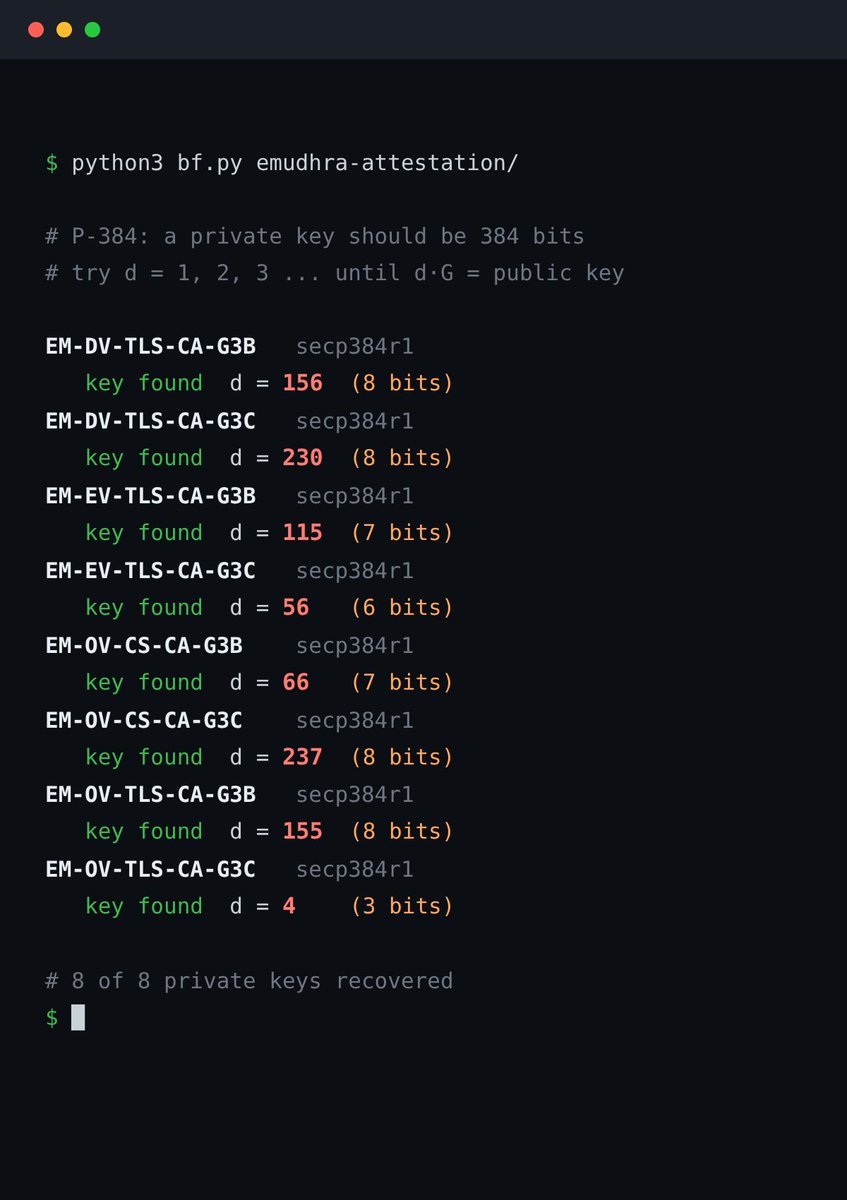
One safeguard key on a certificate was only the number 4…..
…the epitome of unqualified, lazy & incompetent Indians!!!
@POTUS@StephenM@WhiteHouse@HouseGOP@SenateGOP
EMPLOYERS FILED 77,010 CERTIFIED H-1B APPLICATIONS FOR CALIFORNIA IN NINE MONTHS
Here are the top 25 over the same period that California lost about 30,000 tech jobs. It now sits about 36,000 below pre-COVID.
In the same stretch, October 2025 to June 2026, employers got 77,010 H-1B labor applications certified for California worksites.
40,229 were computer jobs, and 34,061 were in Santa Clara County alone.
In the leadership team of eMudhra, out of 15 people, there is not a single Computer Science Engineer.
There is no CTO for the company. One of the VP is a mechanical Engineer.
Looking at the engineering team on LinkedIn, tells the true situation, which is even worse.
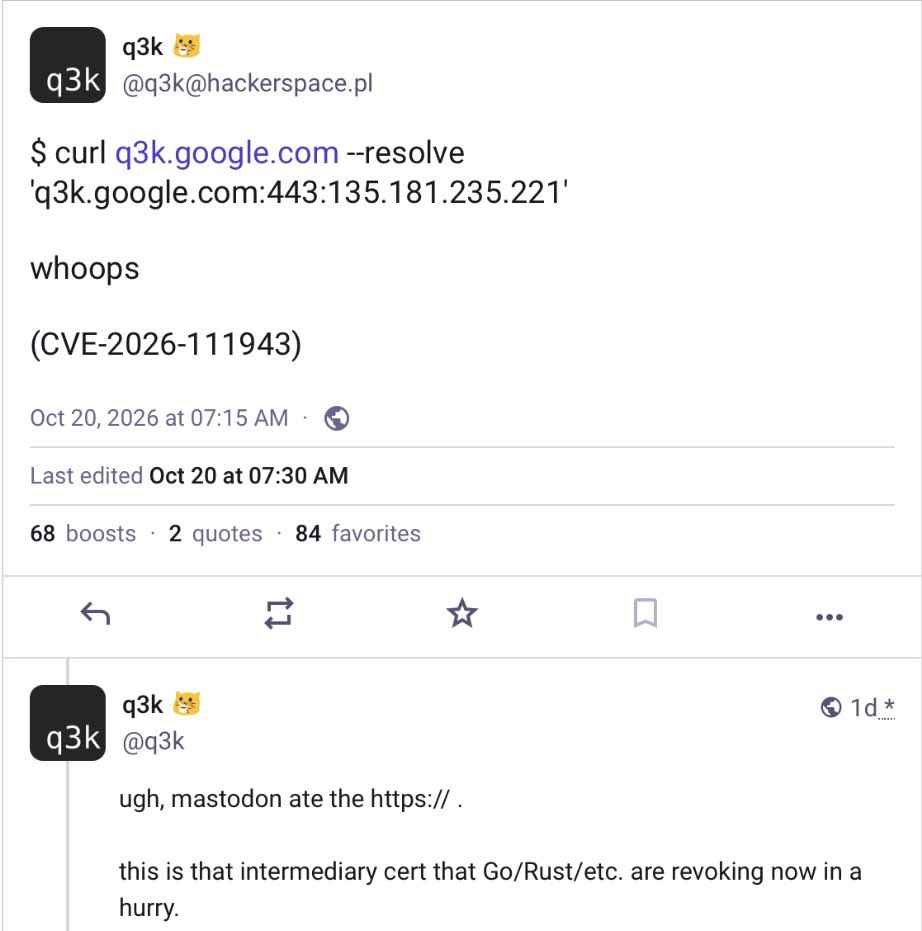
It's supposed to be hard to fake someone else's website. Thanks to the eMudhra fiasco for the last YEAR AND A HALF anyone that could guess the number 4 could fake being ANY (yes including .gov) website and your browser would believe them. India cert authority claims it was..
The rules are simply different in India. You will never see a video of the key ceremony nor the third party security audit. In India a family business can be a CA and entrusted with upholding the security of the internet without any meaningful standards whatsoever.
UPDATE: Specific mitigation guidance for the recently identified PHP critical vulnerabilities is now available. Secure your servers today. Guidance and technical steps here: https://t.co/nuXgQ10Fzc
‼️ BREAKING: The private keys of 8 certificates from Indian certificate authority eMudhra were compromised, Mozilla says. Firefox blocked them within 3 hours.
Each key should be a 116-digit number, but one was just 4.
Anyone can guess them and forge HTTPS certs for any website.
In April of 2025, eMudhra (an Indian Certificate Authority), published 8 intermediate CA keys which were so weak that a small child could guess the numbers in a few seconds.
One of the private keys was, literally, 4.
Just… 4.
This massive problem was not made public until October 17th of this year, when it was discovered by an anonymous guy on the Internet who goes only by “Wayne” (like “Cher”…. but… “Wayne”).
What this means in practical terms: It has been trivially simple, for the last year and a half, to create fake “secure” HTTPS certificates. (One person even created a fake HTTPS certificate for a https://t.co/9rSoW8koVR subdomain.)
It took Mozilla 3 days, after learning about this (from “Wayne”), before they updated their certificate list (which many open source projects — including curl and Python — rely upon).
As of this moment, many systems are still vulnerable (including macOS).
@ghidraninja How did this company get all the “trust certificate”
Contracts ? I have not even heard of them. Apparently their top team are all family members. Sounds like a family business.