Windows SMB Client Elevation of Privilege Vulnerability
CVSS Score: 8.8
Attack Vector: Network
Attack Complexity: Low
Privileges Required: Low
User Interaction: None
Do I have to say more?
https://t.co/SbFqsTWTSN
Yesterday, I chatted with @dannyvanzon, who pointed me to YubiEnroll, a CLI tool from Yubico for enrolling Yubikeys on behalf of your users. It works really neat and is easy to distribute and pre-configure.
Learn how: https://t.co/20YmMnM2JK
I respectfully disagree. You don’t need exceptional talent to prevail in the age of AI. Talent is rare and can’t be taught. But you can learn craftsmanship and careful oversight - essential skills that will set you apart
My thoughts on this:
1️⃣ https://t.co/2EaULpl5yE
2️⃣ https://t.co/f5DnhjcbEr
New changes in the authentication cycle for O365
If you are using evilginx in production to phish for O365 stop immediately as it will send the current domain (your domain) through an API request which will most likely result in a takedown
Phishers be ware
so hopefully that gives a quick demo that this tool after a few weeks of vibe coding has value! This is useful for:
> journalists
> reporters
> soc analysts
> IT staff
> Researchers
Loads more work is required!
https://t.co/bdJdwbawEE
This is legit. Might be the easiest DFIR automation workflow tool I've seen yet. Took ~2 minutes to setup with docker compose, and only seconds to generate some Hayabusa outputs.
I feel like I am only scratching the surface of what's possible, can't wait to dig in deeper🔥
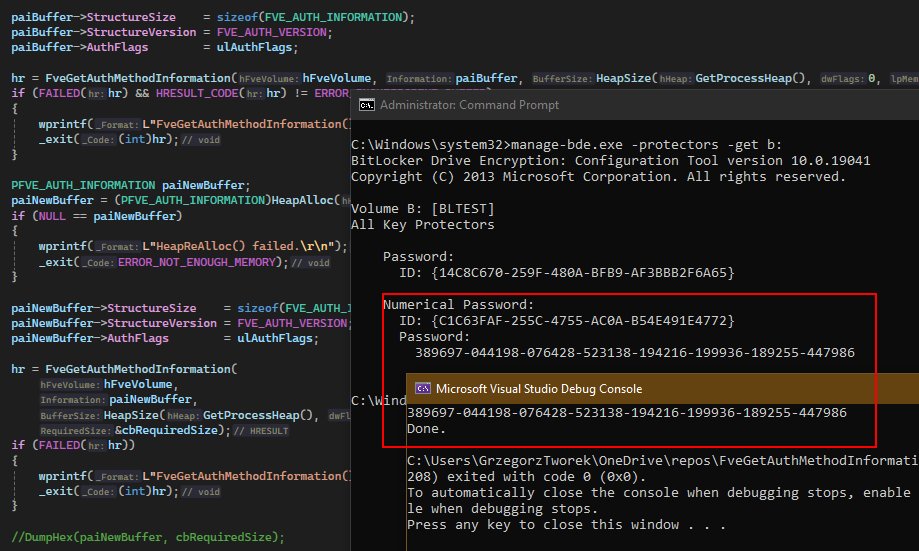
Finally had a moment to dig into unprivileged access to BitLocker Recovery Passwords. Here are some conclusions:
1️⃣ You can read RP using FveGetAuthMethodInformation() if you specify 0x00080006 as Flags. Flags value was the reason why I was able to write new RPs before I could read them ;)
2️⃣ This set of Flags returns E_ACCESSDENIED for fixed drives, works nicely with removable ones. Exactly as some of you suggested.
3️⃣ Other flags make FveGetAuthMethodInformation() return S_OK, but structure contains no usable information.
Of course, you must multiply each USHORT piece of RP by 11. 🙃
Have you gotten your Fido keys for break glass accounts for the October MFA requirements for Entra? Did you know Microsoft now has an official list of approved Attestation Entra Fido keys? Take a look!
https://t.co/InmmcBbxay
#microsoft365#powershell#systemadministrator
So @censysio just deployed the "suspicious-open-dir" label to their search engine.
So far it appears a game changer, giving very solid hit rates on finding malicious infrastructure.
So for today, this will be a thread documenting my findings using the new feature.
1/x
Hackers showed me (there's video) how a web bug let them locate, unlock, honk the horn, start ignition of any of millions Kias in seconds, just by reading a car's license plate.
They found similar bugs for a dozen carmakers over the last two years.
https://t.co/ww9SrV17Xk
Here is a 50-minute tutorial for those who want to build their first RAG application using open-source models.
This is very beginner-friendly.
As long as you are comfortable with Python, you should be able to get a ton from this.