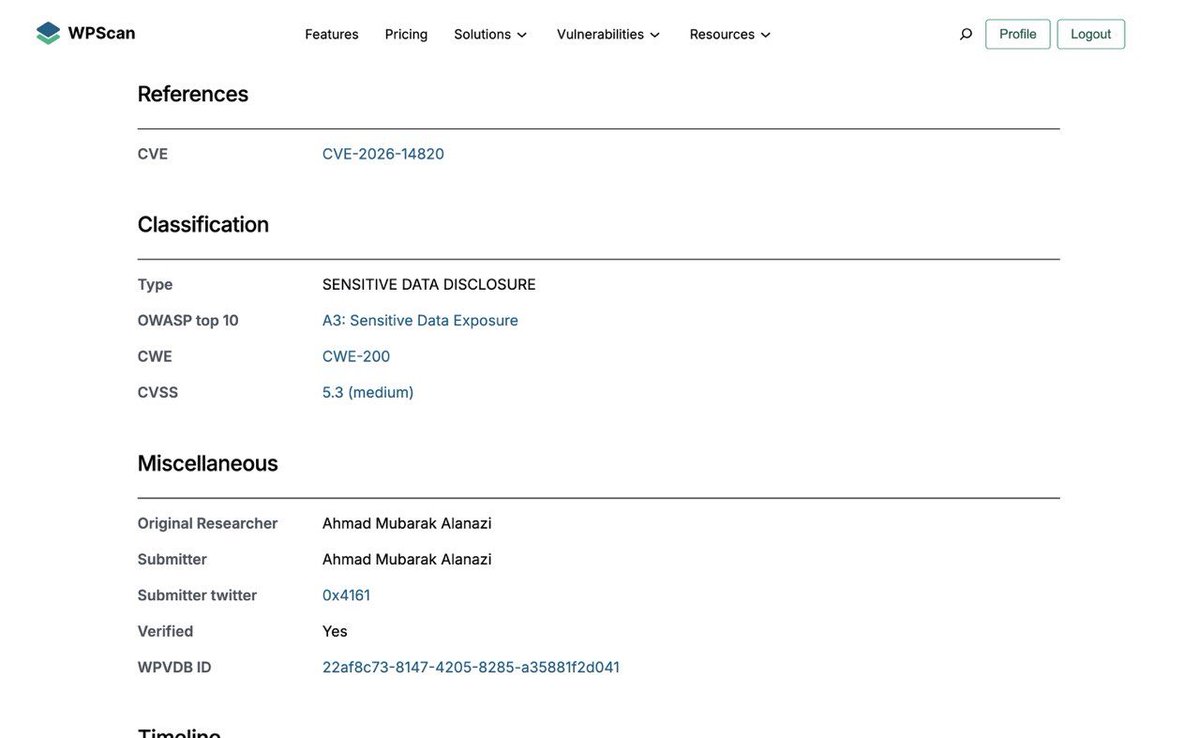
الحمدلله تم اعتماد الـ CVE 🎉
CVE-2026-14820 •
• الثغرة كانت في Wordpress plugin
• تصنيفها Medium
• الثغرة تسمح لأي شخص بدون Authentication إنه يجيب جميع المستخدمين الموجودين في الإضافة
https://t.co/RxK1XUFSy2
So here is new local privilege escalation zero-day I discovered, not patched yet too :).
In simple terms, if you have a service like RDP that exposes an RPC server, there many system services running as SYSTEM connect to it as RPC clients. If that service is turned off (RDP is off by default), it seems that any other process in Windows can expose the same RPC server using the same endpoint.
Now all the RPC calls from that SYSTEM processes will come to this fake server and If the process that deployed the server has SeImpersonatePrivilege, it can escalate to SYSTEM by impersonate the RPC client.
In the white paper below, I describe five exploit paths you can abuse.
However it's architecture problem and maybe there are more. It's Not A Potato
https://t.co/DOfRFgYqI9
الحمد لله حمدًا كثيرًا طيبًا مباركًا فيه، بعد قرابة سبعة أشهر من الدراسة أنهيت مسار الاكتف داريكتوري CAPE وهذي مجرد البداية باذن الله
I have just completed the Active Directory Penetration Tester path on HTB Academy! https://t.co/Oj6TFjZvMW #hackthebox#htbacademy#cybersecurity