Our FSE’23 work: adapting Property-based Testing to find logic bugs in mobile apps. We believe this might be the *right* way to find deep app logic bugs (w/o any false positives).
[PDF]: https://t.co/N5sLWjuyWu
[Tool]: https://t.co/RSS3GQqj3w
[More]: https://t.co/kkUvwjFHWv
Our another FSE’23 work: given a bug, if a fuzzer cannot find this bug, can we give some explanations?
We take the first step to explore this interesting problem in GUI fuzzing.
[PDF]: https://t.co/uHA1VFVfdZ
[Tool]: https://t.co/BBjehW3Kgv
[More]: https://t.co/kkUvwjFHWv
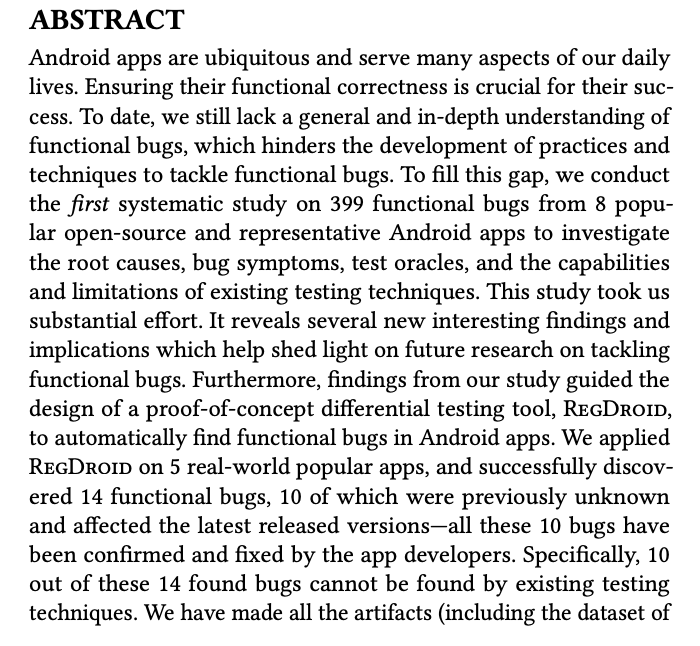
Tackling the oracle problem for testing mobile apps is difficult. Here is our ISSTA'23 work (*An Empirical Study of Functional Bugs in Android Apps*) to investigate this problem.
[PDF] https://t.co/qeiw6kLsET
[Data/Tool] https://t.co/9t1vi399BV
[More] https://t.co/kkUvwjFHWv
It was great fun giving this inaugural lecture. Also, what an incredible and surprising honor to have Prof. Niklaus Wirth in the audience! @CSatETH@ETH_en@ast_eth
We introduce “Intramorphic Testing”, a new, general methodology to the test oracle problem. Unlike metamorphic testing, it is a white-box technique. Core idea: modifications to a program can have an anticipated impact on its behavior that can be validated. https://t.co/b0fint1olY
The EuroLLVM 2022 program is out: https://t.co/WtkECpzqDA. A lot of interesting talks with a keynote by @theodortheod on "Finding Missed Optimizations Through the Lens of Dead Code Elimination"! @RiggerManuel@ast_eth@CSatETH@llvmorg
A brief summary of our Dagstuhl seminar "Ensuring the Reliability and Robustness of Database Management Systems" is now online. We have also been working on a proposal for a follow-up seminar, so fingers crossed! https://t.co/e2l30FX9BO
Software Engineering research! Which research topics are most popular? And how well do individual countries do in SE research? Let us give you some fresh data from @ICSEconf 2022.
Congrats to @theodortheod on receiving both a best paper award (for "Understanding and exploiting optimal function inlining" with @Tobias_Grosser) and a distinguished artifact award (for "Finding missed optimizations ..." with @RiggerManuel) at @ASPLOSConf!!! @ast_eth@CSatETH
As a software developer, you may be called upon to perform some of these tasks in your career.
How well a CS degree prepares you for these tasks (and whether it even should prepare you for these) is left as an exercise to the reader.
🧵
1/
The CASTLE research group (https://t.co/RoqUMZNSIs) at HKUST is looking for a postdoctoral fellow. We are an inclusive group and really want to see some new faces. 😄Please spread this to anyone who may be interested. More info at: https://t.co/73Xnj9GfMS
Fuzzing is an effective offensive security tool that defense has widely adopted. Unfortunately, it’s altogether insufficient for defense.
“I wrote fuzzers and found the vulns!” No. You didn’t. You found some vulns. If you’re in offense, your job is done. In defense it’s not.
1/
Get some tips for your faculty job search! @ggn_dp_sngh recently started at @IllinoisCS and talks to @RiggerManuel about interviewing in the US, and the importance of visibility, networking, and collaborating in the next GAP interview: https://t.co/eD0j5RToHc
@CSatETH@ETH_en
Happy Friday!
Part 3 of the Fuzzing101 with LibAFL series is up! This post covers fuzzing tcpdump, corpus and testcase minimization, coverage visualization, and a tiny bit of scapy for good measure, enjoy!
https://t.co/dPYYXtOjef
New @ETH_en faculty, @shw3ta_shinde, gives great advice on adapting to life as a professor, setting-up a group, fostering collaborations, and life in Zurich & ETH. Tune in to the next GAP interview for her insights!
https://t.co/U6n0VMPnGK
@RiggerManuel@CSatETH@zhendongsu