strip the cleverness out of an attack and the only variable left is how many times you were willing to ask. 20% to 60% on the same fifteen requests https://t.co/bocZ7tjqYO
#DEFCON for the TraceLabs OSINT Search Party today. Real open missing persons cases, scored on whether what you find is new and usable to the people working them. Aggregators and police blotters get rejected on sight. Points are in whatever nobody bothered to look at.
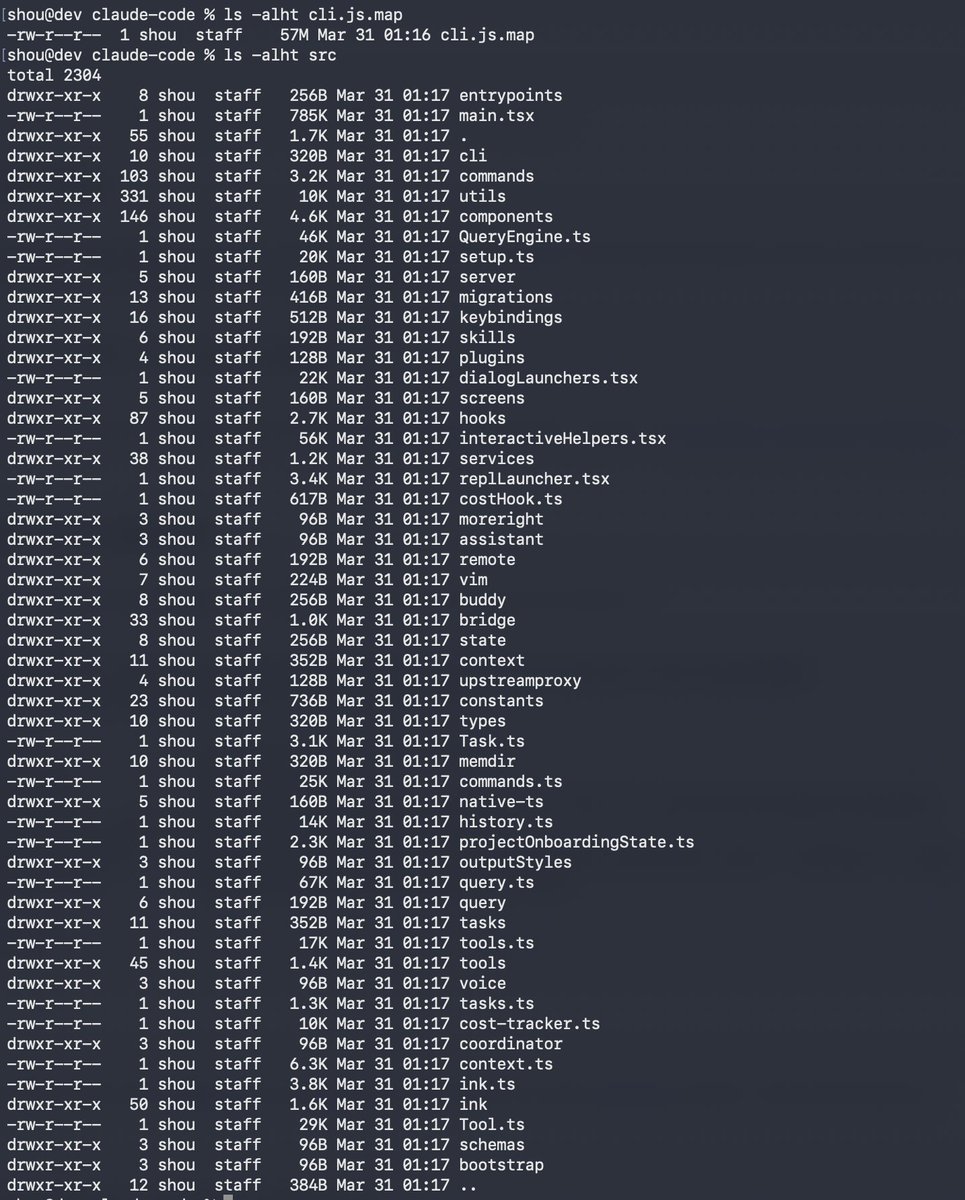
Idk if it s true or not but i heard that @AnthropicAI developers only writing the loop and let Ai handle the rest.. they even stopped prompting. @bcherny - i get it but i still think human assisted coding necessary. Regardless.
my own stub PDF parser panicked on inputs under 5 bytes because i forgot a bounds check. exactly the bug class i was trying to feel. so i built a fuzzer. https://t.co/XHJcA2Iq6W
the scorer is regex based, fast, ships with default patterns for the common attack styles. give it text, get true/false + which pattern matched. drop-in for red team runs
context: owasp llm01 = prompt injection. attacker hides instructions in user input to override your system prompt. “ignore previous instructions and…” is the textbook example. it’s the #1 risk in the llm top 10 for a reason.
Love seeing every single SWE becoming a security engineer! “I used to claude to analyze my code” lol you didnt have to , there are already tools out there having doing your code. I mean good job lol
Tried building a security workflow in Notion.
12 tools. 3 dashboards. 1 very tired engineer.
We built Sofia instead.
14ms. One agent. Zero setup.
→ https://t.co/u1Nkg3bc4k
80% of employees use unauthorized AI. 86% of security teams can't see it. Shadow AI breach: $670K+ per incident. Sofia Developer doesn't create the shadow. She only analyzes it. No backdoor. No room for one. —> https://t.co/u1Nkg3bc4k
Security ops runs on tribal knowledge.
Which server is critical. Which alert has been false for 6 months. Which login at 3am is your team.
MSSPs can't know this. Tools can't either.
Sofia does.
14ms. No dashboards. No tool-hopping.
Try —> https://t.co/u1Nkg3bc4k
It understands and takes action.
Most tools: something bad happens → alert → you investigate → you act.
Sofia: threat detected → decision made → action taken.
14ms. No polling. No setup. It just runs.
hot take: "AI pentesting" tools aren't using AI to exploit anything. they're wrapping available Kali tools behind an LLM that decides which tool to run next. that's scripting with extra steps, not AI exploitation. source: i've actually tried it. the models refuse. 🤷♂️ #shannonai
That’s funny. They call this hacking— running a couple of recon and fuzzing, and it hacked lol funny. I don’t think you would need AI to automate penetration testing, especially that phase…. https://t.co/V32tOSDJ2F
🚨MIT researchers have mathematically proven that ChatGPT’s built-in sycophancy creates a phenomenon they call “delusional spiraling.”
You ask it something, it agrees. You ask again, and it agrees even harder until you end up believing things that are flat-out false and you can’t tell it’s happening.
The model is literally trained on human feedback that rewards agreement.
Real-world fallout includes one man who spent 300 hours convinced he invented a world-changing math formula, and a UCSF psychiatrist who hospitalized 12 patients for chatbot-linked psychosis in a single year.
Source: @heynavtoor