🚨Cyber Alert‼️
🇺🇸USA - Crowdstrike
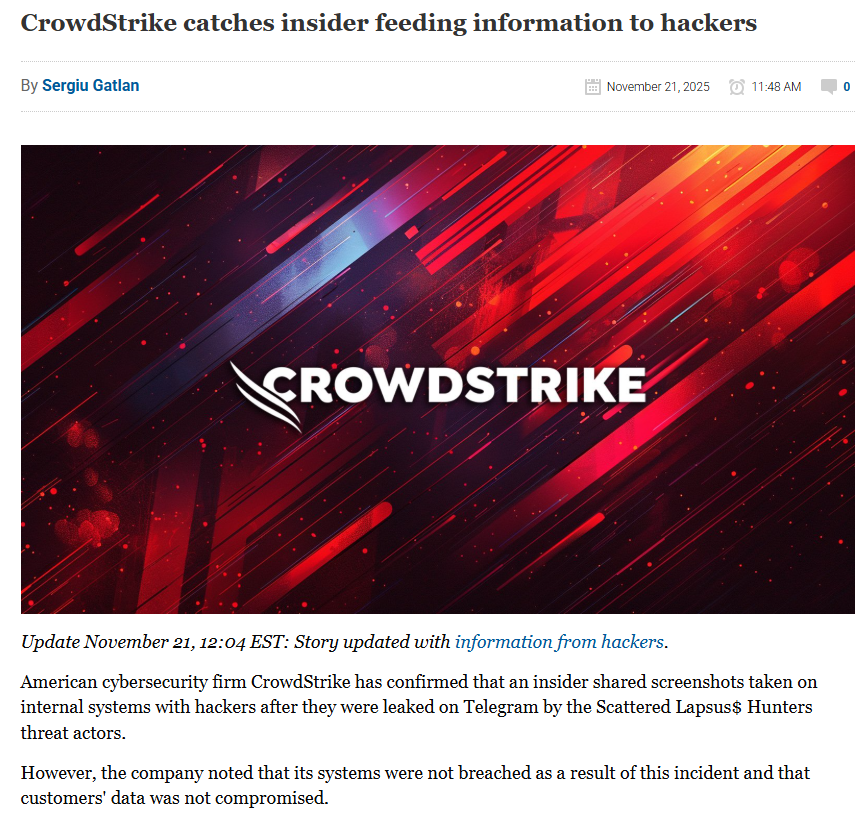
CrowdStrike has identified and terminated a malicious insider who leaked internal screenshots to hackers.
The incident came to light when screenshots of CrowdStrike’s systems appeared on Telegram, shared by threat actors from groups including ShinyHunters, Scattered Spider, and Lapsus$.
According to ShinyHunters, they paid the insider $25,000 to gain access to CrowdStrike's network and received SSO authentication cookies.
Status: Confirmed
Source: https://t.co/2Op2WexKap
🚨Cyber Alert ‼️
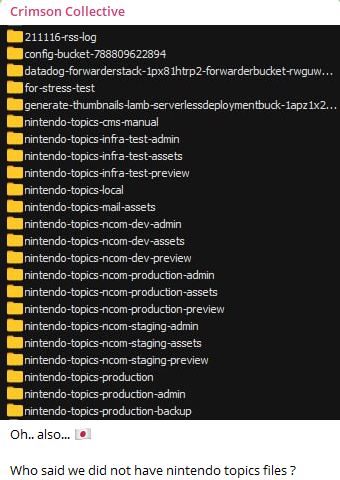
🇯🇵 Japan - Nintendo
Crimson Collective hacking group, known for the breach on Red Hat, now claims to have breached Nintendo.
Discover more at https://t.co/yiQ1nOhPjb
🚨Cyberattack Update‼️
🇯🇵 Japan - Asahi Group Holdings
Qilin ransomware group claims responsibility for a ransomware attack on Asahi Group Holdings.
The group also claims to have exfiltrated financial documents, budgets, contracts, employee personal data, and development plans.
The attack caused a global operational disruption, halting operations at 6 breweries and affecting 30 company sites.
Discover more at https://t.co/yiQ1nOhPjb
🔒 Secure Bits 💡
𝗬𝗼𝘂𝗿 𝗥𝗗𝗣 𝘀𝗲𝘀𝘀𝗶𝗼𝗻 𝗺𝗶𝗴𝗵𝘁 𝗹𝗲𝗮𝘃𝗲 𝗮 𝘃𝗶𝘀𝘂𝗮𝗹 𝘁𝗿𝗮𝗶𝗹…
Did you know that Remote Desktop Protocol (RDP) 𝗰𝗮𝗰𝗵𝗲𝘀 𝗳𝗿𝗮𝗴𝗺𝗲𝗻𝘁𝘀 of your screen on the client?
🖼️ These bitmap caches are stored locally to improve performance — but they 𝗰𝗮𝗻 𝗮𝗹𝘀𝗼 𝗿𝗲𝘃𝗲𝗮𝗹 𝘄𝗵𝗮𝘁 𝘄𝗮𝘀 𝘀𝗲𝗲𝗻 𝗱𝘂𝗿𝗶𝗻𝗴 𝘆𝗼𝘂𝗿 𝘀𝗲𝘀𝘀𝗶𝗼𝗻. For forensic investigators (or attackers), that means possible insight into screen content from previous RDP activity.
📁 𝗙𝗶𝗹𝗲 𝗹𝗼𝗰𝗮𝘁𝗶𝗼𝗻:
%UserProfile%\AppData\Local\Microsoft\Terminal Server Client\Cache\*.bin
🧰 𝗪𝗮𝗻𝘁 𝘁𝗼 𝗲𝘅𝘁𝗿𝗮𝗰𝘁 𝗮𝗻𝗱 𝗿𝗲𝗰𝗼𝗻𝘀𝘁𝗿𝘂𝗰𝘁 𝘁𝗵𝗲𝗺?
Check out: bmc-tools-py — it can turn the cache into a full image collage.
Did you know about this "feature"?
#CyberSecurity #Windows #Hacking #Forensics #RemoteDesktop #SecureBits #HorizonSecured @BlueTeamDave