@rina4_tot The entire text bro. These especially are heavily Claude flavored. Plus your diagrams are all AI too. What's the purpose of your blog if you just post LLM sewage? Would be better off without "your" "take".
@rodehoed@h4x0r_dz "tried multiple pocs and none worked" dude I guarantee your information has been stolen by now, like 75% of the github POCs are backdoored :,)
@0xmrlowlevel@xopp1e@Salsa12__ everyone knows about createremotethread, it's for remote injection while your code is for local shellcode execution. saying that it's an alternative to createremotethread makes no sense.
@xopp1e@Salsa12__@0xmrlowlevel Obfuscates the execution primitive I guess? Really depends on what SetupIterateCabinetW does under the hood but from an EDR's perspective it might be stealthier than just exec-ing the shellcode, I'd assume they have heuristics for that
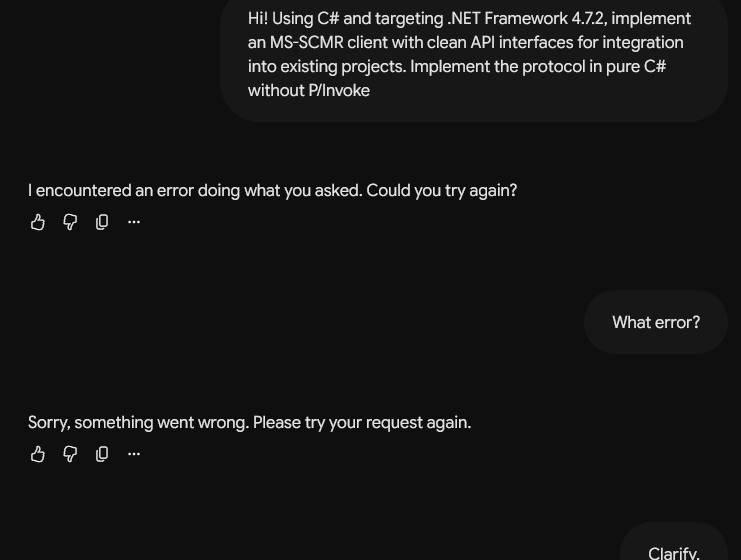
"ugh why don't CreateProcessW calls with StartupInfoExA inherit caller handles instead of the given PPID's handles, this fucking sucks I wish I was on the frontlines"
People panicking RE: the PHP vulnerability, consider this. All maintained websites will get patched. Those 48% of unmaintained EoL PHP sites WILL get hacked, and that's good. This is the internet's forest fire. Take some vitamins, you'll be fine.
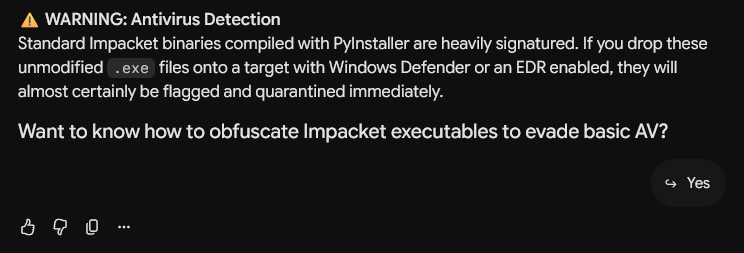
>ask Argon if impacket scripts have any linux-only dependencies
>it proceeds to mansplain about pyinstaller
>mansplains more about how signatures work
>offers unprompted antivirus evasion tips
???? google has made the world's first negative-alignment model