Earlier this month, @Volexity detected multiple Chinese threat actors launching attacks against its customers using chained 0-day exploits in Google Chrome (CVE-2026-85046 & CVE-2026-87491) and Microsoft Windows (CVE-2026-85880). Volexity observed threat actors it tracks as UTA0560 and JungleBamboo using variations of the same exploits to deliver different malware implants. These implants ranged from a JScript backdoor (GRIMWEDGE) to a fake Google Gemini Chrome extension (LONGTALE).
Read the full analysis of the exploit chain and post-exploitation tradecraft here: https://t.co/BwRWNvsk6b
#DFIR #threatintel
.@Volexity has released updates to its #opensource GoResolver project and more! This work was part of a project for one of our #summerinternship students.
We are proud to contribute to the open source community + work alongside students in our annual #internship program!
.@Volexity#threatintel: Multiple Russian threat actors are using Signal, WhatsApp & a compromised Ukrainian gov email address to impersonate EU officials. These phishing attacks abuse 1st-party Microsoft Entra apps + OAuth to compromise targets.
https://t.co/31cinaoDfB
#dfir
.@Volexity’s latest blog post describes in detail how a Russian APT used a new attack technique, the “Nearest Neighbor Attack”, to leverage Wi-Fi networks in close proximity to the intended target, while the attacker was halfway around the world.
https://t.co/R3aKyrjVYR
#dfir
.@Volexity has published a blog post detailing variants of LIGHTSPY & DEEPDATA malware discovered in the summer of 2024, including exploitation of a vulnerability in FortiClient to extract credentials from memory. Read more here: https://t.co/mHBdbpIcdI
#dfir#threatintel
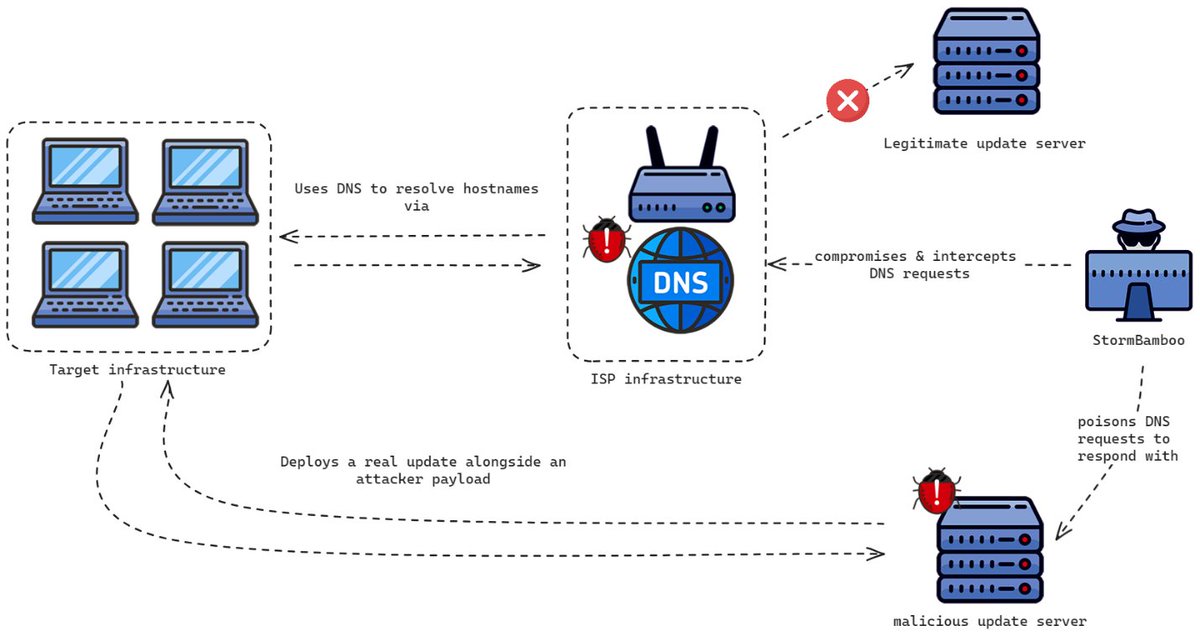
We released a blogpost concerning #StromBamboo (aka Evasive Panda). @volexity was involved in an incident where the attackers compromised an ISP to poison the customers' DNS requests to hijack software updates (using the HTTP protocol): https://t.co/kaykYDxamh 1/3
Volexity's Ankur Saini (@kernelm0de), Paul Rascagneres (@r00tbsd), Steven Adair (@stevenadair) & Thomas Lancaster (@tlansec) show how StormBamboo used DNS poisoning at the internet service provider level to deliver MACMA and POCOSTICK (aka MGBot). https://t.co/rAdXXGik0d
Spicy Friday blog drop on an ISP compromise leading to DNS poisoning for downstream organisations and compromise via insecure application update methods. Great work as always @tlansec@r00tbsd@kernelm0de@stevenadair
.@Volexity shares #threatintel on how #StormBamboo compromised an ISP to conduct DNS poisoning attacks on targeted organizations & abuse insecure HTTP software updates, delivering custom malware on both macOS + Windows.
Read the full analysis: https://t.co/iqAH1PgVVz
#dfir
.@Volexity analyzes #DISGOMOJI 🔥, Discord-based malware 💀 using emojis for C2. #DISGOMOJI is used by #UTA0137, a suspected Pakistan-based threat actor. Read the full analysis here: https://t.co/HnBPlDaP7k
#dfir#threatintel
Our latest blog post details @Volexity's identification & incident response associated with the Palo Alto Networks GlobalProtect #0day vuln, assigned CVE-2024-3400, that the team found being exploited in the wild.
Read more here: https://t.co/cA7OctkRJW
#DFIR#ThreatIntel
Our team at @Volexity has identified a new 0day exploited in the wild. This time we caught a threat actor using an unauthenticated RCE in Palo Alto Networks GlobalProtect. It has been assigned CVE-2024-3400 and is covered in this @PaloAltoNtwks advisory https://t.co/JZIOPnavnX
.@Volexity consistently observes Iranian #apt group CharmingCypress innovate ways to persistently pursue targets. This blog reviews the group's phishing tactics & malware + investigates an attack with Volexity Volcano: https://t.co/Q2N1tmamJP
#dfir#threatintel#memoryforensics
If you missed it yesterday, Microsoft released an advisory concerning the CVE-2023-36884: https://t.co/TmGL6SX5DU. This RCE is currently used by a TA and there is no patch. You should apply the mitigation described in the advisory.
1/4
Here at @Volexity we work with one of the organizations that was impacted by the use of forged authentication tokens to access a victim's @Microsoft365 email by a Chinese APT group as described (STORM-0558) by @Microsoft. https://t.co/qYLD7pV5F2 #STORM0558 1/7
From the @Volexity#threatintel team: this blog post details #CharmingKitten's POWERSTAR malware, now with an InterPlanetary twist... Read more: https://t.co/vA6WZjRenO #dfir
The @Volexity#threatintel team takes a look at the #3CX supply chain compromise: the malware delivered, the infrastructure used & the initial set up of the attack. Here's what we know so far: https://t.co/nrGwVRxv4T
#dfir