Cloudflare open-sourced the security audit skill that seeded its own vulnerability hunting harness. Your coding agent can now run it on your code.
How it works, in 6 phases:
→ maps your codebase
→ hunts for bugs area by area so nothing gets skipped
→ sends every finding to a fresh agent that didn't find it, to confirm it's real
→ writes structured results
→ verifies each record again, independently
→ writes the final report
You get a findings file split into confirmed, needs validation and rejected, so you fix the real problems first.
Install:
npx skills add https://t.co/ptOfJggqQB --skill security-audit
Then open your agent in your project and type: "security audit this codebase"
MIT licensed, 31.3K stars.
I made a short video that explains Entra app permissions and the part they played in the ConnectWise incident: how one app credential reached 173+ Microsoft 365 tenants with no password or MFA, and what to check today.
https://t.co/n5ewnUHA05
How Entra Global Secure Access Works in 30 Seconds
What does the Global Secure Access client actually do? Alex Pavlovsky (Microsoft Entra PM) explains.
Full episode https://t.co/gnvH23WorW
Want to get started with #ansible? In this video, I'll give you a simple introduction and show you how to create your very first playbook. https://t.co/Fqlpe4oRkL @ansible@RedHat
@IAMERICAbooted Thanks for the share Erica. This episode was almost like part two of the chat with you.
https://t.co/mcM8gaIAzc
Wow, I just realized that was a year ago. Crazy!
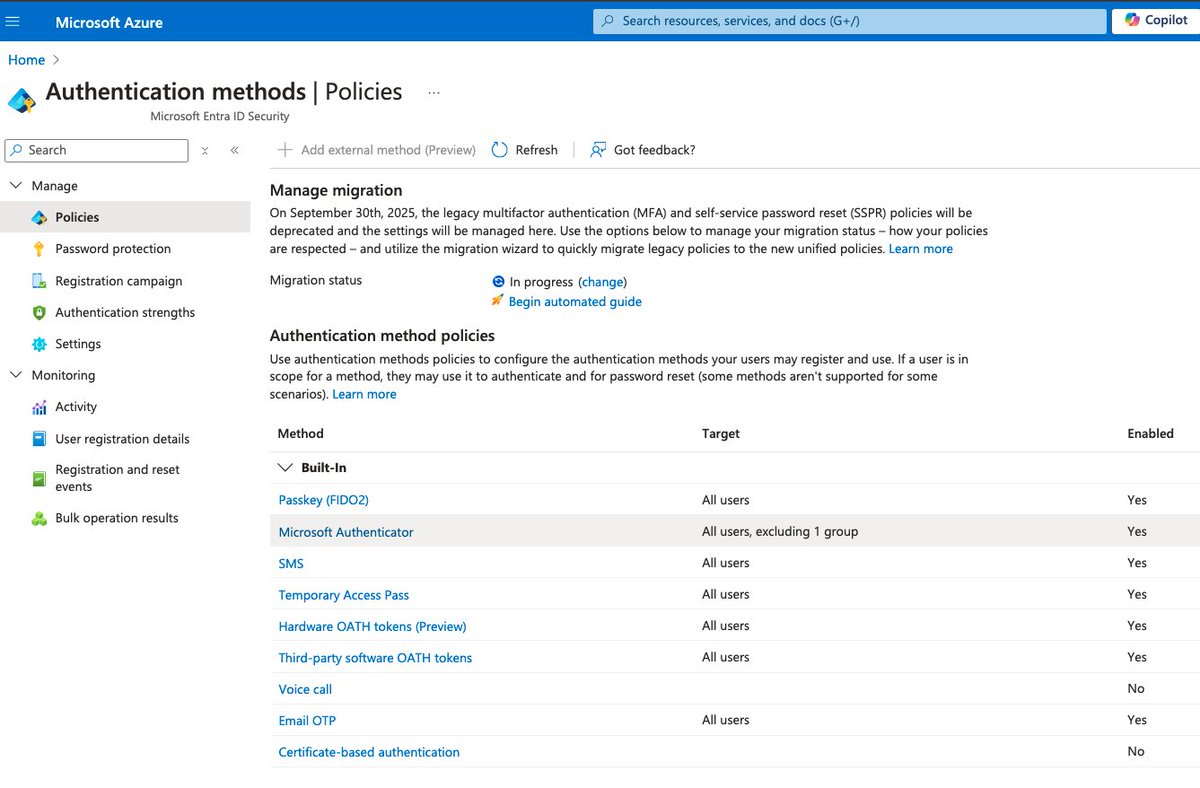
🔐 Ready to simplify identity security?
🚀 Migrate MFA & SSPR settings to the unified Authentication Methods Policy in Microsoft Entra ID for easier management, greater flexibility, and support for modern methods like passkeys.
Start here 👉 https://t.co/DKeAOIDXmk
#Azure #MicrosoftEntra #IdentitySecurity
If you're an IT admin and you’re after quick wins, low hanging fruit and security hygiene-related items, these are some great tools to start with. https://t.co/SvuNZuV7dX
Introducing Cloudflare OS: give every person in your org an agent and workspace that knows how your company works and can reach the systems they use to get their jobs done.
It's open source, and you can deploy it into your own Cloudflare account today.
https://t.co/qXgoC29ZiU
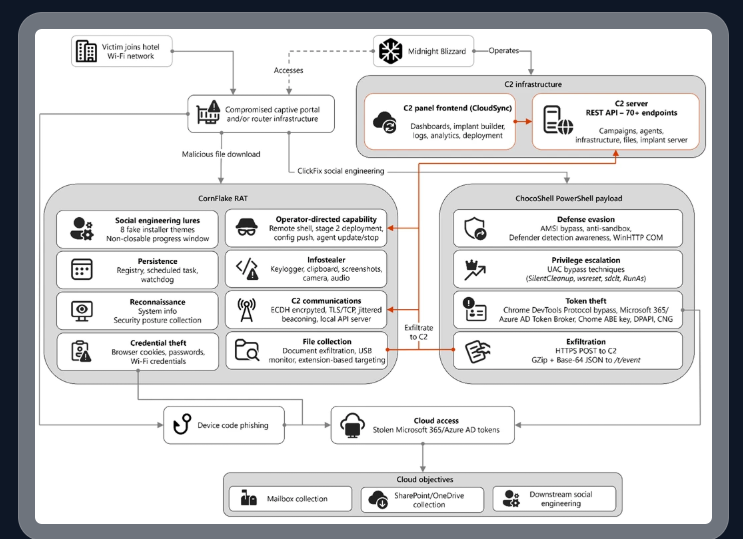
after Forti beleed i find it funny how people look a this and focus on the 'wireless' medium' part.
the routers were compromised....
can i explain a bit here about how that effects ethernet as well... but that's not important
can i explain that captive portals are phishing?
(obviously there's a small amount of difference)
the TA then did click fix (that's malware)
with a compromised router scenario the TA has options when they control DNS, DHCP and the ip- routing interfaces.... which mean this is shaping the network + phishing.... (so it gives the TA more options to phish (that depends on the device config) but the only major difference here is that the setting/context is captive portal UX.
they are tricking people into running commands....
there are key points:
>>> A VPN cannot protect the portal interaction. By definition you have to complete captive portal auth before the tunnel comes up. The attack surface is the pre-tunnel window. Anyone briefing "just use the corporate VPN" has not thought it through.
>>> Nothing about the ClickFix chain requires Wi-Fi. Same payload, same UAC bypasses, same ChromeKatz module, delivered by malvertising or SEO poisoning tomorrow.
>>> Device code phishing works from any network, including a 5G hotspot on a corporate laptop in the office.
so the 'don't use public wifi crowd' or 'always use a vpn crowd' here might not make sense.
1) in the real world if you are at a conference etc. the cell signal is usually terrible
2) in the UK the cell signal is terrible everywhere anyway
3) none of the attacks here are limited to firewall compromise (AITM, device code , clickfix)
4) if these work here the work aywhere....
5) a vpn doesn't stop a captive portal attack
there's IOCs here which are external DNS
the whole: use private comms is great on paper and if u have signal then great. but it's like telling people to not use public roads.
I'll see if we can dig more into the malware side to see if that ran from userland but also the listed behaviors .... would they have been blocked by an EDR?
this malware is also for windows clients.
this again goes back to mrr3b00t's mum in starbucks in her iphone doesn't care so much about this...
more to follow...