@userlolxxl@CanadianPro2@UCPGoA23@medsci_yb3r@TeamNAIT@skocherhan Physical entities are everything that exists within space-time, possesses mass and energy, and can interact with its surroundings. Non-material entities lack mass, do not occupy space, and are not composed of atoms or energy in the physical sense.
🚨 Ransom group "Panzer" publishes "Grupa ABS" - Poland 🇵🇱
📍 Location: Częstochowa, Poland
🏢 Industry: Information Technology Services & Software Development
🔗 Website: N/A
Grupa ABS is a Polish tech company founded in 2010, providing IT services and custom software development from its HQ in Częstochowa. Serving business clients across Poland, the firm reported PLN 24.8M in 2024 revenue, reflecting a solid presence in the national IT market.
Security Threat Update for Alberta: Something is Broken
Yesterday afternoon onwards, after contacting @RCMPAlberta (Leduc Detachment) to follow up on a case (i.e. w. Officers & w. Victim Services) to ask where they would like their HR files to go & to warn of impending threats (was ultimately not provided guidance or help by the admin).
A Threat Actor affiliated w. #ShinyHunters (i.e. the messy SLSH version) went on a tear, & spread an ‘upgraded & updated’ version of BlueLeaks 2.0 (forked) across the web.
This means: @youralberta@ualberta@AHS_media AND Officer Data ( @RCMPAlberta@Edmontonpolice@CalgaryPolice@CrimeStoppersAB ) PII/PHI is currently circulating ‘in the wild’. Assessment and investigation of spread has not been conducted. @RCMPAlberta has been filled in via dm/
This is a Catastrophic and Serious risk to: Officers, those REPORTING and/or providing tips, and to VICTIMS.
If you are an officer of the law in #Alberta - please take extra care of yourselves and those you protect.
FFSS People
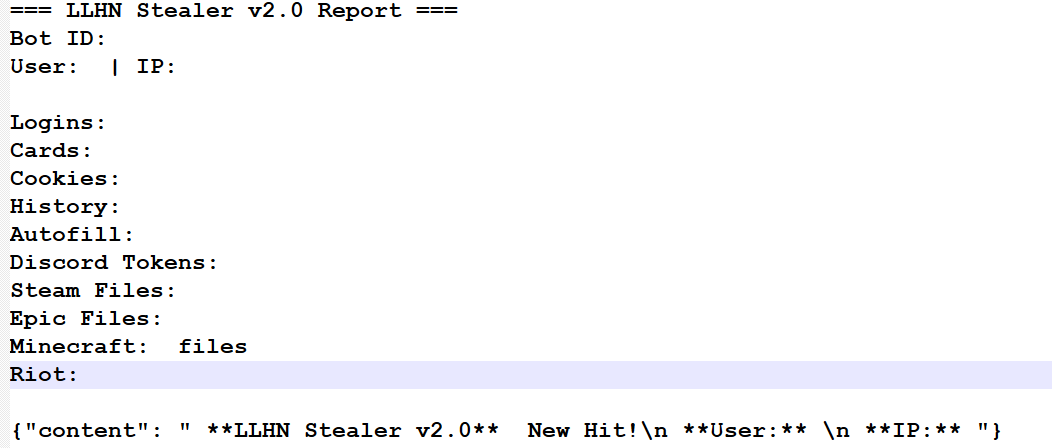
Observed LLHN Stealer v2.0, advertised on a cybercrime forum, with a panel supporting browser, Discord, Steam and wallet data collection.
IOC:
• ad781dcd83ccbc4f5438525b4cd17c86
Reported capabilities include browser credential/cookie theft, Discord/Steam/Riot tokens, MetaMask data, screenshots, clipboard collection, persistence and exfiltration via Telegram, Discord webhooks and file-sharing services.
#ThreatIntel #IOC #Stealer #DFIR