DNS is the layer an operator reads before they touch the app. https://t.co/wA8QhsIVSR scans from the outside, no zone file and no creds, the same vantage as recon: SPF/DMARC, DNSSEC, lame NS, takeover, suspicious TXT, DDNS, parked domains, registrant exposure.
Built by Esteban Borges (@tuitesteban), Octopus at @Huntio and founder of @dnsaudit. Hunt Intelligence hunts C2 and netblocks, and the scanner asks the question he already asks of a domain: who owns it, is the delegation alive, what is dangling.
Three intelligence reads. Lame delegation is a hijack primitive: parent still delegates, child NS stopped answering. Mail policy is campaign prep: DMARC at p=none and MX on a parked domain mean the brand is spoofable before the first lure. TXT and DDNS are pivots, not verdicts: v1.2 claimed 56 TXT patterns and 275 DDNS suffixes. Correlate with age, TLD, and registrar lock. Do not auto-block.
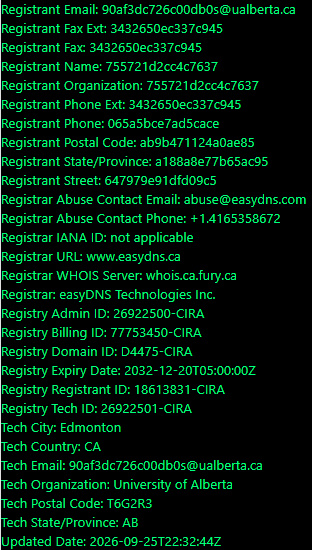
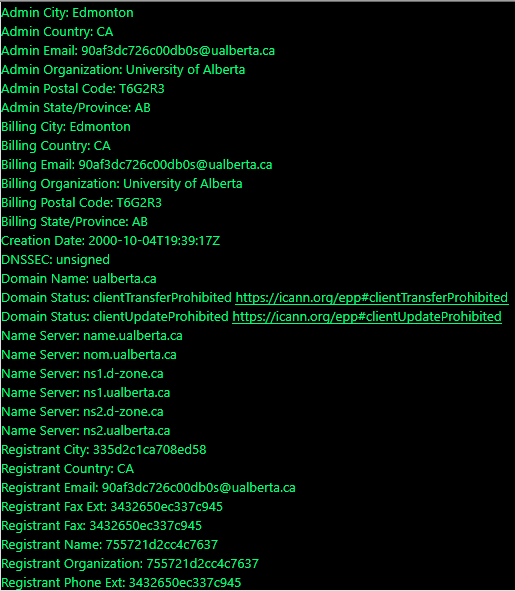
v1.3 adds a Domain Exposure Engine, 26 checks and a separate score: expiry, redemption, transfer, age, DNSSEC, WHOIS privacy. WhoisXML API puts ownership next to the finding. JSON and pip install dnsaudit feed SOAR. It does not replace passive DNS or a sandbox. On their numbers, ~20.9k of ~23.6k scanned domains had a critical finding.
https://t.co/58yqw9Ot5S
Attackers are encrypting payloads to sneak malware past Linux defenses. Spoiler: it doesn't work.Sandfly Founder, @CraigHRowland breaks down the Linux malware trends we're seeing on @DestLinuxPod 👇
@TeamNAIT@medsci_yb3r we did a thing = took initiative.
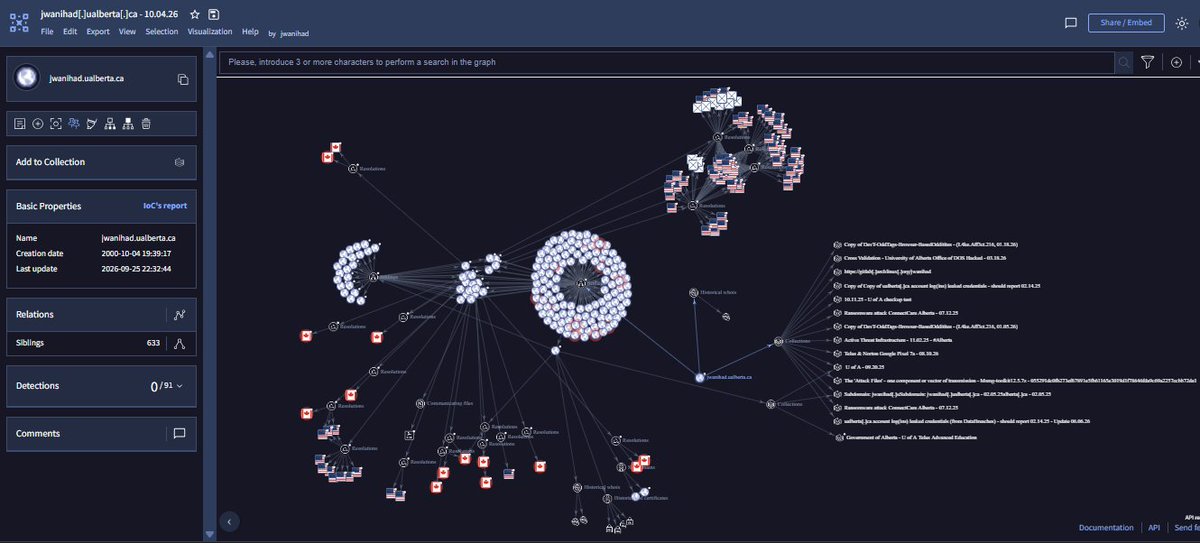
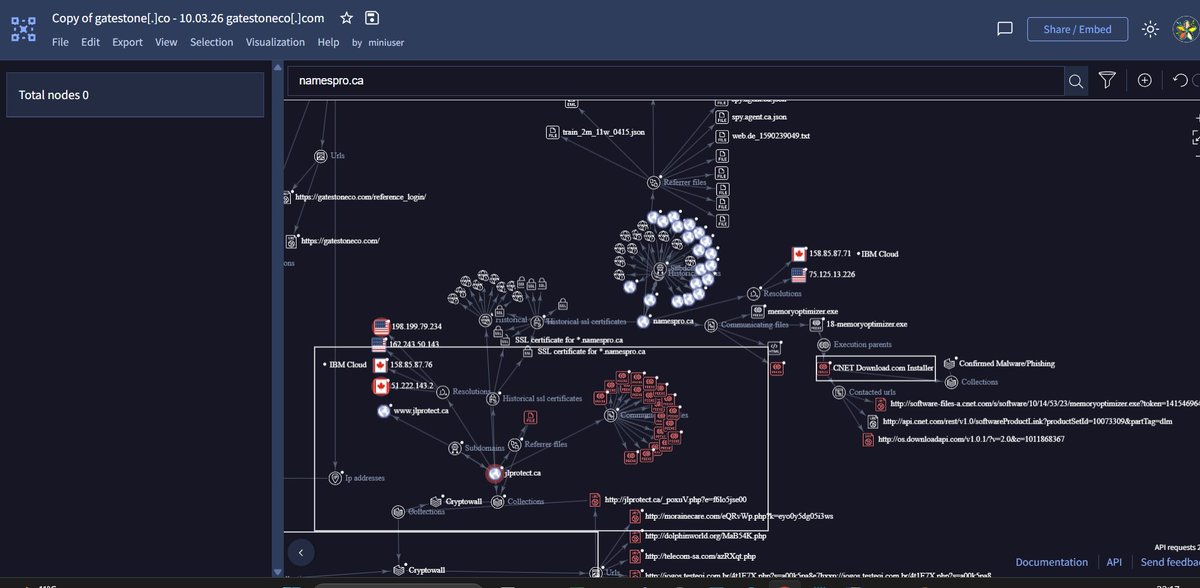
A "DEMONSTRATION" (passive collection).
Let us know if Officer Alex Wheadon of the RCMP contacts you.
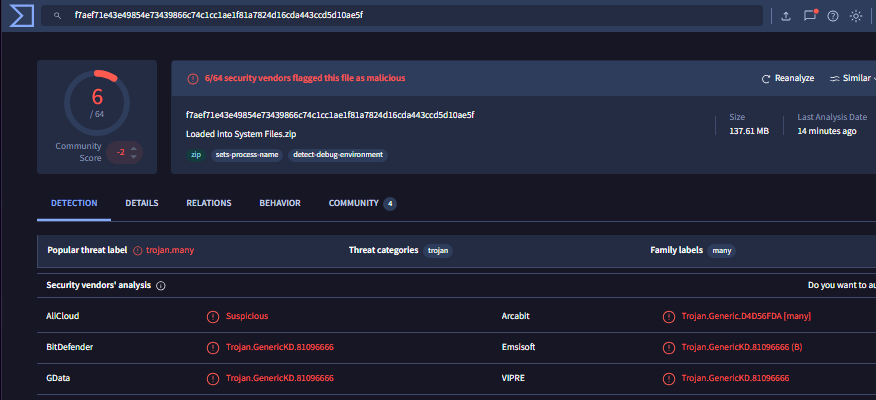
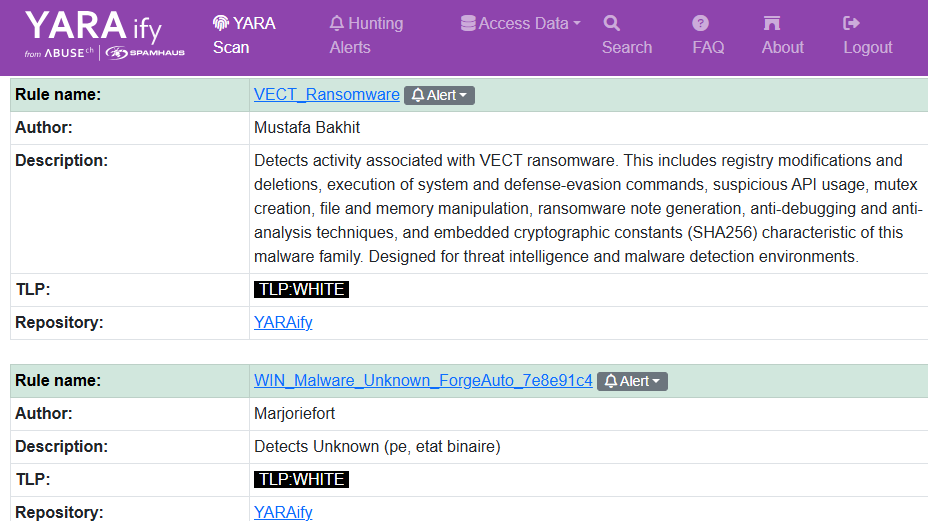
In the above image #YARA scan of #VECT Ransomware.
Case no. 2026972763
@MondoABx@Furnace_roofho@gilmcgowan
You guys are aware we have literally thousands of these lists…
->> We also have copies of your stolen #Healthcare #Government #Education information.
->> So does the UCP (but not #UAlberta, @youralberta, @AHS_Media).
->> Worse: So do cybercriminals. Cold. Heartless. Undetectable.
->> The Problems & Source? We cannot close on our own nor stop.
- - -
One quick fix? We do come with solutions…What would be helpful is:
1) a report to be followed up on by the RCMP (case no. 2026972763)
2) Sharing and/or reporting this issue (it runs deep).
3) a few hours of help from some of our #Government Leadership
Such as:
@albertaNDP@NathanIpYEG@jodi_stonehouse@JodiCalahoo@JanisIrwin@mlasinclair@PeterGuthrie99@nenshi
For so many people what care about ‘big things’ like the current state of #Alberta, the visibility of 3/4 teams here in #YEG is nearly non-existent.
We have identified problems & solutions.
Solutions will not be rolled out w/o help/resourcs/etc.
We are all running ‘on fumes’. @UCPGoA23@TeamNAIT are feeling the frustration.
Fun fact: There is something called being ‘perma - #Hacked’
Much of #Alberta is nearing that point - if that is any incentive.
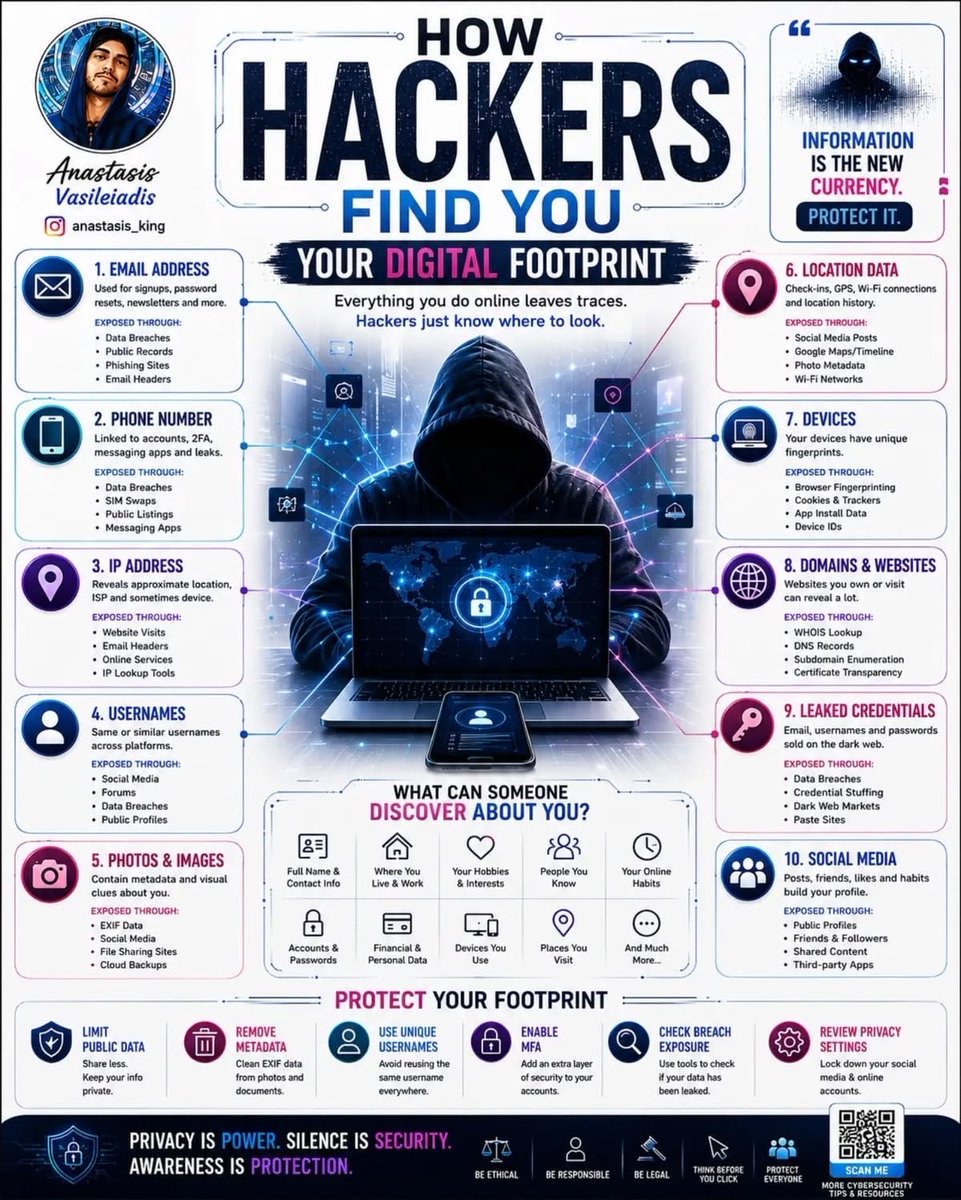
🔓 https://t.co/ZOzSES4XdY checks authorised emails, usernames, phones or domains against indexed breach data, returning matching records and exposed data classes. Defensive breach-exposure monitoring.
Try it out: https://t.co/CLTpMvTdm3