Crypto AML checks from 3 providers — Crystal, VALEGA, BitOK. Risk score, source of funds, sanctions. Telegram bot & KYT API for business. First check free.
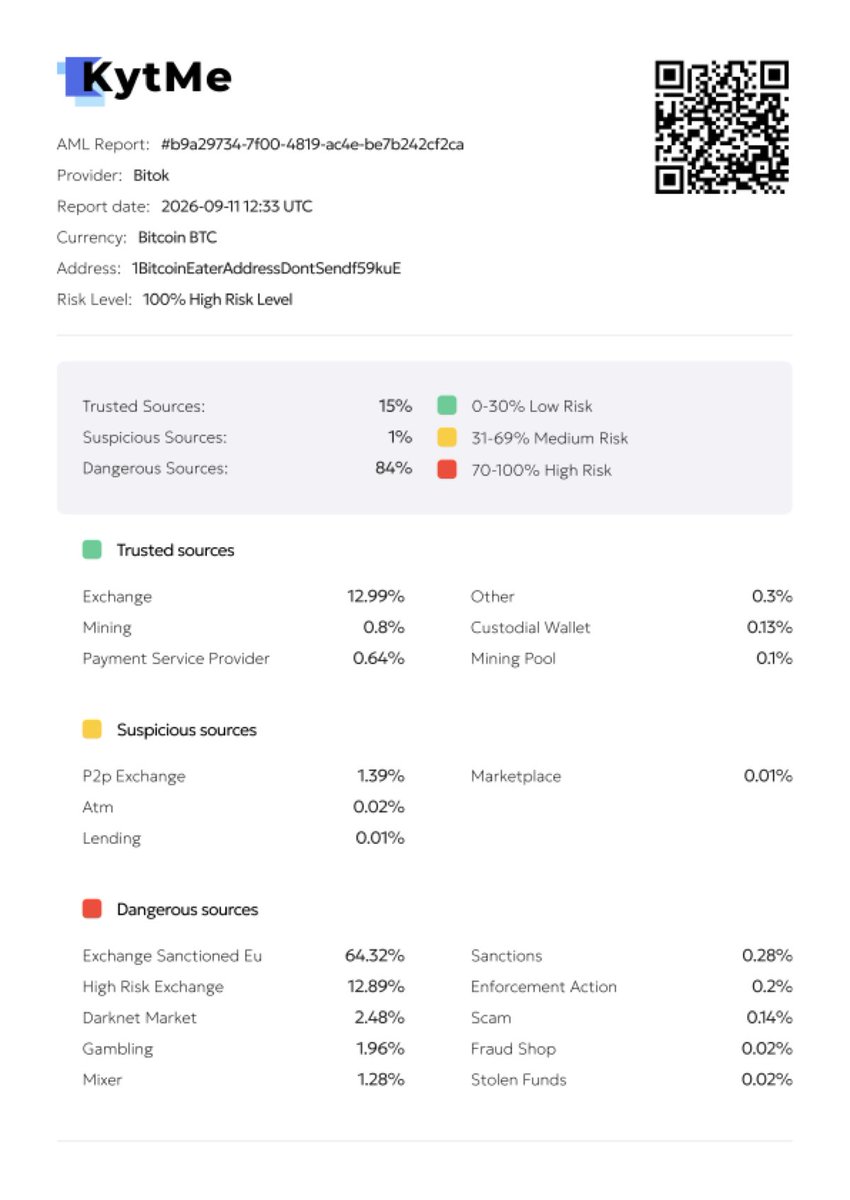
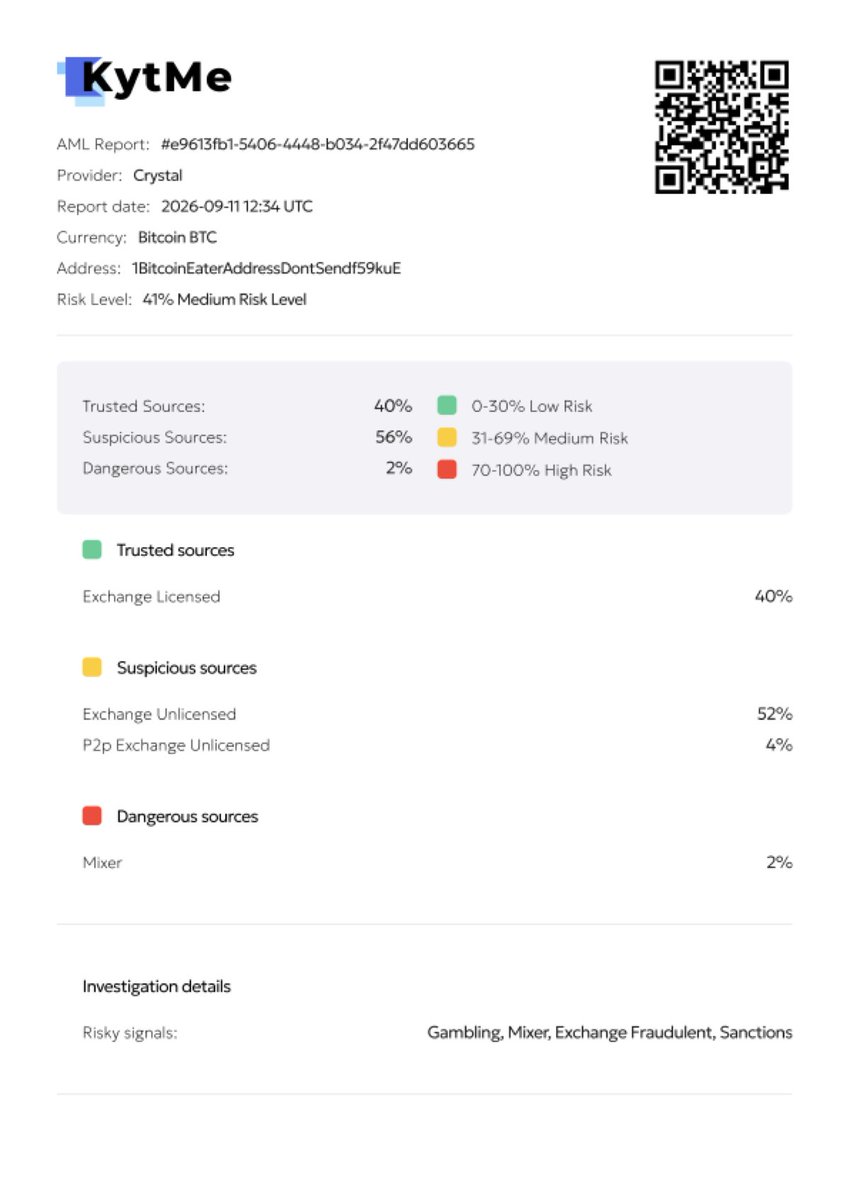
We ran the famous BTC burn address through all 3 AML providers on Kytme:
🔴 BitOK — 100% high risk
🔴 VALEGA — 85% high risk
🟡 Crystal — 41% medium risk
Same address, three verdicts. This is why you compare before you trade.
First check free → https://t.co/DQOCFjjopB
5/5 Attribution is not settled.
Gracy Chen called North Korean involvement "very likely", citing IP addresses tied to VPN services associated with a North Korean group. Fund tracing found overlaps with the laundering infrastructure used after the Bybit and AFX Bridge thefts — a network not previously linked to other groups, which points to TraderTraitor.
If the attribution holds, 2026 becomes the second-largest year on record for thefts attributed to North Korea, above $1B. So far about $690M in 2026 is attributed to such attacks, mostly Drift Protocol and KelpDAO.
The full breakdown:
https://t.co/BPfvP2tYo9
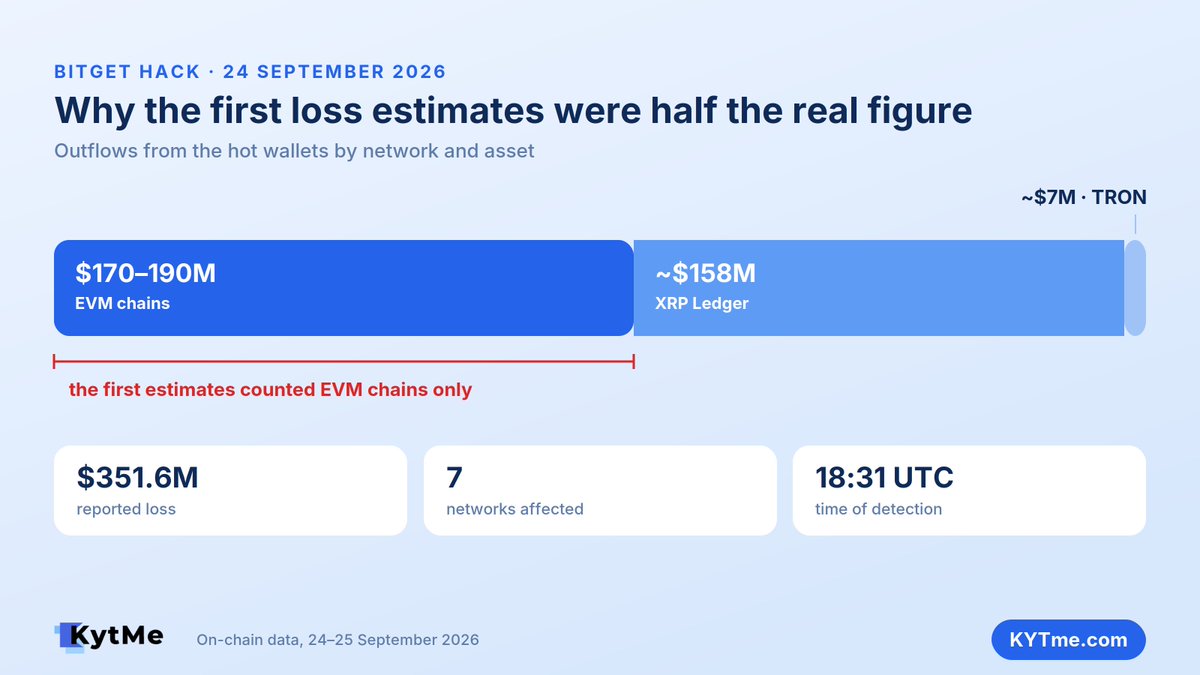
1/5 🚨 $351.6M left #Bitget📷's hot wallets in a single evening — the largest crypto theft of 2026. The outflows ran across seven networks at once: #Ethereum, #XRP Ledger, #Arbitrum, #Avalanche, #Optimism, #BNB📷 Chain and #Base. The exchange spotted the unauthorised transfers at 18:31 UTC, suspended withdrawals and said its $464M protection fund covers the loss. The first public estimates put the damage at $170–190M. They counted EVM chains only: another ~$158M went out in XRP and ~$7M in #TRX.
4/5 Some of it did move, and the route is visible hop by hop.
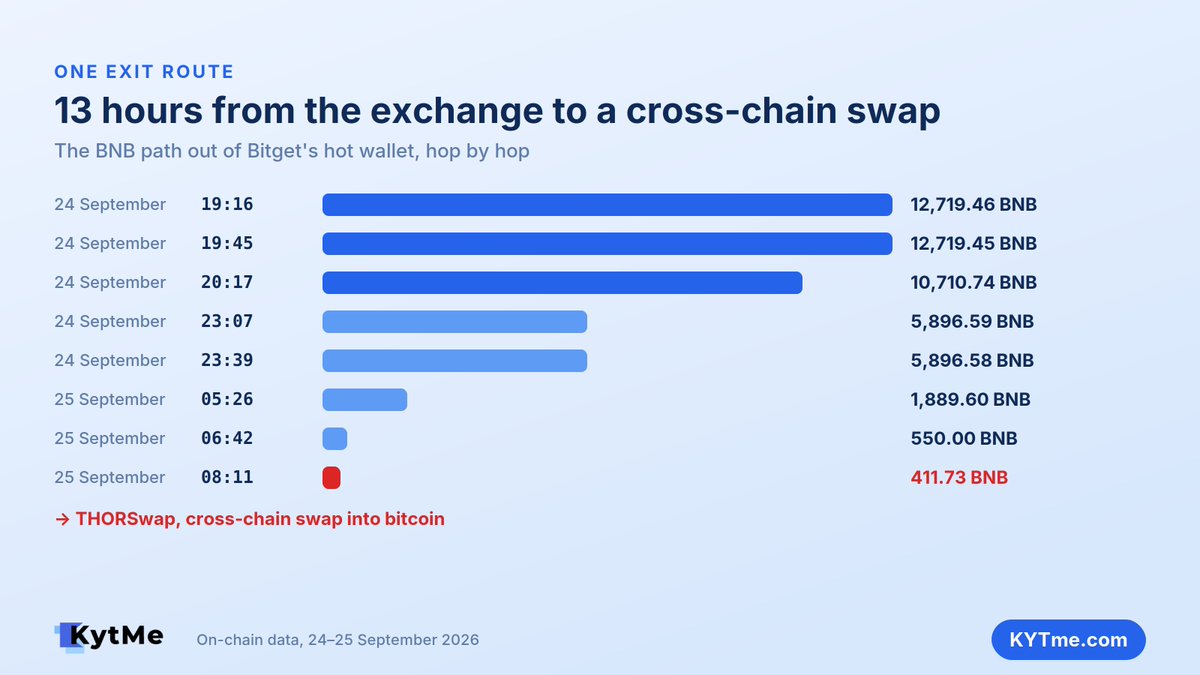
12,719.46 BNB left Bitget's hot wallet at 19:16 UTC on 24 September. The amount then travelled through a chain of wallets, shedding a part at every step: 10,710 → 5,896 → 1,889 → 550. At 08:11 the next morning, 411.73 BNB reached THORSwap and were swapped into bitcoin.
Roughly 13 hours from the exchange to a cross-chain swap. On TRON the stolen TRX was swapped to USDT through SunSwap, bridged to Ethereum via USDT0 and sent down the same route. Smaller amounts went through Across, Bridgers, Chainflip and FixedFloat.
5/5 Attribution is not settled.
Gracy Chen called North Korean involvement "very likely", citing IP addresses tied to VPN services associated with a North Korean group. Fund tracing found overlaps with the laundering infrastructure used after the Bybit and AFX Bridge thefts — a network not previously linked to other groups, which points to TraderTraitor.
If the attribution holds, 2026 becomes the second-largest year on record for thefts attributed to North Korea, above $1B. So far about $690M in 2026 is attributed to such attacks, mostly Drift Protocol and KelpDAO.
The full breakdown:
https://t.co/BPfvP2tYo9
4/5 Some of it did move, and the route is visible hop by hop.
12,719.46 BNB left Bitget's hot wallet at 19:16 UTC on 24 September. The amount then travelled through a chain of wallets, shedding a part at every step: 10,710 → 5,896 → 1,889 → 550. At 08:11 the next morning, 411.73 BNB reached THORSwap and were swapped into bitcoin.
Roughly 13 hours from the exchange to a cross-chain swap. On TRON the stolen TRX was swapped to USDT through SunSwap, bridged to Ethereum via USDT0 and sent down the same route. Smaller amounts went through Across, Bridgers, Chainflip and FixedFloat.
Bitget losses are now $387.5M, and the laundering is following the usual route: bridges, then Wasabi, then Discord and Telegram "order support" out in the open.
Mixers break the trail, but they don't erase it. The money still has to come out somewhere, and screening at the exit is where it gets caught.
ZachXBT: Bitget Hack Funds Are Being Laundered Through Cross-Chain Bridges and Wasabi
According to ZachXBT, Chinese illicit actors allegedly laundering funds from Bitget’s $387.5 million hack on behalf of suspected North Korean attackers have been openly seeking order support through Discord and Telegram channels tied to services they use. He said one operator, known as “Alias 4,” was also involved in laundering funds from the $292 million Kelp DAO exploit earlier this year, with similar patterns observed after other TraderTraitor-attributed attacks. The funds are currently being moved across chains and deposited into mixing services including Wasabi. ZachXBT said he plans to publish additional data in the coming weeks.
@WuBlockchain Same operators, same bridges, same mixers, hack after hack. The playbook is public by now. The real question is why the off-ramps still accept these funds.
❌ @THORChain has refused Bitget's request to cut off addresses tied to the 24 September breach, in which about $387.5M was taken.
#Bitget CEO Gracy Chen called on the protocol to deny service to the attackers' addresses. THORChain's answer: its network halt is a protocol-wide emergency mechanism, not a way to freeze specific funds or block an individual swap.
As precedent it pointed at itself. During the May 2026 exploit that drained $10.7M from its liquidity pools, the attackers' addresses were never blacklisted and were never stopped from swapping.
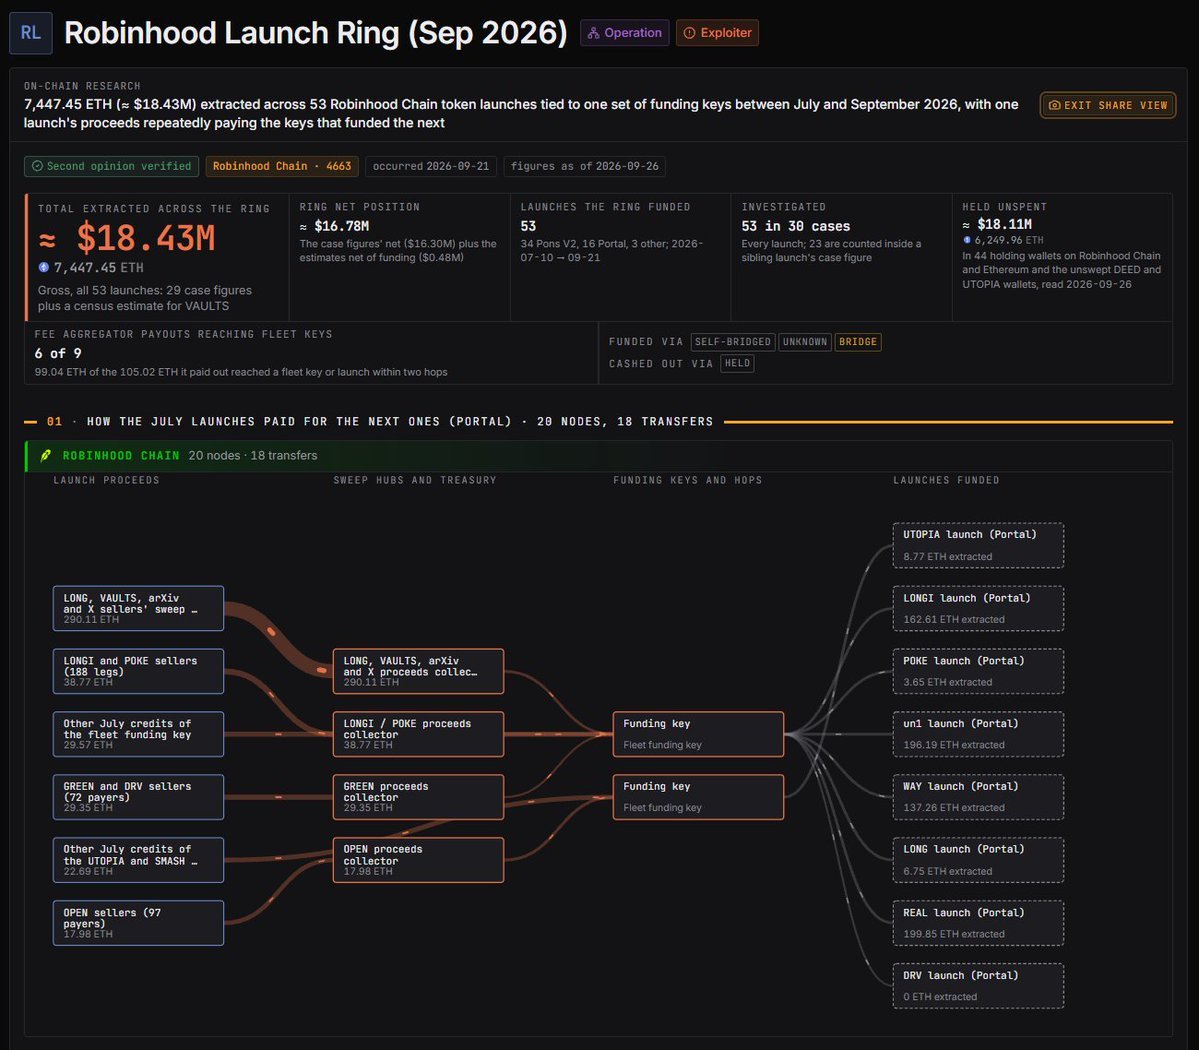
🚨 On-chain analyst Wazz has tied 53 token launches on #RobinhoodChain to a single rug-pull operation. Extracted between 10 July and 21 September 2026: 7,447.45 #ETH, about $18.43M.
The launches were not separate events. 45 of them are linked by fund flows — proceeds from one launch paid for the next. Four were funded from the same private key, four shared a collector wallet. Most used 70 to 200 wallets to snipe over 70% of supply at launch; 34 were deployed through Pons V2.
#CRUMBS, #LEGS and #PINK account for roughly $3.12M, $2.9M and $1.44M. Some launches allegedly ran fake pre-launch contracts to gather buyers before the real contract address was published.
Little of it has moved on: around 6,250 ETH still sits across 44 wallets. Wazz notes the total is likely higher — this is only what could be linked directly.
🚨 A counterfeit @GIWA_by_Upbit network took ~768 ETH — about $2.07M — in roughly 13 hours. Analysts count around 1,350 affected wallets.
Everything checked out on the surface: a bridge on the OP Stack, a working RPC, and GIWA's genuine Chain ID (9134), which is what carried it through initial verification. Admin rights over the bridge stayed with the operator. Once deposits had built up, the bridge code was replaced, the ETH drained and the original restored — inside one transaction.
About 407 #ETH has since moved into #TornadoCash. Another ~358 ETH remains unmoved on three addresses: 221, 107 and 30 ETH.
#hack #scam
⚠️ Security Incident Notice
We have confirmed that the so-called GIWA Mainnet we previously identified was in fact a fake chain set up by scammers.
The fake network used the correct GIWA Chain ID (9134), which made it appear legitimate during our initial verification. We have also identified specific suspicious messages and individuals in the related community that may be connected to this incident.
Unfortunately, significant losses have already occurred through the fraudulent bridge.
We are taking immediate action:
• We are contacting professional security teams to conduct further on-chain tracing and investigate the addresses, transactions, and flow of funds involved.
• We are preserving all relevant evidence, including chat records, RPC information, bridge addresses, and on-chain transactions.
• We are preparing to use funds from our treasury to compensate affected users. The eligibility criteria, loss verification process, compensation scope, and detailed plan will be announced after the investigation and verification process is completed.
Until further notice, DO NOT use any unofficial GIWA Mainnet RPC, bridge, or contract, and DO NOT send funds to any related addresses.
We sincerely apologize to everyone affected by this incident.
Further updates will be published as soon as more information becomes available.
Update: the stablecoin now has a name. After Tether froze its replacement wallets within hours, Xinbi told users it will accept only USDD, a TRON stablecoin with no issuer able to blacklist addresses.
Screening before you accept is now the only safety net.
Follow-up with receipts. Today we ran one of the 52 OFAC-designated Xinbi addresses through 3 screening providers:
🔴 100% — sanctions attribution live
🔴 100% — flagged via Tether blacklist
🟢 0% — "safe address", not yet
3 days after designation. This is what "attribution catches up" looks like.
@YazanXBT Privacy by default vs privacy by choice: every XMR tx is private, most ZEC activity has been transparent - a smaller crowd is a worse place to hide.
But hackers still have to enter and exit XMR via transparent chains. That's exactly where they get flagged.
5/5 The EU's 20th package gives no list of markers that make a service Russia-linked. Waiting for one unambiguous marker means reacting after the money has moved.
Rouble and SBP integration, a list of Russian banks with sanctioned names among them, Russian-language marketing, Russian mobile top-ups as a core service — the combination is itself grounds to act. The 21st package, adopted in July 2026, moves the same way.
The full breakdown and the review method:
https://t.co/ZbEHt2Nu7j
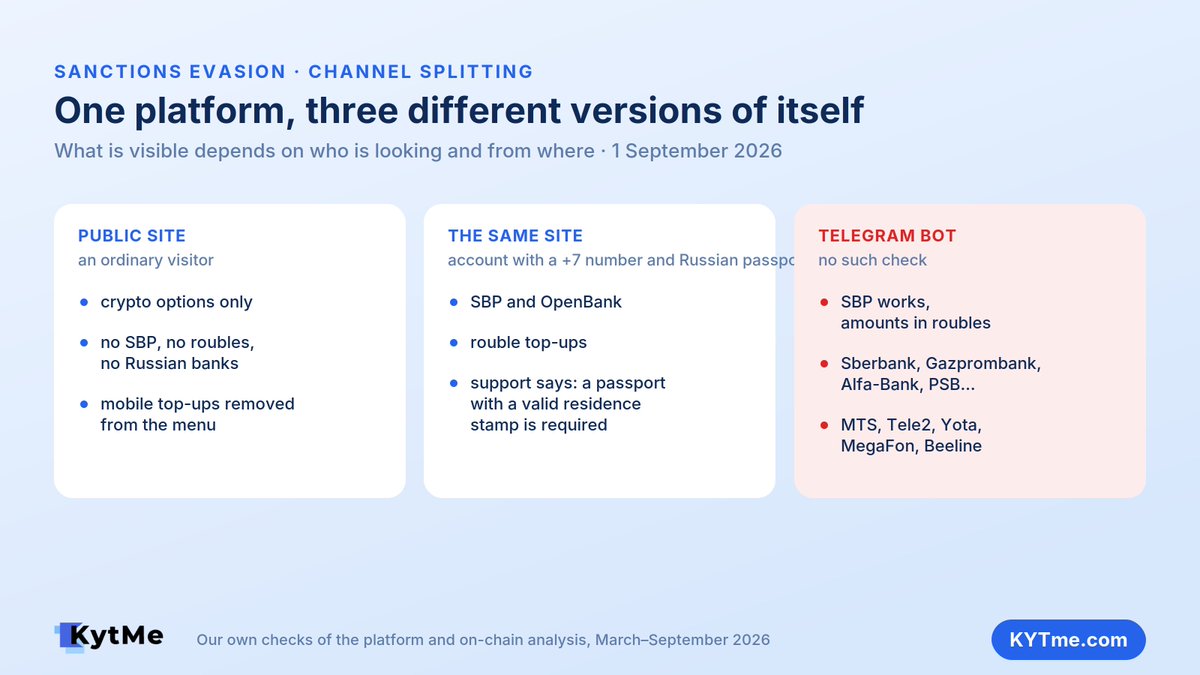
1/5 ⚡️ We were re-checking a Russia-linked crypto platform before reclassifying it as sanctions-restricted. Roubles, SBP and Russian banks had disappeared from the public site — on paper it looked like a full exit from the Russian market.
In the same platform's Telegram bot nothing had moved: SBP works, amounts are in roubles, the bank list still holds Sberbank, Gazprombank, Alfa-Bank and PSB, and the top-up menu lists MTS, Tele2, Yota, MegaFon and Beeline in Cyrillic.
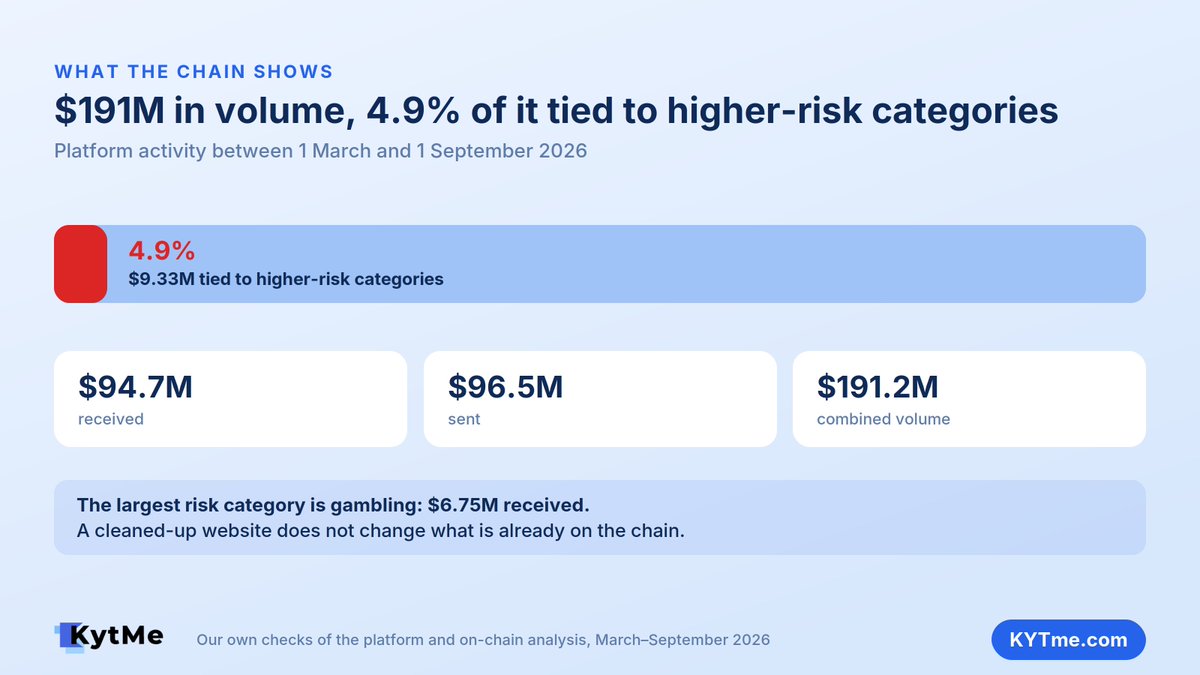
4/5 A cleaned-up shopfront does not change what is already on the chain.
Between 1 March and 1 September 2026 the platform received $94.7M and sent $96.5M — $191.2M in combined volume. $9.33M of it, or 4.9%, is tied to higher-risk categories. The largest of those is gambling: $6.75M received.