We've reached a point where installing a browser extension, IDE plugin or software library deserves the same scrutiny as opening a TCP port on a DMZ server.
Except this attack surface can be spread across thousands of hosts inside your org... and you can't map it with a port scan.
This is pretty embarrassing 🙈
Microsoft has a signed Defender driver that can be abused to kill Defender/EDR and modify protected files and registry settings
We also can’t really solve this the usual way by adding the driver to the vulnerable driver blocklist. It’s Microsoft’s own Defender component!!
MSRC says it doesn’t require immediate servicing because you already need admin privileges 😏
Which probably means this MS-signed EDR killer will stay usable for a while. Nice 🫶
Update:
Crowdstrike came out and released a technical report confirming my analysis. They were reading in a bad data file and attempting to access invalid memory.
This global crash was a two-part bomb. The detonator apparently, was NOT new.. it was PRE-INSTALLED.
/1
In fact, now that I think back on this - TSB leaks showed that NSA TAO would intentionally write random data when hiding their exploit attempts on Sun Microsystems in ebbv5.tgz - by corrupting this file it might have hidden an exploit used during a CNO.
Crowdstrike Analysis:
It was a NULL pointer from the memory unsafe C++ language.
Since I am a professional C++ programmer, let me decode this stack trace dump for you.
The full OCR text with the temporarily visible password is available in the %LocalAppData%\CoreAIPlatform.00\UKP\{<UUID>}\ukg.db SQLite database, nicely gift wrapped 🎁 for infostealer malware to exfiltrate:
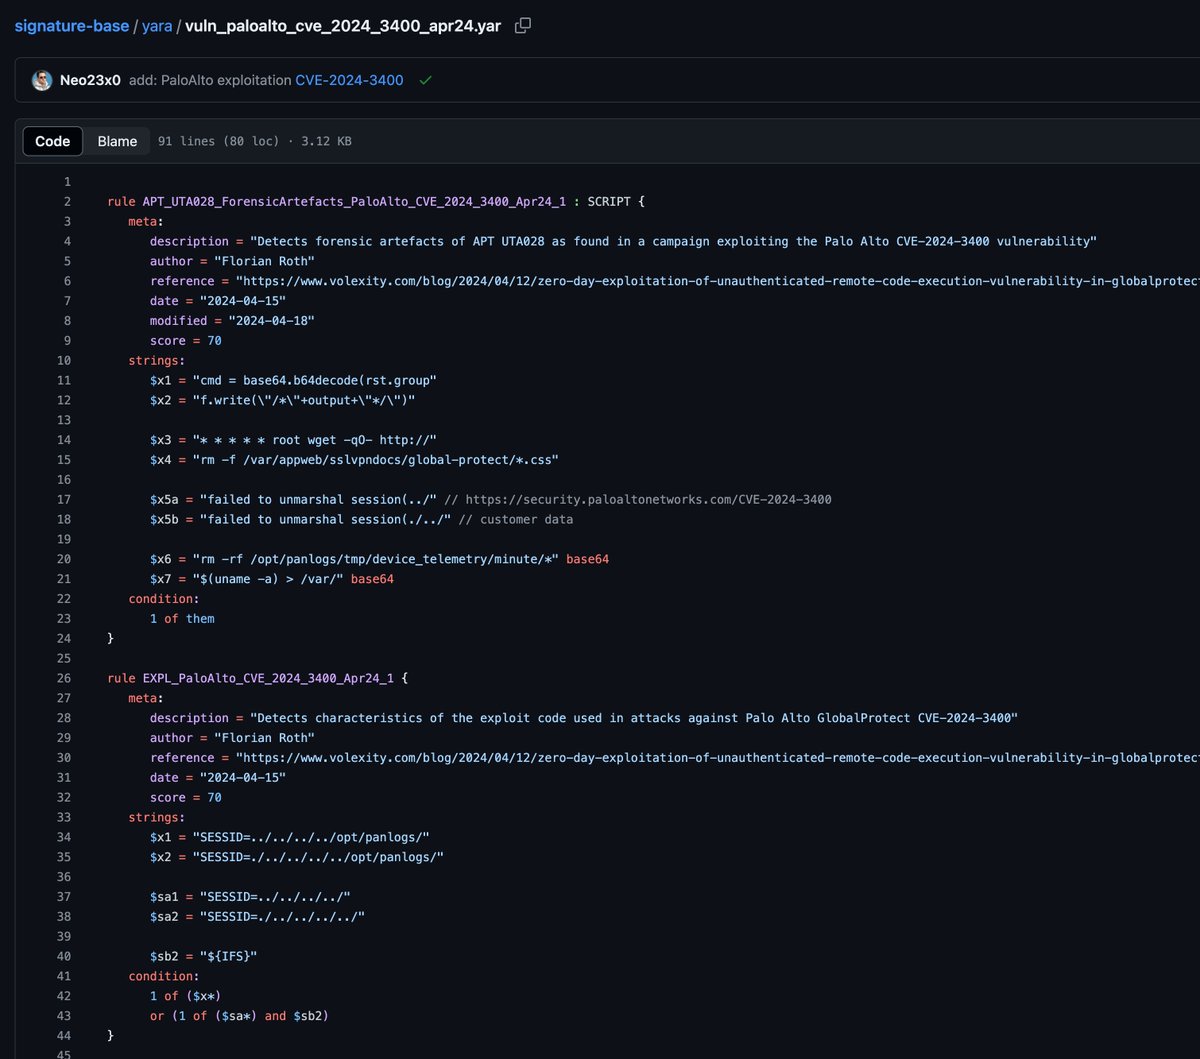
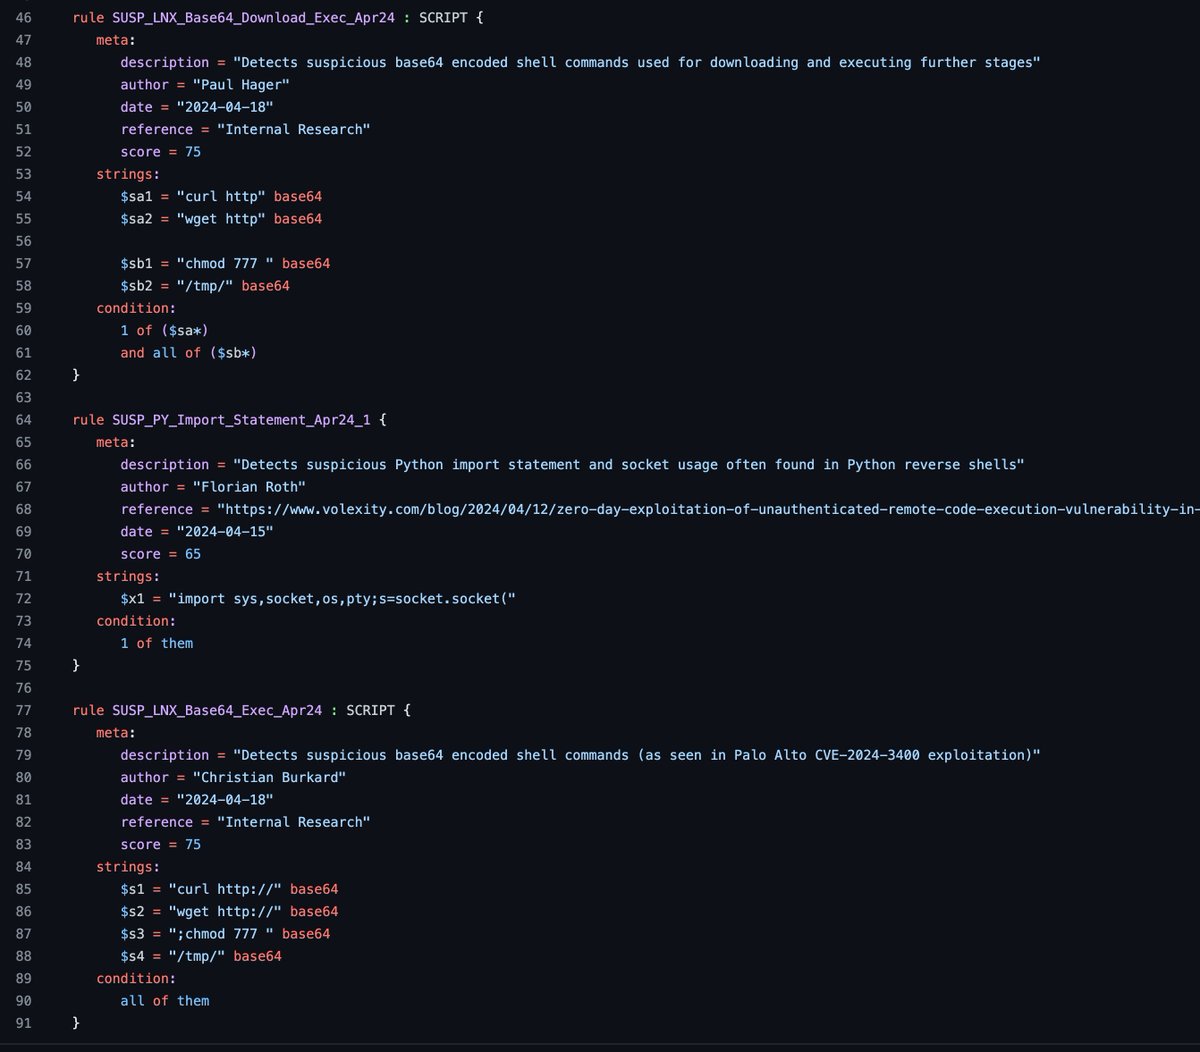
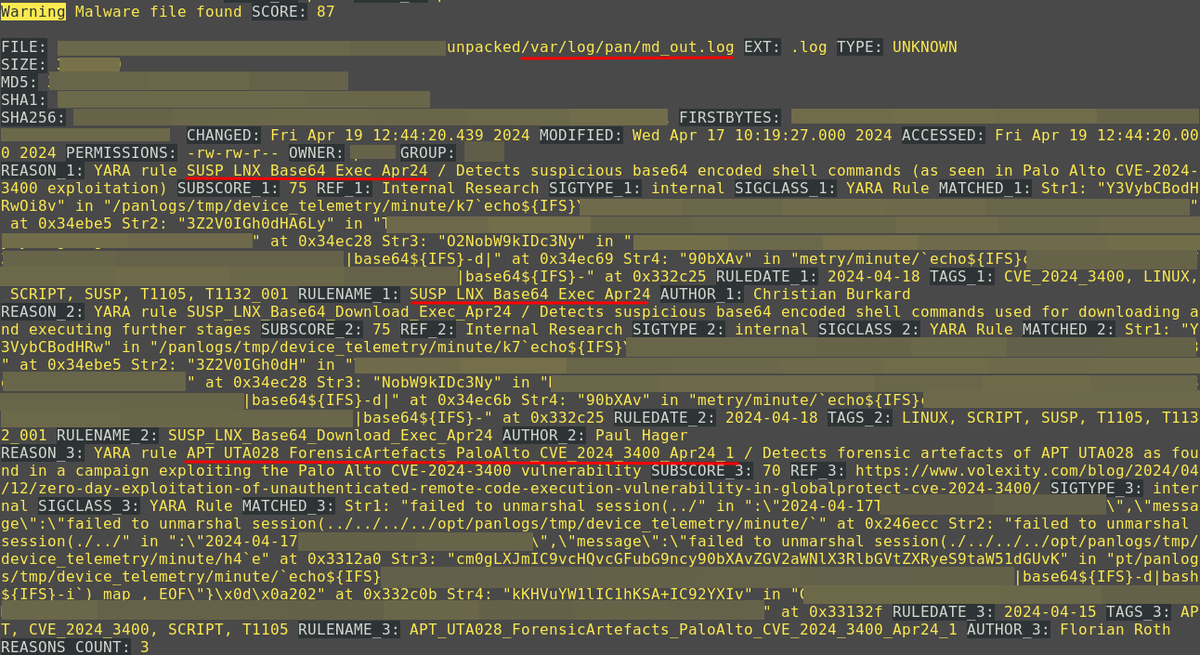
We decided to share our #YARA rules to scan for indicators of the exploitation of CVE-2024-3400 in #PaloAlto's PAN-OS with the community and included some of the generic rules (detect similar attacks)
Three Steps
1. Generate a Tech Support file and extract it
https://t.co/ITPOvDtw7U
2. Download and extract THOR Lite
https://t.co/EVPjanmunk
3. Scan the extracted folder (tech support files)
thor64-lite.exe -a FileScan -p ..\2024XXXX_XXXX_techsupport.tgz_unpacked --intense --cross-platform --max-file-size 500MB
YARA Rules (already included in THOR Lite's signature package)
https://t.co/qMgto8kP9k
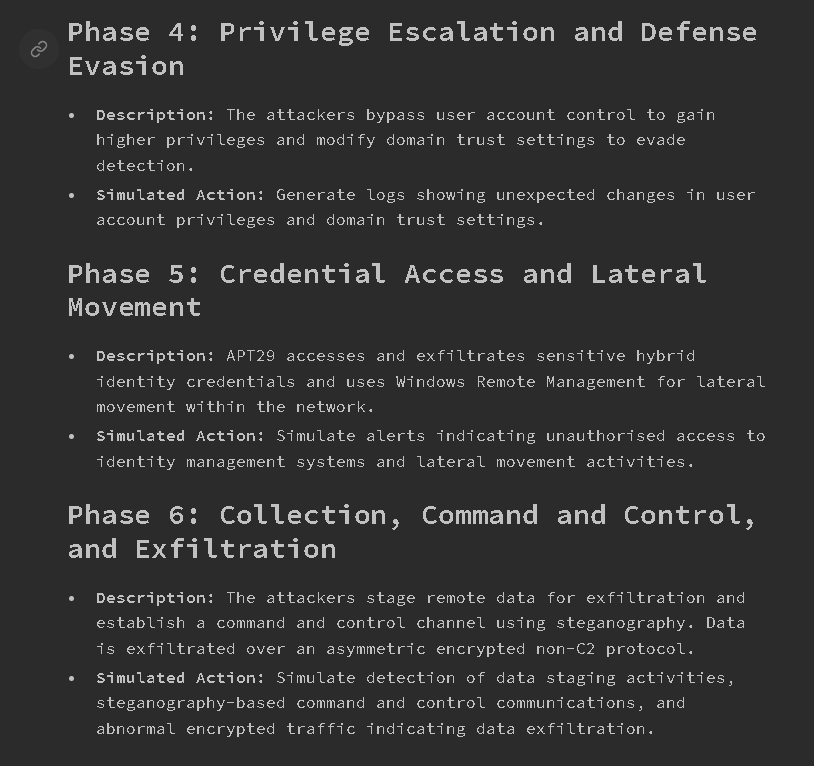
I just came across a tool called AttackGen. It's a simple tool that generates incident scenarios based on a Threat Actor and suggests simulations and possible detections at a high level. #llm#python#threatintel
👉 code: https://t.co/RtnGJQPAEH
👉 app: https://t.co/b1C2kFq9kz
Ever find yourself on an endpoint with SentinelOne and have Local Admin? Just ask SentinelAgent.exe nicely, and it will dump a process for you, including itself!
https://t.co/WU6ZDPR91H
It bombs out on LSASS, but most other processes work.
🔥 New blogpost 🔥
Running PEs inline without a console.
You now can, for example, run PowerShell in CobaltStrike and obtain its output without spawning any process (including conhost.exe)
https://t.co/oF7jh95m0F
Since Cobaltstrike v4.9 is leaked and sooner or later it will be exploited, here is the detection for beacon's core. This detection cannot be modified with malleable profiles. EDRs like Crowdstrike/Elastic/MDATP which constantly scan the memory region for known patterns should easily pick this up. FYI, if BRc4 gets leaked, I would do the same for BRc4 too, like I've done in the past. No hard feelings, just helping the community.
https://t.co/vMzjFtzyfb
My Okta for Red Teamers post is up! We look at how Kerberos SSO works, how to intercept credentials via a fake AD Agent, decrypting AD Agent tokens, adding skeleton key's, and even how to deploy a janky SAML IdP server to auth as any user for good measure. https://t.co/Hs0wN5397s