The Oppenheimer and Martin Moshal (both 'white') funded Herman Mashaba ends this usual boring 'big bad whites love Apartheid' post with "The Sun has Risen".
Sounds like "The New Dawn" 2.0
Grifter's gonna grift I suppose.
Israel is involved in a campaign to rewrite history on wikipedia, and use it to trick AI models. The recent report by @tech4palestine covers in detail exactly how they are doing it.
Read it here: https://t.co/ICF7WcejfM
We are not confused. Service Delivery Must be for ALL residents, not a selected few.
ActionSA leadership will lead negotiations that will result in the best interest of ALL residents.
In dozens of supermarkets across several European countries, a huge amount of food has been dumped after refrigerators and freezers were targeted in a cyber-attack. Read more: https://t.co/gWYpVpasGH
‼️ BREAKING: Oracle Issues Emergency Java Update for Critical 9.1 HTTPS Trust Vulnerability
Details: https://t.co/XZV8KY0rPW
Oracle has released an emergency Java security update to address CVE-2026-91403, a critical vulnerability affecting how Java applications trust digital certificates. Published on October 21, 2026, the alert assigns the flaw a CVSS 3.1 score of 9.1 and covers Oracle Java SE and GraalVM.
The update blocks affected intermediate certificate authority certificates linked to eMudhra. According to Oracle’s security advisory, the issue affects the Java Secure Socket Extension, or JSSE, component.
Oracle rates exploitation as low complexity, with no authentication or user interaction required. Successful attacks can expose or change sensitive data, although the risk matrix lists no availability impact.
#cybersecuritynews #vulnerability
The FBI continues to warn about two critical security flaws in PHP, a programming language used to build many websites and online services. Attackers could exploit these vulnerabilities to break into systems, putting sensitive information and business operations at risk. Security updates are available and should be applied immediately.
If you are a business owner or website operator, check whether your systems are affected. Contact your IT support team, website developer, or hosting provider for help identifying vulnerable systems and applying the necessary updates.
The FBI urges organizations to take the following steps now:
➡️ If an immediate update is not feasible it is recommended that organizations take the system offline until it can be fully mitigated.
➡️ Immediately update affected PHP installations following the guidance on https://t.co/JFOW6jG9Ws. Inventory where PHP runs in your environment, prioritizing internet-facing systems and vendor products that bundle PHP.
➡️ Monitor web servers for suspicious activity, including PHP processes unexpectedly launching command shells or downloading files. Ensure appropriate process-monitoring capabilities are in place to help identify potential exploitation.
➡️ If you find signs of compromise, isolate affected systems, preserve your web server and PHP logs, and report it to your local FBI field office or https://t.co/ZWC7Se2YdU. Those reports help us identify the actors involved and warn other organizations before they become victims.
For the latest information on these vulnerabilities (CVE-2026-109618 and CVE-2026-109619), follow PHP’s announcements on https://t.co/JFOW6jG9Ws, CERT-EU Security Advisory 2026-018, and CISA’s Known Exploited Vulnerabilities catalog.
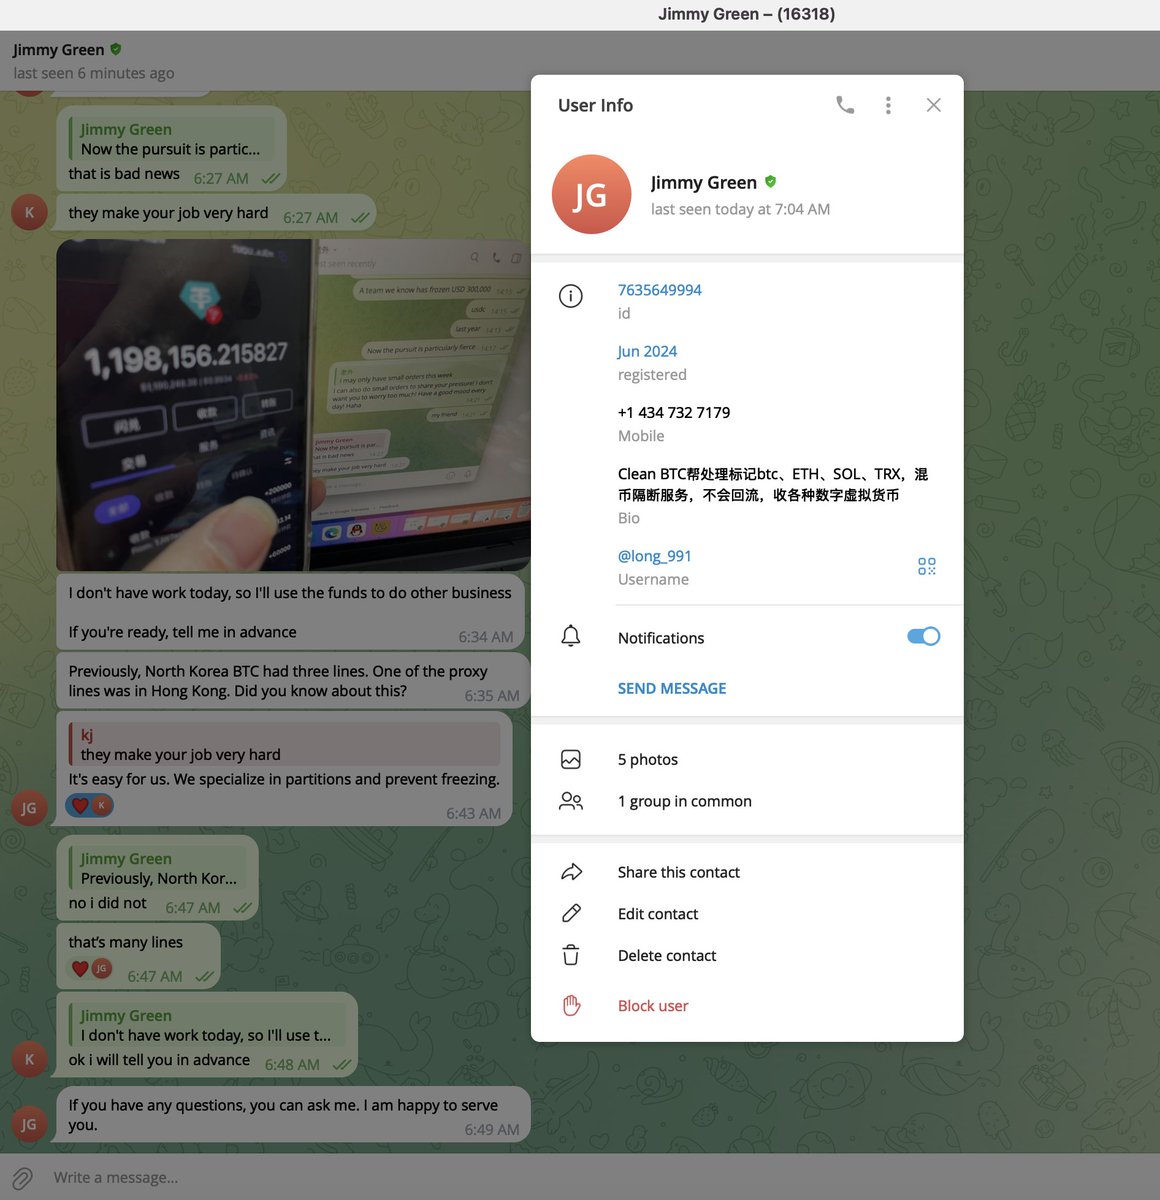
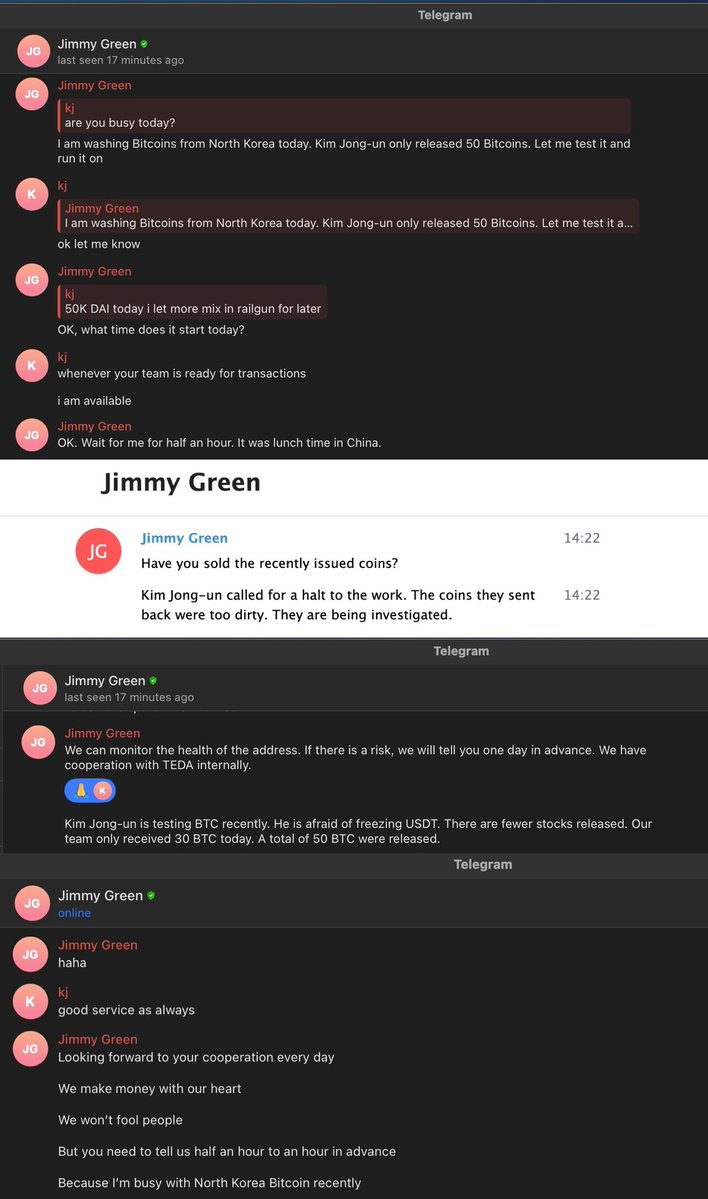
1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group.
Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain.