Did you know you can request a certificate via NTLM relay through these 2 AD CS endpoints? 🔥
/<CAName>_CES_Kerberos/service.svc/CES
/<CAName>_CES_NTLM/service.svc/CES
This article explains it really well 👇
https://t.co/0z5t2eoY8A
RustHound-CE v2.5.21 now also checks whether these endpoints exist (on top of /certsrv/certfnsh.asp) so #BloodHound can graph the path!
#ADCS #ESC_CES
Google Mantis is a skills pack for security review with coding agents
Install:
npx skills add google/mantis
Key commands:
/mantis-threat-model: builds a threat model from your codebase
/mantis-researcher: scans for vulnerabilities
/mantis-review: filters false positives
/mantis-reproduce: writes a PoC and runs it in a sandbox
/mantis-patch: applies a fix and confirms it blocks the PoC
/mantis-report: generates the final security report
This is a good use case for running your agent in a sandbox, since the reproduce and patch steps execute generated code
https://t.co/OhmZDDNcWy
Many folks don't know how to get their hands on firmware for various firewall vendors or what not.
I use this for various automated workflows - though I'm sure folks will lively have many of their own (e.g automating patch diffing).
I put together and share a small toolkit you can point your agent at that will dump the image to S3.
For example, say I wanted to dump PANOS:
1. Accept the BYOL agreement on AWS Marketplace
2. You now have the AWS AMI ID
3. Use this and dump it to S3
4. ???
https://t.co/zRVdvhFYHA
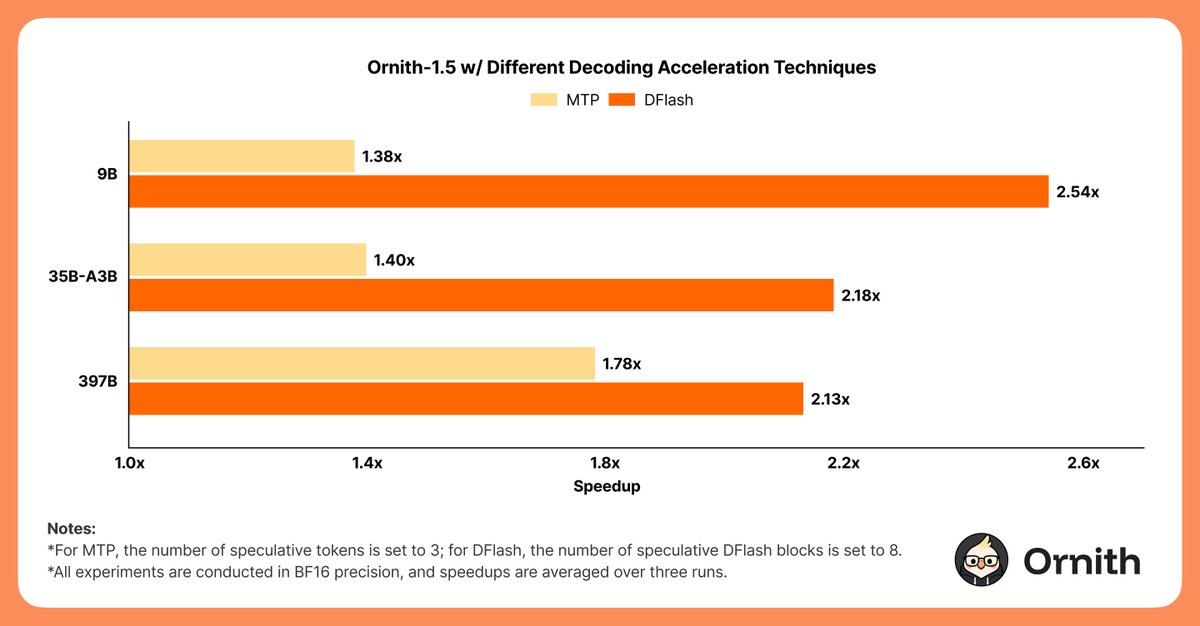
🪽DFlash draft models are available for Ornith-1.5 9B, 35B-A3B, and 397B.
DFlash and Ornith 1.5 make a dynamic duo: DFlash performs as the draft model, accelerating inference by drafting multiple tokens at once. Then Ornith 1.5 verifies the draft tokens in one pass instead of generating one token at a time.
👮 We conducted a performance evaluation of the DFlash models. DFlash achieves up to a 2.54× speedup without any loss in generation quality.
🔌 Come and plug this super buddy into your workstation.
https://t.co/g4LXGxBAXk
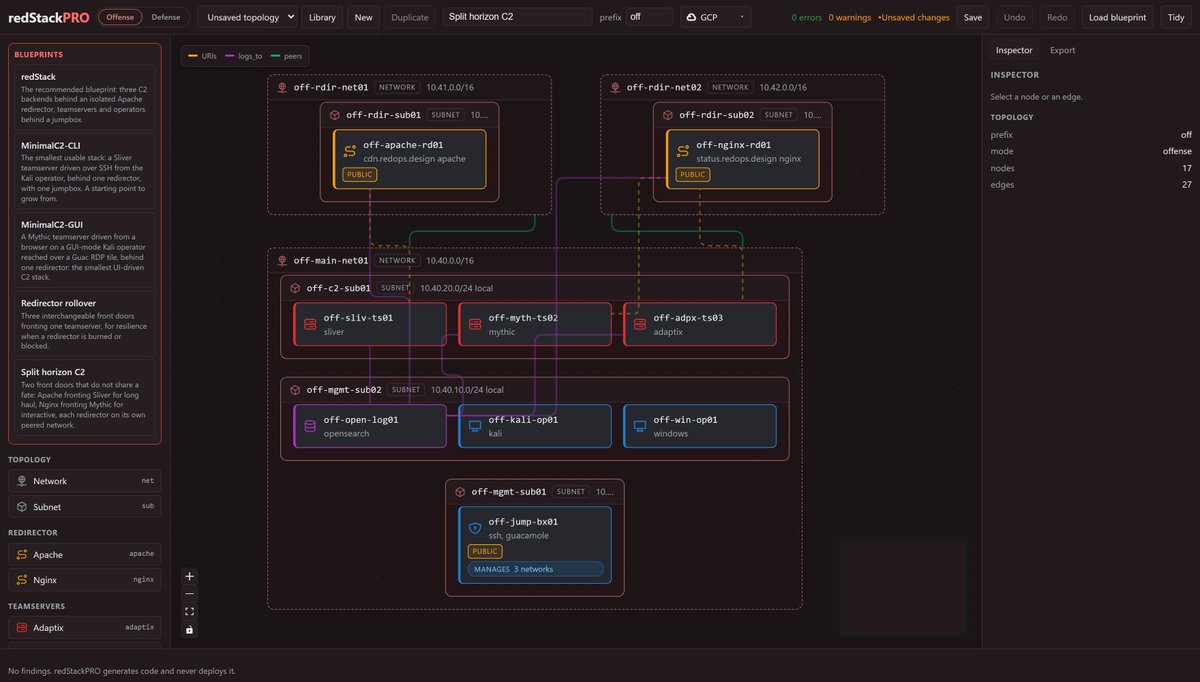
A canvas for red team infrastructure and cyber ranges. Compose a topology, export runnable Terraform and Ansible, and deploy it yourself. Your cloud credentials never leave your machine. dev by devZero.
Github:- https://t.co/iomG8r2HNS
InjectSetConsole - Performs process code injection by leveraging a Windows named pipe. Unlike traditional techniques, it does not use the:
✅ VirtualAllocEx &
✅ WriteProcessMemory APIs
https://t.co/h9MFY6W5tr
New GGUF:
huihui-ai/Huihui-GLM-5.3-Flash-abliterated-GGUF
This is an uncensored version of zai-org/GLM-5.3-Flash created with abliteration.
Note
GGUFs come from unsloth/GLM-5.3-Flash-GGUF.
Only layers 15 to 35 (0-based indexing) have been ablated, while the other layers remain unablated.
https://t.co/AgddpmkwH4
iMessage EXR. zero click. heap overflow before the banner finishes.
CVE-2026-86869. libAppleEXR sizes the buffer for 3 channels. 12 bytes.
CompressedInterleave4 writes 4. 16 bytes. every pixel.
three of those four bytes come from the file.
BlastDoor never decodes EXR.
Spotlight and the photo indexer do, later, with SDR hardcoded on.
no tap. same ImageIO path on iPhone, iPad, and Mac.
fixed in the 27 releases. older fleet still sits on it.
credit: Niels Hofmans / ironPeak
https://t.co/viusjHmr47
#iOS #ExploitDev #InfoSec
Purple Team Automation - Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK. https://t.co/rk0t5WqjOI
So I wanted to share a bit of data to show what happens when you TASK an LLM to conduct an offensive security engagement.
This is in a lab, this was without using any skills, any mad prompts, this was in a safe environment.
https://t.co/D1n2unprWn
🗞️For years you needed a jailbroken iPhone to decrypt iOS apps. That’s the part that just moved. Full IPA decrypt. No physical iPhone. No jailbreak🔥
https://t.co/tQRNQMRfna