Totally get it. But 100 words? It takes me 50 just explain my teams background let alone the problem and how we are solving it. Would you recommend only introducing who I am and just leaving the details as a read in the attached deck?
One last question on revenue. So far in my conversations with different investors who claim "early" or "idea" stage, still ask for one thing... revenue.
How do you have revenue at idea stage? Do you think that is the new norm for all investment stages, from here on out?
AI is finding vulnerabilities faster than ever. Bank of America just hired 1,000 contractors to help fix them.
And our industry's answer? More tools with AI sprinkled on top. 🙄
Cybersecurity doesn't need smarter silos. It needs one autonomous system that continuously reasons, acts, verifies, and learns.
That's the thesis I've spent the last year building into WireWolf.
We need to make security operations intelligent, not just the tools.
It's hard, really hard to build something.
You have an idea. You care about the problem, you believe in what you're building, and you put your all into it. You would think when you talk to people about it, at least some of that would come through. That they would understand you're genuinely trying to help.
But a lot of the time, it doesn't.
You need feedback, so you ask for it. And before you even get a chance to have a real conversation, the ask gets shut down. Sometimes they say it. Sometimes you can just tell they've already decided you want to sell them something.
I don't expect everyone to care about my idea as much as I do. And I don't expect everyone to think it's good. That's why I'm asking for feedback in the first place. Tell me what's wrong with it. Tell me what I'm missing. But damn, at least give me a chance to ask.
The investor market doesn't help either. I've reached out to hundreds of investors, including ones who say they invest at the very earliest stages. And all they really want to know is whether you have paying customers.
I'm trying to get people to talk to me so I can build something they'll actually want to pay for. That's part of the work. But getting anyone to even have that conversation feels like its own full-time job.
So you have an idea you're passionate about, you're willing to put in the work, and you truly want to help people by building it?
Well, that's too damn bad. Come back when it's already working.
@SecAlertsCo KEV plus a CISA deadline of Oct 16 is a short fuse when you have more than one tenant. MSPs, do you have a count of unpatched endpoints yet?
@ESPProjects #4 is the one shops skip. They deploy the patch and never check it landed. How do you verify across every client without eating the whole week?
@The_Cyber_News MotW bypass means the email attachment that used to look "local" is fair game again. MSPs, are you patching this before the next phishing wave or waiting for Friday?
@TheCyberSecHub Fully patched and still rooted is the nightmare pitch for every MSP running client VPNs. How many of your clients are on Ivanti Connect Secure right now?
@TheHackersNews Spotting 1,413 CVEs is easy. Picking which ones get fixed at 40 clients this week is the actual work. MSP owners, who sets that priority on your team?
Looks like Microsoft had a bit of fun. They shattered their own Patch Tuesday record by fixing 1,413 vulnerabilities, including one that’s being actively exploited.
This is a real problem. With AI helping uncover more vulnerabilities, the amount of remediation work is going to keep growing. Something needs to change.
The only way I see this scaling is to turn remediation into one continuous autonomous loop. Find the vulnerabilities, identify the risk, remediate, and verify the fix. Then keep going.
That’s what I’ve been working on at WireWolf. We need to spend less time chasing fixes and more time on the things that matter tomorrow.
Read the article
https://t.co/GGHgcf9MYB
@haleymbryant I just filled out the "Pitch Us" form. I would love to connect and discuss what we are doing over here at https://t.co/Yo5Bt3UadN
https://t.co/M8205OlRYP
Cybersecurity has never been a single job. It has been a collection of disconnected tools, manual handoffs, and broken workflows.
WireWolf brings the entire operation into one continuous loop. Recon and OSINT, attack surface discovery, vulnerability scanning, external and internal pentesting, defensive validation, and remediation all run as a single, AI-driven cycle.
Alpha moves through every phase, reasons in real time, and stops at the boundary so you stay in control. No more tool-hopping. No more context loss. Just continuous coverage that actually closes the loop.
Let’s talk target selection.
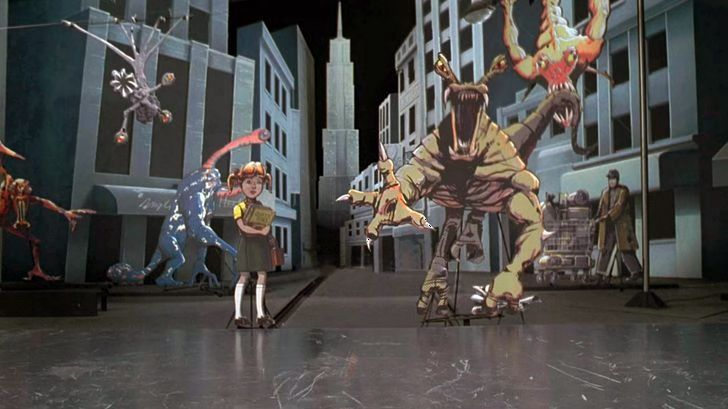
In Men in Black, Will Smith shoots the little girl instead of the intimidating aliens. A kid carrying advanced physics books through an alien-infested neighborhood at night? Something didn’t add up.
He looked beyond appearances.
Cybersecurity needs the same discipline. CVEs, CVSS scores, and CISA’s KEV catalog are useful. But none tells the whole story.
The real question: Which vulnerabilities put the business at risk?
Do we run the affected version? Is it internet-facing? In KEV? Business-critical? Linked to ransomware or active campaigns?
The highest CVSS score doesn’t automatically deserve your first move. Context matters.
Stop chasing counts. Focus on risk. Make your move.
How do you separate vulnerability noise from the threats that matter?
Noise has always been a problem. It’s just going to get worse. Not all alerts require your attention, especially if the tool you are using pops for every range of CVEs. Baking critical criteria based on the org environment is the best way to keep your eye on the ball. That is what we focused on at WireWolf.
SonicWall SMA1000 got a CVSS 10. It was disclosed Oct 6 and exploited by Oct 8. Finding it took seconds; patching every client is the actual job.
MSP owners: how many of yours are patched right now?
https://t.co/ooweyF64Gb
RMM abuse jumped 277% last year. Attackers don't pick locks when you leave the master key under the mat.
MSP owners: what's the one thing you've done to lock yours down?
https://t.co/yTpZngLNV1
@dailytechonx Huntress found the second rogue ScreenConnect client uninstalling the first to cover its tracks. MSPs: are you allowlisting your own ScreenConnect instance, or just the app name?