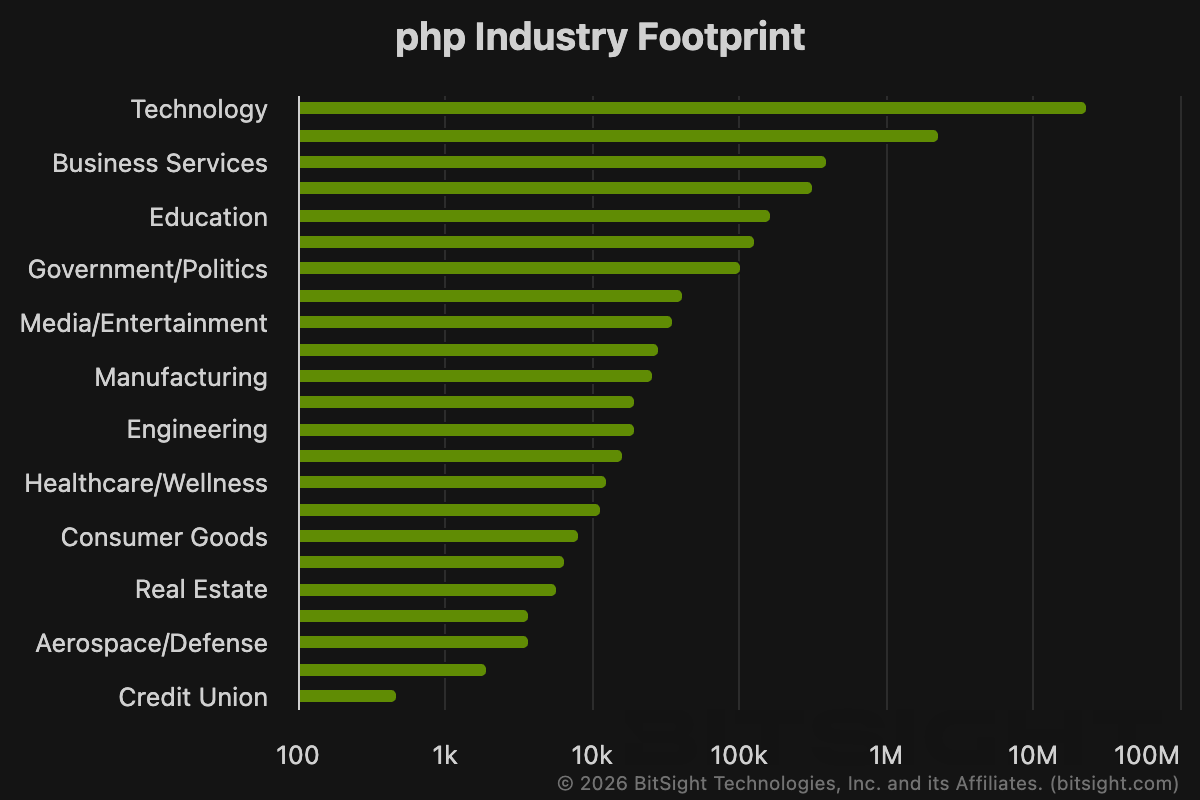
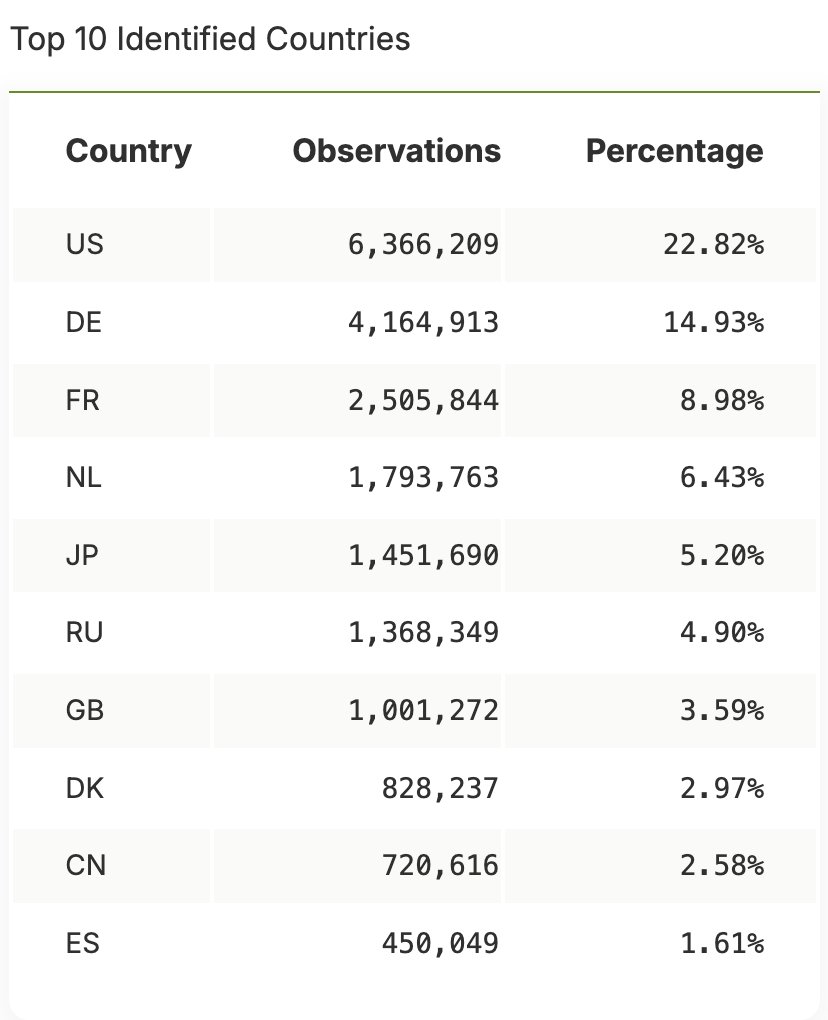
Evolving threat 🚨 CVE-2026-111497, previously known to affect Node.js (node2shell) and Python has evolved into “HTTP2Shell.”
A significant blast radius.
This vulnerability leaves many libraries and applications using HTTP vulnerable to pre-auth RCE via Brotli decompression.
Please be aware. Fixes not yet available for all affected services. Look for Brotli (1.2.1) dependency upgrades when they become available.
Une troisième faille critique dans PHP : la CVE-2026-115560
Pour s'en protéger en attendant la mise à jour :
"Set session.upload_progress.enabled=0 and restart every worker until the next regular bugfix release, to fully protect from CVE-2026-115560."
👉 https://t.co/9NjXMTAwIi
A brief update on the critical vulnerabilities in PHP:
We have not yet validated exploitation in the wild and we have no evidence of successful wide scale exploitation. There are currently several exploit PoCs publicly circulating, many of which appear to be "vibe-coded" and are incapable of remote code execution. We have validated some PoCs, however, that are capable of RCE against default deployments of mod_php but not PHP-FPM.
Nonetheless, exploitation may have already begun in a limited fashion and the threat is viable and very serious. Defenders should:
1) Patch & Restart by upgrading to PHP 8.5.12, 8.4.27, 8.3.36, or 8.2.35 and restarting web services
2) Layer Temporary Safeguards at the network edge (WAF/proxy rules) and server configuration level if immediate patching requires a maintenance window
3) Protect Credentials by monitoring for abnormal session traffic and rotating keys and passwords on compromised internet-facing PHP systems exposed prior to patching
🔗 We are continually updating our Cloud Security blog post on this topic with real-world guidance and actionable defense strategies as we learn more. Please keep monitoring these posts for updates as you prioritize your patching efforts: https://t.co/uDnd6gk988
🔗 Technical details from Wiz: https://t.co/RqmTqEDM2V
🔗 Details of the exposure from VirusTotal: https://t.co/Toix3AM0yq
SCOOP: Major U.S. banks are detecting unauthorized third-party AI agents inside customer accounts, including some attempting to take actions that appear to be independent of user instructions, sources told Axios.
The findings have alarmed banking executives, who are racing to restrict access to their systems as AI moves at a velocity faster than financial institutions can respond, multiple industry and bank executives told Axios.
Several banks are now preparing for worst-case and even “day after” scenarios, including how to rapidly secure or restore customer accounts if things go wrong, the people said.
Several bank executives told Axios they're struggling to distinguish between human users and AI agents. One executive said banks also struggle to determine whether agents are authorized by customers or potentially operating without their permission, more akin to rogue agent behavior.
Read my latest for Axios here: https://t.co/Q3bda5In8q
Security called me at 6:12 AM today.
"Patch every PHP server immediately."
I asked what happened.
"Two critical vulnerabilities. Remote code execution. No authentication required."
Cool.
How many PHP servers do we have?
According to inventory: 12
According to reality:
Nobody knows.
We found one running WordPress.
Three running old internal tools.
One under someone's desk.
Two inside vendor appliances.
A forgotten employee directory from 2016.
And a server named:
PHP-OLD-DO-NOT-TOUCH
Naturally, that one runs payroll exports.
Then we found a PHP 5.6 box.
I asked who owned it.
The documentation said:
BRIAN.
Brian left in 2019.
We called Brian.
He said:
"Oh wow, that's still running?"
Excellent.
By 8 AM, leadership joined the incident call.
CEO:
"Can hackers actually get in?"
Security:
"Potentially yes."
CEO:
"Without a password?"
Security:
"Yes."
CEO:
"Then why do WE need passwords?"
Not the lesson.
Finance asked if we could wait until the weekend to patch because downtime affects revenue.
Security explained that the alternative was letting strangers execute code on our servers.
Finance asked for a cost comparison.
At 9:17, someone suggested temporarily taking the vulnerable websites offline.
Marketing refused.
"Our campaign is live."
So for the next hour, the company officially decided maintaining a landing page for 20% off webinar registration was more important than preventing remote server takeover.
We finally patched everything we could find.
Then our scanner discovered another PHP server.
Hostname:
TEMP-PHP-2014
Uptime:
4,512 days.
Nobody knows what it does.
Nobody owns it.
Nobody can shut it down.
But every time we block network access, the warehouse stops printing shipping labels.
Security has classified it as critical infrastructure.
It is running PHP 5.4.
The vulnerability has existed longer than half our employees.
The emergency patch took four hours.
Finding out what PHP actually runs took eleven.
The internet isn't held together with code.
It's held together with servers everyone is afraid to turn off.
The PHP Foundation has blamed Chainguard for breaking the embargo before patches for the PHP2Shell vulnerabilities were ready to be shipped.
PHP blog post: https://t.co/hbVEO8sd3V
Chainguard response: https://t.co/AwVRF32WXQ
Re: the widely circulated blog claiming the PHP bugs aren't easily exploitable: @trailofbits has a working exploit that gets a shell on an unmodified MediaWiki installation.
https://t.co/mSr6Vkc4pj
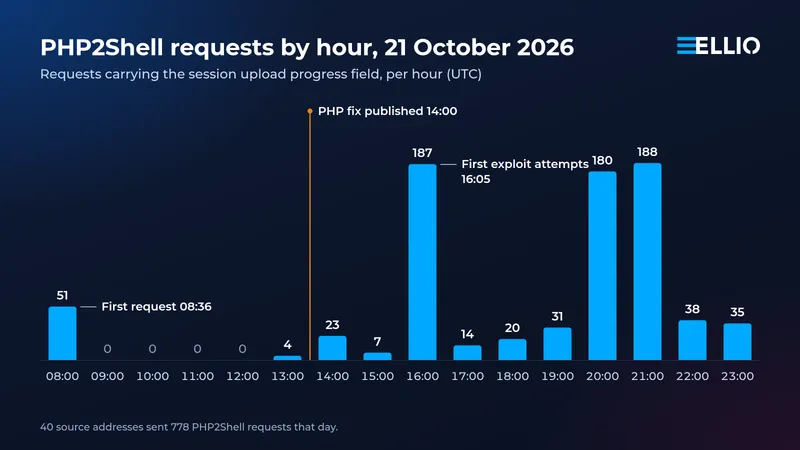
We're now seeing upload progress probes for PHP’s critical RCE vulnerability, CVE-2026-109618.
Our honeypots captured three HTTP requests from two source IPs, including PHP test code embedded in upload filenames.
Timeline (UTC):
• 20 Oct, 19:45: Previdian early-warning email sent.
• 21 Oct, 13:05: First attempt captured by our sensors.
• 21 Oct, 13:27: Follow-up warning emailed.
• 21 Oct, 13:30: PHP security fixes released.
• 21 Oct, 15:15: Previdian’s temporary virtual patch available.
Our initial warning preceded our first sensor observation by approximately 17 hours 21 minutes.
The evidence and IoCs:
• Observed source IPs: 166.1.90[.]109 & 43.134.82[.]85
• Multipart POST requests to /
• Fields: PHPSESSID and PHP_SESSION_UPLOAD_PROGRESS
• Two requests used the upload filename: <?php echo 1;?>.txt
Attackers did not manage to execute PHP or upload files in these first instances.
Update to PHP 8.2.35, 8.3.36, 8.4.27 or 8.5.12, or your vendor’s patched package.
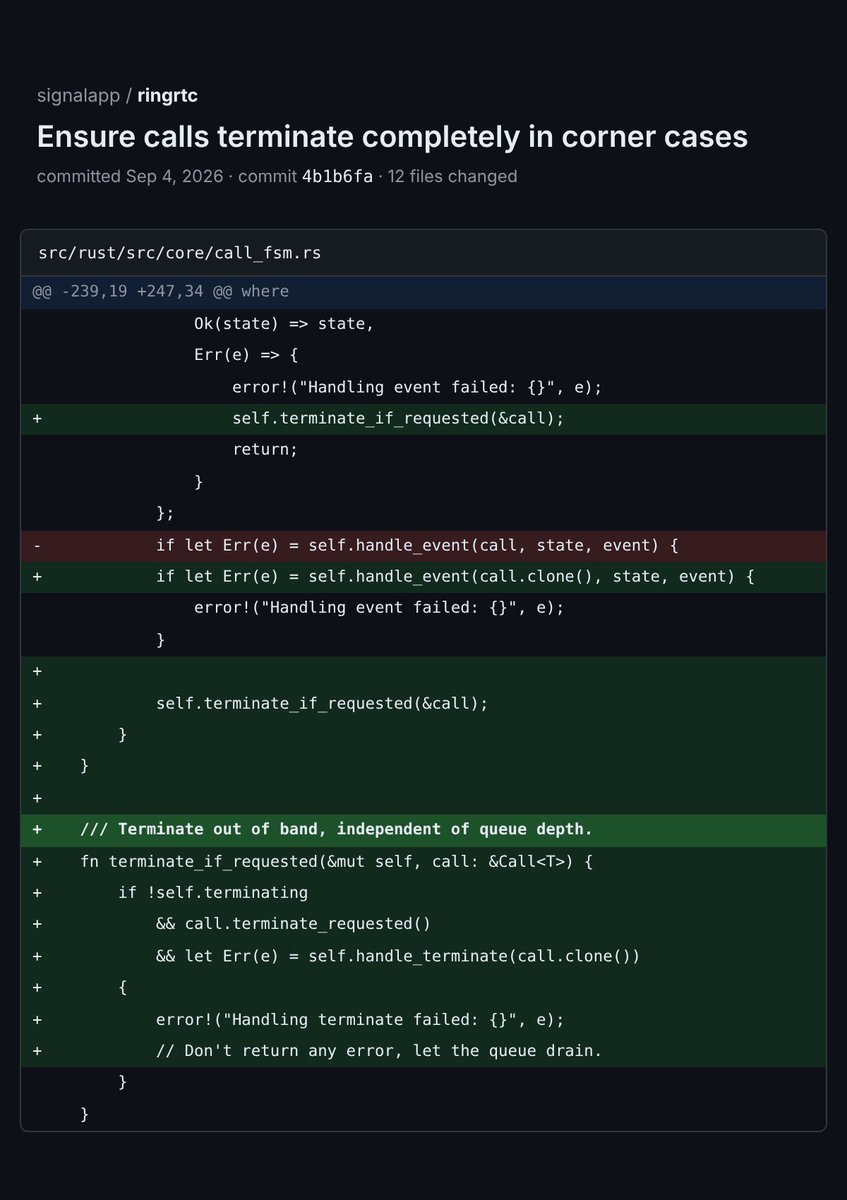
‼️ A critical Signal bug could keep your microphone, and possibly your camera, live after you hang up.
The other caller can flood the call's event queue so your hang-up is never processed.
Dubed CVE-2026-113380 it scored 9.3 and got fixed in September.
Someone tried to exploit the critical PHP2Shell vulnerabilities four days before the vulnerabilities were published, according to Amazon.
Other security firms have also observed evidence of exploitation attempts in the wild for both vulnerabilities.
https://t.co/hKAXJxXa2T
PHP2Shell (CVE-2026-109618/109619) hit our MadPot honeypots on Oct 17, four days before disclosure.
Investigating? Start your timeline there, not at the advisory date. Patch to 8.5.12 / 8.4.27 / 8.3.36 / 8.2.35 now.
https://t.co/Rb1yoaQF7b
GitLab has patched a critical vulnerability rated CVSS 10.0 that could allow unauthenticated remote code execution on self-managed servers.
CVE-2026-110264 affects releases dating back to GitLab 7.0 in 2014.
If you self-host GitLab, check your version and upgrade to the fixed release. Even installations patched on October 12 may need another update.
A recent patch doesn't always mean you're covered.
🚨 Why was a good part of the web down on 21 October?
The answer: PHP2Shell. Two critical PHP vulnerabilities, rated 9.2/10, triggered a wave of precautionary website shutdowns ahead of the release of security patches.