The new MeshCore site has dropped: https://t.co/Uyk2iD6AMx
This will be the go-to site for trusted info, especially for developers. Technical docs are here: https://t.co/s8PM8OGqLz
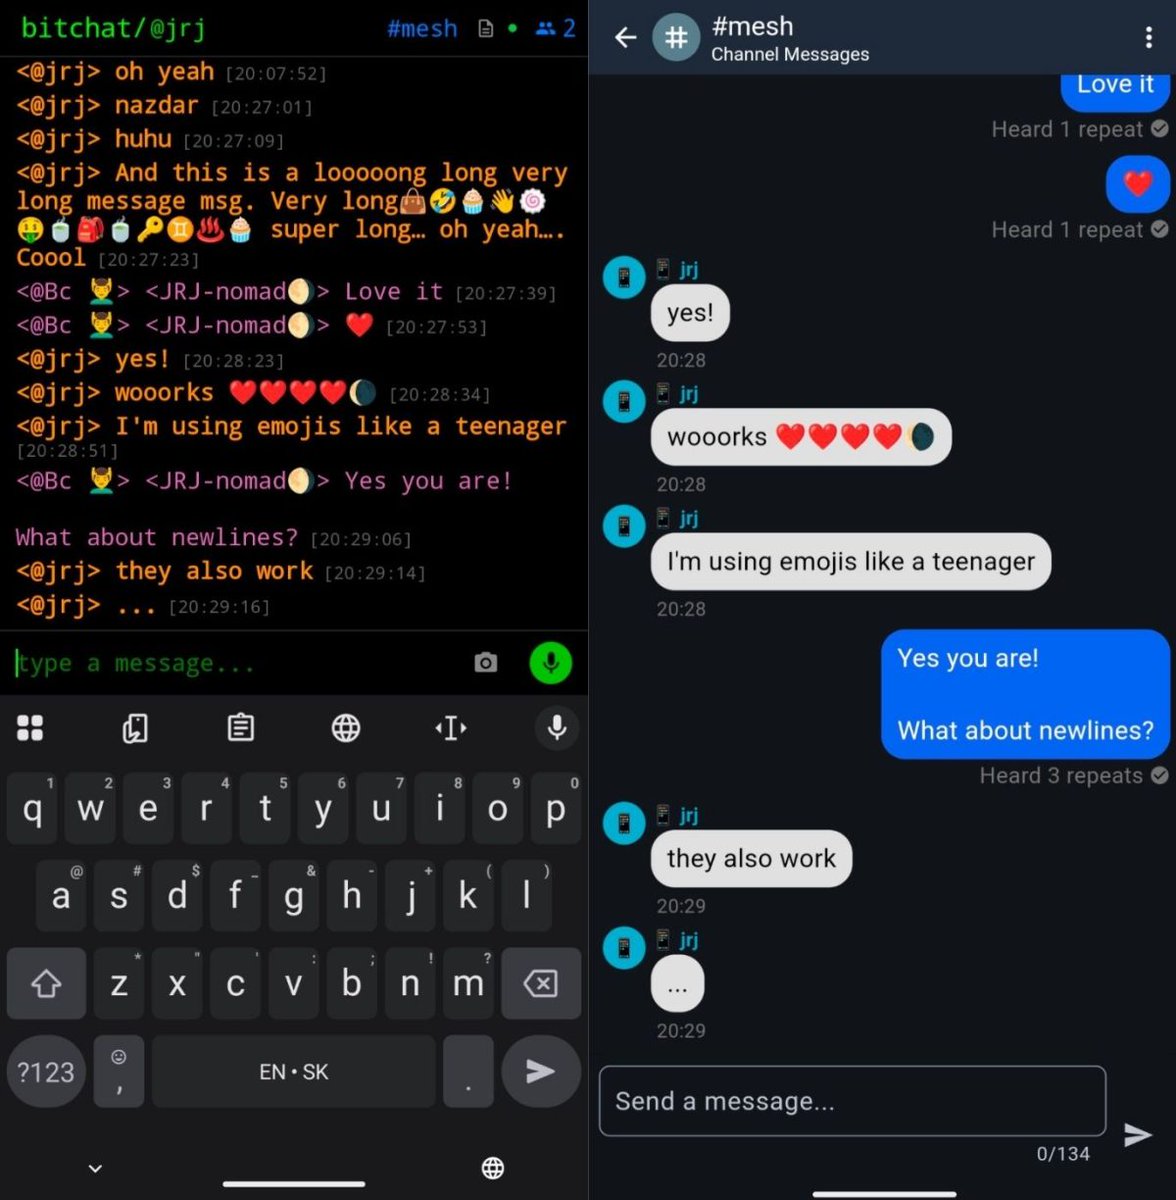
🌐 Bridging Bitchat + MeshCore: Resilient communication when infrastructure fails
Bitchat = Bluetooth mesh on phones you already have (~100m range)
MeshCore = LoRa long-range mesh (km+ with cheap hardware)
The bridge connects them. Your phone talks to the city-wide mesh network.
Perfect for disasters, protests, internet shutdowns.
Code: https://t.co/YbP7eVXWiW
Releases: https://t.co/vUVkAY2vjf
Read more: https://t.co/sgRvezRGeC
@fullspectrumdev Hey mate! Thanks for the tag. For reference, my repo is a fork of attermann's repo on GitHub. https://t.co/wtZs7oAhh8 this evolved into https://t.co/DsHghKJndN and https://t.co/LSVJ2ry0hx (transport_node branch) these are semi functional but I haven't seen any updates in a while.
If you haven’t heard of Reticulum, today is a great day to check it out!
Build your own fully encrypted mesh networks, with automatic route discovery.
Sideband + MeshChat now have audio messages, even over LoRa radio!
https://t.co/PtnkHDPyfB
https://t.co/K0OjZHZY1L
@adamwathan Hey mate! Just letting you know https://t.co/9G702Lyybk is returning infinite redirects. Also seems to be affecting https://t.co/RvMAPFVBMD
@leitom@lito_ordes@gonedark Oh man, I’ll never work on a Laravel project again without writing tests… it’s so satisfying doing a composer update, or upgrading to new major versions and seeing exactly what broke and where, if anything broke at all. Have a few projects that have around 2.5k tests each 😂
Just put up a blog post on how to smuggle your IPv4 packets through a DNS tunnel when a network allows you to perform arbitrary DNS queries. Useful on mobile networks when you have no data allowance or WiFi hotspots that require you to purchase a voucher. https://t.co/i7lwNNssAQ
@NSExceptional Are you telling me I’ve been doing it the hard way for years 😭😭 “Apple > System Preferences > Security & Privacy > General > Open Anyway”…
@topjohnwu@Google I've submitted a vulnerability report for this through Google VRP. If they decide to make my report public after it's been patched. Here's a link to the report. https://t.co/hjeTzvB2Nd
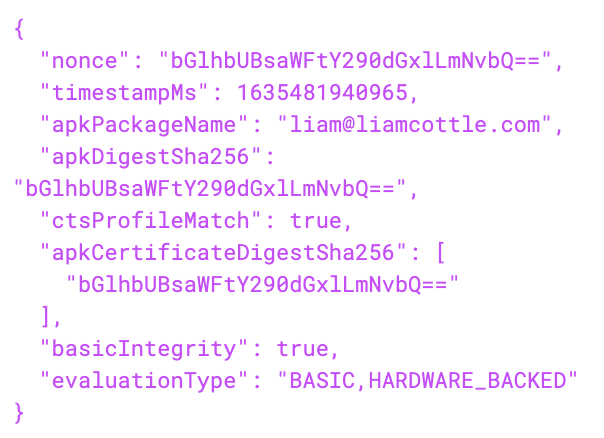
I haven't done a CTF for years, but I feel like obtaining the HARDWARE_BACKED flag in Google's SafetyNet Attestations with arbitrary data is pretty cool. What's the next challenge? @google@topjohnwu#safetynet#attestation#android#ctf#tee#security https://t.co/pAOP0m7hYH
@topjohnwu@Google Which app signature are you referring to? I can provide arbitrary results for apkDigestSha256 as well as apkCertificateDigestSha256 while still getting hardware_backed. I can't see an app signature in the ASN.1, only the application id.
@topjohnwu@Google Thanks! I wasn't really sure how to respond to your tweets at first. As far as I can tell it really depends on the use case though. For general "anti-abuse" checking through https://t.co/RxSc2BS5nG the hardware_backed flag can't be relied upon anymore.
@topjohnwu I do understand how attestation works, and it is possible to generate arbitrary attestations. Checkout my gist. You can see it’s signed by Google if you validate the X5C. https://t.co/Kh8cVYBSkO