We analyzed #RaspberryRobin's built-in exploits and explain how to identify and bypass each of the malware's many anti-analysis tricks and evasions.
Check out our blog 👉 https://t.co/kW3oLWOVaG
New job opening! 🚀 Check Point Research is opening an *international* and *fully remote* team of Vulnerability Researchers and looking for experienced researchers, from different types of expertise (OS, Cloud, IoT, Mobile, ...), to join the team.
https://t.co/twe4ELD1jl
Is RC4 Broken? Yes and no — a lot of uncharted territory remains. We look at some cool and unusual attacks that engage with very weak RC4-like toy ciphers in their own terms of number theory and permutation groups. Featuring lots of colorful circles!
https://t.co/yNB1nKjdVc
In our latest research we describe 20 #evasion and anti-debug techniques encountered in #blackbasta#ransomware signed dropper. We provide links to our Evasion Encyclopedia with all the mentioned techniques and suggested mitigations.
https://t.co/4OVeFCq5xB
New job opening! 🚀 Check Point Research is opening an *international* and *fully remote* team of Vulnerability Researchers and looking for an experienced vulnerability researcher to lead the team.
The position allows a large amount of hands-on research.
https://t.co/kWA2V4YLxJ
#BREAKING We found files related to the attack against the Steel Industry in Iran.
Initial analysis shows that the malware is connected to the attacks against Iran Railways last year, an attack that was thoroughly described in our previous research.
Here's what we know so far >>
A sample of Industroyer2 appeared on Virus Total 👀. It's not the exact one described by @ESETresearch as the hard-coded configuration differs between the samples.
Sample -> https://t.co/mpskumM7bM
#industroyer2
New job openings — completely remote! 🚀 @_CPResearch_ is expanding and looking for experienced Threat Researchers and Reverse Engineers to investigate top-tier intrusions and nation-state attacks.
Feel free to DM me if you have any questions 😊
👉 https://t.co/UTDTVmcbmr
Microsoft finally killed "enable macros" at a click. Why was this necessary? How did VBA malware become such a nuisance? Judge for yourself whether you're in the "end of a cybercrime era" camp or the "bypasses out tomorrow, business as usual" camp. https://t.co/7jRzvIHUqM
New job openings! 🚀 Check Point Research is expanding and establishing a new *international* force of Threat Researchers. We are looking for experienced Threat Researchers and Reverse Engineers to investigate top-tier intrusions and nation-state attacks.
https://t.co/DPZeQ3HPuI
You’re curious about vulnerability research, but taken aback by the cloud of terms to memorize, processes to follow and names to know? We’ve got you. This breezy, ultra-dense course will introduce you to the who, the what, the why and the how of the field.https://t.co/2G8XYXyg8Q
The 32bit version of CVE-2021-1732 was recently uploaded to Virus Total from Pakistan. The 0-day exploit was used by Bitter APT and developed by the US-based offensive company Exodus Intelligence (aka “Moses”).
https://t.co/CvjHbGGLmh
Took awhile but I was able to create a POC for CVE-2021-40444, the chain itself is very interesting, took me sometime to figure out the .cab file correct structure
We analyzed the recent attacks on Iran and uncovered a hacking group named Indra, who's operating since 2019 against targets in Syria. We share an analysis of their operations and tools, including 3 variants of their wipers — Meteor, Stardust, and Comet.
https://t.co/yEdxX6GcBM
We are excited to publish our analysis of a long-running operation by #IndigoZebra#APT. The attackers targeted the Afghan government and other Central Asian countries — Kyrgyzstan and Uzbekistan, since at least 2014.
Read the technical analysis >> https://t.co/IgYL1FdbRo
We have recently discovered 4 security issues applicable in most MS-Office products.
Read all the details here:
https://t.co/KxPiOnCxeq
cc @sagitz_@NetanelBenSimon
When threat intel meets research - In this short article, We explain how #IcedID C&C servers could be tracked easily by utilizing few simple tools. We also share a list of currently tracked servers and a script to validate them.
https://t.co/S7yGht56R0
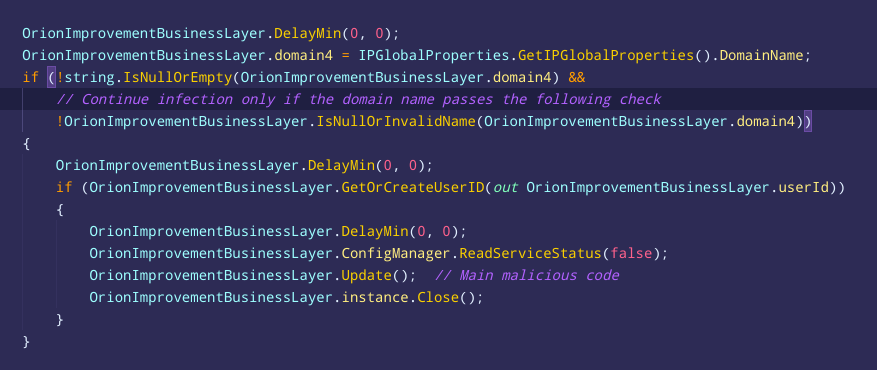
The attackers behind the #SUNBURST malware put a lot of effort into trying to avoid detection by analysts and security vendors. Not only this, but they also tried to make sure to stay under the radar of #SolarWinds developers and employees. A thread >>