@DebadreeC i feel like this is bullshit cos chinese probably do this in chinese and on their internet so we dont get to see it. just from twitter itself, i see them acting like indians in many ways
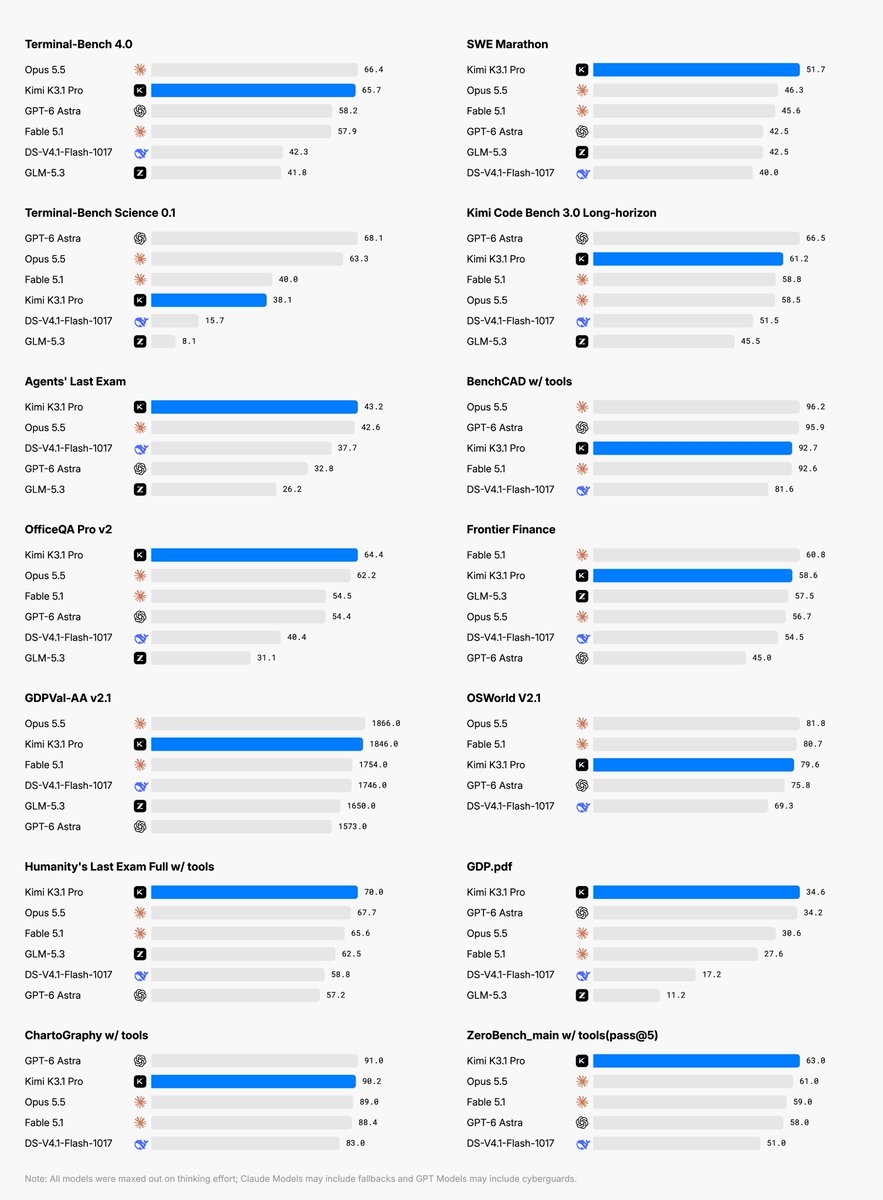
Introducing Kimi K3.1 Pro: our most capable 3T-class open-weight model.
🔹 1M-token context, 2.8T total / 104B active params (MoE), Multimodal.
🔹 Full-project coding: games in Unreal, Unity & Godot.
🔹 Excels at parametric 3D modeling in Blender & CAD.
🔹 More reliable at finance work: Accurate modeling with hallucination down by 65%.
🔹 Matching the strongest proprietary models across coding, agentic and knowledge benchmarks.
Kimi K3.1 Pro and K3.1 Pro Highspeed (2–3× faster) are now live on https://t.co/85jA71X9gw, Kimi Work, Kimi Code, and the Kimi API.
Open weights by Nov 4, 2026.
🔗 API: https://t.co/XCrgjXAqMw
🔗 Tech blog: https://t.co/5iPP0MBej6
@sadist_2003 he is doing good in assembling and has also started a display manufacturing facility. i dont think he is considering venturing again into this business
SITUATION DETECTED: Warhound launched from stealth today with a $200M seed at a $1.2B valuation. Ben Lamm and Palmer Luckey are cloning gene-edited bio-enhanced dogs and equipping them with custom Anduril vests, goggles, and sensors for the military and law enforcement.
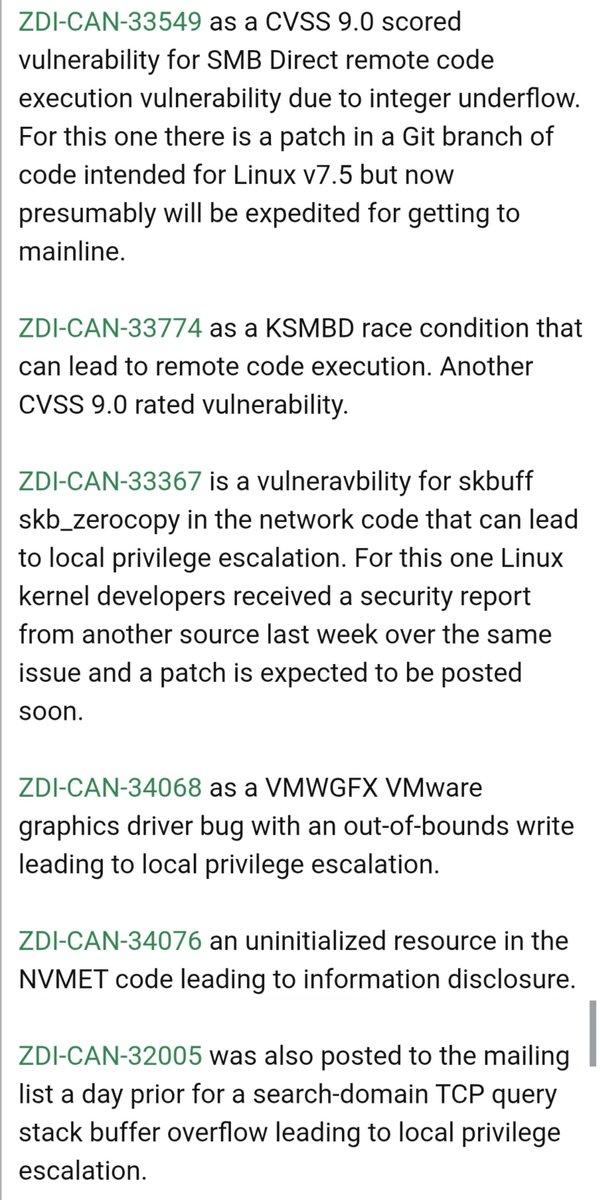
3% of “critical” software security bugs, in all of recorded history, have been found in the last month.
This is on pace to find another ~100,000 bugs this year alone, adding ~26% more vulnerabilities to the all time total
Do you realize how fucking insane that is?
🚨 BREAKING: Node.js just dropped its OWN security bombshell.
4 HIGH-SEVERITY vulnerabilities patched TODAY, including one that could let hackers remotely execute malicious code on vulnerable servers.
→ 10 SECURITY FLAWS were addressed in today's Node.js release, FOUR rated HIGH severity.
→ REMOTE CODE EXECUTION: CVE-2026-111497 is a serious flaw in Node.js's Brotli decoder that could allow attackers to execute malicious code remotely.
→ TLS SECURITY BYPASS: Two separate vulnerabilities could trick affected applications into accepting certificates for the WRONG server under certain conditions.
→ Think about that. Your application could establish an encrypted connection while failing to properly verify WHO it's talking to.
→ THREE MAJOR NODE.JS VERSIONS AFFECTED: Node.js 22, 24 and 26 all required emergency security updates.
→ RUNNING NODE.JS 18 OR 20? Those versions are END-OF-LIFE and aren't receiving these official security patches.
→ PATCH IMMEDIATELY: Update to Node.js 22.23.4, 24.22.1 or 26.12.1, depending on your release line. If you're using Docker, rebuild and redeploy your containers.
PHP AND Node.js both facing major security disclosures on the SAME DAY.
If you run a website or application, TODAY is the day to check your servers.
And remember: the public release of security patches can give attackers a roadmap to systems that haven't updated.
Don't be the last one to patch.
Railway is compromised, rotate all API keys as soon as possible
Deployments are down so don’t wait to redeploy
Attackers are draining keys in real time, we didn’t lose much but can confirm this is still an active attack
Stay safe friends
@catdaddyissues i think pollution can be reduced but it will stay for a bit as we continue to grow. but our window of pollution will be smaller than the countries which went through the growth cycle we are going through cos of innovation in tech, science. the same happened in renewable energy
So basically, today PHP got two critical bugs that let anyone run code on your server without even logging in, which is bad, and then the details leaked before the patch was even out, which is worse, and it works on WordPress and MediaWiki and Magento and Joomla and Laravel, and Censys says like 1.5 million servers are running a version with no fix, so the NSA was like "take your system offline," and the FBI was like "take your system offline," and CISA and the UK and CERT-EU were all like "take your system offline," and then the Prime Minister of Japan, the actual Prime Minister, posted at 5:55 in the morning telling 48.8 million people to take their system offline, so everyone took their system offline, like the Dutch cybersecurity agency took its own website offline, and the Dutch parliament went offline, and the Port of Rotterdam went offline, and Finland and France and Denmark started pulling government sites, and Wikipedia went down, and https://t.co/QlOXb3COq3 went down, and Asana and GOG and Something Awful went down, and the University of Vienna's webmail went down for some reason, and that's just PHP. Because GitLab also dropped a CVSS 10.0, which is the highest score they give out, for a bug that's been there since 2014, so that's every self-hosted GitLab for twelve years, and then LiteLLM 1.107.0 got hijacked and shipped a credential stealer and a remote access trojan in every single wheel and the Docker images, including latest, and you didn't even have to import it, just installing it was enough, and it's the second time this year, and then Railway paused every deployment on the entire platform because someone got into the environment variables, so now everyone has to rotate every secret they've ever stored there, and TiDB Cloud said someone was walking around inside with stolen credentials for basically a month and an extortion group says they took 10.6 terabytes, and Zeabur got breached for the second time in two months and is just shutting down, like the whole company, and Node.js patched remote code execution and a TLS bypass, and CISA says Plex is being actively exploited, and someone took over 300 Tor exit relays to steal SSH passwords, and SafePay ransomware has hit over 600 critical infrastructure orgs, and India's biggest bank filed a data loss incident, and Japan has been in an official state of emergency in cyberspace since October 9, which honestly explains the 5:55 AM post. Oh, and eMudhra, a certificate authority that's issued over 60 million certificates, whose entire job is proving websites are who they say they are, was supposed to be using private keys that are random numbers over a hundred digits long, and one of them was 4. Just 4. And the others were like 66 and 237. Anyway, it's Wednesday.
@catdaddyissues that will happen but ai will also figure out a way to tackle pollution i guess. maybe a more efficient way to absorb CO2 from the atmosphere. i guess we will need a lot of energy for that so yeah india will have to work on increasing energy generation by a lot