Someone submitted 18 "critical" vulnerabilities to Zethora using AI.
Our Sentinel (LoopGhost) built 12 end-to-end PoCs to test every single one.
Result: 0 Criticals. 0 Highs. 1 Medium (already patched).
They got the severity wrong on all 18 findings. The code held.
It doesn’t. But the scam is well-evidenced. In their commits they wrote “we fixed this according to security report [my GHSA ID]”. I did find their legal entity details and their founders are doxxed. They then publicly refused to reply to my reports and told me to legally escalate this if I want to (implicitly acknowledging that they don’t care and that they scammed me)
@ibrahimatix0x01 This is an independently run bug bounty program, with no third-party platform or intermediary involved. Have you ever pursued legal action over a bug bounty dispute?
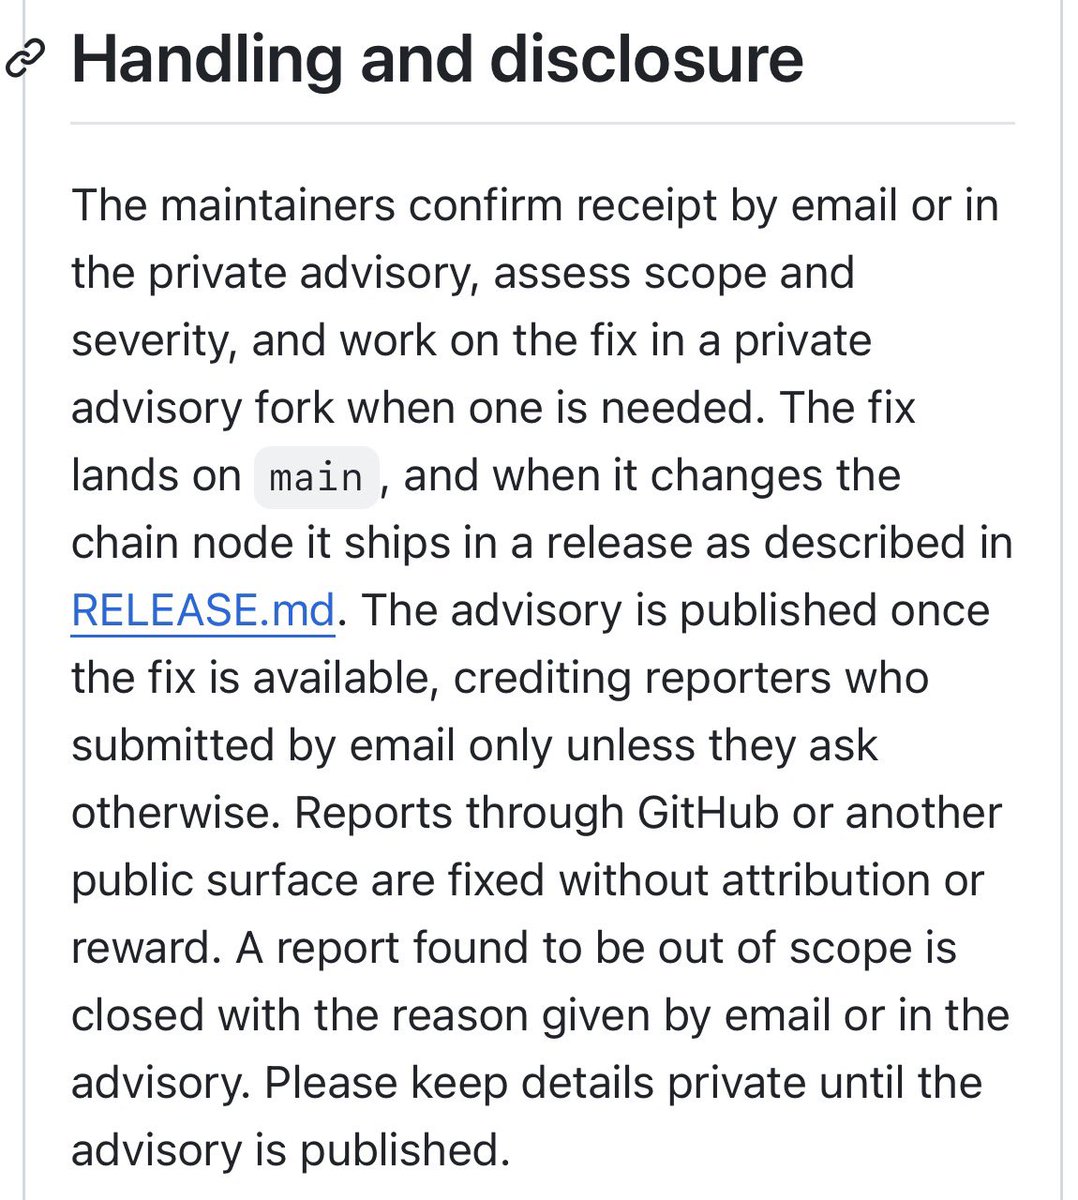
Why don’t you provide a reply according to your own security policy?
You have failed to honor your own SECURITY.md commitments. You silently fixed my reported vulnerabilities without ever acknowledging, assessing, or responding to my reports. Why are you falsely claiming that these issues have already been addressed with me when I have received absolutely no communication?
Last chance, provide a reply and address this or I’ll escalate it.
@sidioralabs@paxeer_app@Schlegel335 Provide a reply inside each GHSA if you indeed want to resolve this and pay the corresponding bounty amounts.
Just come here and provide a reply to each of them:
��� https://t.co/YkTjdfyf2V
• https://t.co/9YRn5Fg6vn
I am giving you 48 hours to resolve this cordially.
@sidioralabs you have not discussed anything with me and I have never harassed any of your community members. Please don’t lie. You never provided a formal reply to these bug bounty submissions, and your public commits show that you applied the fixes thanks to my reports. Be serious and honor your own bug bounty terms. I ask you to provide a formal reply within the next 48h inside each GHSA before I escalate this.
Hello @paxeer_app . Please provide a reply to GHSA-mjjc-9pq8-vv3w and GHSA-fhhj-6jhx-mwph. I submitted them under your bug bounty program, you fixed them referencing my GHSA IDs and never provided a reply nor a bounty decision. I have attempted to get in touch with you, but I have not received a response.
Hello @Schlegel335 . SLA has passed and I have not received a reply from the team. Could you please ask the dev team to provide a clear reply according to what is promised on SECURITY.md?
I genuinely don’t want to believe Paxeer is acting in bad faith or deliberately avoiding its bounty obligations, but the continued silence and recent treatment are becoming increasingly concerning.
I just want this resolved fairly and privately. If you indeed want to resolve this, please DM me and let’s clarify this.
@Schlegel335@paxeer_app Please provide a reply and clarify this @Schlegel335 . There is no public evidence supporting your duplicate claims, and the fix commits reference my GHSA IDs.
Your own Git history contradicts your duplicate claims.
My GHSAs were submitted on Nov 1 at 00:21 and 09:31 UTC. Neither vulnerability appeared in spec.kvx at the respective pre-submission commits (a8dfde87 and 973b9196).
Both tasks (22.23.1 and 22.23.3) were first introduced in commit 4087468 on Nov 2 at 23:21 UTC, 47 and 38 hours AFTER my reports. That commit explicitly references my private GHSAs and calls the tests “the reported reproductions.”
I only went public because you ignored my private reports. You’re the one choosing to prolong this publicly with personal attacks.
I’ve now provided concrete evidence contradicting your claims. I expect you to honor your own bug bounty terms, process both rewards, and respond PRIVATELY within EACH GHSA. If you still claim duplicates, provide timestamped pre-submission evidence there.
Please stop mocking me. I’m being serious, and I don’t understand why this has turned into a public shitshow. From the very beginning, all I asked for was an update within each GHSA, not a public argument. It’s the bare minimum after taking the time to responsibly report these vulnerabilities.
Why so much arrogance and hostility? I’m a security researcher who spent considerable time identifying and responsibly reporting vulnerabilities to help secure your network. Instead of even basic acknowledgment, I’ve been ignored and now treated with mockery and disrespect. I genuinely don’t understand this attitude.
I only reached out publicly because your team repeatedly ignored my reports and follow-ups through the proper channels.
After all the time I’ve invested in your security, I think the bare minimum is a professional, detailed response within each advisory (GHSA-mjjc-9pq8-vv3w and GHSA-fhhj-6jhx-mwph), including the specific evidence supporting your duplicate claims.
I’m simply asking for transparency and basic respect for my work. Is that really too much to ask?
I genuinely have no idea what you’re talking about when you claim that “this reporter was informed.” Nobody has informed me of anything. Your development team has completely ignored my reports and every single follow-up, without providing even one acknowledgment or response.
For absolute clarity, I am referring specifically to the following two GitHub Security Advisories:
GHSA-mjjc-9pq8-vv3w
GHSA-fhhj-6jhx-mwph
I find it absolutely disgraceful that I have to learn about your supposed bounty decision through a public tweet, rather than through direct communication in the GitHub Security Advisories where I responsibly disclosed these vulnerabilities.
You now claim that both issues were already in your public task list, flagged days before my submissions. If that is true, providing evidence should be straightforward. Please share the exact public records, including their original creation timestamps, demonstrating that both specific vulnerabilities, their root causes, and their security impact had already been identified before my reports.
It is extremely suspicious that two severe vulnerabilities affecting your live mainnet were supposedly known to your team, yet remained unpatched until approximately 48 hours after I submitted my reports.
Your team appears to have had no difficulty using my disclosures to implement fixes, yet somehow could not find the time to show basic courtesy and respect for my work by communicating with me directly, even after your own disclosure SLA had expired.
Please provide this evidence directly within EACH of the two GitHub Security Advisories, rather than making unsupported claims about prior discovery and communications that never took place.
Please act professionally. Independent security researchers deserve transparency, respect, and proper communication, not silence followed by a public bounty rejection without supporting evidence.
@happydreamer31@paxeer_app Hey. Did they mitigate your vulnerabilities on main? They did mitigate the ones I reported, but I have not received any update…