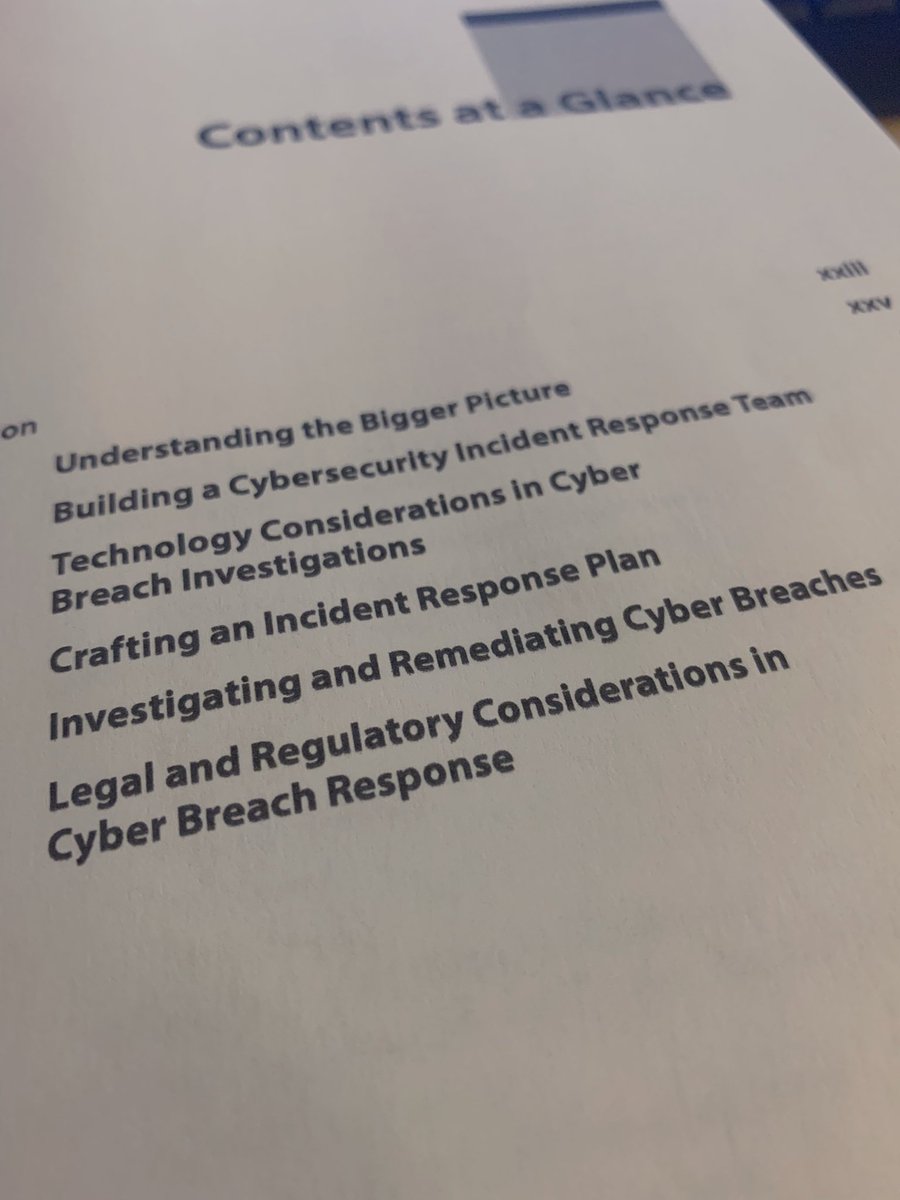
https://t.co/L8ZZM4Bdcf
Provides a timestamped, outside-in view of how public routing collectors see your internet footprint.
AI assisted in its development, but no AI is used at runtime to collect, evaluate, score, or interpret evidence
124 años de colonialismo, es demasiado. Mañana, luego de negociaciones que llevamos trabajando desde noviembre del 2021, la Cámara de Representantes votará sobre el histórico proyecto de Estatus vinculante, el H.R. 8393.
Aquí mis expresiones hoy en el Comité de Reglas.
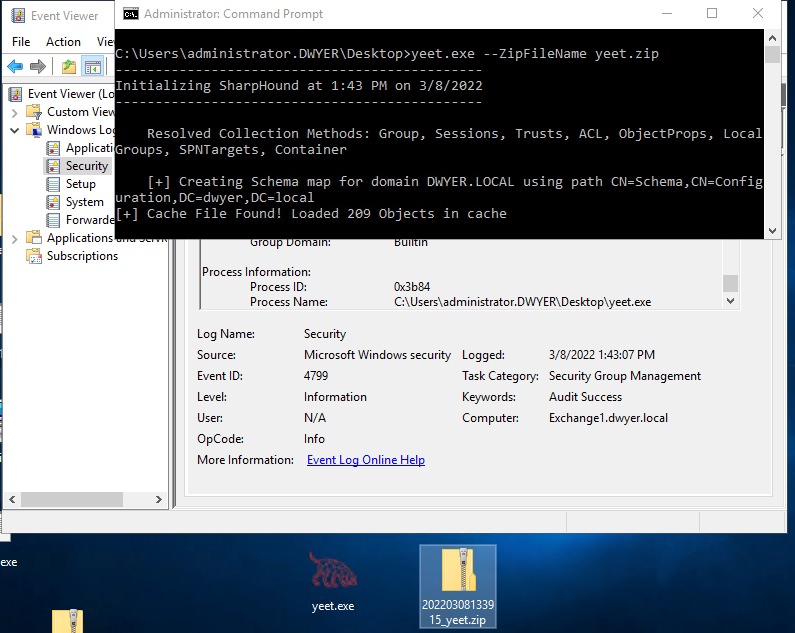
Is it easy to modify the name and output file of SharpHound? Yes. How often do we find evidence of SharpHound being run just with the defaults? It's a lot you guys. Zip files named "*Bloodhound*" and EID 4799 containing "SharpHound.exe" works...like a shocking amount of times
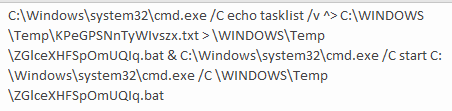
ProcesName:"cmd.exe"
CommandLine contains "/c echo" AND ".bat" AND ".txt"
UserName:SYSTEM .
Rule was created 4 years ago. Still works. Caught an evil fishy running this today.
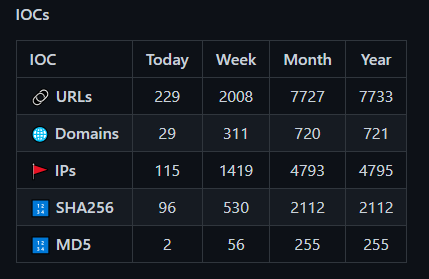
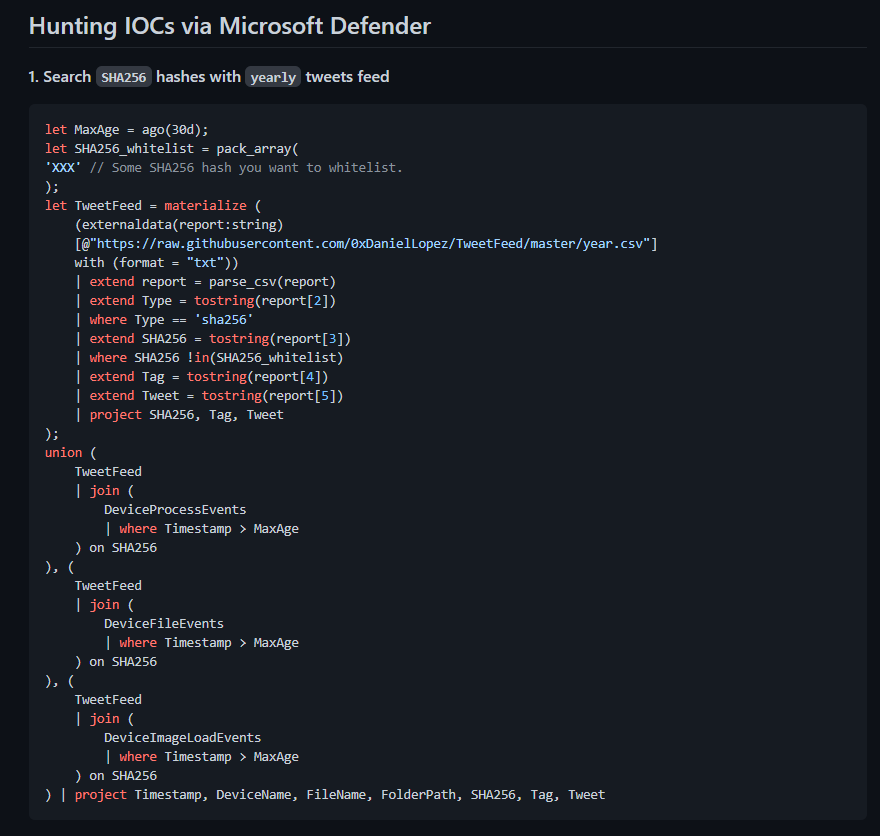
Presenting "TweetFeed"
Public repo that collects IOCs posted on Twitter in order to search them in your environment.
Interesting for #BlueTeam members, contains:
- URLs
- Domains
- IPs
- MD5/SHA256 hashes
Also includes queries for MS Defender.
🔗 https://t.co/C0a7fdxCvS
Well Posh-SSH 3.0 is out, with breaking changes, been ready for release now more than a week but nervous about breaking dev pipelines .. 🤞 .. at some point I had to release https://t.co/RHv0u4Pnxb changes https://t.co/ESGgUxWnAa #powershell
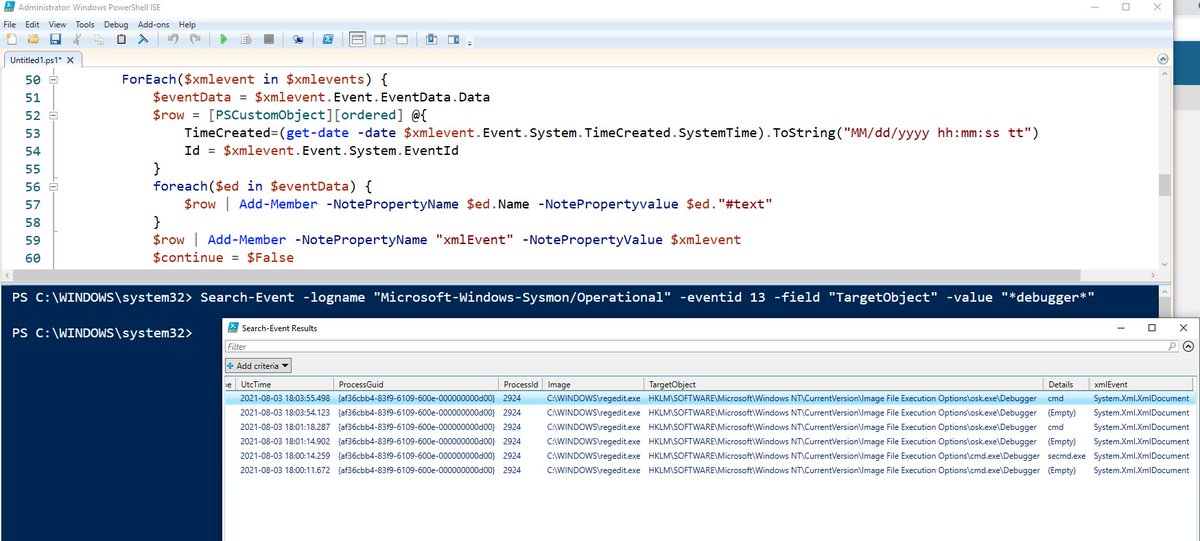
I am releasing Search-Event! My solution to a better way of searching through Windows Event Logs. Uses Out-GridView but you can use the -raw and export to csv/xls if you want. Has raw search functionality as well. https://t.co/nvMAIdgih7
Lateral Movement using DCOM Objects - Guide to using DCOM Objects in order to Move Laterally in the Network.
#infosec#pentest#redteam
https://t.co/K1ARS23ua8
RW operators continue to switch to tunneled RDP when they move into the data collection and exfil stage of the op. Real low hanging fruit to detect this behavior in the WELs that might save your bacon. note: if adv fwds to "localhost" the source network address is ::1 @XForceIR
Living off the land #DFIR. Things you can use during incident response when you can't bring your tools or run scripts:
1 - Use Windows Resource Monitor to see active network traffic by process name, remote IP and destination ports
APTSimulator 0.9.0 featuring #CobaltStrike beacon activity simulation with
- NamedPipe Creation
- Service installation & exec pattern
- HTTP beaconing
https://t.co/iaWzoQerXG
If you want to help, add some steps in here:
https://t.co/FtKPAVSWTP
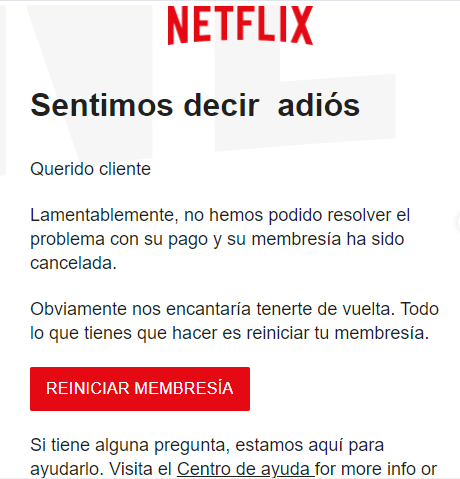
Llegó este correo
El botón de "REINICIAR MEMBRESÍA" lleva a una página que parece de @netflix y dice netflix en la dirección, pero NO ES NETFLIX
https:// netflix-cliente [.] com /account/app/login
Signal made Instagram ads that shows users how much Facebook knew about them.
Facebook banned them.
“Being transparent about how ads use data is enough to get banned; in Facebook’s world, the only acceptable usage is to hide what you’re doing.”
https://t.co/DwAZeD5IWn
Who is ready for a high performance Sysmon EDR based on Powershell?
✅MITRE ATT&CK
✅Yara Scanning
✅Kill Parent and all Child Processes
✅Kill Network Connections
✅Firewall Processes
✅Kill Parent/Child Processes
✅Notifications
https://t.co/XKU2J3tXze
.\install_edr.ps1