Released: November 2026 Exchange Server Security Updates https://t.co/pwQGUzQ9z8
The SUs also resolve the issue with the Windows Server updates from October, but no need to remove any reg keys you added.
#MSExchange#Security#Updates
‼️ WARNING - Cisco confirms active, in-the-wild exploitation of a new critical flaw (CVE-2026-76519 // CVSS 9.8) in Cisco Secure Email Gateway.
Unauthenticated attackers can achieve full root command execution simply by sending an email with a crafted attachment.
Details >> https://t.co/Yb1QWiWxQu
Bring Conditional Access and MFA to your on-prem resources with Microsoft Entra.
Get started. https://t.co/dKhr4Wr1Gi
Connect users to on-premises resources while enforcing Conditional Access policies, including MFA, and eliminate the need for VPNs using Secure Access Service Edge with Microsoft Entra.
Route authentication through Microsoft Entra before granting resource access, even within legacy on-premises systems. #SASE #MicrosoftEntra #GlobalSecureAccess
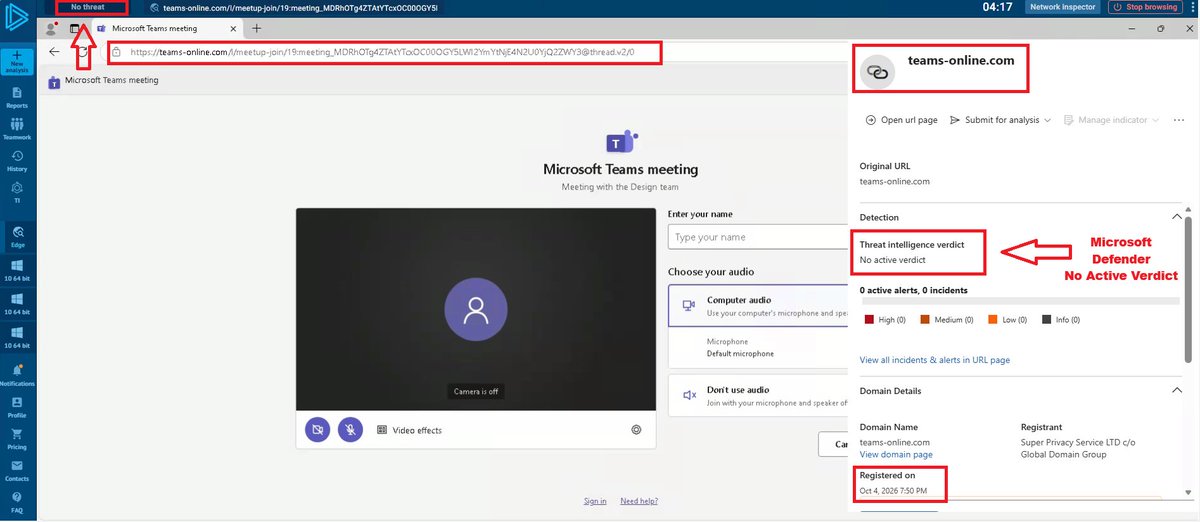
🚨 Threat Alert: A newly registered domain, 𝘁𝗲𝗮𝗺𝘀-𝗼𝗻𝗹𝗶𝗻𝗲[.]𝗰𝗼𝗺, created just 𝟰 𝗱𝗮𝘆𝘀 𝗮𝗴𝗼, is actively mimicking the full Microsoft Teams login and user interface.
At the time of analysis, 𝗠𝗶𝗰𝗿𝗼𝘀𝗼𝗳𝘁 𝗗𝗲𝗳𝗲𝗻𝗱𝗲𝗿 𝗿𝗲𝗽𝗼𝗿𝘁𝗲𝗱 𝘇𝗲𝗿𝗼 𝗱𝗲𝘁𝗲𝗰𝘁𝗶𝗼𝗻𝘀, so don't rely solely on endpoint protection. Consider proactively adding this domain to your tenant's block list and web filtering policies immediately.
#threathunting #threatdetection 🫡
Storm-2945, a sub-cluster of the Russian state actor Midnight Blizzard, has resumed their CaptiveCrunch campaign. https://t.co/Dmf4gQOVqI
First reported by Microsoft Threat Intelligence in July 2026, the campaign uses manipulated network traffic and captive portals in the hospitality sector to gain access to targets.
The renewed activity is consistent with reporting from Black Lotus Labs suggesting that multiple managed service providers are implicated; Storm-2945’s continued access to these upstream providers has likely enabled this rapid re-deployment.
We have updated our blog to provide more recent network infrastructure indicators, detections, and hunting guidance. We want to thank Google Threat Intelligence Group (GTIG) for their collaboration on tracking the reemergence of this activity.
PSA: Starting the second week of September 2026, Microsoft will raise the minimum allowed version of Exchange 2016/2019 servers that connect to Exchange Online over an inbound connector type of OnPremises to the October 2025 SU.
https://t.co/kKDEmnWXdd
#MSExchange#Security
Nearly 22,000 Microsoft Exchange servers exposed online remain unpatched against a high-severity authentication bypass vulnerability that allows attackers to hijack all user mailboxes.
https://t.co/RGMp2NItTW
DUDE Manager v1.7.x introduces Posture.
A review surface for runtime mode, permissions, telemetry evidence, config state, and redacted exports before relying on the automation.
Automation needs evidence.
https://t.co/aZ7dvGRQ4S
#MicrosoftIntune#PowerShell#EntraID#MVPBuzz
@BleepinComputer Device-code flow was built for TVs and printers. Tycoon2FA abuses the 15-min token window after just one click. Block it in Conditional Access for any user who doesn't need it. https://t.co/erqBhksJSn #ZeroTrust
An oldie, but still valuable way of finding inactive Exchange Online distribution lists. Use the message trace log to check for expand events and then use the unique email addresses found to know if a DL is active or not.
https://t.co/0s7QmVKKfn
#Microsoft365#PowerShell
Microsoft Defender for Office 365 has new LLMs that are able to detect attacker intent with 99.995% accuracy, and now blocking 140,000 BEC emails per day.
"These models have been trained on one of the largest datasets in the industry and enable more accurate identification of text-only attacks"
Available by default in Defender for Office 365 Plan 1, which is included in Microsoft 365 Business Premium.
Announcement: https://t.co/JAaeFqk2ZC
@rucam365 Yes I use Break Glass Accounts, normally 2. Super strong passwords, locked up in a safe or stored in Cyberarc or something similar.
• Global Admin (not PIM enabled)
• Password Never Expires
• No MFA
• Excluded from all Conditional Access policies
• Cloud-only
💥 BOOM! We just can't stop with all the Entra announcements 😂
Platform SSO for macOS is here!!!! 👏 🎉🥳🙌🍾
With Microsoft Entra Join for macOS you can now use Touch ID to unlock your device and be signed into Entra ID under the hood using a device-bound key.
🧵👇
It's here folks. 🎉 Microsoft really, really wants to eliminate passwords and the answer is passkeys!
Learn all about the announcement and how you can enable the preview and try it today.
https://t.co/BjrpKPZ1Tj
This is the way.
@RebeccaWUvell Kan väl finnas typ 1000 anledningar, som att ha kommit hem från resa eller vad som helst, men samtliga är helt oviktiga, det viktiga är att du inte har med saken att göra och att du ber dig fruktansvärt illa åt mot alla de som nu sörjer en tragisk olycka. Skäms
Important note! If you are using a trial license to test #msintune Cloud PKI your keys will be store in software, not HSM! HSM is available only for licensed deployments. Keep this in mind because you can't change it later! #PKI
@MSFT365Status So many helpful people here! It will for sure be fixed much faster because of your “down in Bigcity” comments. Or “going Slack” comments. Keep it up! Have a great weekend! 🕺🧠
As part of our work to remediate any residual impact, we’re removing affected false-positive spam messages from quarantine and replaying the messages. We're closely monitoring the service as our work progresses, more info is provided in the admin center under EX682041.