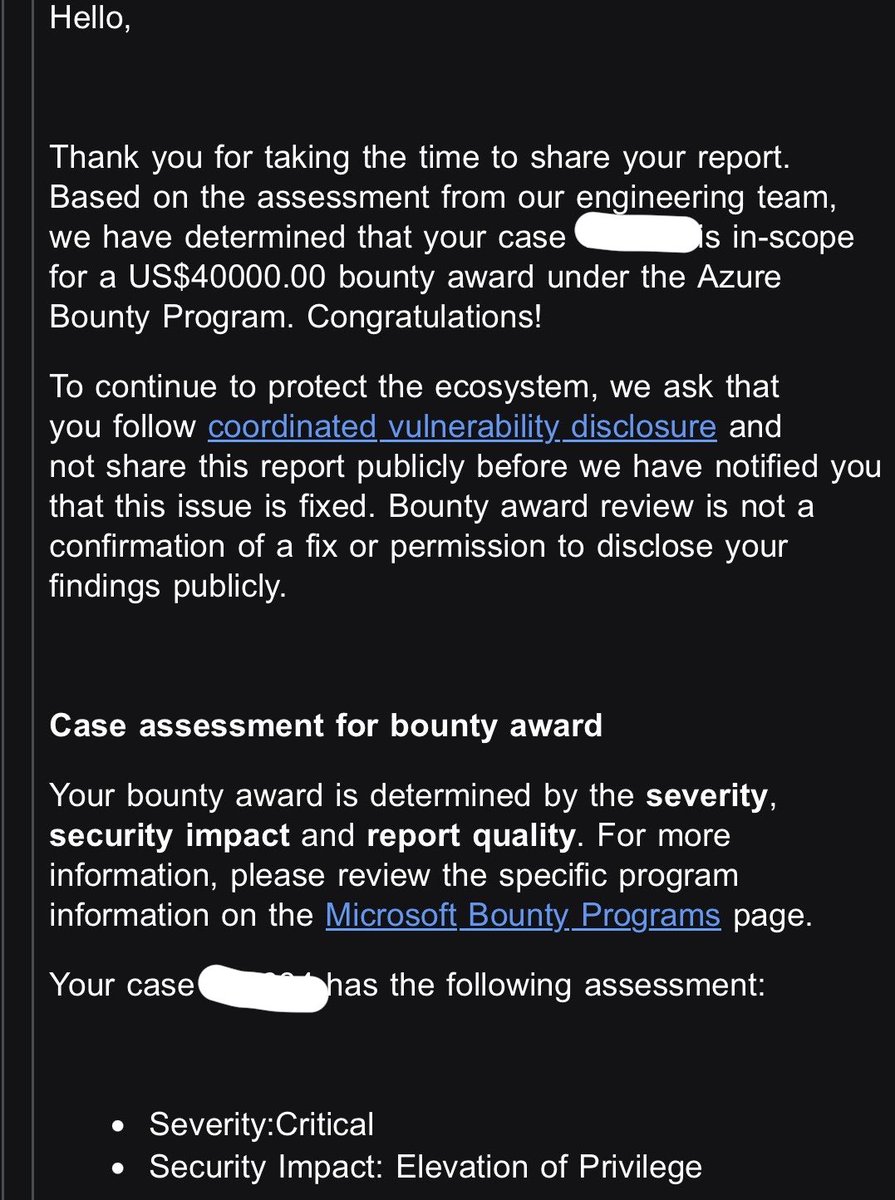
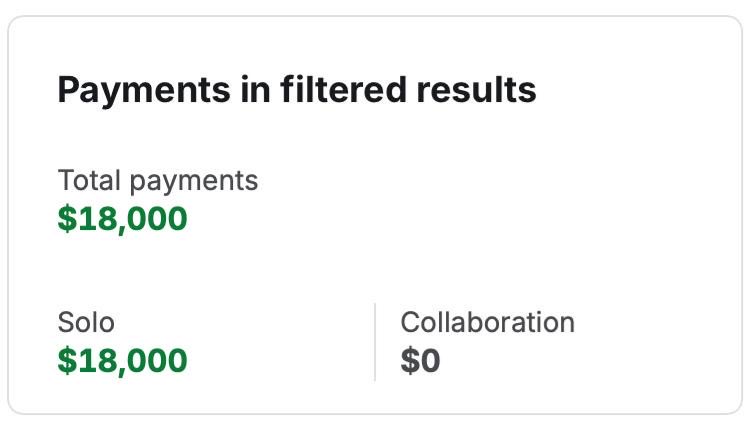
@watcherendpoint That with some brainstormed attack scenarios, if extension available try this and that, (mainly focused on custom extensions and how they processed users input and who have access to them)
@watcherendpoint I corrected that it was 4,8 , besides that they seem the same to me for security research
Manual (recon, and mapping important attack surface) by itself was amplified by llm basically i put a lot of a bug class findings into conversation, combined …
@PoCForge For poc i have a specific skill when it comes to cross tenant or privilege escalation inside cloud, where i use canary files/content and models has to adapt whatever it produce to reading that content
People defending this don’t know terms and conditions they accept before submitting a report, if you intend to play the vigilante just don’t do bug bounties, playing the double sides is bit hypocritical
@methematikoi allaaaah I love the hate towards that dude, I remember I tried to reason with him once and blocked me, maaan he is such a slop, was made from hype and Mgharba Hnan
Made over $25K hacking marketplace app permission issues across various bug bounty programs.
Here's my latest writeup on how a malicious app might take over a GitHub repository: https://t.co/LmPuptQpnZ
#bugbounty
Also, and due to the fact that most of the times its shared instead of dedicated hardware, you can find different kind of cross tenants issues, and most of them are logical, doesn’t require you fuzzing the engine, that’s exactly what I am trying to build at @Poneglyphsec 1/n
Microsoft’s finding wasn’t my only hit for managed db bugs using AI
https://t.co/ZIgvW1Iuxg
And I know its full of em dashes (i wrote initial draft and AI rewrote later)
Besides this managed runtimes/dbs are a good area of research 1/n
@mfmASmOO7 become good at coding with C++, networking, and jump to CTFs, use AI as tutor and accelerator, that what I heard from someone who got 100K from google in bug