New Op Report: a live DPRK linked operator ran a full "PolinRider" supply chain intrusion inside it. Package lure → JS C2 → Python stealer → persistence disguised as a .NET service.
Not a signature feed. The operator, captured live.
Abe RAT signed "Kimberley Hankinson"
h/t @malwrhunterteam
"Abe" is likely short for "App-Bound Encryption". Uses hidden browser to decrypt passwords
Leveraged @malbeacon 's DeceptionPro to watch hands on activity.
Full blog: https://t.co/JEUIixYOUk
Thanks to @malbeacon 's DeceptionPro, we got another stage and a new C2.
The next stage, if installed on a server, copies itself to hosts that RDP to the server. See details in the blog post: https://t.co/90Wd9NzpFd
C2: work.nddswa[.]com
🩸 KongTuke ClickFix → an EtherRAT that reads its C2 off the Ethereum blockchain. No registrar, no takedown.
Then hands-on-keyboard to SystemBC. 12 days, captured live w/ full TLS inspection.
New Op Report: a live DPRK linked operator ran a full "PolinRider" supply chain intrusion inside it. Package lure → JS C2 → Python stealer → persistence disguised as a .NET service.
Not a signature feed. The operator, captured live.
New Op Report with @proofpoint PackClient, a new C2 framework from Chinese speaking actor TA4922, detonated in a live DeceptionPro honeynet.
The RAT was just the doorman. 4.5 hours in, the operator enrolled the victim into an attacker owned ManageEngine Endpoint Central server.
New Op Report: an operator took the bait on one of our honeynets and ran the whole chain.
Phishing lure to batch script to silent ScreenConnect install, hands-on-keyboard then XLoader / FormBook.
Interactive RMM + automated stealer in one op. Not a pairing we'd seen before.
Mustang Panda walked into two DeceptionPro environments and stayed for days. IBM X-Force wrote it all up: a brand new hidden VNC backdoor (Havencode), Toneshell v10 over WebSockets, a full exfil playbook, and typos in the shell proving a human was typing.
#XWorm#AdaptixC2#ScreenConnect
I have been working with @malbeacon and the https://t.co/ZEYjVVBKZD platform.
Here's a write up of a recent deception operation👇
https://t.co/Dx77XgAl4f
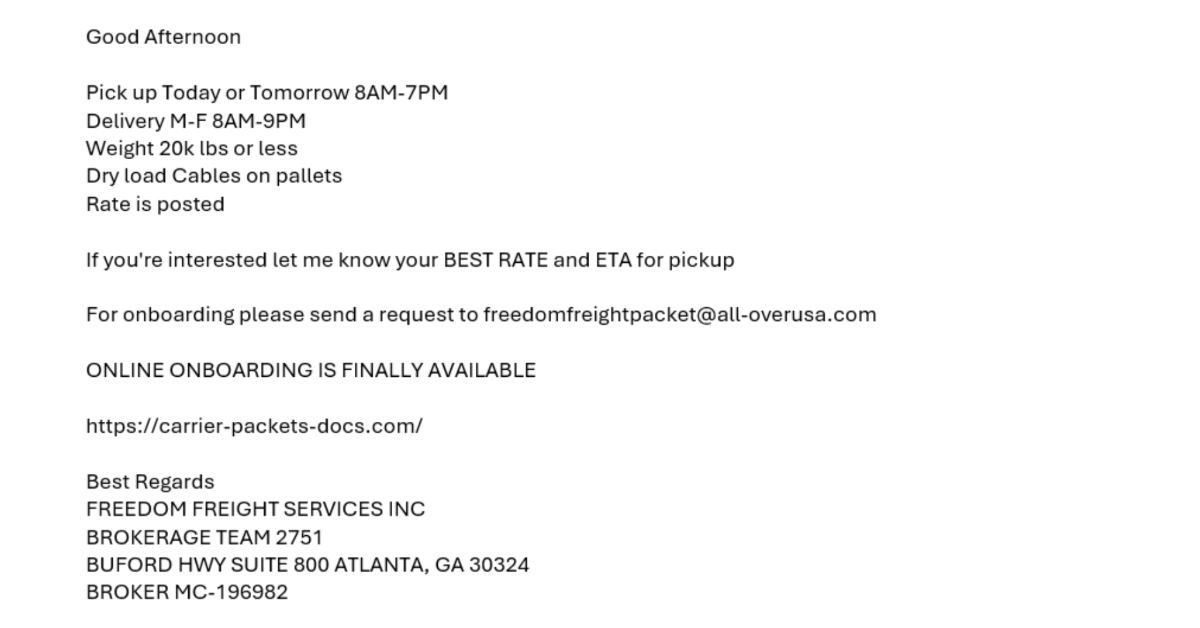
Proofpoint baited a cargo/transport industry threat actor into performing its activities in a decoy environment operated by https://t.co/74FvO0XMu5 for 30+ days.
The result: rare, visibility into post‑compromise operations, tooling, and decision‑making. https://t.co/jT3KF4O1NM
New @Proofpoint blog: cargo theft actor spent 30 days inside DeceptionPro environment revealing:
* 4 RMM tools
* Malicious code signing-as-a-service
* 13+ PowerShell scripts, and bank access.
* HoK activity whole way.
This is real adversary telemetry.
Link in thread.
🚨 Trojanized CPU-Z → STXRAT → PureLogs Stealer → PureHVNC → 54hrs of exfil through a hidden QEMU VM.
We caught everything after.
First documented full post-exploitation chain for this campaign. IOCs & hunting artifacts link in thread
#ThreatIntel#DFIR#Malware