🌍 Top Targeted Countries — October (Month-to-Date)
Ransomware attacks from the start of October until today:
🇺🇸 United States: 37
🇧🇷 Brazil: 4
🇬🇧 United Kingdom: 3
🇩🇰 Denmark: 2
🇹🇭 Thailand: 2
🛡️ Come see what you're missing: https://t.co/1TFlJ1IuL7
#CyberSecurity #Ransomware #ThreatIntelligence #InfoSec
Google's Android developer ID requirement is now live. Apps from unregistered developers are blocked on certified Android devices in Brazil, Indonesia, Singapore, and Thailand. The rule goes global in 2027.
To register, developers hand Google a government ID, their legal name, address, email, and phone number. They also pay $25. This applies even if the app never touches Google Play.
Google says sideloading isn't going anywhere. F-Droid called that claim "clear, concise, and false." Users who want an unverified app now face ten steps, developer mode, several warning screens, and a 24 hour wait.
Google is clearly putting the squeeze on Android's openness.
https://t.co/dhJ63S2uOK
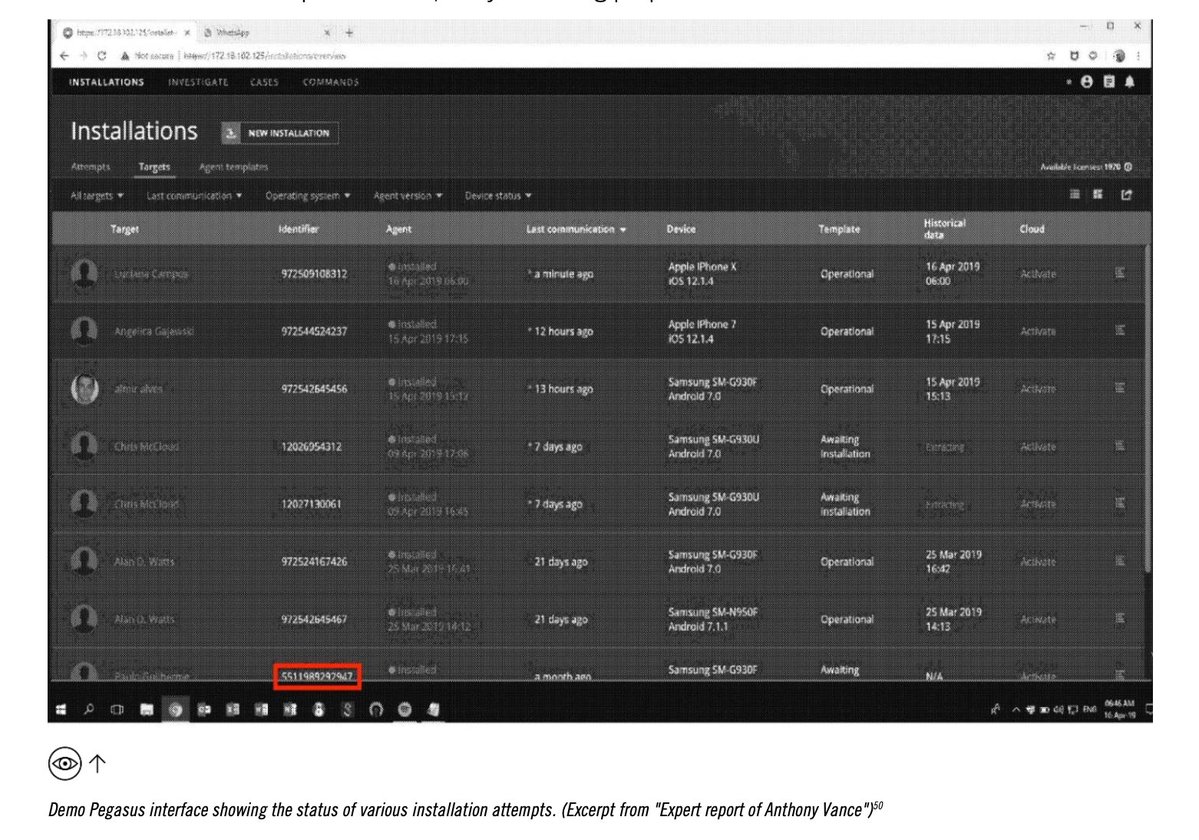
‼️ Amnesty International has linked the 2021 Pegasus hacks of Spain's defence and interior ministers to Morocco.
A Spanish court order names the Apple account that compromised Margarita Robles' and Fernando Grande-Marlaska's phones with zero-click iMessage exploits during that year's diplomatic crisis with Rabat. It was also used against an exiled Moroccan journalist and a French pro-Sahrawi activist. NSO's own documents show every client gets its own attack accounts.
Amnesty says Morocco's DGST also selected almost 13,000 numbers as potential Pegasus targets and planted spyware on phones sold to activists in shops.
🚨 In a new @amnesty report, an ex-security agent exposes how Morocco’s surveillance system works, explaining how journalists & activists are targeted in operations designed to instill fear & ultimately silence & stop them from doing their work.
https://t.co/6K7pXw6XfN
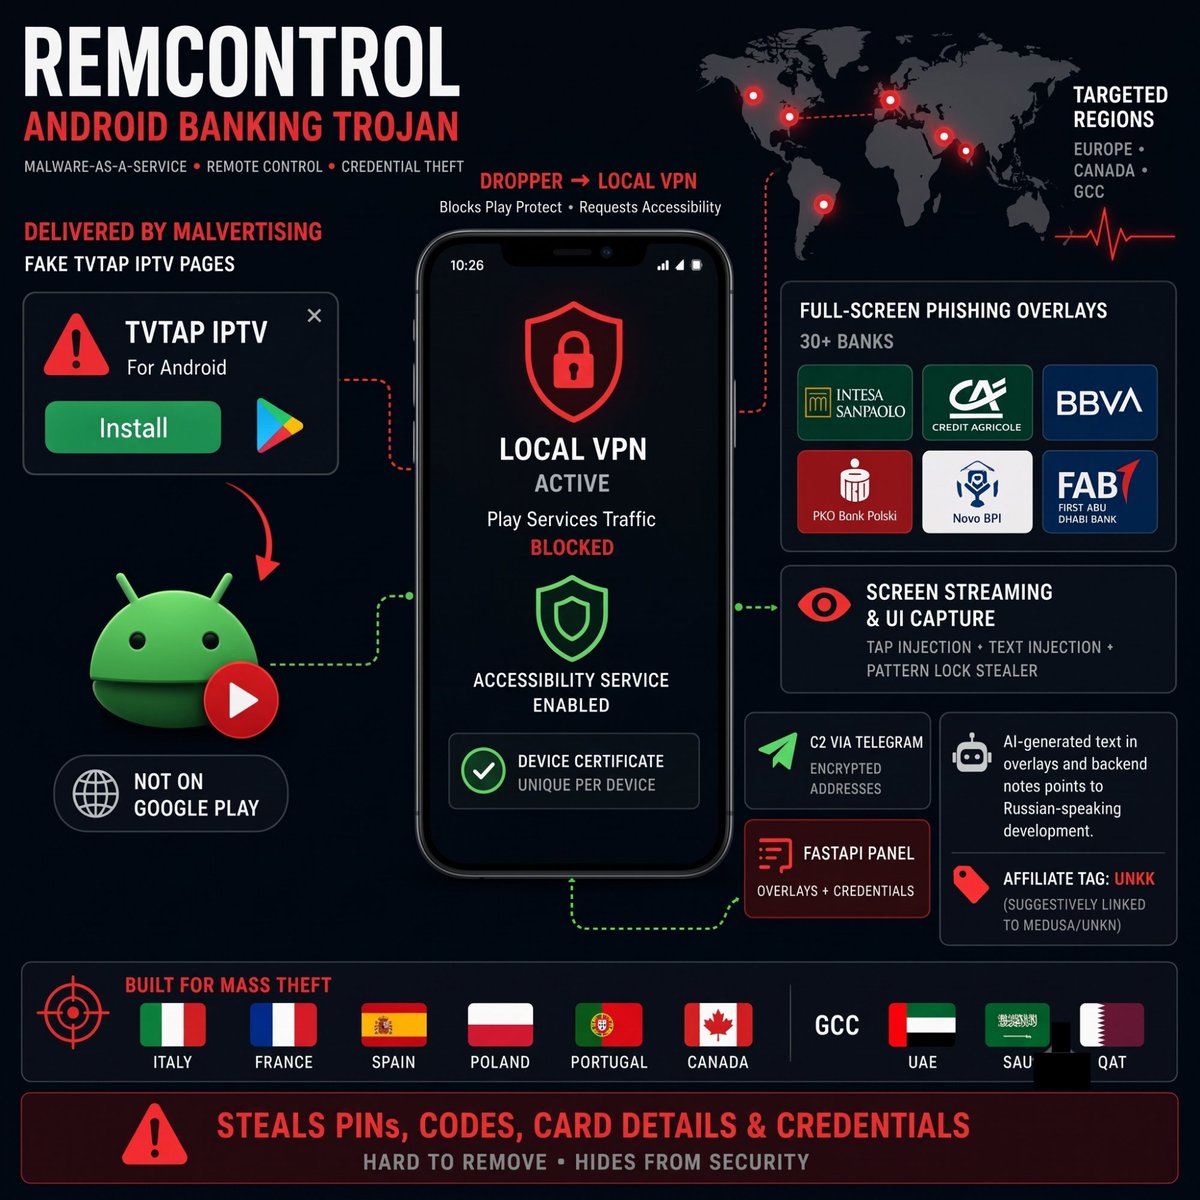
🌍RemControl Android banking trojan, tracked by Group-IB as operator UNKK, spreads through fake TVTap IPTV pages and steals credentials across Europe, Canada, and the Gulf
1️⃣RemControl is a newly documented Android malware-as-a-service banking trojan whose infrastructure has been active since at least May 2026 (a command server domain was registered on 12 May) and whose first samples reached public analysis in July 2026 (VirusTotal submissions from 19 July).
2️⃣It is delivered by malvertising to fake Google Play pages that impersonate TVTap, a third-party IPTV app not sold on the official store; at least one Italian campaign used geofencing and mobile User-Agent checks, and the pages carried Meta Pixel tracking identifiers.
3️⃣After install, a dropper starts a local VPN that blocks Google Play services traffic so Play Protect cannot scan in real time - the same technique seen in ToxicPanda - then requests Accessibility Service access and signs a unique certificate per device.
4️⃣With that access it can show full-screen phishing overlays for more than 30 banks in Italy, France, Spain, Poland, Portugal, Canada, and GCC states, steal PINs, codes, card details, and credentials, stream the screen and UI tree, inject taps and text, capture pattern locks on major OEMs, and block removal from settings.
5️⃣Operators pull encrypted command-and-control addresses from Telegram, exposed FastAPI panel documentation confirmed overlay and credential endpoints, and AI-generated text left in overlays and backend notes points to Russian-speaking development; Group-IB links the affiliate tag UNKK only suggestively to the Medusa affiliate UNKN, with no published victim or loss figures.
#privacy #cybersecurity #android #ios #mobilesecurity #appsecurity #malware #spyware #malloc #news
Happy Independence Day, Cyprus! 🇨🇾🕊️
Today we celebrate the history, culture, and unbreakable spirit of our island home under endless blue skies. 🌊☀️
Drop a 🇨🇾 below to celebrate with us! 👇
📸 IG nature_in_motion
#VisitCyprus#Cyprus#CyprusIndependenceDay
Researchers at Island say that attackers are creating their own content inside ChatGPT – via CustomGPT – and then buying Google ads to direct people to it. Full article ➡️ https://t.co/6efhjJn4BB
❗️ Tech site Android Central's entire staff has been fired because of the rise of AI chatbots.
Several staff confirmed their exit on LinkedIn.
Owner Future plc hasn't commented, and the site is still online.
Google search traffic was falling faster than expected as people transitioned to AI, which led to fewer clicks to their website.
🚨 YOUR ANDROID CAN RECORD DEVICE ACTIVITY. CHECK WHAT YOU’RE SHARING!
With System Tracing active, your phone can capture processes, CPU activity and system events. Those recordings can accompany bug reports.
Before sending diagnostics to anyone, check Developer Options → System Tracing. Turn off “Record trace” unless you’re troubleshooting, and review “Attach recordings to bug reports.”
At @efani, we recommend treating diagnostic files as potentially sensitive. NEVER send them to someone whose identity you haven’t verified.
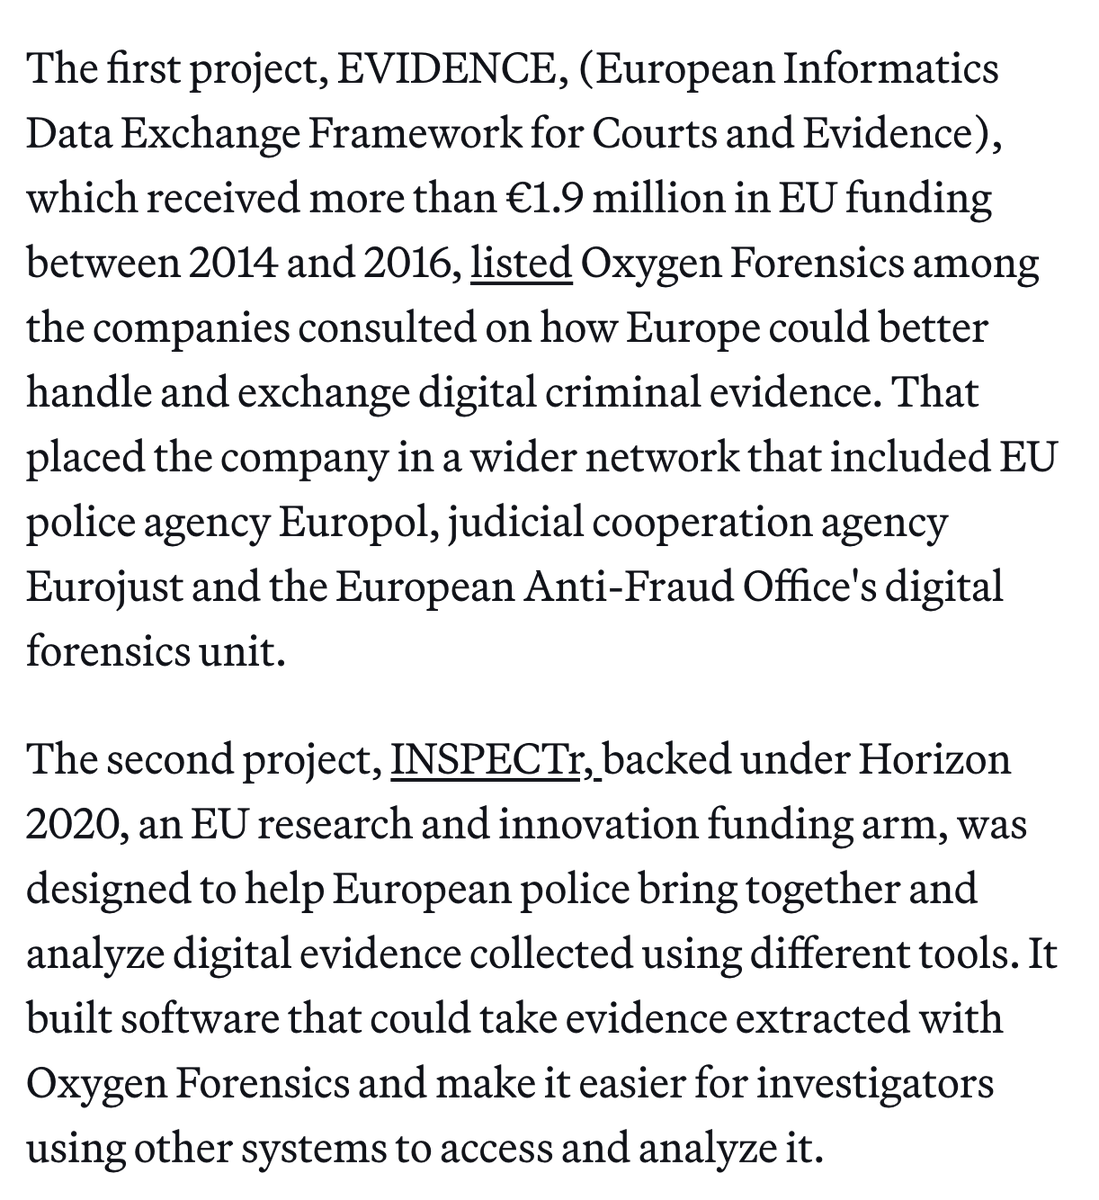
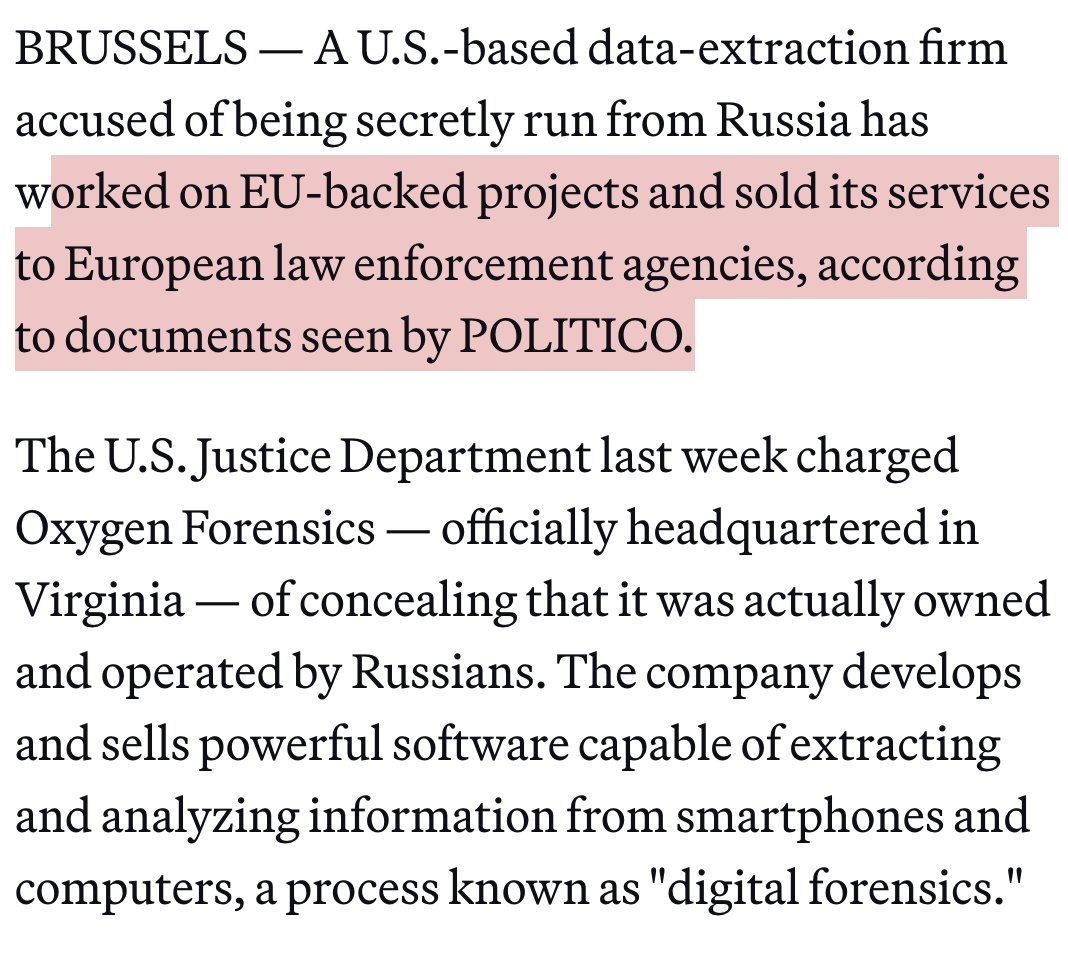
European cops bought this phone-cracking tech for years
Turns out it was secretly 🇷🇺Russian, managed from Russia by a team servicing the FSB!
There were clear warning signs. Dissidents & civil society warned about Oxygen Forensics.
It didn't matter, and police in....
🇩🇪 Germany
🇪🇸 Spain
🇮🇹 Italy
🇵🇱 Poland
🇱🇻Latvia (bought just this Month!)
🇭🇺 Hungary
🇷🇴 Romania
...kept buying.
Even the European Commission was listed as a client.
Well, the US just arrested the CEO & seized the website.
BIG PICTURE:
As spyware researchers, we've warned that European countries aren't properly vetting the phone hacking companies they use.
The national security risks are blindingly obvious.
Will Europe start paying attention to the danger now?
Story by @AntoanetaRoussi
https://t.co/FRYeltFkw5
It looks exactly like a regular flash drive.
but it's not.
When you plug in a normal USB drive, your computer mounts it as storage but when you plug in a Rubber Ducky, your computer registers it as a keyboard.
keyboards are trusted by default so no antivirus scan.
The Ducky immediately starts typing a preloaded script at up to 1,000 words per minute. faster than any human.
In seconds it opens:
— opens a hidden PowerShell window
— downloads a reverse shell
— creates a backdoor account
— exfiltrates saved passwords
— installs persistent malware
DuckyScript 3.0 made it worse. the payload now detects which OS it's on Windows, macOS, Linux and adapts automatically.
in 2026 red teams are documenting multi-vector attacks: one person plants the Ducky while an accomplice calls the IT helpdesk pretending to be a vendor. distraction and compromise simultaneously.
‼️ OnePlus confirmed a stock phone could be rooted by an installed app. Then it warned the researcher not to publish.
The app needs no special permissions. OnePlus confirmed the two flaws in May, but no fix was available when the researcher disclosed them. No real-world exploitation is known.
How the root chain works → https://t.co/0WRNLlTvyd
Spoofed "CEVA" and "TKW Logistics" app pages are pushing Android spyware as a fake system service — it reads your SMS and reroutes calls, hiding in plain sight. Sideloaded apps walk right past your VPN. Do you verify before installing on a work phone? 🔗 Link in comment below