LockFile ransomware attempts to evade protection with 'intermittent encryption' and making Windows write the encrypted documents for them, throwing off statistical content analysis and runtime behavior detection. Get the lowdown in our dissection 101: https://t.co/utPdAeRnZx
How Do You Get Hacked With Zero Malware?
WantToCry brute forces exposed SMB shares, steals your files, encrypts them on the attacker's infrastructure, then writes them back.
We walk through the attack step by step 👇
https://t.co/fbARCDaL9n
"Exploit mitigation" stalled around 2008. The attacks didn't.
AI turns a patched bug into a working exploit in hours. Why endpoint exploit mitigation stalled in 2008, and what a default-on mitigation layer looks like now: https://t.co/QEtB1FMLcD
@Kostastsale Real dilemma. But customer-written prevention rules only work for a skilled few. Most bought protection, not a second job tuning it. The fix is a vendor loop with an active team: resolve the false alarm once, push it to everyone before they hit it. Few EDRs have a strong loop.
AI is most effective against attackers when it is embedded into orchestrated defense.
Sophos has joined the @OpenAI Daybreak Cyber Partner Program, bringing leading cyber-capable models directly into the defensive workflows our teams already run.
🔗 https://t.co/9mYJAI2SO2
For five years, Sophos engaged in defensive and counter-offensive operations against China-based, state-sponsored threat actors.
Now @DarknetDiaries, the most popular cybersecurity podcast in the world, has spent 90 minutes telling the full story.
🎧 https://t.co/XfhngKx3C7
Ransomware: AI changes the writer. It doesn't change the math.
Why most endpoint protection still treats ransomware as just another piece of malware, and what changes when you watch the data instead of the attacker. https://t.co/ZkgOljMnqk
AI finds bugs faster, but hasn't changed how they're exploited. Sophos targets the primitives, not the provenance. AI-written or manual: they hit the same architectural wall. We build the friction where defenders win, on every process, by default: https://t.co/5tmPejZd8t
Waar zit je aanvaller écht? Mijn onderzoek met de CTU toont hoe cloud VM's "rogue insiders" worden:
1️⃣ Geo-blocking omzeilen 🌍 2️⃣ Via RDP/VPN je infra in; de VM wordt deel van jouw netwerk 3️⃣ Remote encryptie via SMB (geen lokale signalen!)
Details: https://t.co/2BVmovObCO
.@StealaBrainrotR Security concern: Unknown player appeared in our private server during Gingerbread Town Event and last night during Christmas Eve admin event, a paid Festive 67 was removed from my son's base while allowed players were asleep. Looks like an exploit. Please act.
A Chinese APT leveraged Claude AI to run an end-to-end intrusion — recon, exploit generation, lateral movement — all executed via Anthropic’s own systems.
Defenders are officially in a new era. https://t.co/SrHOFCpq0G
Threat actors regularly look for ways to disable security products. Tamper protection – a mechanism designed to stop threat actors from interfering with security products – is therefore a critical part of any security suite.
@fmeeus1 Idd, zowel Codex Sinaiticus als Vaticanus eindigen Marcus 16 bij vers 8. De verzen 9–20 zijn een latere toevoeging (2e eeuw). De NBV21 meldt dit in een voetnoot. Soemerische opstandingsmythen zoals die van Inanna (later Ishtar) zijn >1000 jaar ouder dan het christendom.
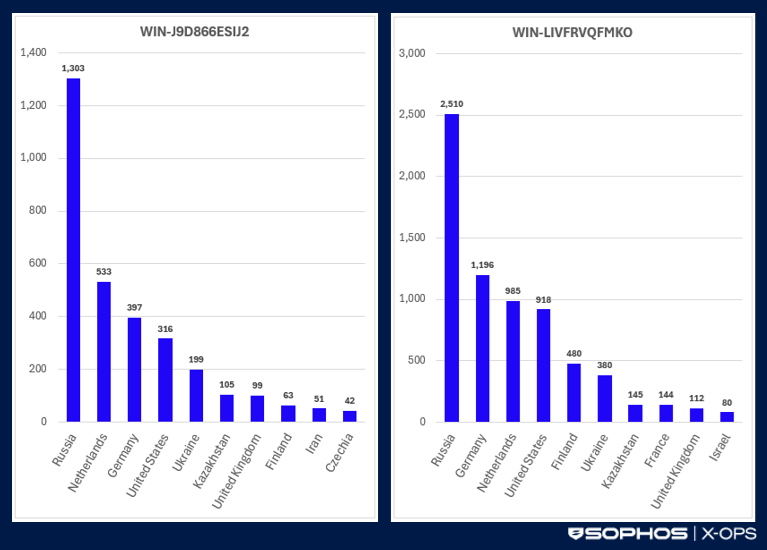
At the end of 2023, Sophos X-Ops noted a 62% year-on-year increase in ‘remote encryption’ attacks – where ransomware attackers compromise an unmanaged or under-protected endpoint, and leverage that access to encrypt data on managed, domain-joined machines.
Everyone says Europe can't compete with America in tech.
But 48 hours ago, Mistral's 'Le Chat' just proved them wrong:
• 13x faster than ChatGPT
• 100% open-source
• Completely free (vs $20/month)
The European AI breakthrough Silicon Valley didn't see coming 🧵: