Kurz in eigener Sache:
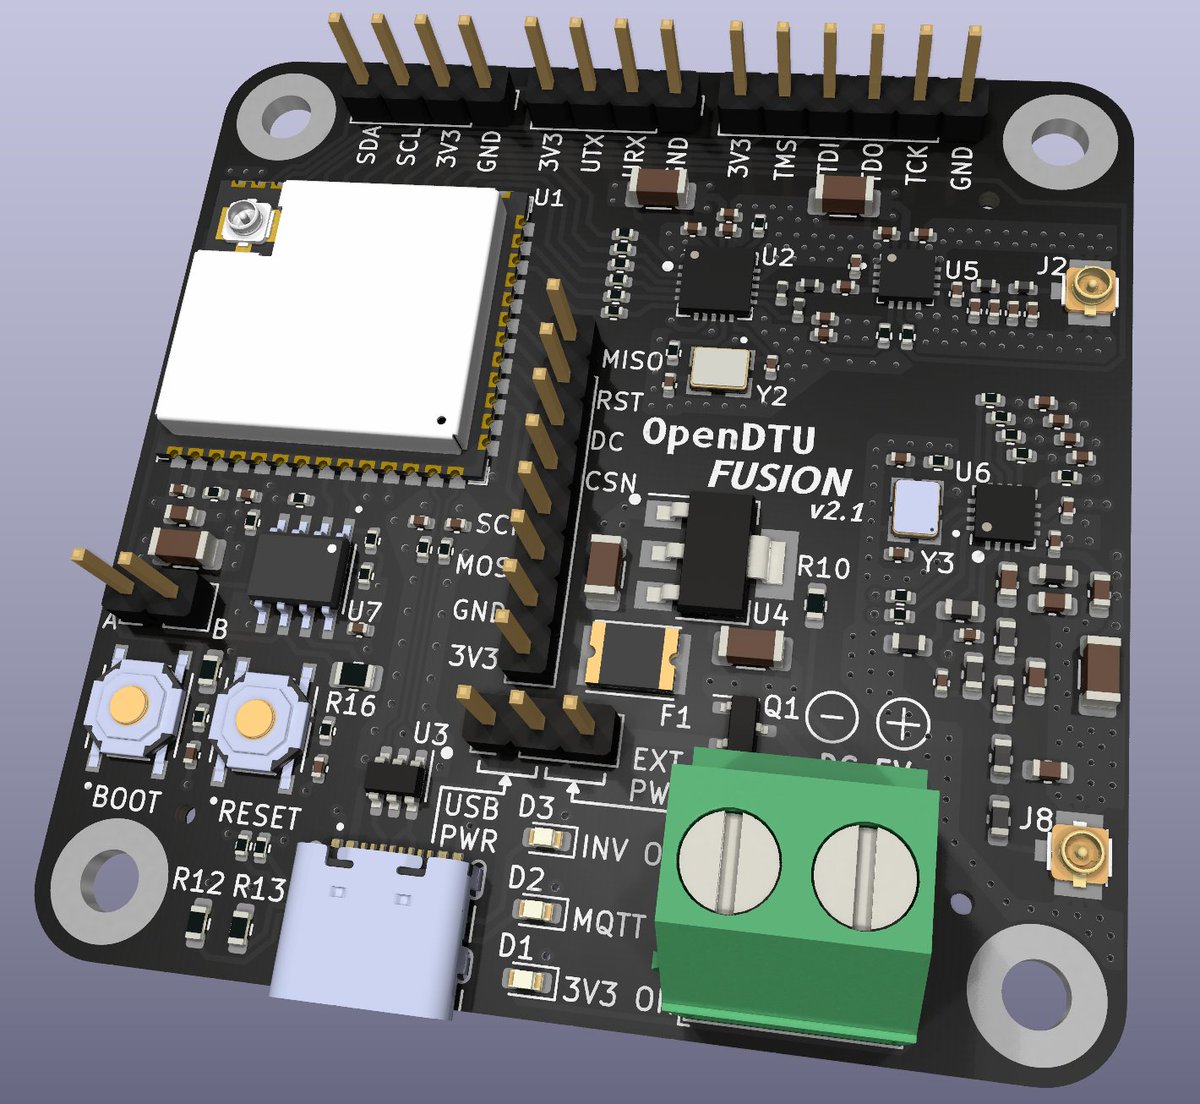
Wer ein Balkonkraftwerk/Solaranlage mit Hoymiles (HM/HMS/HMT) oder manchen TSUN Wechselrichtern betreibt und eine "China-Cloud-freie" Möglichkeit zur Smart-Home oder Nulleinspeisung haben will:
Das OpenDTUFusion-Board aus meiner Feder ist jetzt verfügbar!
Also ich bin kein Verfassungsrechtler, aber eine eidesstattliche Erklärung über das Abstimmungsverhalten einer geheimen Wahl kommt mir irgendwie illegal vor.
https://t.co/igMeytuZFW
Ok I admit I did not have 'SpaceX rewrites aviation control software to launch more' on my bingo card.
This company does not take no for an answer it's truly something else...
In a comment to the FAA, SpaceX says it wants to launch 10,000 times per year.
The FAA asked for input on where to build new spaceports and how to give rocket launches priority in US airspace. They're preparing for 10,000 launches a year by 2035.
SpaceX replied that rockets aren't the bottleneck anymore, the FAA's outdated air traffic processes are. They created their own airspace tool (Cleared) that most major US airlines already get for free.
They also noted that Starbase Louisiana is designed for ~30 launches and reentries PER DAY (!!)
Announcing 3 Critical vulns for hundreds of millions of IoT, Firewalls, OT, and Military devices including: Palo Alto Networks, Comcast, D-Link, HP, Canon, Honeywell, GE, Oracle, Siemens, Rockwell, Digi, Lockheed Martin, Boeing...
The vulns are with GoAhead Web Server which is a backend library used by these devices. There's a patch available from GoAhead but that doesn't mean there's a patch available for the devices yet -- that's up to the manufacturer.
- TLS traffic over DHE ciphers have a 1-byte secret, "04", meaning anyone can decrypt connections to these devices and steal login credentials and session tokens if the client negotiated with DHE ciphers like the latest TLS_DHE_RSA_WITH_CHACHA20_POLY1305_SHA256, which is extremely likely.
- LibreSSL mTLS has been completely bypassed, meaning anyone can connect over mTLS. If you have one of these devices listening on the internet and are expecting mTLS to protect it from attackers, take it offline or patch asap.
- OpenSSL Certificate Revocation Lists (CRLs) are not enforced, meaning if a user device is stolen or compromised, and you revoke that mTLS cert, nothing actually happens. There are a lot of other attacks this can be used for.
These are critical because these types of devices run our world. Water systems, electricity, military, firewalls, critical infrastructure.
https://t.co/AYUgNsrA0f
Disruption.
And people - again - would not believe it.
By the way: This is backed by the tech the laggardcy EU wants renamed to 'assisted driving' because they couldn't be bothered increasing road safety instead of ill-guided protectionism. It's sickening.