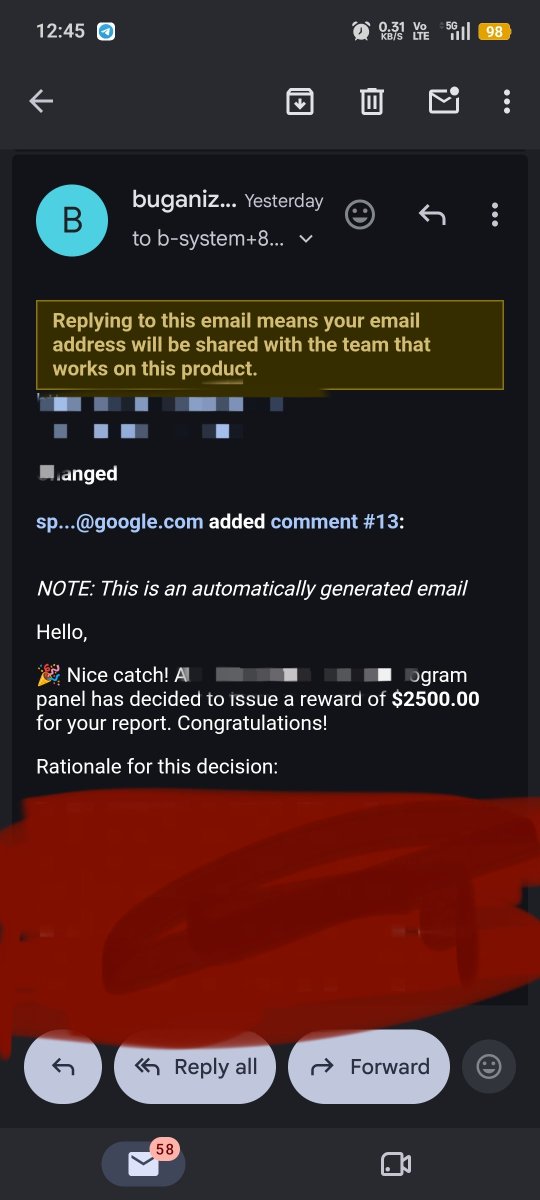
Found a BAC and submit it within just an 20 minutes.
It was a popular public program, decades old, and heavily fuzzed by bug hunters.
Yet somehow, a simple BAC was still hiding in plain sight
@morbintimenfts@levinhjs Nope not recieved single update . I asked them bot replied The panel is still reviewing your report. We appreciate your patience and will send you an email as soon as a decision is made.
I am still waiting for bounty
@MrsteveonX@tabaahi_ Brother, I don't know him personally. I joined bug bounty in 2019, while I think he joined around 2021–22. He may be a good hacker, but posting fake news and AI-edited bounty screenshots just to gain fame is disappointing. Why do people resort to lying for attention?
I found this interesting "403 Forbidden" Bypass; through "Microsoft-Azure-Application-Gateway/v2"
1. Accessing the URL returns "403 Forbidden"
2. Appending the query "?x=.js", successfully bypasses the Azure restriction leading to direct access to the restricted resource.
➡️ DELETE /api/user/999 → 403 ❌
Try this:
➡️ POST /api/user/999 + X-HTTP-Method-Override: DELETE → 200 ✅
➡️ POST /api/user/999?_method=DELETE → 200 ✅
Gateways/auth middleware often match on verb+path. Frameworks (Laravel _method, Express method-override, Rails) may accept overrides at the router level.
Same for edge rules that only guard GET/POST. Try HEAD/PATCH/OPTIONS too.
SSRF Isn’t Always Hidden in Parameters
(Case 1 — Leading Slash)
====>
GET /SSRF-server HTTP/1.1
Host: app
(Case 2 — Without the Leading Slash)
====>
GET SSRF-server HTTP/1.1
Host: app
At first glance, the difference is just one character: /.
When your done from subdomain enum, use this tip over intruder
Happy hunting bros ❤️
#BugBounty #SSRF #WebSecurity #CyberSecurity #Pentesting #BugBountyTips
6 months ago I found these vulnerabilities across several companies and earned $15K in bounties
I haven’t hunted on web apps in a while and I really miss it
Hope my writeup helps other hunters
Broken access control on Next js server actions
https://t.co/FZYNkvuZlx