Information Systems student | Full-stack Developer
Exploring Web3, AI agents, and interactive digital experiences. Building, learning, and shipping projects on
Cara bikin laporan Bug Bounty yang bener.
Biar cepet di-triage, bounty-nya juga lebih layak.
Sebelum nulis coba cek & lakui ini
• baca scope & aturan program, pastiin bug in-scope
• cek duplikat di disclosed reports/changelog
• uji aman: pake akun sendiri, jangan sentuh data user lain, hindari DoS
• verifikasi ulang, jangan sampe false positive
Struktur laporan kurang lebih seperti ini
1. Judul
Spesifik: jenis bug + lokasi + dampak.
Salah: "XSS di website"
Bener: "Stored XSS di kolom komentar /posts/{id} memungkinkan pengambilalihan sesi"
2. Ringkasan
2-3 kalimat. Apa bug-nya, di mana, akibatnya.
3. Severity
Usulin Low/Medium/High/Critical. Idealnya pake CVSS + alasan. Jangan dilebih-lebihin, karena kredibilitas mu taruhannya.
4. Langkah reproduksi
Ini bagian paling penting.
Harus bisa diikutin orang asing dari nol.
Cantumin URL, parameter, metode HTTP, akun/role, payload atau request lengkap, plus browser/versi.
5. Proof of Concept
Screenshot, video singkat, atau skrip minimal.
Samarkan data sensitif. Buktikan dampak tanpa ngerusak.
6. Dampak
Skenario realistis aja.
Siapa terdampak, data apa yang bisa diakses, apa yang bisa dilakuin penyerang.
Jangan berspekulasi liar.
7. Rekomendasi perbaikan
berikan saran singkat: validasi input, output encoding, cek otorisasi di server, rate limiting.
Opsional, tapi biasanya disuka tim.
8. Info tambahan
Lingkungan uji, tanggal/waktu, referensi CWE/OWASP.
Tips biar diterima:
• satu laporan = satu bug, kecuali chain dan lo jelasin rantainya
• bahasa profesional & netral, jangan nuntut atau nyebut bounty di awal
• fokus dampak bisnis: account takeover, data leak, RCE biasanya suka dinilai tinggi
• selalu ada bukti yang bisa diulang
• berhenti setelah bukti cukup, jangan exploit lebih jauh
• balas klarifikasi cepet & sopan
• patuhi disclosure policy, jangan publikasi sebelum diizinin
Kesalahan umum yang sering terjadi
• judul terlalu umum
• langkah reproduksi ambigu
• lapor hasil scanner tanpa verifikasi
• severity dilebih-lebihin
• lapor out-of-scope / known issue
• spam laporan duplikat / berkualitas rendah
Template ringkasnya
Judul: [Bug] pada [komponen] memungkinkan [dampak]
Ringkasan → Severity (CVSS) → Langkah Reproduksi → PoC → Dampak → Rekomendasi → Lingkungan
Laporan jelas + bukti kuat + dampak nyata = triage lebih cepet, peluang bounty lebih gede.
Simpan buat temen hunter atau kamu sendiri.
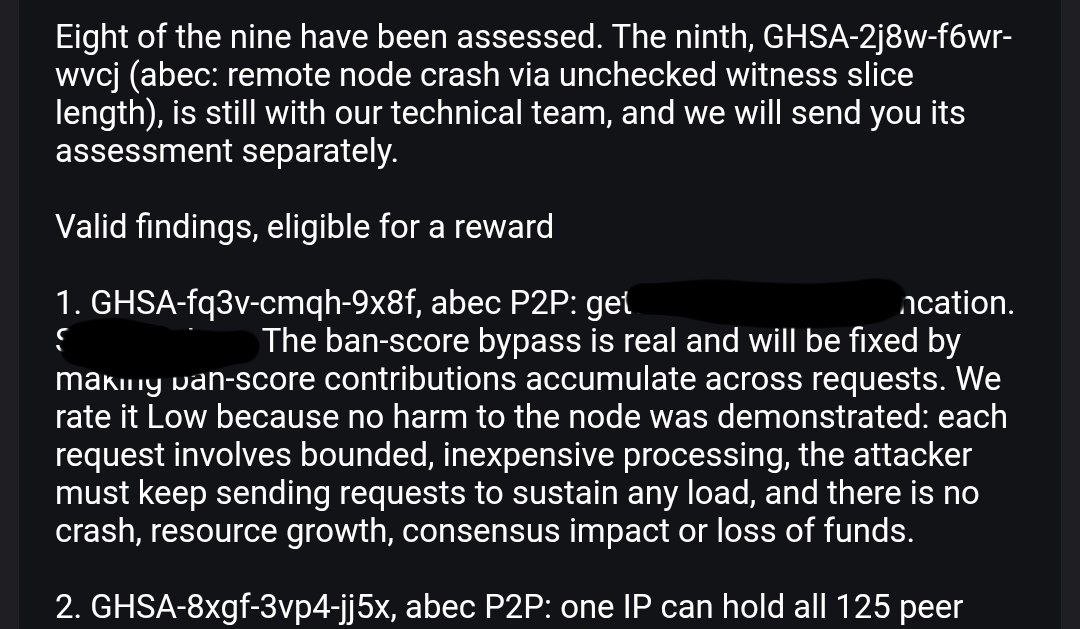
Gambar sebagai contoh laporan bug yang di terima
Over the past week, I’ve been overwhelmed by the love and support of friends, industry colleagues, and people I've never met. Thank you to everyone who has shown kindness to my family and me. It means the world to me.
I came to the United States 53 years ago, and becoming an American citizen is one of the greatest gifts and proudest moments of my life. NVIDIA has been my life’s work. Building it into the company it is today alongside my colleagues has been a privilege and an honor. Nowhere but in America could a company like NVIDIA be possible. I love our country, and I love NVIDIA.
I did not live up to the standards expected of everyone at NVIDIA, and I have made serious mistakes in my personal life. I created problems for the Board that I deeply regret. I own my mistakes completely, and I am committed to cooperating with the Board’s independent investigation.
Since my departure, I’ve seen an outpouring of calls from NVIDIA’s employees, investors, business partners, and customers for me to return as CEO. Many continue to reach out to me directly as the company navigates complex technology, market, competitive, and geopolitical dynamics. NVIDIA is a once-in-a-generation company. If the Board of Directors decides that my return is in the best interest of our shareholders, our employees, the company, and America, I would be honored to answer these calls and return as CEO.
Thank you again to everyone who has shared their good wishes. I am profoundly humbled by your support. To my family: I love you, and I will spend the rest of my life being worthy of yours.
Jensen
This is just 97 KB of HTML file 😲
An entire underwater world with kelp forests, manta rays, schools of fish, a sunken ship and realistic lighting
built by Fable 5.2 in a single prompt
Laurel is now live on NEAR mainnet!! 😎🔥
Same contract as testnet. Scores come from Intel TDX enclaves and verify to Intel’s root.
Press “Ask the champion → Mainnet”: real NEAR goes to the model’s owner.
https://t.co/Kmlji5Rl2P
@NEARProtocol@NEARdevs#NEARHackathon
Laurel is now live on NEAR mainnet!! 😎🔥
Same contract as testnet. Scores come from Intel TDX enclaves and verify to Intel’s root.
Press “Ask the champion → Mainnet”: real NEAR goes to the model’s owner.
https://t.co/Kmlji5Rl2P
@NEARProtocol@NEARdevs#NEARHackathon
Every AI model grades its own test, and we just believe the score.
Laurel, on NEAR: small models are scored on a private test set inside a TEE, the winner lives in a smart contract, and AI agents pay it per prediction.
Built at NEAR HACKATHON @NEARProtocol#NEARHackathon
Every AI model grades its own test, and we just believe the score.
Laurel, on NEAR: small models are scored on a private test set inside a TEE, the winner lives in a smart contract, and AI agents pay it per prediction.
Built at NEAR HACKATHON @NEARProtocol#NEARHackathon
@NEARProtocol Fake seller, not a thief? Both sides’ evidence is encrypted in the browser to a NEAR AI model in a TEE. The contract checks its signature; a 3-member DAO decides.
AI agent tricked into paying a scammer? Frozen in 10 s, sent back.
What would you undo? @NearLegion@NearBuilders
Key leaked? Your crypto is gone. No undo.
Undo: USDC on NEAR waits 5 min. PANIC on your phone freezes a theft and brings it home. No vote. No gas: NEAR meta-transactions.
Built at NEAR HACKATHON @NEARProtocol#NEARHackathon
https://t.co/rJJcVyteAV
https://t.co/BdyIx73Q2B
@NEARProtocol Enter your own model with one command (exhibit 05 uses real NEAR mainnet data, closes 12 Nov).
Don't trust us either: one command re-checks every claim from the chain.
https://t.co/3iCZdNt2Zs
What would you want judged this way? @NearLegion@NearBuilders
Every AI model grades its own test, and we just believe the score.
Laurel, on NEAR: small models are scored on a private test set inside a TEE, the winner lives in a smart contract, and AI agents pay it per prediction.
Built at NEAR HACKATHON @NEARProtocol#NEARHackathon
@NEARProtocol How it works:
• the test rows are a secret only the evaluator pinned in the contract can read
• a sealed split picks the winner
• an agent holds a NEAR key that can only call predict, and every answer pays the model's owner on-chain
https://t.co/Kmlji5Rl2P