Your payment details can remain safe while your personal information is exposed.
Landmark Group's Shukran loyalty programme reported unauthorised access involving customer names, contact details, and dates of birth. Such information can help criminals create convincing phishing.
Your production systems may be secure.
But what about your CRM, support tickets, sales conversations and internal tools?
The recent WorkOS incident is a reminder that business data can become a security risk even when production systems aren't compromised.
#CyberSecurity
Your backup dashboard says SUCCESS. But can your business recover after ransomware?
An untested backup could leave your team facing downtime when recovery matters most.
Don't make an actual attack your first recovery test.
#CyberSecurity#Ransomware
Temporary vendor access can become a permanent security gap.
Before granting privileged access, check:
• Named account
• Least privilege
• Expiry time
• Activity logs
• Confirmed revocation
Closing the support ticket doesn't remove access.
#CyberSecurity#IdentitySecurity
A Google Cloud outage disrupted UK banks and other services on 20 October. It was attributed to a power event, not a confirmed cyberattack.
The lesson: third-party failures can disrupt your business, too.
Map dependencies. Test fallback plans.
#CyberSecurity#CloudSecurity
A cyberattack doesn't need to steal data to disrupt a business.
The reported supermarket refrigeration incident in France is a reminder that connected equipment is part of the attack surface.
Restrict remote access. Monitor control changes. Segment OT networks.
#CyberSecurity
AI agents now access email, databases, APIs and business apps.
But what identity do they use when they act?
Shared accounts make attribution difficult. Broad permissions create unnecessary risk.
Agents need clear identities, limited permissions and an activity trail.
FortiMail alert: CVE-2026-104286 is a CVSS 9.8 flaw under active exploitation.
It can let unauthenticated attackers write arbitrary files via crafted HTTP/HTTPS requests.
Check exposure, investigate for compromise, and apply remediation.
#CyberSecurity#FortiMail
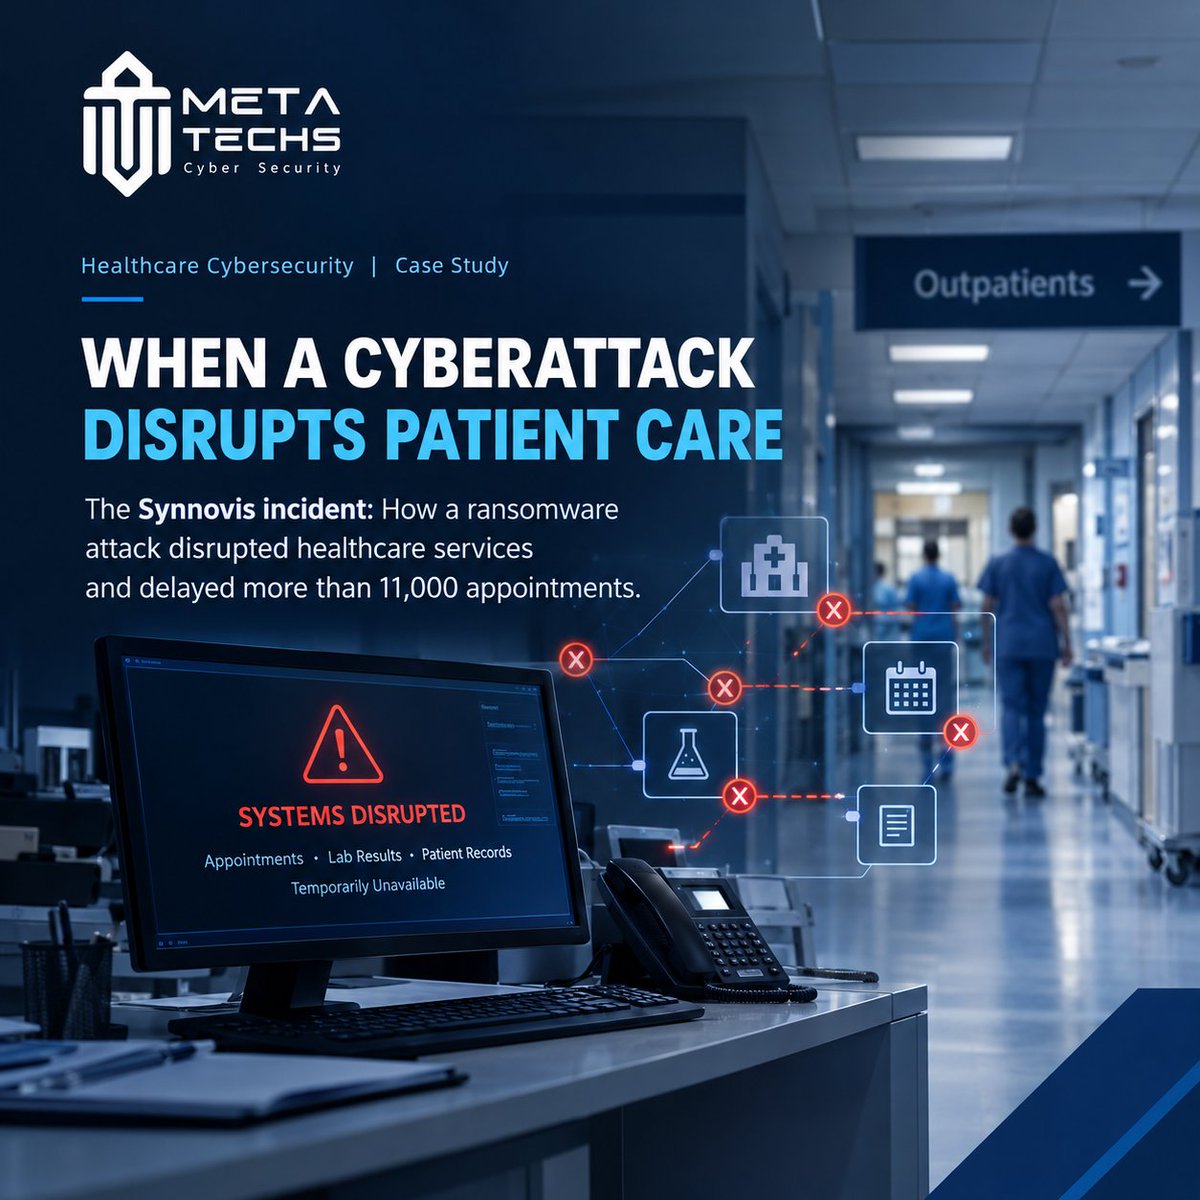
A ransomware attack on NHS supplier Synnovis disrupted healthcare services in London in 2024.
More than 11,000 outpatient and elective procedure appointments were delayed.
Healthcare cybersecurity is also a patient safety issue.
Deleting a file doesn't always erase its data.
Your computer may simply mark the storage space as available. Forensic investigators can sometimes recover the file until its data is overwritten.
On SSDs, TRIM can make recovery difficult or impossible.
You can't secure what you don't know exists.
Firewalls, EDR, SIEM and vulnerability scanners can still miss an exposed asset.
A forgotten subdomain, unmanaged device or new cloud resource can become a blind spot.
Do you know everything your organisation needs to protect?
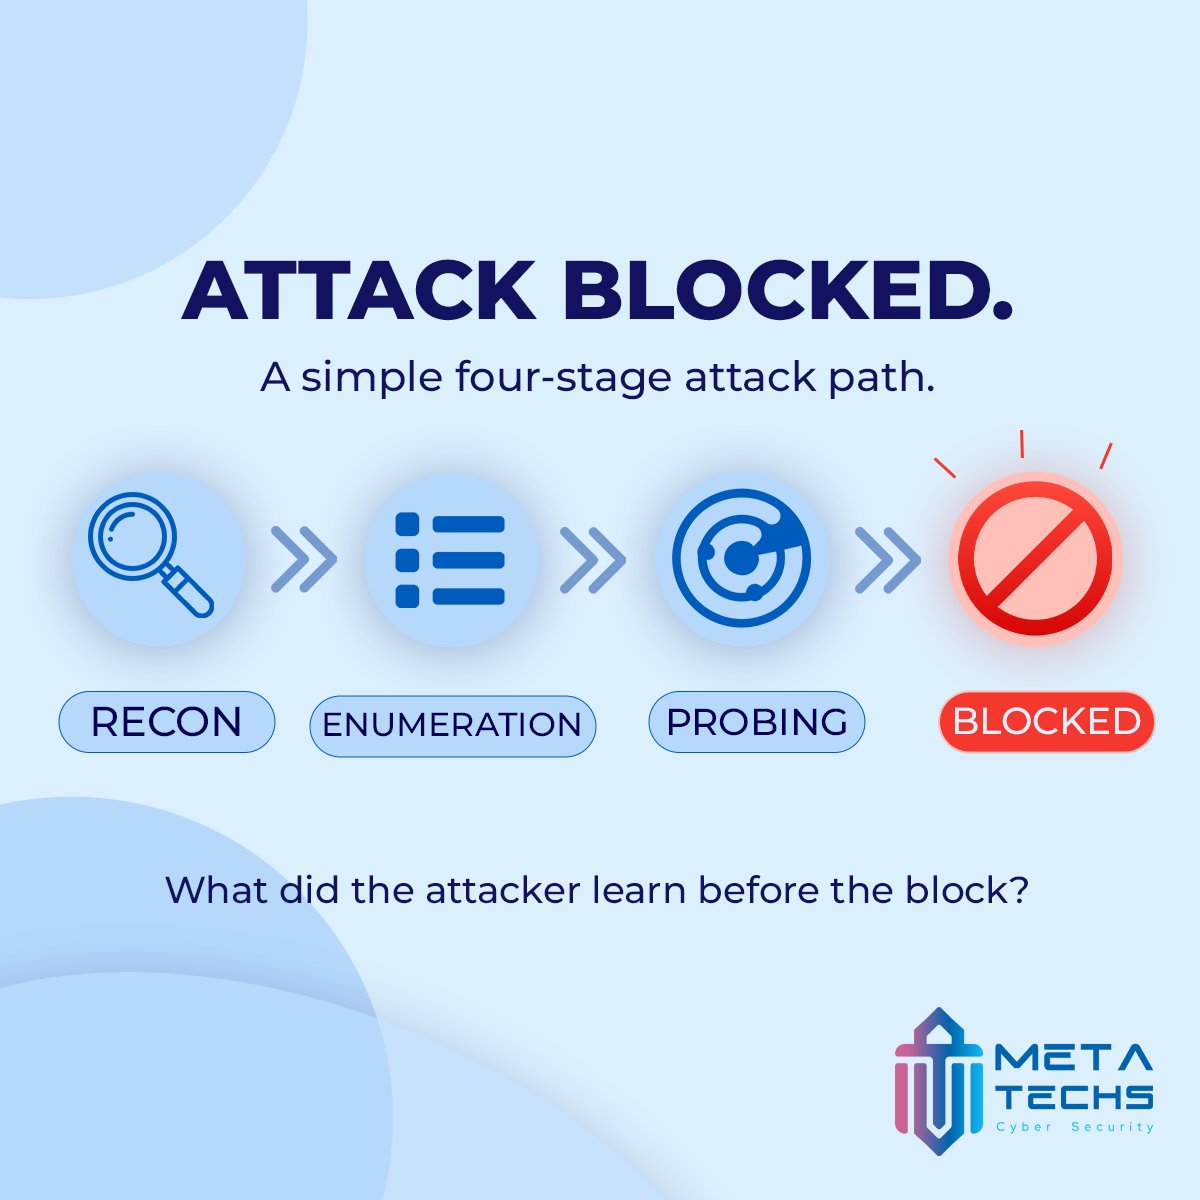
The attack was blocked.
But what did the attacker learn before it was?
- Reconnaissance.
- Enumeration.
- Authentication probing.
- Endpoint discovery.
Blocking the final request doesn't erase everything that happened before it.
#Cybersecurity#ThreatDetection
The employee left. The access may still be there.
Email deactivation is only one step. VPN access, SaaS accounts, active sessions, shared credentials and privileged permissions also need review.
Offboarding is complete only when access is revoked.
Firewall can be working while your business remains exposed.
The risk may be inside approved access:
• Excessive permissions
• Unused accounts
• Former vendor access
• Shared passwords
• Unreviewed cloud connections
Security starts with knowing who can access what & why.
The UAE is using AI to fight AI-powered attacks.
Hacking attempts have reportedly reached ~800,000 a day, around 4× pre-war levels.
Now the race is becoming:
AI-powered attacks vs AI-powered defence.
Who can adapt faster?
#CyberSecurity#UAE#AI
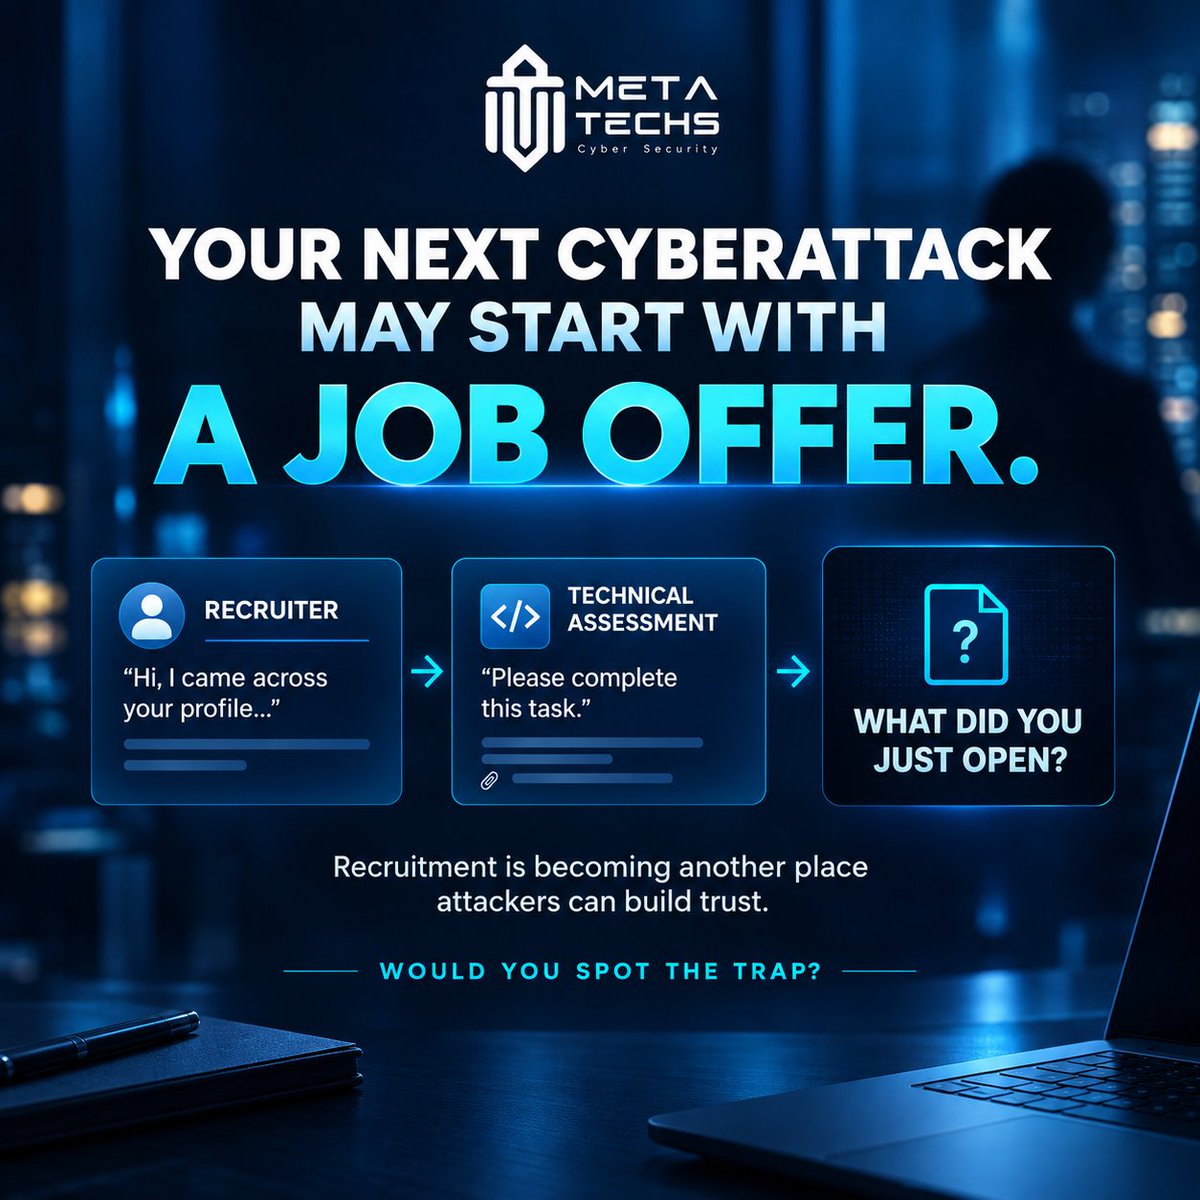
Your next cyberattack may start with a job offer.
A recruiter messages you.
The company looks familiar.
Then comes a technical assessment.
Recent attacks targeting professionals in the Middle East and Africa used this kind of recruitment approach to deliver spyware.
If an AI agent had access to your company today, what would worry you most?
Data. Credentials. Cloud. Code.
You can only pick one.
What is your choice?
#CyberSecurity#AISecurity#AgenticAI
Your AI Coding Assistant Can Be Turned Against You.
Attackers reportedly used Cursor to target at least 7 companies, including for credential theft and exploitation.
AI coding tools are becoming part of the attack surface.
What can your access?
#CyberSecurity#AISecurity
Your cloud may be secure. But who has access to it?
A recent study of 3,000 organizations found weak IAM controls across 87% to 97% of cloud environments.
One compromised identity can become a much bigger problem when permissions are excessive.
Everything looks normal. Until you look at the permissions.
One cloud identity has more access than it needs.
If compromised, those privileges could become an attacker's shortcut.
Can you spot the risk?
#CloudSecurity#CyberSecurity#IAM