@netresec Another issue for me, also with Emotet, but for spam. I tried run: "polarproxy -v -p 10465,25,465 -p 10587,25,587" but no SMTP(s) packets are caught and decrypted by PolarProxy although there are spams running.
@netresec Thank you @netresec for the response. I'll try it that way but I'm afraid it won't be suitable because Emotet has multiple C2 IP(s) and we don't know which one will work.
@_VinCSS_ has successfully detected and prevented a phishing attack campaign to distribute malware to customer that was protected by us. Here is my detail analysis about #Trickbot, one of the most dangerous malware!!!
[Eng]https://t.co/ISj9b3j5OO
[Vie]https://t.co/6F2v3DP2GB
#Qakbot#Qbot My journey to analyze how QakBot infects after launched by malicious Excel document, the techniques used to make the analysis difficult, and how to extract the C2 list. #VinCSS#MalwareAnalysis@erikpistelli@hasherezade
Check it out: https://t.co/o2CZIlZ6DV
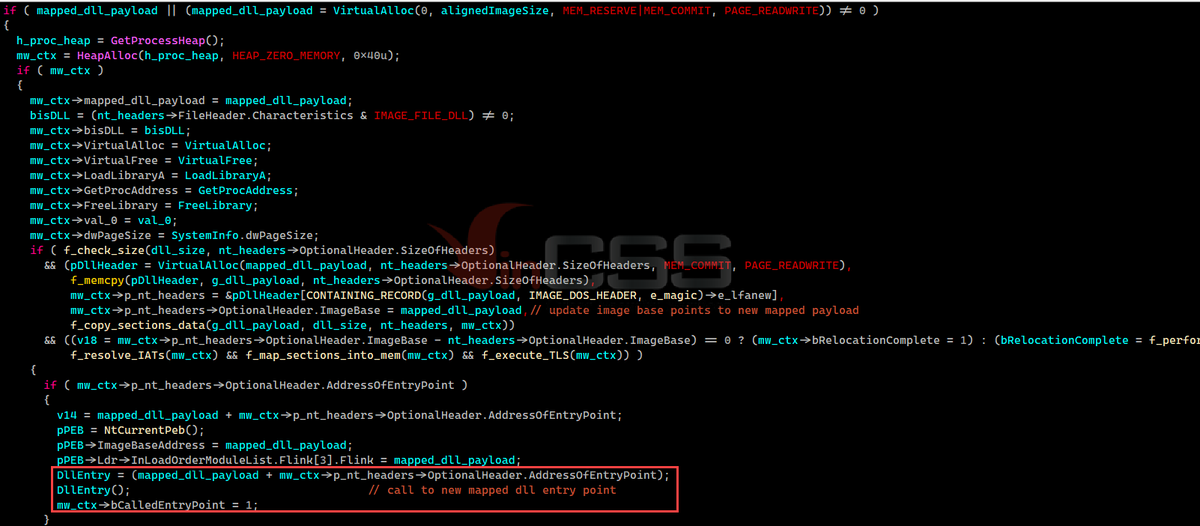
All Emotet epochs now are delivering the payload (https://t.co/Tv21VmJm4s) which has the code to remove Emotet on 25 March 2021 12:00. I believe that #Emotet#Killed
@craiu@hatr I guess they want to take advantage of Emotet's working flow to uninstall it properly. E.g: in case there is a flaw in the code, they still can deploy another one via Emotet's update protocol.
@craiu If you guys here are (were) playing with Emotet, then we known that Emotet gangs just started their update cycle for their arsenals early this year (modules, email templates using password in images ...) but after that they has been taken down.
We are checking on the #Emotet 'cleanup binary'.
It seems the actual date to trigger the uninstall routine is April 25.
More details to come.
/cc @campuscodi@LawrenceAbrams
https://t.co/OwM2trJdBu
https://t.co/UpQjxZhMwY
And Emotet bot is controlled to connect to these servers only:
80.158.3[.]161:443
80.158.51[.]209:8080
80.158.35[.]51:80
80.158.63[.]78:443
80.158.53[.]167:80
80.158.62[.]194:443
80.158.59[.]174:8080
80.158.43[.]136:80