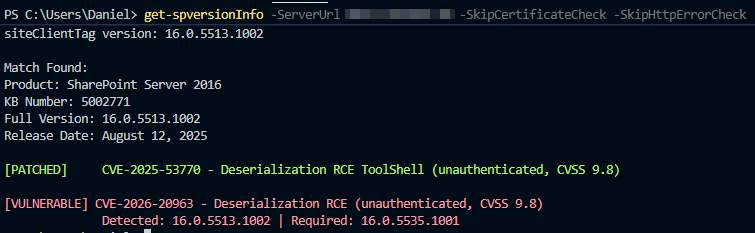
If you haven't patched yet.
Your Active Directory is currently indefensible.
https://t.co/sbhYArMTNh
🤷♂️
Join @techspence and I @ @wpninjasus in Jan as we dig into what this means and what you can do...
When you first enable the subscription for Cowork consumption, just FYI on some gotchas:
1. It's applied to all users by default. If ou don't want this, you have to select a group.
2. The default is set to unlimited credits. You probably don't want to do this unless you want a huge bill 😆
3. Make sure you enable spending alerts!
‼️ #Notepad++: disponibili #PoC per le CVE-2026-48800, CVE-2026-48778 e CVE-2026-48770 che interessano il noto editor di testo
Rischio: 🔴
Tipologia:
🔸 Arbitrary Code Execution
🔸 Denial of Service
🔗 https://t.co/DEGdsIPlJS
🔄 Aggiornamenti disponibili 🔄
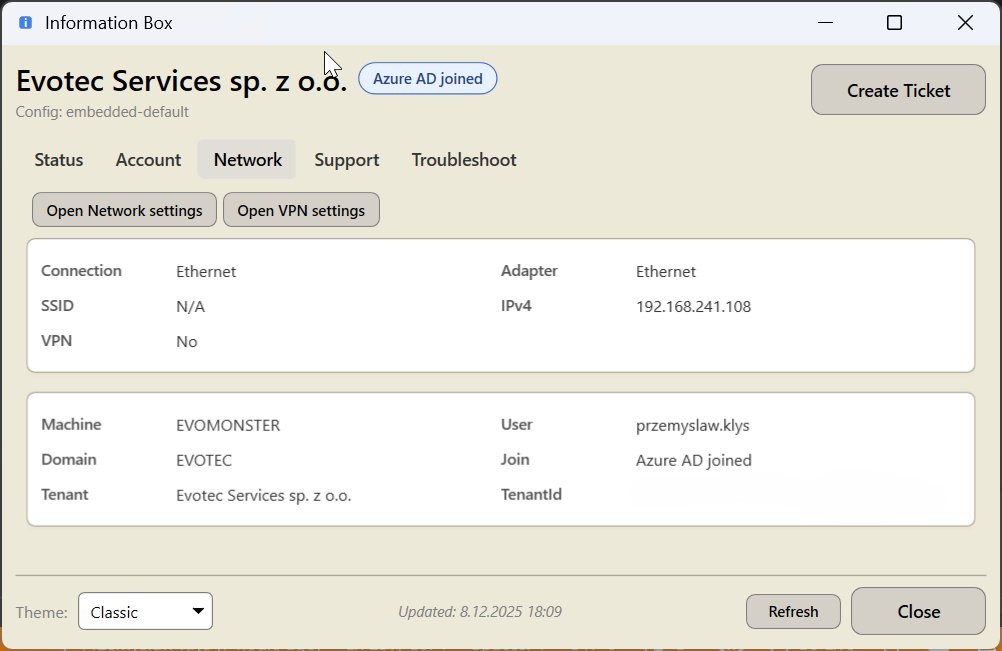
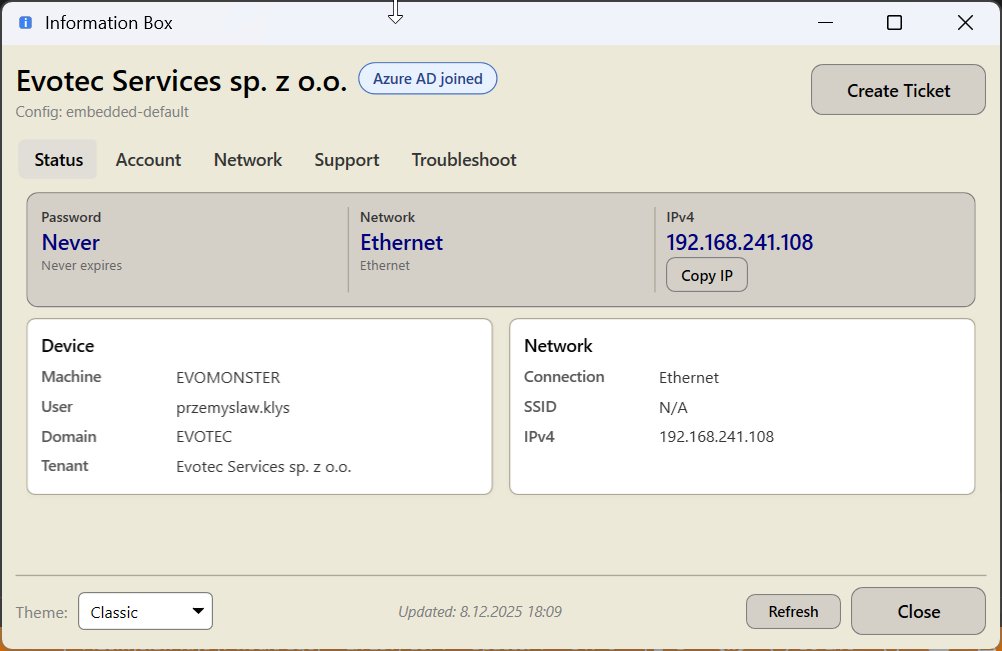
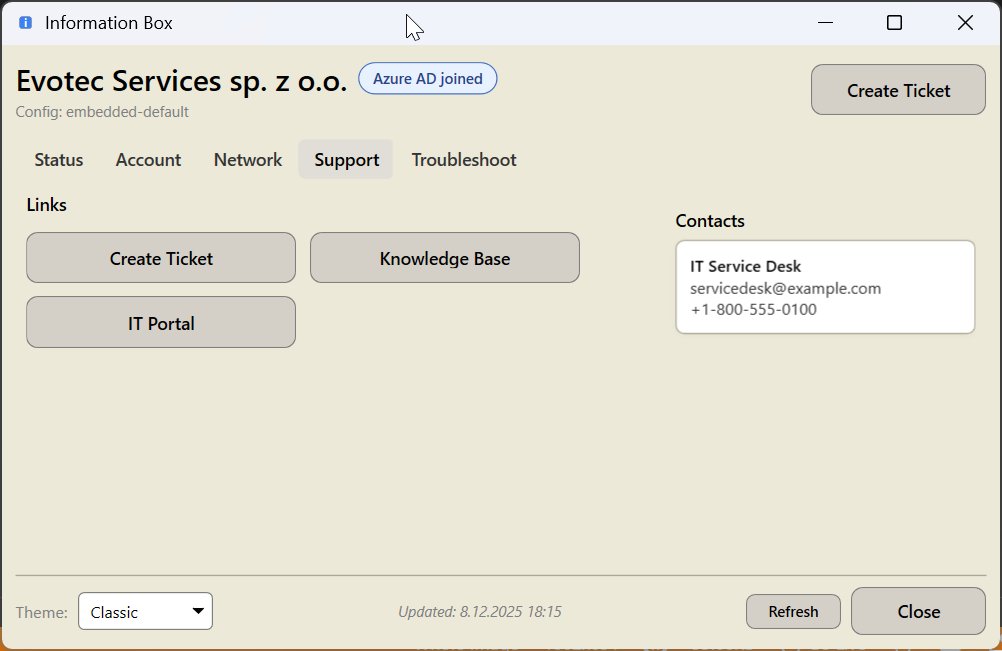
For those that don't really want/can't apply backgrounds to help their users I also have Information Box project which does similar thing, is super configurable, but it's a tray app instead of BGInfo alternative.
It works with both ActiveDirectory and EntraID.
https://t.co/hu761zrswR
⚠️ BitUnlocker Attack on Windows 11 Allows Access to Encrypted Disks in 5 Minutes
Source: https://t.co/dq8KjmuHtP
A new tool, BitUnlocker, reveals a practical downgrade attack against Microsoft's BitLocker encryption, allowing attackers with physical access to decrypt protected volumes on patched Windows 11 machines in under 5 minutes by exploiting a crucial gap between patching and certificate revocation.
The attack is rooted in CVE-2025-48804, one of four critical zero-day vulnerabilities. Systems that have completed the KB5025885 migration, moving the boot manager signature to the newer Windows UEFI CA 2023 certificate, are also protected against this downgrade path.
#cybersecuritynews #Windows11
‼ #Exploited#DirtyFrag: rilevato lo sfruttamento attivo in rete delle vulnerabilità CVE-2026-43284 e CVE-2026-43500, relative al #kernel#Linux
⚠ Ove non provveduto, si raccomanda l’applicazione delle misure di mitigazione fornite
Launching https://t.co/Z3gUh4OCOA
Look up any OAuth app ID and find out what it actually is across thousands of legitimate, risky, and malicious apps (Entra, Google, GitHub).
Multiple feeds, API, detection ideas and remediation guidance. Still improving the detections a bit 🦾
👋 Folks, I'm starting a new series of Entra Hardening tips from today.
Here's how it will work. One new tip every weekday (I take a break on weekends).
----
Tip #1: Privileged accounts in Entra ID should be cloud native identities
If your privileged accounts in Entra ID are synced from on-prem AD then you have a problem.
Attackers that compromise your on-prem infrastructure can pivot to the cloud, into Entra ID and gain access to the cloud servers, data, Microsoft 365 and other SaaS apps.
Why?
We've seen this happen multiple times. The biggest ones have been Solorigate (compromise ADFS and pivot to cloud), other examples include Storm-0501 (compromise AAD Connect server) and more.
The Fix?
Reduce the blast surface. Don't allow accounts synced from on-prem to be granted privileged roles.
Instead create admin accounts natively in Entra ID and grant privileged roles to these cloud only accounts.
Things I didn’t know when I started in IT that I know now:
- You shouldn’t use the same password for all local admin accounts
- You shouldn’t use your Domain Admin account for all administrative duties
- 99% of vulnerabilities won’t hurt you. Your time is better spent identifying and fixing the 1% that could
- You shouldn’t yolo lone ranger patch vulnerabilities without working with the rest of the team
You learn so much (many times the hard way) working in IT, but it’s invaluable experience for those wanting to work in cybersecurity roles later.
Most sysadmins didn’t sign up to be AD security experts…but attackers don’t care.
Im such a big fan of ADeleg and my wrapper ADeleginator because it gives you a quick way to spot dangerous permissions without some of the heavy lifting of other tools.
Here’s how to use it…
1. Download it to a domain joined system
2. Launch it and connect
3. Click view -> index view by -> trustees
4. Check the following for dangerous permissions:
Domain Users, authenticated users, everyone, domain computers
Link for ADeleg 👇
https://t.co/2hEKym6VMe
Link for ADeleginator 👇
https://t.co/LyXl9E28Yd
🗣️Want ready‑to‑use detection content - from playbooks to hunting queries and SIGMA rules, focused on modern adversary techniques?
Join the iPurple community and get access to it.
⏰Link Expires in 24H
https://t.co/boX3WNlfLr