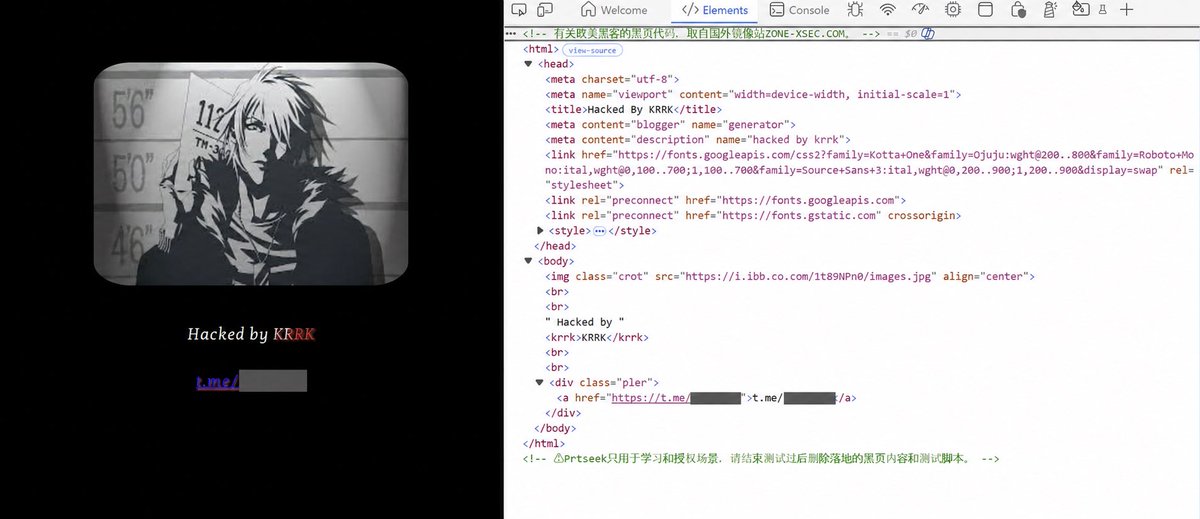
KimJEN 공개 자료 속 31개 대학 시스템을 분석했습니다. 29개에서 rERP 반복 수집, 조회 제한 우회, 학사·행정 DB 반출, 서버 설정·키 후보와 홈페이지 변조 정황을 확인했습니다. #KimJEN#OSINT#데이터유출 https://t.co/CJT7cI2Sub
Tracing KimJEN through exposed data: our review found ARTEX-related paths in five Python scripts and a Prtseek reference copied across seven files. What the evidence confirms—and what it does not. #ThreatIntel#OSINT#ARTEX#Prtseek https://t.co/z1Am61W2x5
🚨 Threat actor “KimJEN” has posted alleged database leaks involving South Korean universities on RaidForums and Telegram. — Reported by #TEAM_D4rkn3ttz@mingming0l
On November 11, 2026, KimJEN claimed to share a database from Inje University, listing 359 tables that allegedly contain course, attendance, user, and related records.
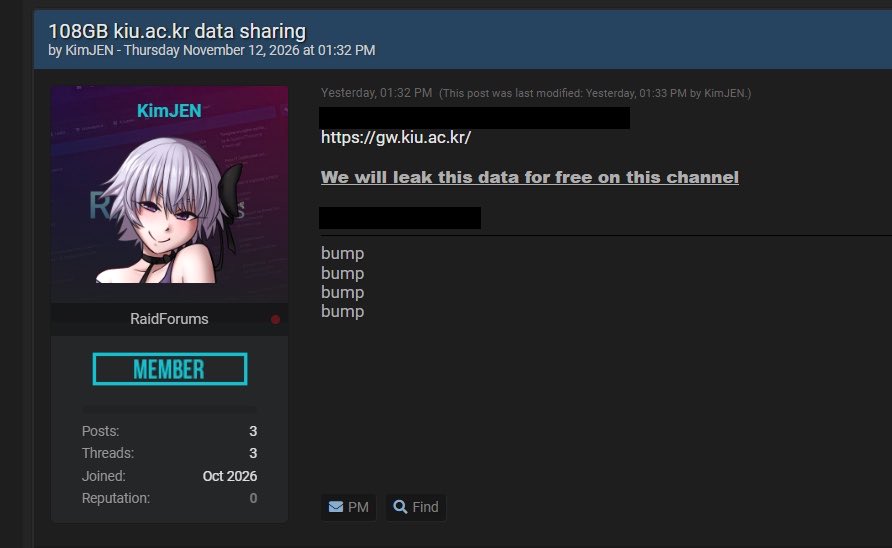
On November 12, the actor posted another thread claiming to share 108 GB of data associated with Kyungil University.
The actor later shared an “ACTIVE BEACONS INVENTORY” image with the message “Which will be the next?” The displayed IP addresses reportedly included infrastructure associated with Korea National University of Transportation and Dong-Eui Institute of Technology, potentially implying future targeting.
⚠️ The posts and screenshots confirm that these claims were published, but the authenticity, acquisition method, full scope of the datasets, and whether the two additionally referenced universities were compromised have not been independently verified.
The Telegram address and exact IP addresses have been omitted to limit access to the alleged data and avoid exposing potentially targetable infrastructure.
#CyberThreatIntelligence #ThreatIntel #DataBreach #SouthKorea
KimJEN의 인제대·경일대 자료 유출 주장과 추가 표적 암시를 TEAM_D4rkn3ttz가 분석했습니다. 개인정보·메일·서버 설정 등 공개 자료의 분석 결과와 미확인 사항을 정리했습니다.
#TEAM_D4rkn3ttz#KimJEN#정보유출#사이버보안 https://t.co/UzrvFJSD3h
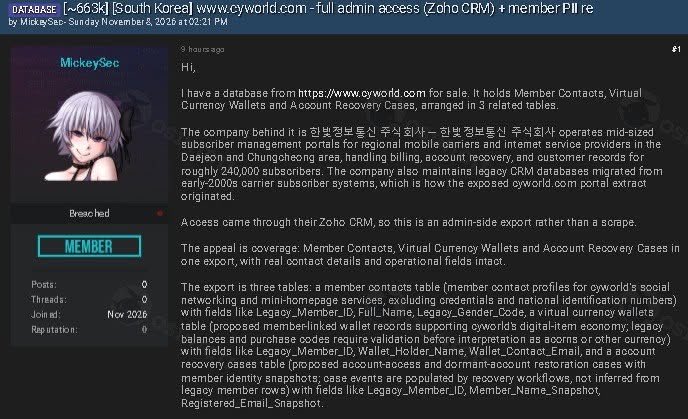
🚨 A threat actor's claimed sale of 663K+ https://t.co/kHu1OGk4HW member records is assessed as likely fabricated, with evidence pointing to a Zoho CRM trial account and synthetic data. — Reported by #TEAM_D4rkn3ttz@mingming0l
In a bf[.]st post dated November 8, 2026, the threat actor MickeySec claimed to be selling https://t.co/kHu1OGk4HW member contacts, virtual currency(acorns ‘DOTORI’ or other currency) wallet and account recovery records for $4,550. The actor described the data as an "admin-side export" obtained through a South Korean company's Zoho CRM.
🔎 Key Findings:
[Proof Screenshots]
- The Tasks list closely matches the default sample data provided in a Zoho CRM trial account, including dates, statuses, and priorities. Only the industry descriptions and company names appear to have been altered.
- Python byte-string escape sequences (\xb9\xb1...) appear in the browser tab title, suggesting improper character decoding or script-based handling of Korean text.
- Despite claiming "full admin access," the actor provided no evidence demonstrating access to administrative settings or privileged CRM functions.
→ Assessed as likely staged screenshots from a Zoho CRM trial environment.
[Sample Data]
- Record IDs are sequential, and creation timestamps are exactly one second apart, suggesting automated record generation.
- All members share an identical registration date, and every account balance is 0.
- The 'Created_By' and 'Modified_By' fields are empty, which is inconsistent with the populated audit fields observed in the reference Zoho CRM exports reviewed by the team.
- Email addresses appear to have been derived from mis-encoded Korean name strings.
→ Taken together, these patterns strongly suggest script-generated synthetic data rather than authentic member records.
[Timeline Inconsistency]
- The sample data contains a migration date of June 10, 2024. This date falls after Cyworld's service suspension in August 2023 but before Cy Communications (싸이커뮤니케이션즈), the entity that later acquired the service, was established in September 2024. This raises questions about who conducted the migration and under what operational circumstances.
[Named Entities]
- No publicly available evidence was found linking the companies named in the actor's post or screenshots to Cyworld's ownership, operation, or data management.
[Prior Breach Correlation]
- The claimed access method, involving a third-party Zoho CRM, differs from the circumstances of the 2011 SK Communications breach, which affected more than 35 million Nate and https://t.co/kHu1OGk4HW users.
- The claimed wallet and account recovery tables were not among the data types publicly reported in the 2011 incident.
- No evidence was identified linking the current claim to the 2011 breach.
⚠️ Based solely on the public post, proof screenshots, and sample data, the advertised dataset is assessed as likely fabricated. However, the possibility that it contains records sourced from prior breaches cannot be ruled out. No compromise of https://t.co/kHu1OGk4HW related to this claim has been independently verified or officially confirmed.
#CyberThreatIntelligence #ThreatIntel #DataBreach
다크웹, 어디까지 알고 계신가요? 🔎
Team D4rkn3ttz(다크넷즈)가 K-디지털포렌식위크 2026(K-DFW 2026) DFC Village에 Intelligence Community로 참여합니다!
이번 행사에서는 다크웹 위협 인텔리전스를 직접 경험하고 탐색할 수 있는 콘텐츠를 준비했습니다.
🧩 실제 분석 과정을 담은 다크웹 퀴즈
🔎 출처 기반의 다크웹 유출 조사 서비스
🗺️ 위협 그룹·포럼·유출 사건을 연결한 다크웹 생태계 지도
📅 2026년 11월 10일(화) 13:40–18:00
📍 서울 엘타워 8층 엘가든
현장에서 직접 만나 뵙겠습니다!
🔗 https://t.co/mL4e0Is7kP
#KDFW2026 #DFCVillage #TeamD4rkn3ttz #ThreatIntelligence #DarkWeb #CyberSecurity
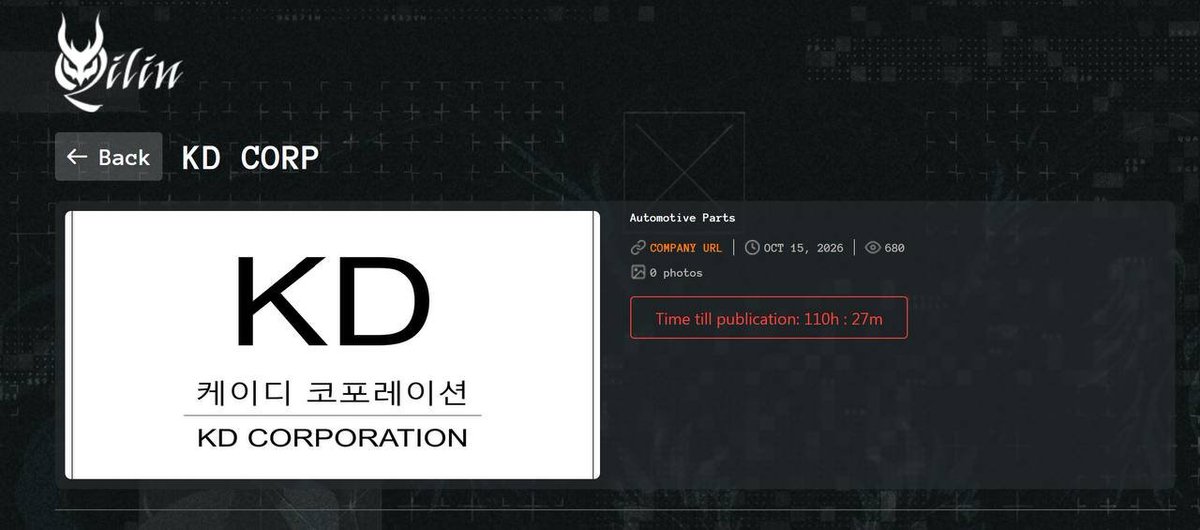
🚨 Qilin, a ransomware group, has threatened to publish data allegedly stolen from KD CORP, a South Korean company. — Reported by #TEAM_D4rkn3ttz@kwisejh@mingming0l
The group’s data leak site displays a countdown indicating that the allegedly stolen data is scheduled for publication in approximately 110 hours.
⚠️ Details listed by Qilin:
- Target: KD CORP
- Website: https://t.co/Yd8SuFMCby
- Listing date: October 15, 2026
- Industry: Automotive parts
- Status: Publication pending
🔍 The logo image and company link in the listing point to KD CORPORATION, a South Korean fabric agency specializing in European textiles. However, Qilin lists the industry as “Automotive Parts.” This discrepancy may reflect confusion with the similarly named automotive parts manufacturer KD (https://t.co/qYmToKujc9), but this explanation remains unconfirmed.
No data has been released to support Qilin’s claim. The claim, the identity of the allegedly compromised company, and the authenticity and scope of the allegedly stolen data remain unverified pending further evidence or official confirmation.
#ransomware #cybersecurity #threatintel #cyberthreatintelligence p
We analyzed 10 claims of leaked Korean data for sale, documenting signs of fabrication and sample reuse, alongside the evidence and limits of our assessment. https://t.co/38p3niUxRL
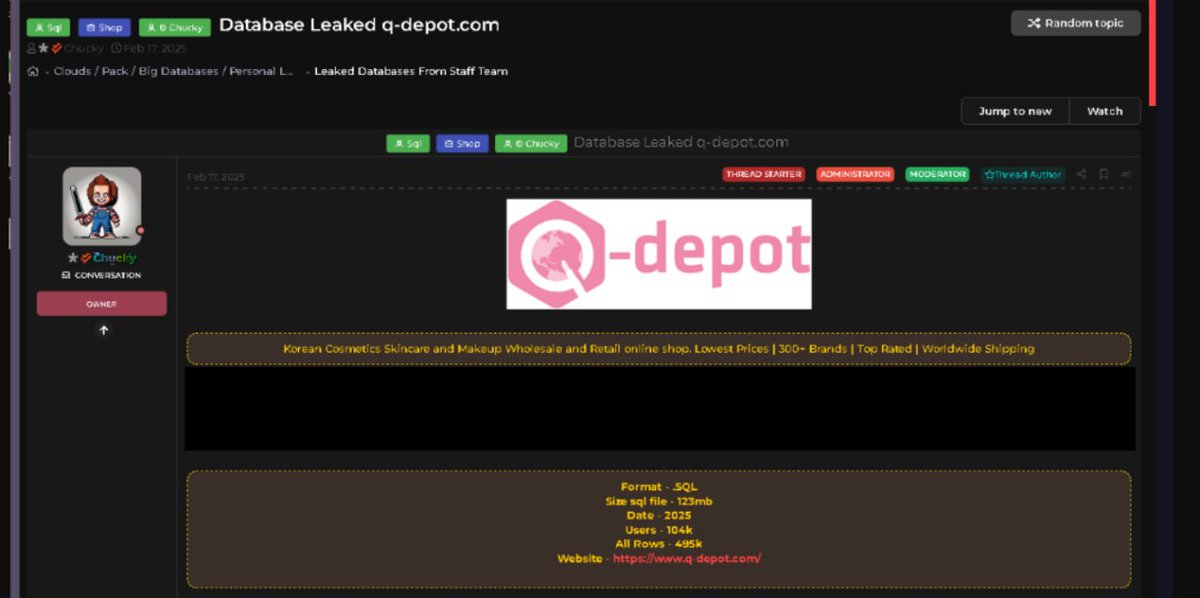
🚨 A threat actor "replaceboundless" reposted a leak claim for Q-depot, a Korean and Japanese cosmetics wholesale platform, listing roughly 100K accounts.
The claim was first posted on Leakbase on Feb 17, 2025. — Reported by #TEAM_D4rkn3ttz@mingming0l
📦 Scope of exposure
• Posted by Chukey (original) and replaceboundless (repost), and reposted on multiple forums since Feb 2025. Several reposts appeared to reuse the same dataset or samples, while a Darkforums listing claimed to offer a newer June 2025 version
• The posters claim about 104K users, 495K rows, and a 123MB SQL file (15.5 MiB compressed). The figures below are our own count from the dump we obtained
• A database described by the poster as Q-depot's database is a 129MB MySQL dump containing 97,053 accounts (names, email addresses, phone numbers, IP addresses), 24,994 addresses, and 7,496 orders
• Also includes 78,300 bcrypt password hashes, API tokens, integration keys (payment, SMS, email), and MySQL user password hashes (existence and counts only; key validity unverified)
• 1,264 accounts (1.3%) have Korean mobile numbers
🕒 Timeline • Feb 17, 2025 — Chukey first posts the database on Leakbase
• Feb 22, 2025 — Blinkers reposts it on BreachForums
• Jun 6, 2025 — BlackH0le claims a newer June 2025 version on Darkforums
• Sep 25, 2025 — Tanaka reposts it on Darkforums
• Feb 14, 2026 — request89 reposts it on Darkforums • Jun 10, 2026 — zuma reposts it on Pwnforums
• Oct 5, 2026 — replaceboundless reposts it on Pwnforums
🔎 Data analysis Evidence that the data is likely related to Q-depot's operations
• The records show the database was set up on Sep 7, 2022, and 55,084 accounts (57% of the total) were created in bulk on Nov 14–15, 2022. Q-depot's official YouTube channel introduced its new ERP ordering system, still in test mode, on Nov 27, 2022, and the timing fits if existing accounts were transferred in bulk in November.
• The database structure (membership tiers, wallets, points, coupons, tracking numbers per box) and all 346 brands match Q-depot's public site, and account IDs are fully consistent across orders, wallets, and support tickets.
🔎 Suspicious points
• Phone numbers are unverified (no field on the registration page, almost no phone verification records) and vary widely in format.
• Although the site uses email and password login and has an email verification step, 217 of 228 accounts with misspelled domains (such as gmail.con), which cannot receive a verification email, are recorded as having completed email verification. Of these 217, 210 were created in bulk in Nov 2022, and 206 of those 210 completed email verification in the same second they were created. The remaining 7 were created after the bulk creation. How these records were generated is unconfirmed.
⚠️ Conclusion
• The timing, structure, and consistency suggest the data is likely related to Q-depot's operations, but the email verification records of accounts with misspelled domains remain suspicious and need further checking.
• Whether the dump was extracted from Q-depot's servers and how the intrusion occurred are unconfirmed, and Q-depot has made no official statement as of Oct 8, 2026. A Darkforums listing claims a newer June 2025 version, but the data we analyzed ends on Feb 17, 2025.
• The claim or related data appeared in 6 subsequent forum posts over about 1 year and 8 months, including a listing that claimed to offer a newer June 2025 version. If the leak is genuine, this continued circulation could lead to secondary harm such as phishing, smishing, and account takeover through cracked or reused passwords.
#ThreatIntel #CyberThreatIntelligence #DataBreach #SouthKorea #DarkWeb
Over the past two months, Team D4rkn3ttz investigated how leaked personal data moves across the open web, Telegram, and the dark web.
We aim to reveal the reality behind data breaches—and the people affected by them.
“The Hackers’ Marketplace” starts here:
https://t.co/X9KY2aNNsS
#DarkWeb #ThreatIntelligence #CTI
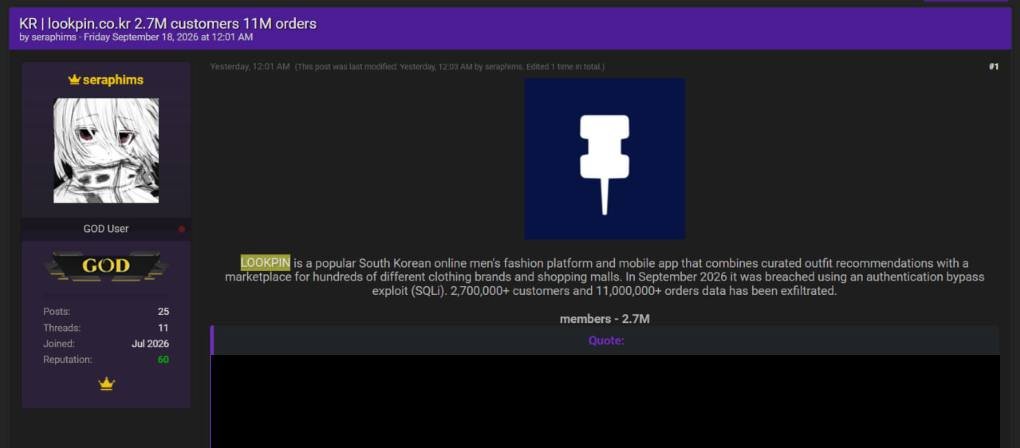
🚨 A threat actor "seraphims" claimed to have breached South Korean men's fashion platform LOOKPIN, offering 2.7M + member records, 11.5M + order records, and 3.47M + saved shipping addresses for sale at roughly $2,000. — Reported by #TEAM_D4rkn3ttz@mingming0l
🕒 Timeline
• Sep 16, 2026 — LOOKPIN detects an unrecognized account and cuts off access to the analytics system
• Sep 18, 2026 — Threat actor posts the breach claim on Darkforums and Pwnforums
• Sep 18, 2026 — LOOKPIN sends breach notification emails to affected users
📁 Claimed scope of the leak
• Members: 2,703,169 records — email, phone number, bcrypt password hash, login IP/session history, member level, PCCC (personal customs clearance code)
• Orders: 11,514,758 records — recipient name, phone number, address, payment processor transaction details
• Saved shipping addresses: 3,474,294 records — recipient name, phone number, address, PCCC
🔎 Sample data validation
• Sample field structure matches LOOKPIN's Lv.1–Lv.13 member level/point system
• Sample shipping-address fields and payment-related data match LOOKPIN's actual service infrastructure
• Names and contact details of several LOOKPIN personnel found in the member sample were consistent with publicly available information
• Member, order, and shipping records were cross-linked by shared member ID, name, and email, consistent with a relationally connected production database
LOOKPIN sent breach notification emails to affected users, confirming that email addresses, password hashes, phone numbers, and IP addresses had been exposed, and stated the incident stemmed from exploitation of a vulnerability in its Metabase analytics system. The scope LOOKPIN has confirmed differs from the scope claimed by the seller, so whether the seller's data is actually tied to this breach remains unconfirmed.
#CyberThreatIntelligence #ThreatIntel #DataBreach #SouthKorea
🚨 An alleged National Health Insurance Service (NHIS) database containing approximately 48M records is being advertised on a dark web forum for $450 — Reported by @mingming0l@kwisejh#TEAM_D4rkn3ttz
📋 Alleged database schema includes:
insured_no, name, rrn, gender, birth_date, age, insurance_type, subscriber_class, employer, household_no, monthly_income_krw, monthly_premium_krw, premium_share, dependents_count, region, acquisition_date, last_checkup_date, long_term_care_grade, arrears_status, card_status, data_export_date
⚠️ The provided sample contains multiple indicators of fabricated data.
🔎 Our foundings from the exposed sample:
• Some acquisition_date values predate 1977, the year South Korea's national health insurance system was introduced — including entries showing acquisition dates of "1962" and "1947."
• Values in the insured_no field contain nine digits, which does not match the expected 11-digit format of Korean health insurance certificate numbers.
• One record lists “고양신협” as an employer. No credit union branch with that exact official name could be identified; credit unions operating in Goyang use names such as “덕양신협” and “원당신협.”
• The NHIS sample database documentation describes eligibility attributes using fields such as sex, age, region, and income decile. The alleged sample instead provides exact monthly income through monthly_income_krw, rather than a decile bucket.
• Sex values in NHIS sample datasets are generally represented as coded values such as 1 and 2, while the exposed sample uses the Korean text values “남” and “여.”
The exposed sample shows strong signs of synthetic or fabricated data. The broader 48M-record claim remains unverified, and the sample alone does not establish a compromise of NHIS systems.
#CyberThreatIntelligence #ThreatIntel #DataBreach #OSINT #NHIS #SouthKorea
⚠️ UPDATE: Further review of the data directory listing GUNRA claims to have stolen from South Korean manufacturer World Tube identified
a directory structure suggesting a possible connection to the company’s internal operations — Reported by
#TEAM_D4rkn3ttz@mingming0l@kwisejh@k_anrms
🔎 Directory and filename information published by GUNRA revealed references to:
• Employee names and apparent roles
• Customers, business partners, and subjects of exchanged materials
• World Tube product or part identifiers
• Factory, production, logistics, and quality-management operations
If GUNRA possesses the underlying files, sensitive corporate, technical, and supply-chain information may have been
exposed.
GUNRA has publicly exposed the directory structure and filenames associated with the alleged dataset. The contents of
the underlying files have not been independently examined.
No official confirmation from the affected organization has been identified. Gunra’s alleged breach and data claims
therefore remain unconfirmed.
#Ransomware #CyberSecurity #ThreatIntel #CyberThreatIntelligence #SouthKorea
🚨 GUNRA, a ransomware group, has threatened to publish 100 GB of data allegedly stolen from Worldtube, a South Korean automotive parts manufacturer — Reported by #TEAM_D4rkn3ttz@mingming0l@kwisejh@k_anrms
The group’s dark web leak site currently displays an active countdown indicating that the alleged data is scheduled for publication in approximately 10 hours.
⚠️ Details listed by GUNRA:
Target: Worldtube
Website: https://t.co/nloydmNKXx
Location: South Korea
Industry: Automotive parts manufacturing
Claimed revenue: US$20 million
Claimed data volume: 100 GB
Status: Publication pending
🔍 This information is based solely on GUNRA’s claims. No leaked files have been independently examined, and the authenticity, scope, and validity of the alleged compromise remain unverified pending further evidence or official confirmation.
#ransomware #cybersecurity #threatintel #cyberthreatintelligence