Graduate scholarship opportunities are now open through the Mastercard Foundation Scholars Program at AUB.
Apply for a fully funded PhD program by March 12, 2026.
@TheCryptoOG89 Hi Agresh,
Just checked out Avinya’s case studies—great work in web3. Any room for a volunteer or dev? I’m web3 + AI UX focused, happy to help where it counts.
GM 🌍
GM Audacity Traders
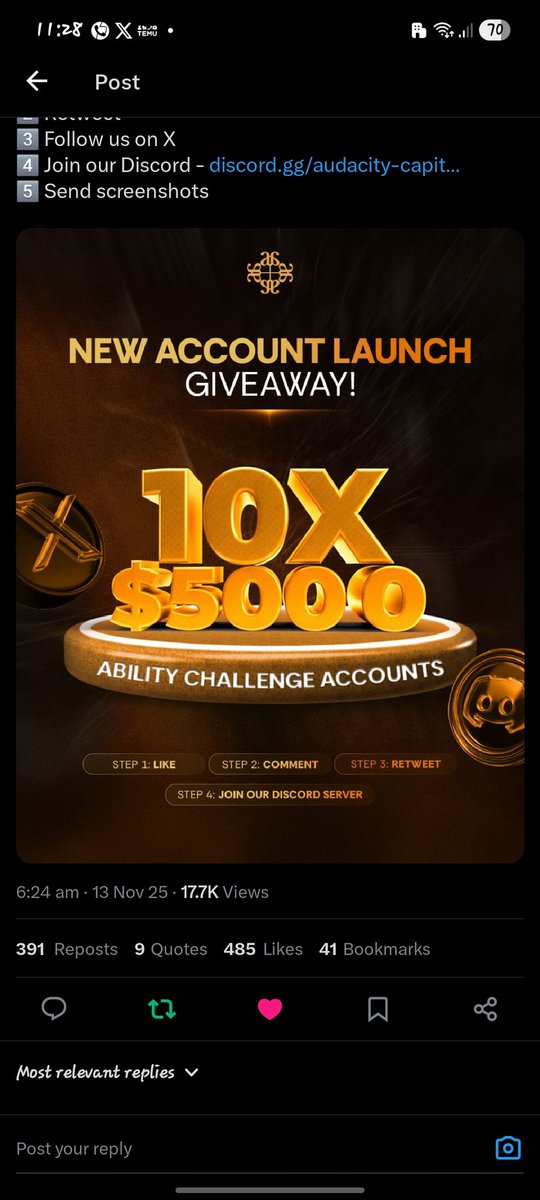
We just unlocked a MASSIVE GIVEAWAY of $50,000 in FREE FUNDED OPPORTUNITIES to celebrate our new Accounts Launch.
To enter:
1️⃣ Like this post
2️⃣ Retweet
3️⃣ Follow us on X
4️⃣ Join our Discord - https://t.co/5T9yiozaDi
5️⃣ Send screenshots
Severe pain, that is what Samuel has been helplessly living with since he was 6. Onovo samuel Ikechukwu has been battling with avascular necrosis of the head of the femur, even though he lives in pain, he kept fighting through the pain. He got admission to study Radiography showing his determination, but the pain became crippling last year.
THREAD
Please RT
🎉 GIVEAWAY ALERT
To celebrate the launch of Stand, we’re giving:
1st winner: 1 Desk 5 Pro + Stand
2nd winner: 1 Desk 5 + Stand
5 runners-up: 1 Stand each
To ENTER:
– RT this post
– Follow @autonomous_labs
– Comment "Stand" + your standing goal
Ends Sep 28.
Your customer support is a joke. “5-min response” notification but I waited 5 HOURS. The agents keep asking the same questions I already answered. Zero professionalism, training. Do you even care about your customers?
@vstar29@RichardOyome @geegpay_hq @RaenestHQ
@danle18846132@vstar29@RichardOyome @geegpay_hq @RaenestHQ You guys had better go train your customer support team. Creating an account is a problem, and getting support from them is also a problem. That response time is so annoying. They just keep you waiting like you don't have better things to do when there are other platforms.
2.6 billion downloads, every week!
That’s the scale of the developer account hijacked in the recent NPM breach.
For those who missed the headlines:
A developer's account was phished after receiving a 2FA refresh email, perfectly impersonating NPM.
The developer whose account was hijacked maintains NPM packages with over 2.6 billion weekly downloads!
The developer's npm account was now used to inject malicious code into these popular packages and publish them in his repository!
My high level thoughts about this breach in particular:
- It's not as bad as we are screaming it to be, because within 15 minutes, the packages were noticed to be malicious. They were taken down within an hour; which I believe is actually great open source community initial response.
- If you were installing packages within the time of these malicious packages being live, yes you should worry.
At RSAC this year, through my talk, titled “How Your Engineering Teams Are Being Attacked-Its Not what You Think.”, I warned about something that the NPM breach proves.
Engineering teams aren’t just being attacked through code flaws, they’re being attacked through trust.
1. As a growing supply chain attack vector, malicious npm and PyPi packages are becoming a clear favorite in the toolkit of attackers. I hope this screenshot below paints a bigger picture of the real lessons and what you must keep your thumb on. Watch my full RSAC talk on YouTube using this link 👉 https://t.co/OOlIKLmh0U
2. Phishing emails are looking more legit by the day. When you sprinkle in fatigue, which the developer alluded to in his linkedin post, it's a recipe for disaster. Like my friend Anna Collard 🌻will always say, we must build digital mindfulness and cognitive resilience.
3. Phishing emails are looking more legit but not necessarily more sophisticated. Legitimate domain impersonation is still a top deception tactic. For example, the developer(maintainer) got the phishing email from support@npmjs[.]help but the legitimate domain controlled by NPM is https://t.co/RL55clLWxM. Do you see what I mean?
4. I hope this reminds us all, that trust is the real attack surface and human identities (and NHIs) are a master key. We must all continue to immunize ourselves with the knowledge and tools to stay safe.
5. Let's go back to the basics...understanding your dev exposure is super important!
Stay Cyber Safe!
Cybersecurity is broad.
Before you start thinking “ethical hacker” or “SOC analyst,” pause.
The real first step? Understanding the domains, the core areas of cybersecurity that guide everything from career paths to certifications.
Let’s break them down 🧵
Just learnt some ethical hacking and wondering what field to explore? Here's a list of fields to explore:
1. Web App Security – Hacking websites to find bugs like XSS, SQLi, and IDOR.
2. Network Pentesting – Attacking networks to uncover misconfigurations and flaws