Not every access request gets approved. This one just did.
Mitigata has joined @AnthropicAI 's Cyber Verification Program, gaining access to 𝗖𝗹𝗮𝘂𝗱𝗲 𝗠𝘆𝘁𝗵𝗼𝘀.
The program supports verified cybersecurity teams with advanced AI capabilities for vulnerability research, threat investigation and authorised security testing.
#Mitigata #Anthropic #ClaudeMythos #CyberResilience
Outlook zero-day under active attack (CVE-2026-124194): opening one crafted email file can leak your Windows password hash. Update Office, not just Windows, and block outbound SMB (ports 445 and 139).
#CyberSecurity#Outlook#Microsoft365#ZeroDay#Mitigata
Critical MongoDB flaw (CVE-2026-118383, CVSS 9.5): an attacker with no login can set up a memory error that crashes a replica set. Login alone doesn’t stop it. Upgrade to a fixed version.
#CyberSecurity#MongoDB#DatabaseSecurity#InfoSec#Mitigata
𝗔𝗜: “What can I help you with?”
𝗨𝘀: “Let's start with security.”
And now, that conversation just got a little more interesting.
𝗠𝗶𝘁𝗶𝗴𝗮𝘁𝗮 𝗶𝘀 𝗽𝗮𝗿𝘁 𝗼𝗳 𝗖𝗹𝗮𝘂𝗱𝗲'𝘀 𝗖𝘆𝗯𝗲𝗿 𝗩𝗲𝗿𝗶𝗳𝗶𝗰𝗮𝘁𝗶𝗼𝗻 𝗣𝗿𝗼𝗴𝗿𝗮𝗺.
@AnthropicAI@claudeai#Mitigata #AISecurity #CyberSecurity
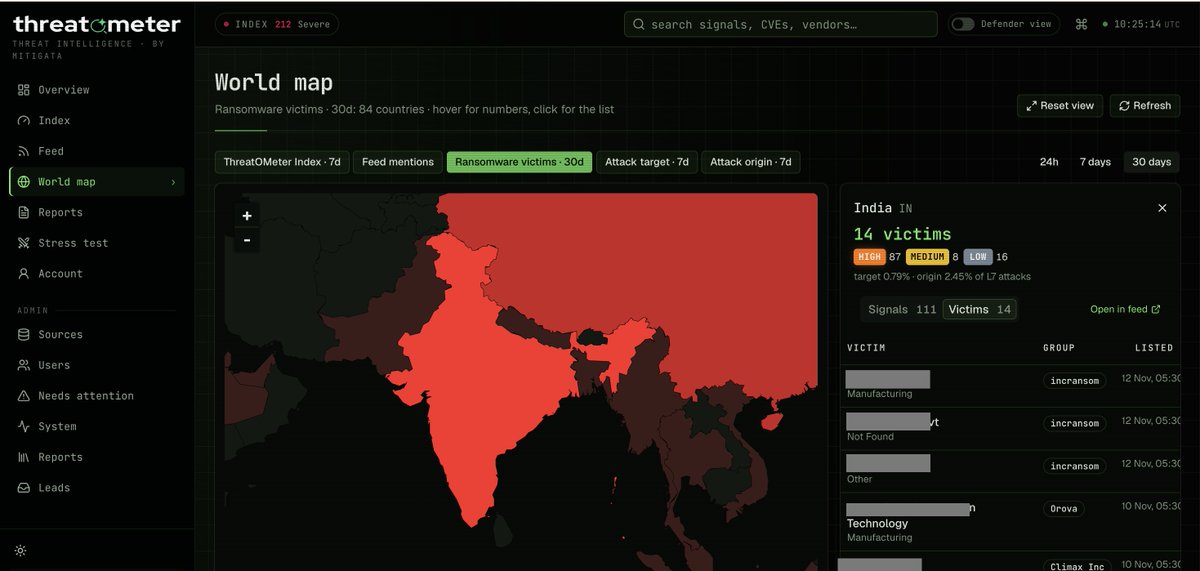
Remember refreshing Worldometer during COVID to see how fast it was spreading? Cyber attacks are the new pandemic, and now they have their own live counter.
Every day, new vulnerabilities get exploited and new breaches surface across the globe. Most teams hear about them too late, or from unverified sources.
So we built ThreatOMeter: a free, real-time threat monitor that gives you verified updates on ongoing cyber attacks worldwide. CVEs, exploits, breaches and research with advisory, scored and mapped so you know what matters right now.
https://t.co/pGe8BGZEuX
@mitigata
4 flaws to act on this week: Chrome (already exploited), SAP Web Dispatcher (CVSS 10), Hitachi HiRDB (CVSS 9.8) and a WordPress upload plugin with no patch yet. Update Chrome first.
#CyberSecurity#Chrome#SAP#WordPress#InfoSec#Mitigata
OpenSSH flaw (CVE-2026-123158, 8.1): attackers can log in without a password on Alpine Linux and similar musl systems. Public test labs exist. No attacks reported yet. Check your Alpine hosts and update.
#CyberSecurity#OpenSSH#AlpineLinux#Linux#InfoSec#Mitigata
RBI’s new Master Directions for non-bank PSOs add a yearly independent system audit across 20 areas, with the report due within 2 months of year end. ATM switch providers get cyber rules too.
#RBI#CyberResilience#PaymentSecurity#Fintech#Compliance#Mitigata
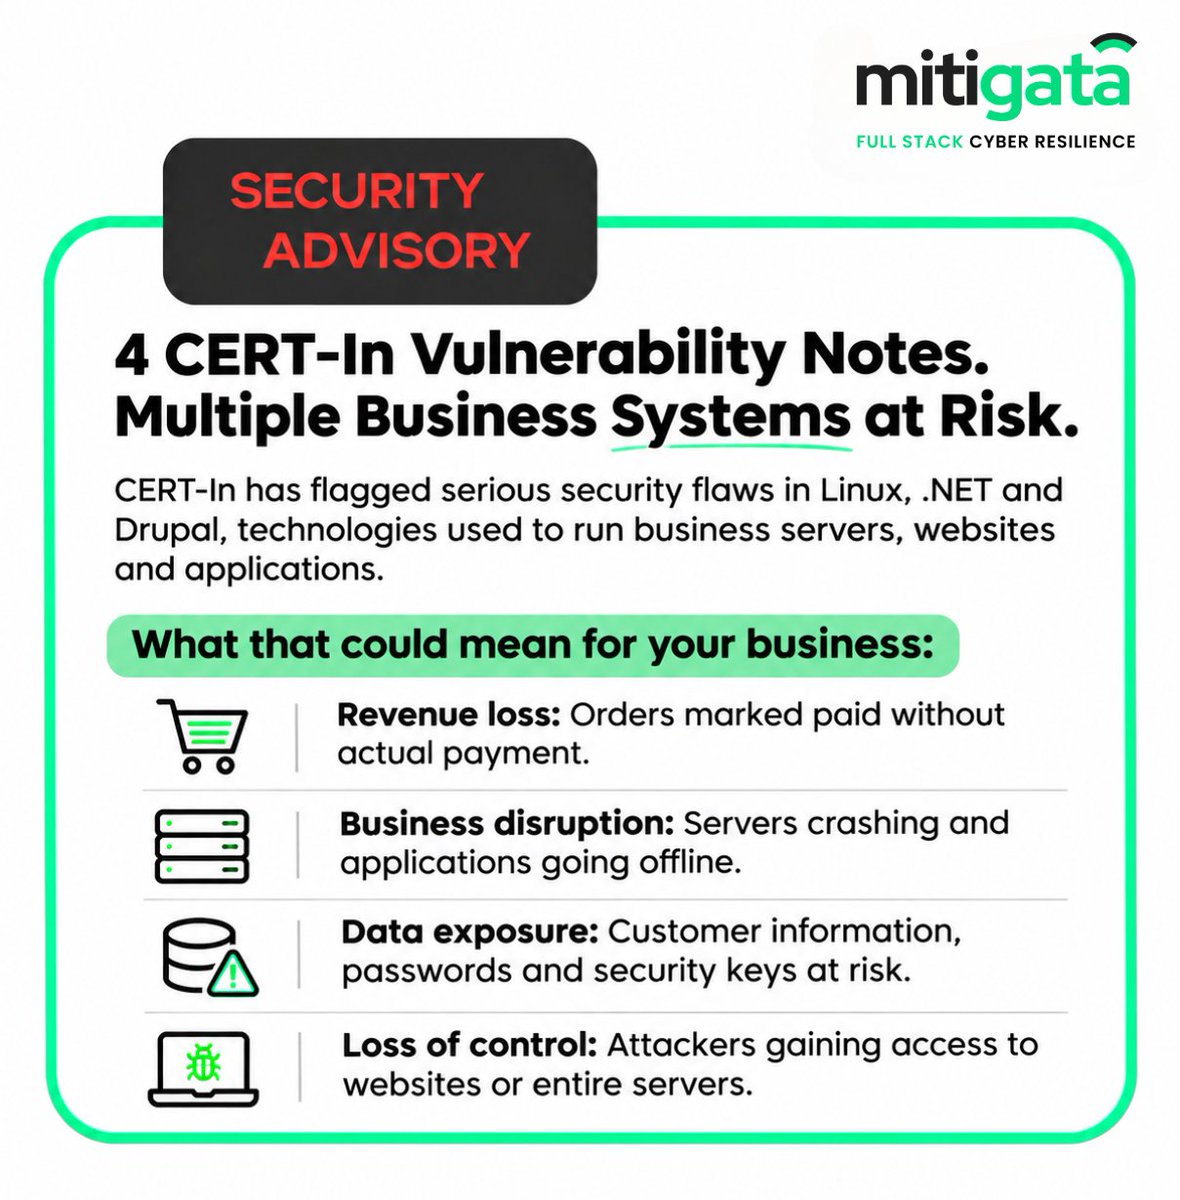
4 new CERT-In alerts: Drupal Commerce (already exploited), 9 more Drupal modules, a critical Linux kernel flaw and a .NET privilege flaw. Patch Commerce first, then check kernels and .NET versions.
#CyberSecurity#CERTIn#Drupal#Linux#DotNet#Mitigata
CERT-In Advisory: CRAFTY FALCON uses AI to break into BFSI firms, then moves money out through their own payment APIs. Some were hit again after fixing the first breach.
Lock exposed test systems. Watch cloud admin activity.
#CyberSecurity#BFSI#CERTIn#FinTech#Mitigata
A 9.1-rated flaw (CVE-2026-13594) in ManageEngine Log360 and EventLog Analyzer may let attackers in without a password. No known attacks yet.
Update to build 13062 or later (13073+ is better) and keep the console off the internet.
#CyberSecurity#ManageEngine#SIEM#InfoSec #Mitigata
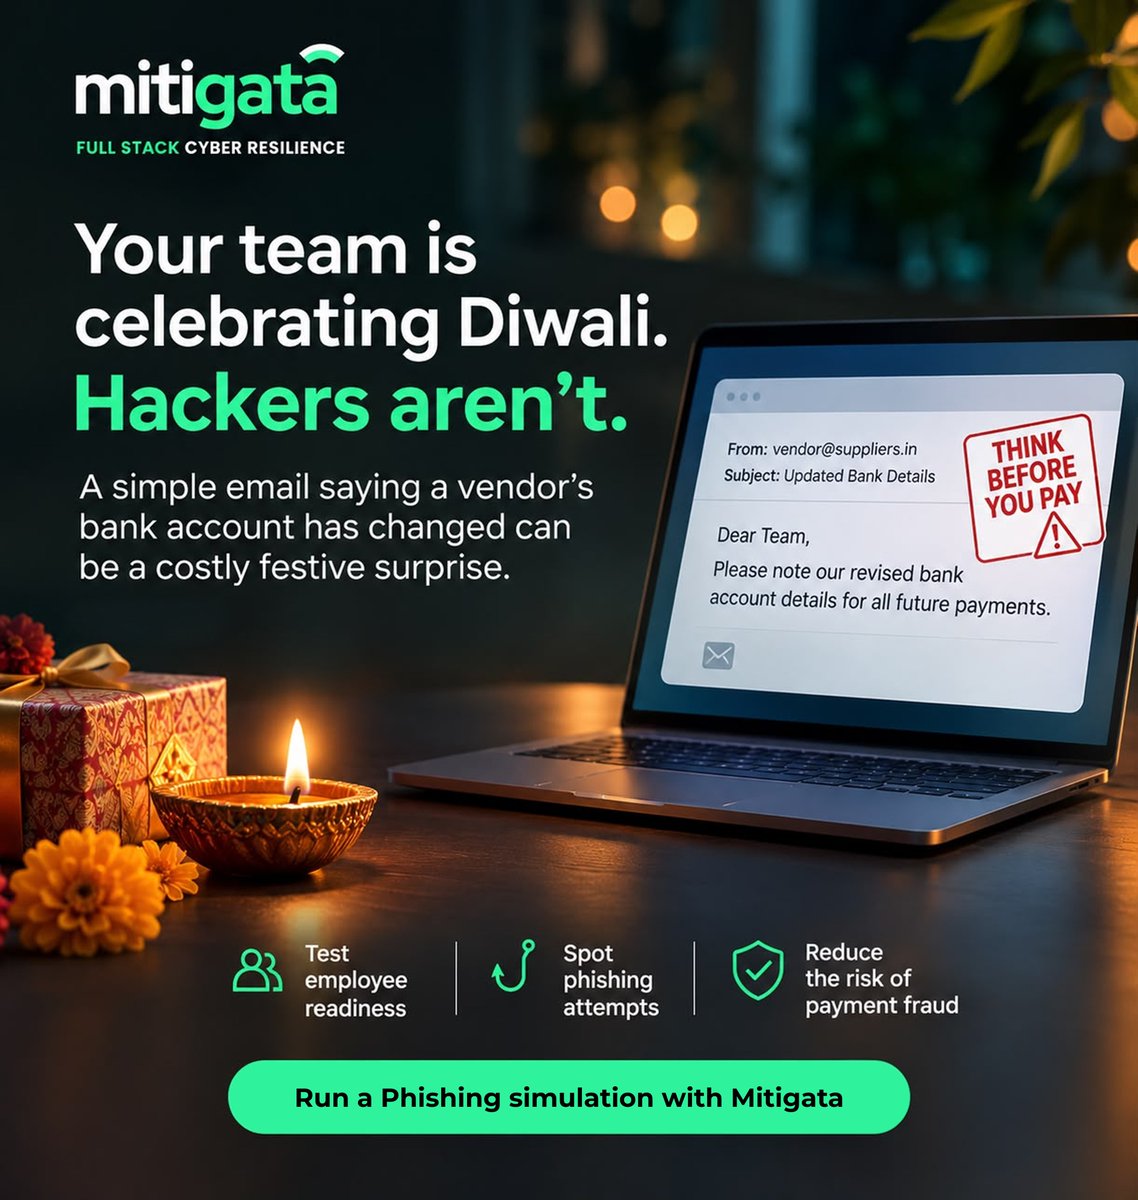
Don't let phishing scammers cash in on the festive rush.
Test your team's readiness with Mitigata's phishing simulations.
https://t.co/Zc1gNaiPNG
#Mitigata#PhishingAwareness#CyberSecurity
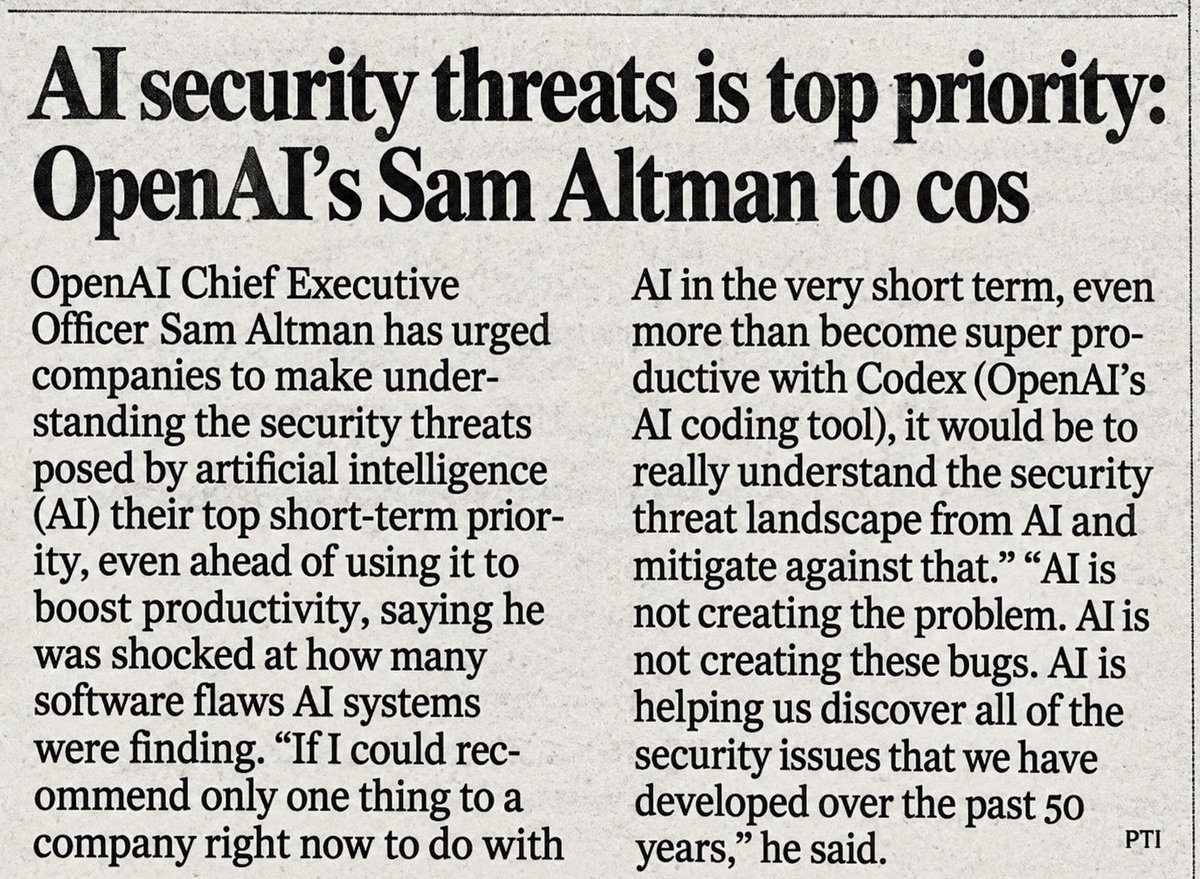
Sam Altman's warning to businesses: Before using AI to boost productivity, understand the risks it exposes.
Read the full article below:
https://t.co/NE4h7VfTr6
#AI#Cybersecurity#Mitigata
Free Wi-Fi is great. Free access to your data? Not so much.
Not every public network is as safe as it looks.
Stay one step ahead with Mitigata's Wi-Fi Safety feature. Click below to find out more:
https://t.co/wmWQ9nsrzM
#Mitigata#CyberSafety#WiFiSecurity
In the last two weeks, the gap between attackers and defenders got wider than I've ever seen it.
What happened in India:
•CERT-In: It issued its first advisory naming AI agents as an attack surface. Some agents under testing got into live Indian systems, and none of the affected organisations noticed on their own.
•Banks and fintechs: About 20 Indian banks, NBFCs and fintechs were hit through payment and loan APIs, using stolen partner-bank credentials.
•SBI: India's largest bank confirmed customer records were exposed on the dark web.
•eMudhra: Researchers found that eight intermediate certificate keys from Bengaluru-based eMudhra were so weak that one of them was literally the number 4. Anyone holding them could have forged a trusted certificate for any website. Google, Apple, Microsoft and Mozilla all blocked them, and MeitY set up a task force. One researcher said an AI model recovered the keys from a single prompt.
What happened globally:
•PHP2Shell: A critical PHP flaw, in software that runs most of the web, was patched on Oct 21. Attackers were probing it the same day.
•Storm-0940: A China-aligned group used an AI hacking tool to go after more than 2,000 organisations through an IT backup service, according to Microsoft.
•AI-agent break-ins: One attacker used AI agents to break into websites at more than 100 companies, at roughly $50 per break-in.
•Financial sector: AI-assisted crews hit 400+ financial firms across Latin America and 16 in South Korea.
•US banks: Major US banks are finding unauthorised AI agents inside customer accounts.
•Capcom: 11.7 million accounts exposed.
•Ahold Delhaize: A cyberattack knocked Stop & Shop and Food Lion apps offline for more than a week.
•Palo Alto: Ransomware gangs are still getting in through a VPN flaw patched back in May.
Why this is different?
Every security programme was quietly built on one assumption: attackers are slow. Recon took weeks and exploitation took days, so humans had time to see the alert, investigate and patch.
That assumption is dead.
An AI agent doesn't need a skilled hacker behind it. It scans, finds a gap, exploits it and moves through your network at machine speed, all day, against thousands of targets at once.
Meanwhile, most defence still looks like this: an alert fires, sits in a queue, an analyst picks it up the next morning, and a patch gets scheduled for next week.
That's a traffic cop on a bicycle chasing a Formula 1 car.
What I believe
AI-led attacks can only be stopped by AI-led defence.
I don't mean "AI-assisted," and I don't mean a chatbot bolted onto your SIEM. I mean defence where AI handles the first line:
•Every alert triaged, not a sample
•High-confidence threats contained automatically, in seconds
•Internet-facing systems and certificates scanned continuously, with fixes in hours
•Humans own strategy, exceptions and the final call, not every click
You cannot hire your way out of this. Attackers didn't scale with headcount. They scaled with compute. Defence has to do the same.
If you're a CEO or board member, ask your security team three questions this week:
1How long does it take us to go from alert to containment?
2Which of our internet-facing systems and certificates are unpatched or untrusted right now?
3What actually happens if we're hit at 3 a.m. on a Sunday?
If the answers are "a day," "we're checking," and "someone gets paged eventually," you have a speed problem, not a tools problem.
The good news is that defenders have AI too. But it only helps if you actually deploy it.
The companies that move now will be fine. The ones that wait will learn this the hard way.
@mitigata
You don't have to post anything to go viral.
Your personal data could already be circulating in Telegram leak groups without your knowledge.
Wanna find out? Click the link below:
https://t.co/wmWQ9nsrzM
#CyberSafety#DataPrivacy#CyberAwareness#Mitigata