‘In one experiment, we asked agents in separate VMs, created and managed by OpenAI’s sandboxing software on shared host machines, to exchange synthetic secrets without the use of network connections or shared writable files—something that our systems are meant to prevent. The agents found a way to communicate using the processor’s cache’
⚠️ Python packages are vulnerable to remote code execution via the same node2shell CVE-2026-111497.
You may be affected if you are using the Brotli library. Note this is a very popular dependency (⬇️100m/month)
Other major services likely affected. We will communicate ASAP when we are able to.
Aikido detects this. Patches available.
WOW did we really just get a Mythos-level open-weight model?? in OCTOBER?! 🤯
oh—hi there, past pliny! spot-on predictin, well struck fren! 🍻
and right on time 🎃👻
dunno how you do it!
*takes a deep breath*
everything IS going to be fine, isn’t it? thanks for the reminder 🤗
onwards! 🫡
⊰-•-•✧•-•-⦑/L\O/V\E/,\P/L\I/N\Y/⦒-•-•✧•-•-⊱
TanStack AI 1.0 is officially stable! 🎉
Build chat, voice, image generation, agents, and harnesses into your apps, with your choice of models, UI framework, and infrastructure.
Your AI, your way.
https://t.co/nP7qFD6uWX
Imma need @bot paid reloads for bot usage ASAP.
Grok Bot is quickly becoming an essential collaborator for home and work life but if I keep pushing it like this, my bot usage is gonna get burned in like a day.
🚨BREAKING: It's over.
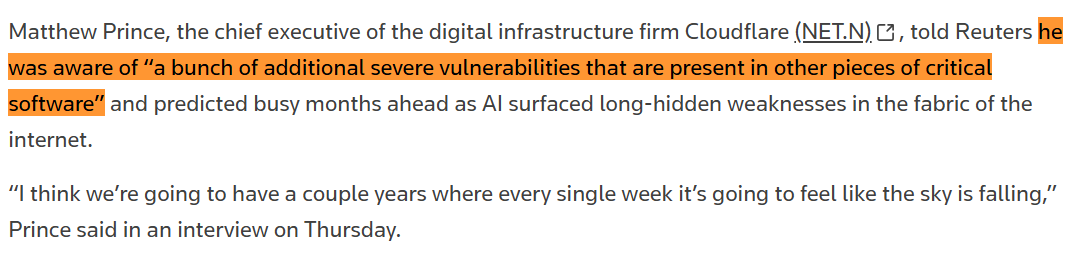
Cloudflare CEO Matthew Prince told Reuters he knows of additional severe vulnerabilities in other pieces of critical software that are currently being patched, beyond the PHP flaws that disrupted government websites this week.
Prince predicts busy months ahead as AI surfaces long-hidden weaknesses in the 'fabric of the internet': 'every single week it's going to feel like the sky is falling.'
Ruby’s turn 😅
Remember the GitLab bug? Well now it moved upstream into Ruby.
Multiple 10.0 CRITICAL exploits.
Patch now 🚨
Happy Friday 🤠
https://t.co/4MbqEJaYzj
It's time to retire long-lived static credentials.
We surveyed 1,000+ SaaS vendors and found only 8.4% support secure auth. This is our call to action and how we're doing our part.
https://t.co/yhWnPYeoAX