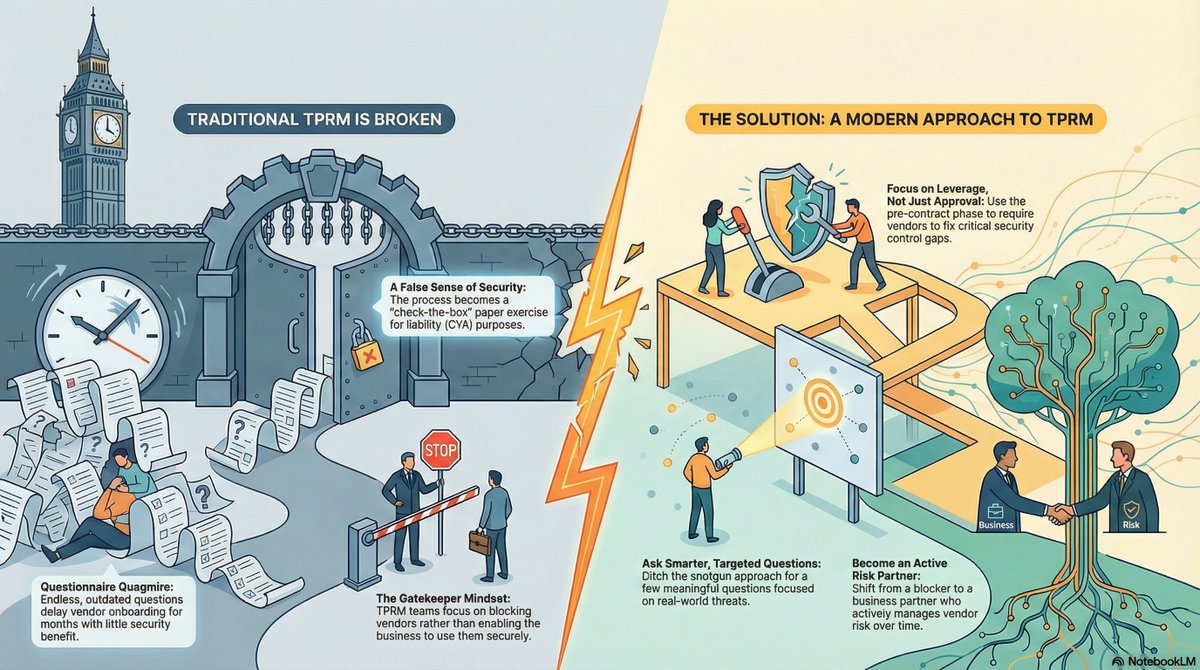
Have you ever filled out hundreds of security questions for procurement?
This discussion between G Mark Hardy and Nate Lee in a recent episode of @cisotradecraft highlights few ways to improve this. #GRC#ThirdPartyRisk#TPRM#DevSecOps#CyberSecurity https://t.co/u9b0AC7sEA
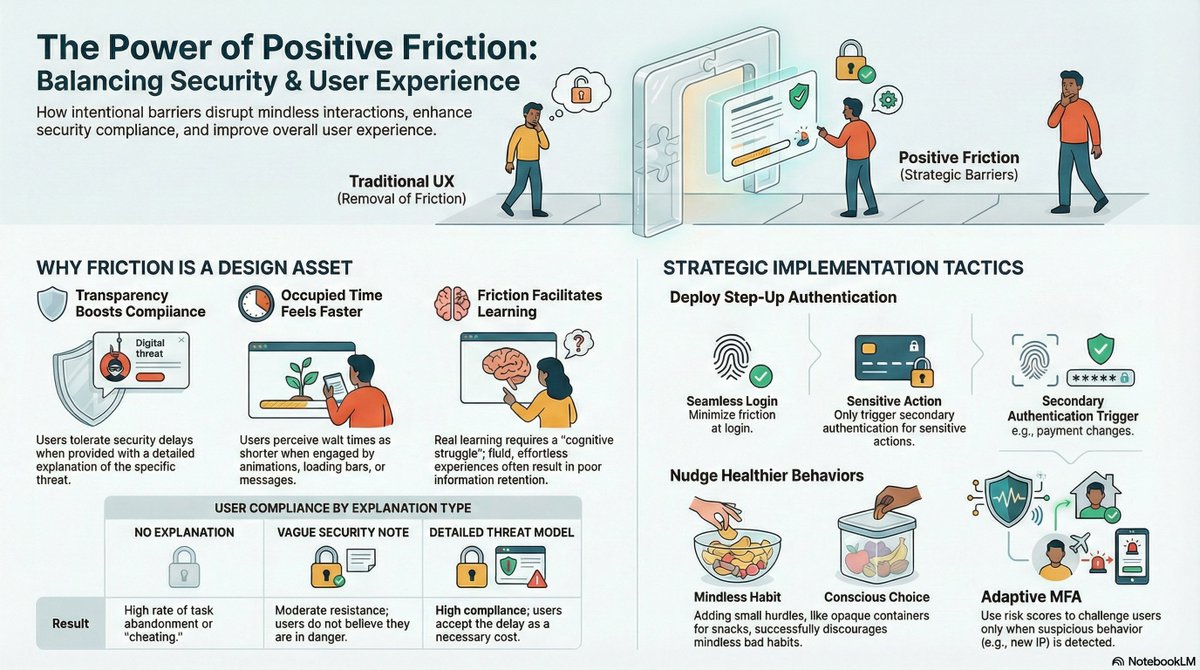
Security friction isn’t the enemy - meaningless friction is. Friction without context or ownership becomes noise. Security is a culture where teams pause to understand risk, not just tick boxes. Ariel Shin & Rahul Zhade #SecurityCulture#AppSec#DevSecOps https://t.co/L5RJZNscls
Authorization hierarchy decides what an identity can do. For AI agents calling APIs at machine scale, flat scopes = over-privilege and blind spots. @aaguiar from @auth0 details the layers of API Authorization. #APISecurity#AISecurity#ZeroTrust#DevSecOps https://t.co/OoydsZZsb1
SPIFFE gives each workload a cryptographic identity, enables mTLS, and supports least privilege across distributed AI services. Pablo Diaz from @HashiCorp shows how Identity is the control plane for AI security. #AISecurity#SPIFFE#ZeroTrust#AgenticAI https://t.co/nGbFb3Wlv9
.@TreasureData's Eric Chow shows how agentic TPRM solution uses AI agents + automation to parse compliance reports and turn manual reviews into minutes, boosting speed and consistency. #TPRM#CyberSecurity#AgenticAI#RiskManagement https://t.co/ApB0gUUmyB
.@GHSecurityLab Taskflow Agent uses AI to automate vulnerability triage, reduce false positives, and help teams find real vulnerabilities faster. This is how we secure AI-generated code at scale.
#AISecurity#AppSec#DevSecOps#AgenticAI https://t.co/QJRhchQNe2
Validate tool-call origin, require consent for invocations, and flush stale context between turns to reduce injection attacks for agents. Clinton Carpene, Alex Rosenzweig @blocks#AISecurity#AgenticAI#Guardrails#ThreatModeling https://t.co/cisH9P8j7Q
The Agentic Trust Framework applies Zero Trust to agents using continuous identity, behavior, data, & segmentation checks, maturity controls for autonomy. This is how secure agentic AI is governed. @jlwoodruff#AgenticAI#ZeroTrust#AISecurity#DevSecOps https://t.co/IDPBYn04NX
In AI systems, the prompt is the attack surface. NOVA by @fr0gger_ is a prompt pattern matching engine - lets you hunt and detect suspicious prompts using keyword, semantic, and LLM-based rules. https://t.co/FaKv9uDnK0
#AISecurity#PromptPatterns#DevSecOps#ThreatHunting
AI code generators produce fast results - but they also repeat insecure patterns. Fix it with structured prompt patterns like Anti-Pattern Avoidance and Secure/Insecure Diff. @EndorLabs https://t.co/eNf2OrswhV
#PromptPatterns#SecureCoding#AISecurity#DevSecOps
Prompt patterns make AI responses predictable and safe. Context engineering = structured prompt blocks + hard constraints + reusable patterns. Read the research paper here by researchers at Vanderbilt University. #PromptEngineering#AISecurity#AgenticAI https://t.co/GN5vyTzblX
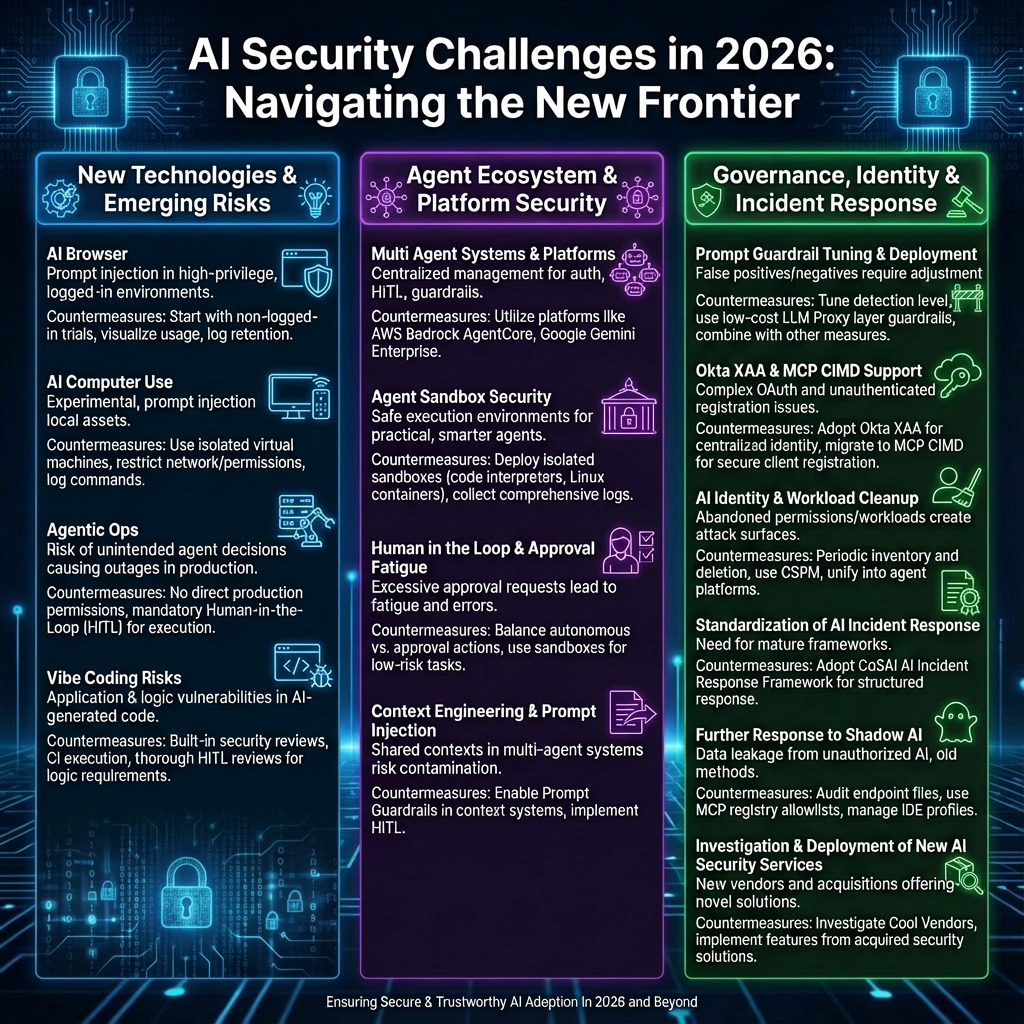
From confused deputy to MCP auth flaws, prompt injection, in 2026, we see agentic ops, multi-agent platforms, sandboxes, identity complexity, prompt guardrails, and standardized AI IR. Hiroki Akamatsu shares https://t.co/BCPD18Subd
#AISecurity#AgenticAI#CyberSecurity#DevSecOps
Clawdbot showed how dangerous exposed AI agents can be. @Cloudflare's Moltworker shows how they should be built.
It uses Workers, Sandboxes, AI Gateway, and Zero Trust access to mediate every agent action. https://t.co/M98gYdo19W
#AISecurity#AgenticAI#CloudSecurity#ZeroTrust
Are your Postgres servers melting down right now? Congratulations AND you need PG Dog - the founder Lev is one of the world's experts at scaling and sharding databases - he did it for Instacart and his software can do it for you.
If your replicas are falling behind and your IOPS are pegged, it's time.
https://t.co/q0Acmi4riq
In Kubernetes, nodes/proxy GET is widely considered “read-only.” But via WebSockets, it can execute commands in any Pod - effectively cluster-wide RCE.
Research shared by @GrahamHelton3 in his blog post.
#KubernetesSecurity#DevSecOps#CloudSecurity https://t.co/Mx7xToHnOi
The amount of crap I get for putting out a hobby project for free is quite something.
People treat this like a multi-million dollar business. Security researchers demanding a bounty.
Heck, I can barely buy a Mac Mini from the Sponsors.
It's supposed to inspire people. And I'm glad it does.
And yes, most non-techies should not install this.
It's not finished, I know about the sharp edges.
Heck, it's not even 3 months old.
And despite rumors otherwise, I sometimes sleep.
AI agents like Moltbot are always-on control planes connected to real systems and credentials.
@pyotam2 and Team found publicly exposed instances with secrets, integrations, and automation workflows. #AgenticAI#DevSecOps#aisecurity#identitysecurity https://t.co/9Ql4Bdev4W