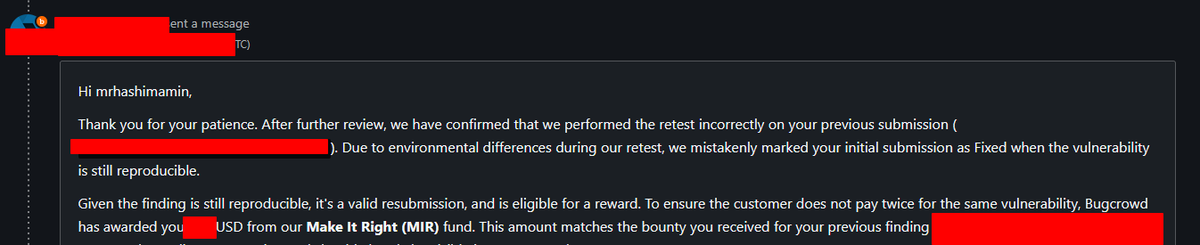
I love @Bugcrowd tbh <3
A year ago, I reported my first bug to a public BBP on BC. A month ago, it got "resolved"...
I reproduced it again with the same steps xD and BC paid me twice for it
A simple P3 PrivEsc.
- Docs: u can't convert private chats to public
- Using the app: `P` > private, `O` > Public
- convert public chats to private (feature)
- Modify the `privacy` to `O`
- Done
https://t.co/fgPdKEVCb8
---
#bugbountytips#privesc#infosec#bugbountytip
Bug: Logic flaw led to PrivEsc
Severity: P3 aka $$$
- Adding new user to chat -> 403
- Attacker use a feature No.1
- Attacker turns on a feature No.2
- User2 (Attacker2) has been added (Automatically while using Feature No.2)
https://t.co/OhMuATJgnR
#bugbountytips#Infosec
Add a comment
Delete it -> 200 ok -> deleted
Delete it again -> 200 ok -> next comment deleted
User adds a new comment -> old comments restored
Send it every 2 seconds with python -> comments deleted again -> useless comment function
https://t.co/pm0UCqxvgJ
#BugBounty#infosec
1. `/createuncommittedpurchaseorder` has an IDOR, but it's a 32-character UUID.
2. Complete the purchasing process and there's another IDOR, which is used to retrieve this long UUID xD
For more details: https://t.co/lwhiCGC6eo
#BugBounty#bugbountytips#hackerone
Today I reached the 400th report submitted to @Hacker0x01 , 140 out of them is Duplicate + 109 is informative , Just keep Going and chase ur dreams everywhere , U have to keep walking to arrive 😄