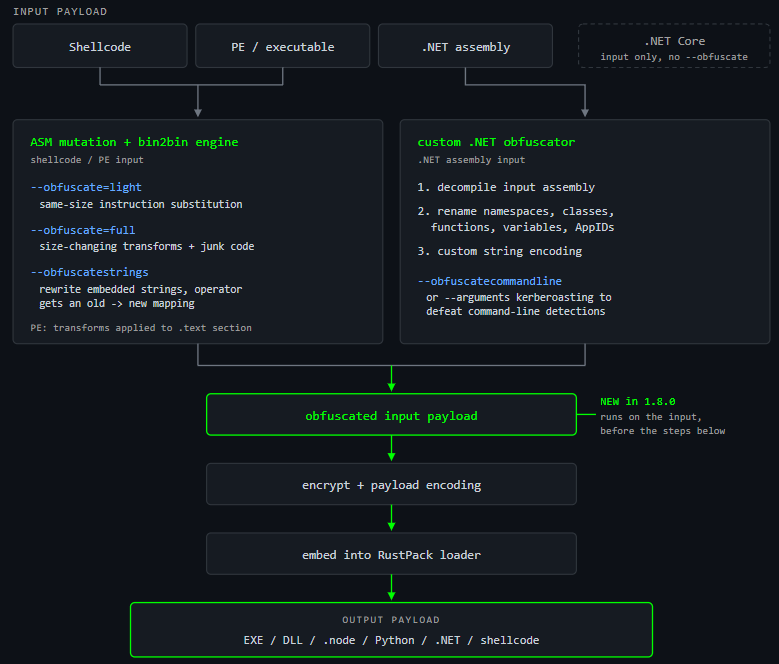
RustPack Release 1.8.0 was shipped to our customers recently. Short Blogpost with the most relevant new features for everyone here 🔥🔥
https://t.co/ufDNFPhaqH
#RedTeam#OST#Pentest#Maldev
Initial access. Post-exploitation. Persistence.
These are the phases most of you need to simulate in your day-to-day engagements.
RustPack can help across all of them. Our latest blog post covers a range of common TTPs and shows how RustPack can help you save time, reduce effort, and streamline your operations. 🫡
https://t.co/W4uhn3mx0g
#OST #maldev #Pentest #RedTeam
Backdooring existing executables or DLLs for stealthy payload execution? With version 1.7.0 of RustPack, this can be easily done in a few seconds.
We live-debug/trace the execution flow in the target executable to find a suitable backdoor position at runtime, instead of patching the entry point. 🤠
Even Frontier LLM models analysing the output executable with reversing tools at hand and one task - determining whether the target is benign or malicious - will tell you this is benign. 🔥
We work hard, you get the best possible evasion!
#redteam #ost #pentest #maldev #evasion
Did you know you can hide payloads in images or videos without breaking them? 🎓 That's called steganography.
Since RustPack version 1.6.0, we support steganography to, for example, hide payloads in any PNG image file. The image file can get dropped to disk on the target system, but can also get hosted on a remote webserver. The RustPack loader will than download the .PNG file from disk or the remote webserver and retrieve the encrypted payload to execute it in an OPSec safe way from memory. 🔥 Defenders will only see an image being downloaded, which won't lead to attention on a proxy/firewall or NDR solution as it's really "just a picture" - or at least looks like that.
In this exemplary video, we embed a messagebox shellcode in a picture to retrieve it from the MSecOps website at runtime. Of course, this feature will also work with any DLL payloads, for example, with a sideload. And any other input, such as Command & Control shellcode, can be used!💪
RustPack version 1.6.0 was just sent to our customers! This release includes multiple enhancements to existing bypass techniques, but also has some major new features such as:
- Steganography support - embedding encrypted payloads in PNG images 🫡
- Payload retrieval from a remote web server - and yes PNG images can also get downloaded from a web server instead of from disk only
- Position Independent Code output format, RustPack can now be considered as your personal polymorphic Donut on steroids! Create shellcode from .NET assemblies or PE files to stealthily load them at runtime. 🔥🔥
The MSec Operations - @MSecOps - Discord channel provides vetted Cyber Security experts the opportunity to exchange TTPs, to ask questions and to get answers! 😎 More than 280 verified people already joined.
https://t.co/bsKKeG8Jat
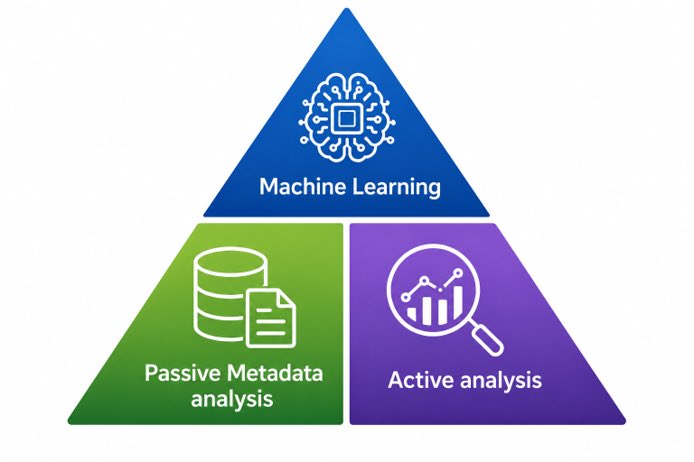
Machine learning-based detection is not yet widely used by AV/EDR vendors to flag potentially malicious executables. However, some few vendors have already implemented effective engines for unsigned executables. 💡And this has nothing todo with signatures!
In the past, the easiest way to get rid of such detections was to use a DLL instead of an executable, as for those the detections are not that aggressive - yet. From our perspective it's only a matter of time untill DLLs get flagged in a similar way. What are you using to tackle such detections?
RustPack 1.5.1 has just been released to our customers. The main change in this release is the implementation of multiple new parameters to bypass these machine learning-based detections. 🔥
Tools such as https://t.co/IKyo8x29Vk from Impacket are usually flagged for lateral movement due to the pre-built service executable that is dropped on the remote system. However, some vendors also flag Impacket based on its behaviour.
With RustPack, you can easily create service executables that won't be detected by signatures or behaviour-based detection. 😎
In this demo video, an unsigned service executable is generated. This will only fire the payload on a system with the hostname 'Win11' — environmental keying will prevent the payload from showing up in a sandbox or cloud analysis.
To avoid Impacket detection, we drop and execute the binary via the recently released Titanis protocol library from @TrustedSec:
https://t.co/AZcygPtDjb.
The result is an Adaptix C2 connection in the SYSTEM context. 🫡
#Pentest #RedTeam #Malware #OST
Around three months ago, we provided our customers with RustPack version 1.4.0. 💪 This version included several changes to the core code of the loader component. For example, there were new options to disable the use of indirect syscalls in case any vendor creates detections on those in the future. It is also possible to switch to ntdll or Win32 function usage. Other changes included:
- Process hollowing support as an alternative to module stomping (which was already included), with a new OPSec save spawn/inject technique for shellcode execution; no ETWti events for the execute primitive, which could lead to a memory scan. 🔥
- It is now possible to store encrypted payloads on the target system's registry and load them from there at runtime.
- Environmental keying support has been added: the payload will only fire when the target system is joined to the specified domain or when the hostname matches. 🛸
- Additional random anti-emulation stubs were added for each payload and tested successfully against major EDR vendors.
- The documentation has been overhauled to include detailed instructions on how to find custom DLL sideload binaries, how to weaponise them, and how to perform COM hijacking! 🎓
RustPack 1.5.0 was released to customers just today. The main change here includes:
- Polymorphic obfuscation for each payload, with lots of newly added code stubs.
- Control flow obfuscation to make static or dynamic analysis more difficult.
- Several anti-static analysis stubs that will lead to broken control flows for reverse engineers.
- New anti-debug checks at runtime.
Interested in using RustPack yourself? Contact us at info[at]https://t.co/7A5FxNExvF! 🫡
Creating COM hijacking payloads has never been easier than with RustPack! With COM Hijacking, you can persist on a target system by 'living' in trusted user processes, such as the Chrome browser. You only need to bring one DLL. When the user opens Chrome, for example, a C2 connection is established. 🔥
Achieving stable payload execution without crashing or freezing the target system requires an understanding of what is relevant.
Additionally, lots of processes may attempt to load the hijacked CLSID; you don't want to receive 43 beacons per day from the same system. Limiting execution to a defined process is important here! 🎓
What about combining that payload with environmental keying, anti-emulation, anti-sandboxing, as well as AMSI and ETW bypasses? Doing all this yourself will take time. With RustPack, however, you can create such a payload in a few seconds, and it's stable!
The video demonstrates how to create a payload DLL to execute Adaptix C2 shellcode in the Chrome browser. 🛸
Rumour has it that Jonas Lykkegaard's self-delete technique doesn't work on Windows 11 anymore. Well, the original proof of concept (PoC) does not, but slight modifications bring this technique back to Win11!😎
With #RustPack, you can easily generate self-deleting executables or DLLs. The following video showcases a DLL being executed from rundll32.exe and deleting itself while the process continues to run. 🔥 Of course, this also works for DLL sideloads.
Having problems generating payloads yourself? Don't have time for proper evasion? Your loaders get flagged regularly? We've got you covered — contact us at info[at]https://t.co/7A5FxNExvF 👍
And yes, out custom Ruy-Lopez technique even works perfectly fine for e.G. DLLs that are run via rundll32.exe. Same works for sideloading DLLs, and so on. 😎
The Ruy-Lopez technique sometimes helps a lot with evasion. The technique was published and open sourced by our founder @Shitsecure two years ago. In #RustPack version 1.3.1 we added a custom, non-public version of this technique that is much more OPSec safe than the public version.
The original release only allowed spawn/inject, which is relatively limited. If you wanted to stay in your local process or sideload binary, you could not use it. In RustPack you can use Ruy-Lopez for local execution AND spawn/inject for both executables and DLL payloads. And it will prevent userland EDR DLLs from loading on top of amsi.dll. 🤠
For a few months now, all Sliver payloads have been flagged by many vendors because of the built-in AMSI patch bypass. Most people stuck to modifying the sliver source to get rid of these detections. Well, if amsi.dll is never loaded at all, the patch won't happen either, and you can get rid of this detection just by using the Ruy-Lopez technique. 💡
The following video shows how to pack a Sliver executable with RustPack to get a fully functional connection without any detections. 🔥
And this is just a small use case. A fully interactive Powershell runspace with all amsi related DLLs blocked and no userland hook DLLs sounds great too, right? Easy to build with RustPack in a few seconds. Execute all those Powershell scripts like it's many years before 2025. 🥳
#RedTeam #Pentest #OST #Malware #Maldev