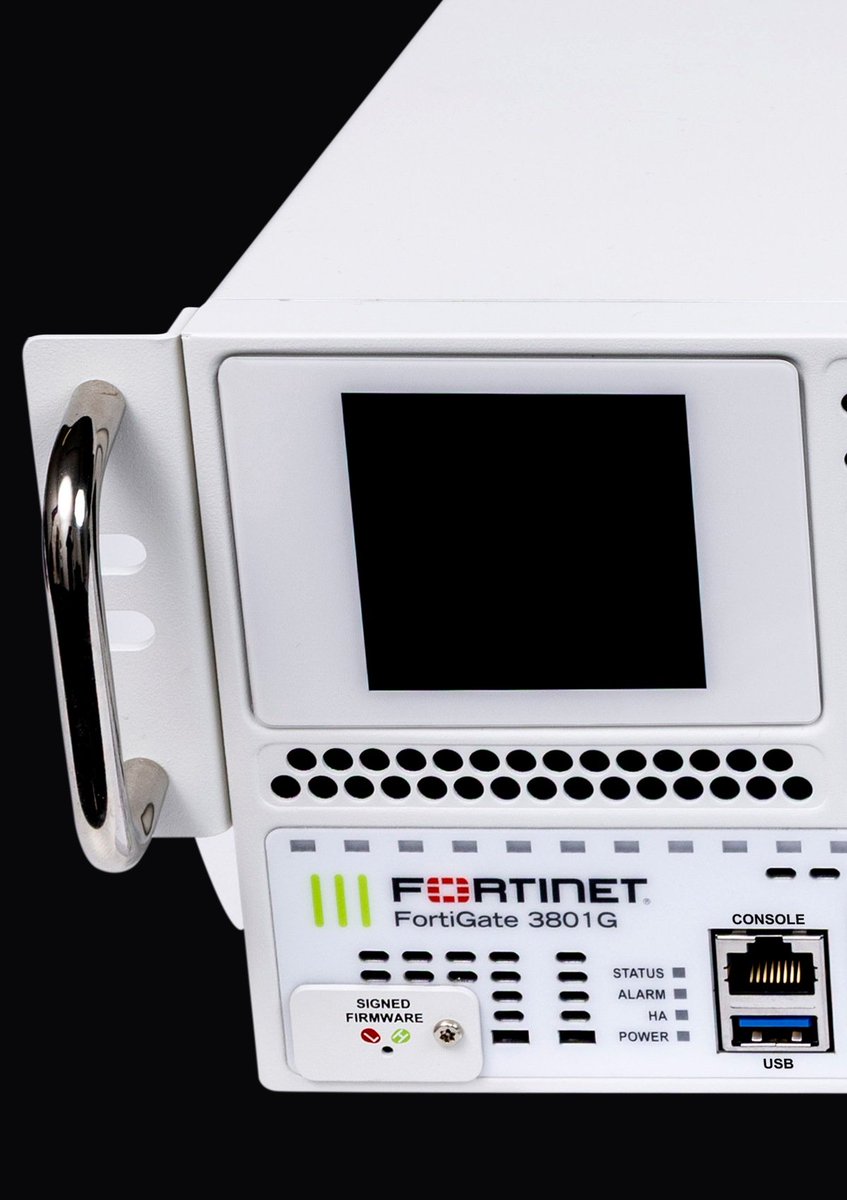
‼️ Fortinet is telling customers to patch its firewalls now but won't say what the critical flaws are until November 10.
Its AI testing found them with help from Anthropic, OpenAI, Google and SpaceX.
It says AI now lets attackers turn a patch into an exploit in hours or days.
⚠️ Python packages are vulnerable to remote code execution via the same node2shell CVE-2026-111497.
You may be affected if you are using the Brotli library. Note this is a very popular dependency (⬇️100m/month)
Other major services likely affected. We will communicate ASAP when we are able to.
Aikido detects this. Patches available.
Evolving threat 🚨 CVE-2026-111497, previously known to affect Node.js (node2shell) and Python has evolved into “HTTP2Shell.”
A significant blast radius.
This vulnerability leaves many libraries and applications using HTTP vulnerable to pre-auth RCE via Brotli decompression.
Please be aware. Fixes not yet available for all affected services. Look for Brotli (1.2.1) dependency upgrades when they become available.